
CVE-2026-31431
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
binary-exploitationeducationexploitation+3
pulentoski/cve-2026-31431Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 trinadh465/frameworks_base_aosp10_r33_cve-2022-20138
Android framework patch for CVE-2022-20138, addressing a privilege escalation vulnerability in AOSP 10.
 trinadh465/frameworks_base_aosp10_r33_cve-2023-20911
Android framework patch for CVE-2023-20911, addressing a security vulnerability in AOSP 10.
 asbawy/graftraverse-cve-2021-43798
CVE-2021-43798 MiNi Exploitation Framework
 satheesh575555/frameworks_base_aosp10_r33_cve-2022-20142
Android framework base repository for AOSP 10 r33, containing the fix for CVE-2022-20142, a privilege escalation vulnerability in the Android…
 trinadh465/frameworks_base_aosp_10_r33_cve-2022-20338
Android framework patch for CVE-2022-20338, addressing a vulnerability in AOSP 10. Provides source-level fix for mobile security.
 1numak1/cve-2025-31337
CVE-2025-31337 Security Advisory - Critical Buffer Overflow in AI Chatbot Framework
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 azdevops143/fragnesia-charan-cve-2026-46300
Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…
 jshdevs/cve_kernellinux_jsh
Framework modular Bash para auditar CVE-2026-31431 (CopyFail) y CVEs relacionados del kernel Linux en distros RPM-based (AlmaLinux, Rocky, CentOS…
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 helsecert/cve-2022-22965
Detection scripts and guidance for CVE-2022-22965 (Spring4Shell) vulnerability in Spring Framework, including PowerShell and Bash scanners for…
 uthrasri/frameworks_opt_net_wifi_cve-2021-0390
Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.
 r00t4dm/cve-2018-14667
about CVE-2018-14667 from RichFaces Framework 3.3.4
 uthrasri/framework_base_cve-2023-21285_nopatch
Android framework vulnerability analysis and exploitation demonstration for CVE-2023-21285, providing a no-patch test case for security researchers.
 cj-0107/cve-2022-26134
PoC for CVE-2022-26134, a Confluence Server OGNL injection vulnerability, built on the pocsuite3 framework for authorized security testing.
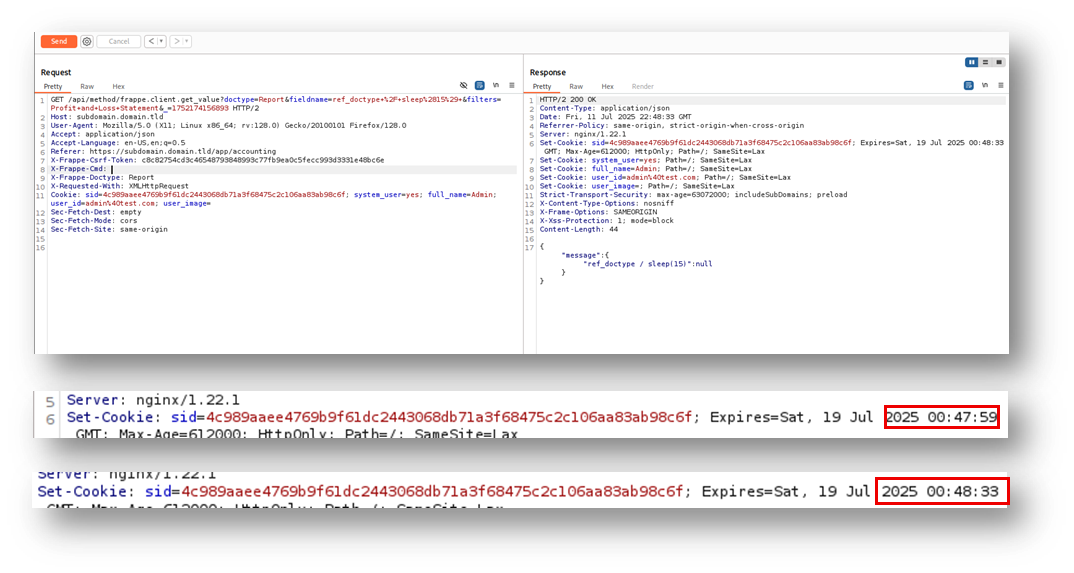 moalali/cve-2025-56380
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
 snip3r69/spring-shell-vuln
Spring has Confirmed the RCE in Spring Framework. The team has just published the statement along with the mitigation guides for the issue. Now, this…