
CVE-2017-5123
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
binary-exploitationcontainer-escapeexploitation+2
teawater/cve-2017-5123Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 hexastrike/ivanti-connect-secure-logs-parser
A Python script for examining Ivanti Secure Connect (ICS) event logs, designed to support investigations into vulnerabilities CVE-2025-0282,…
 titus-soc/-cve-2024-3094-vulnerability-checker-fixer-public
A lightweight utility designed to detect and remediate systems affected by CVE-2024-3094, a critical vulnerability impacting [insert affected…
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…
 wh04m1001/cve-2023-20178
Proof-of-concept for arbitrary file delete vulnerability in Cisco Secure Client and AnyConnect, enabling privilege escalation to SYSTEM via Windows…
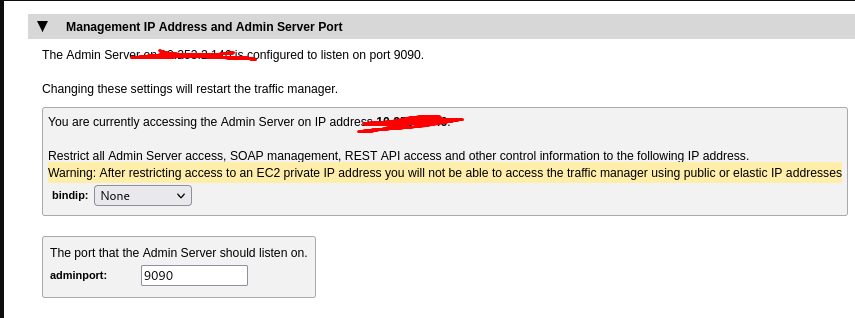 aerchy/cve-2024-7593
Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…
 kukrimate/cve-2020-14372
Proof-of-concept exploit and write-up for CVE-2020-14372, demonstrating Secure Boot bypass via malicious ACPI SSDT to disable kernel lockdown and…
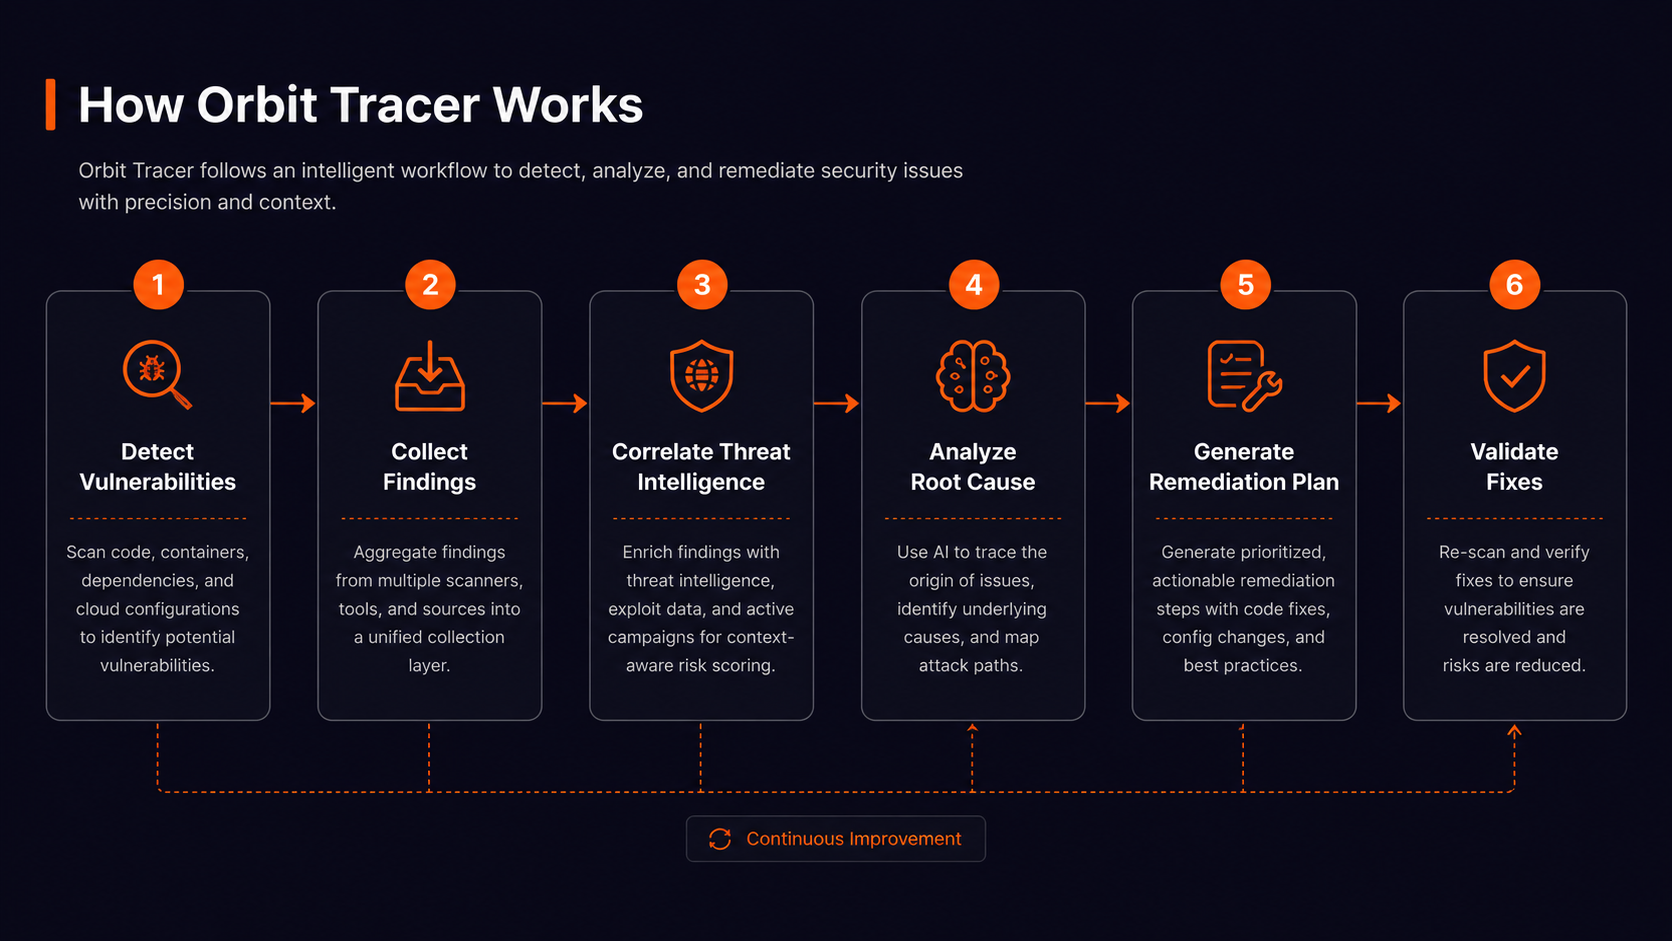
 rajus-agent/orbit-tracer
Orbit Tracer Security Agent for intelligent security remediation. Traces vulnerability blast radius using Orbit's knowledge graph, scores risk,…
 mingchen-script/cve-2020-1472-visualizer
PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
 aqhmal/pulsexploit
Automated script for Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API. You must have a Shodan account to use this…
 trinadh465/platform_external_libvpx_v1.8.0_cve-2023-5217
Patched libvpx codebase addressing CVE-2023-5217 with sanitizer support and cross-platform build configurations for secure VP8/VP9 encoding.
 remenis/cve-2025-63666
Tenda AC15 cookie exposure
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 george0papasotiriou/cve-2026-23008-solidity-assembly-return-data-size-confusion
Educational PoC for Solidity assembly return-data size confusion; includes vulnerable contract, exploit simulation, and mitigation guidance for…
 gmh5225/blackash-cve-2025-0282
Remote code execution exploit for CVE-2025-0282 targeting Ivanti Connect Secure, Policy Secure, and Neurons for ZTA gateways. Uploads a web shell to…
 es0/cve-2019-11510_poc
PoC for CVE-2019-11510 | Pulse Secure 8.1R15.1/8.2/8.3/9.0 SSL VPN - Arbitrary File Disclosure vulnerability
 comparedarray/printix-cve-2022-25090
A "Creation of Temporary Files in Directory with Insecure Permissions" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print…
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…