
badspin
 0xkol/badspin
Bad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)
android-securitybinary-exploitationexploitation+2
0xkol/badspinBad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)
 farazsth98/chronomaly
Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.
 fi01/cve-2015-3636
Proof-of-concept exploit for CVE-2015-3636 targeting 32-bit Android OS kernel privilege escalation.
 markakd/bad_io_uring
Android kernel exploitation for CVE-2022-20409
 retme7/cve-2014-7911_poc
Local root exploit for Nexus5 Android 4.4.4(KTU84P)
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
 michalbednarski/reparcelbug2
Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 lntrx/cve-2021-28663
Proof-of-concept exploit for CVE-2021-28663, a design flaw in the Mali GPU Android kernel driver enabling arbitrary read via memory alias and…
 viralsecuritygroup/knoxout
A PoC of KNOXout (CVE-2016-6584) - bypassing Samsung KNOX protections and root Samsung Galaxy S6 Android Device.
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…
 laginimaineb/cve-2014-7920-7921
Exploit code for CVE-2014-7920 and CVE-2014-7921 - code-exec in mediaserver up to Android 5.1
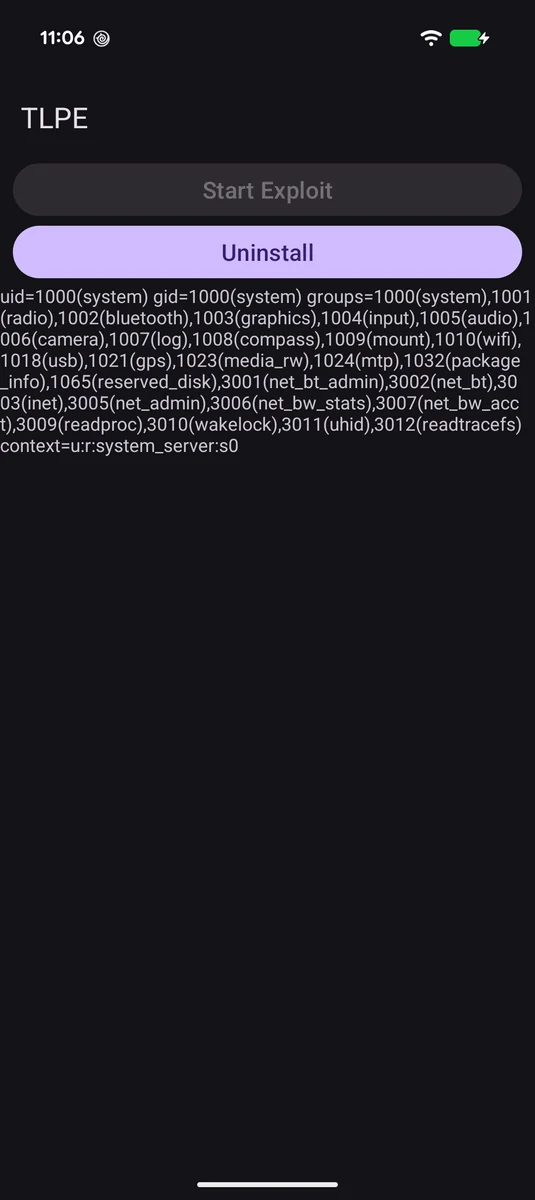 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…