CVE-2021-45428-Defacer

Python-based exploit for CVE-2021-45428, targeting a specific web application vulnerability for penetration testing and security assessment.

Python-based exploit for CVE-2021-45428, targeting a specific web application vulnerability for penetration testing and security assessment.

Exploit for CVE-2024-25600, a web application vulnerability, enabling proof-of-concept testing and security assessment of affected systems.

Ruby-based exploit for CVE-2020-15169, demonstrating a specific web application vulnerability with proof-of-concept code for security testing and…

Exploit for CVE-2021-24499 targeting a specific web application vulnerability. Provides proof-of-concept code for security testing and vulnerability…

Exploit for CVE-2016-4971 targeting a web application vulnerability, providing proof-of-concept code for security testing and validation.

Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data

LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…

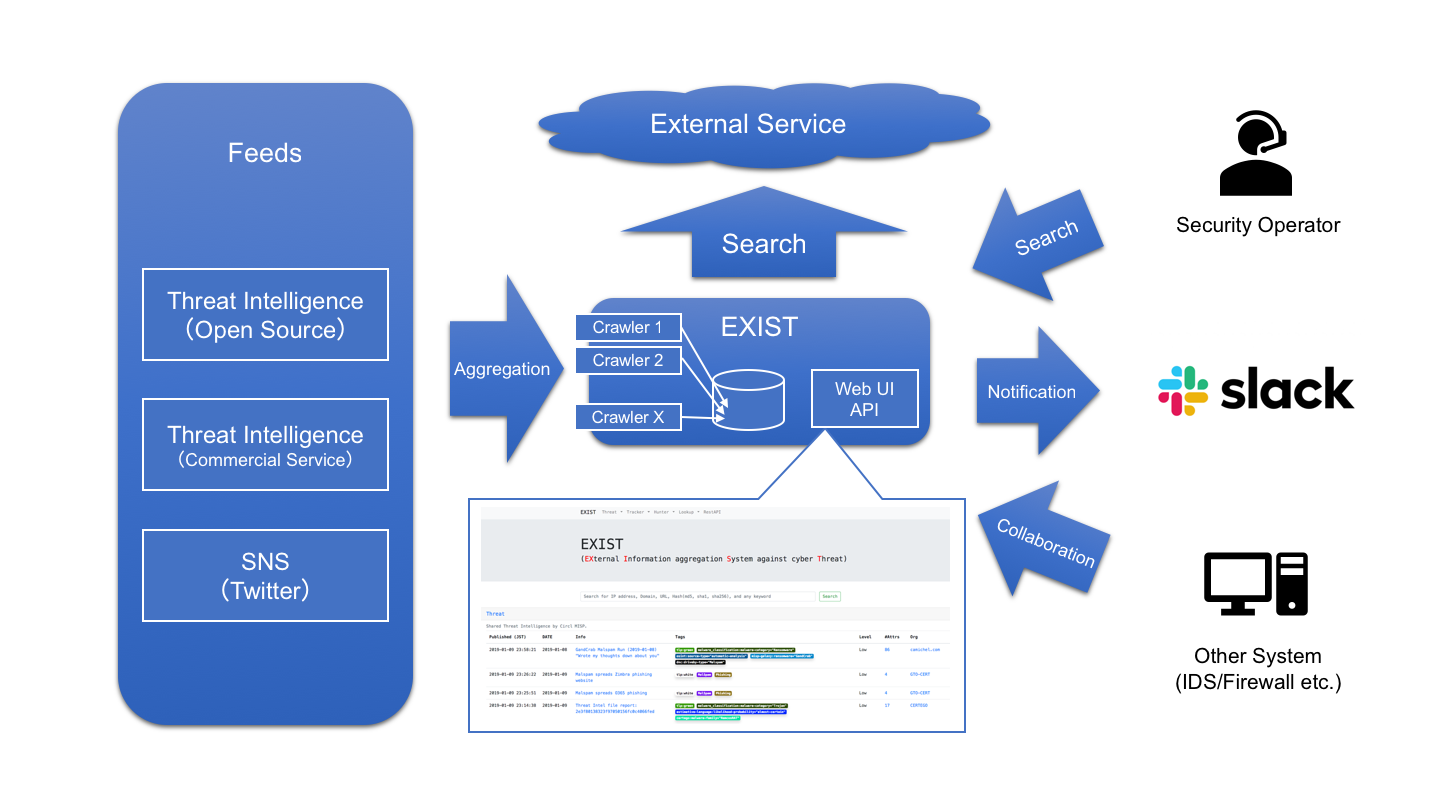
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…

Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…

Proof-of-concept exploit for CVE-2024-24725, demonstrating a web application vulnerability with PHP-based exploitation code for security testing and…

Exploit for CVE-2019-3396 targeting a web application vulnerability. Designed for penetration testing and security assessment of affected systems.

Proof-of-concept exploit for CVE-2021-22145, demonstrating a web application vulnerability with automated exploitation logic for security testing and…

Intentionally vulnerable PHP web app demonstrating SQL injection authentication bypass and unauthorized data disclosure modeled after CVE-2024-8465…

XSS Vulnerability in Rittal

Exploit implementation for CVE-2014-6287, targeting a remote code execution vulnerability in a web application. Provides a proof-of-concept for…

Proof-of-concept exploit for CVE-2023-30800, demonstrating a web application vulnerability with a Go-based payload generator for security testing and…

Proof-of-concept exploit for CVE-2023-42793, targeting a specific web application vulnerability to demonstrate exploitation and aid in security…