
CVE-2010-5301
 lem0nsec/cve-2010-5301
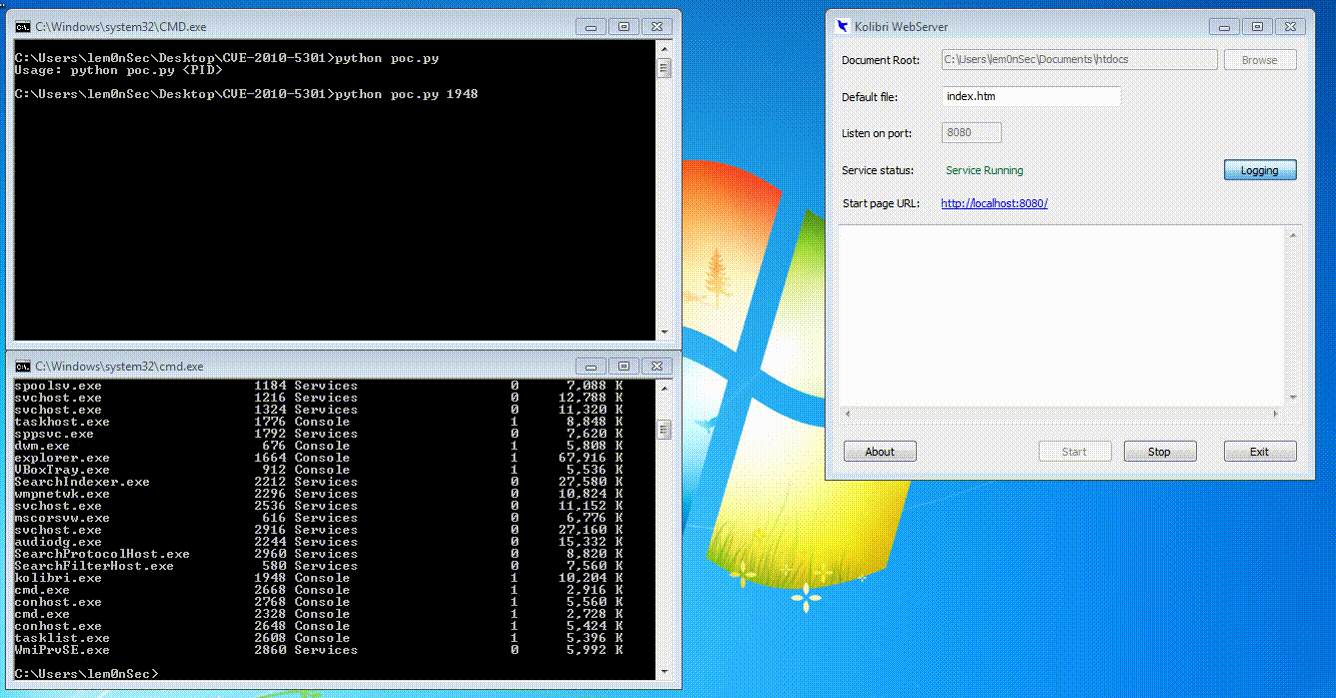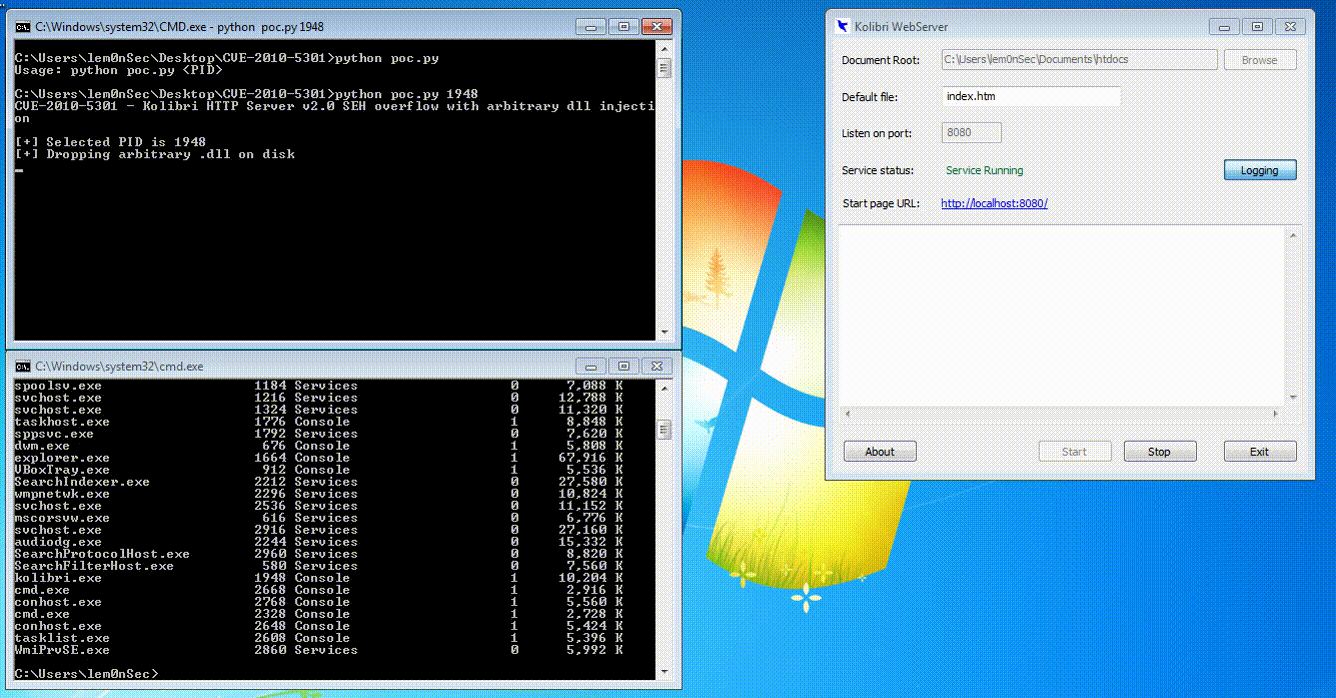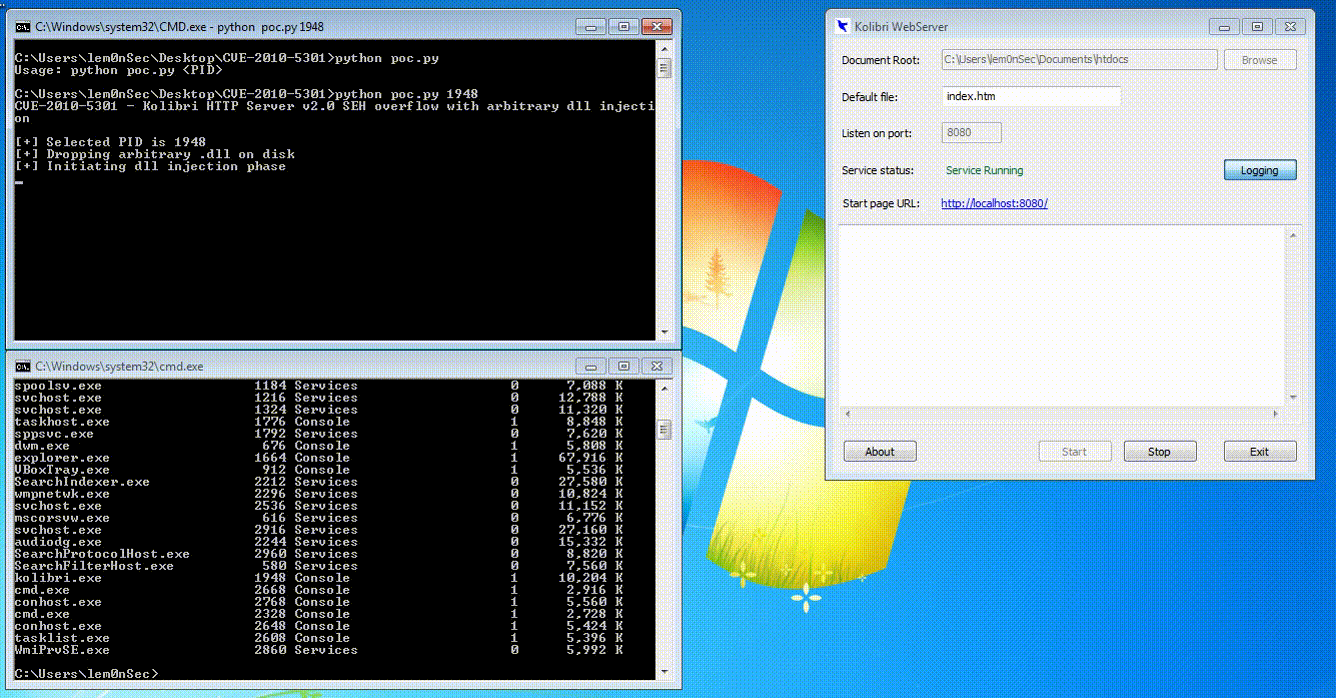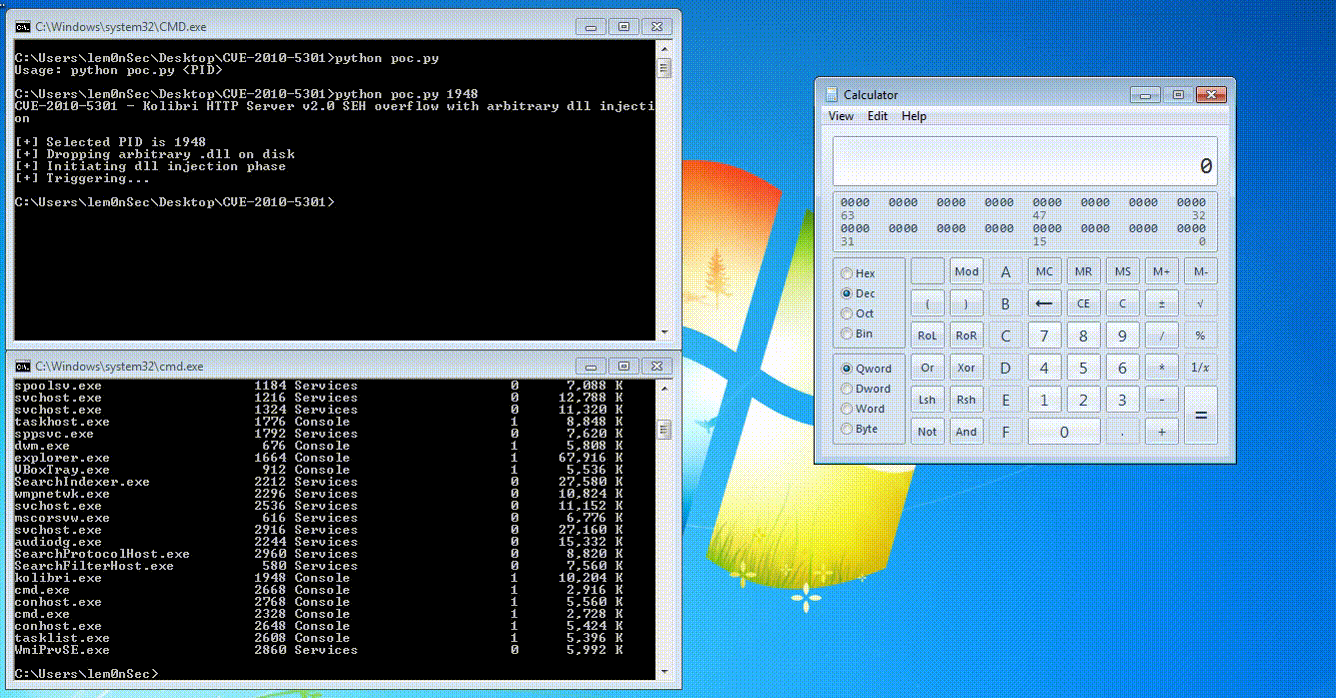
A proof of concept of an SEH overflow with arbitrary dll injection
binary-exploitationexploitationpayload-development+3
24 years ago
lem0nsec/cve-2010-5301A proof of concept of an SEH overflow with arbitrary dll injection
 duyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation
DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
 winter3un/cve-2021-1675
Remote privilege escalation exploit for CVE-2021-1675 (PrintNightmare) with DLL injection and port forwarding support for remote execution.
 metehangenel/mshtml-cve-2021-40444
Automated exploit for CVE-2021-40444 (MSHTML remote code execution) with DLL compilation and deployment via a single bash script.
 evilashz/cve-2021-1675-lpe-exp
PrintNightmare , Local Privilege Escalation of CVE-2021-1675 or CVE-2021-34527
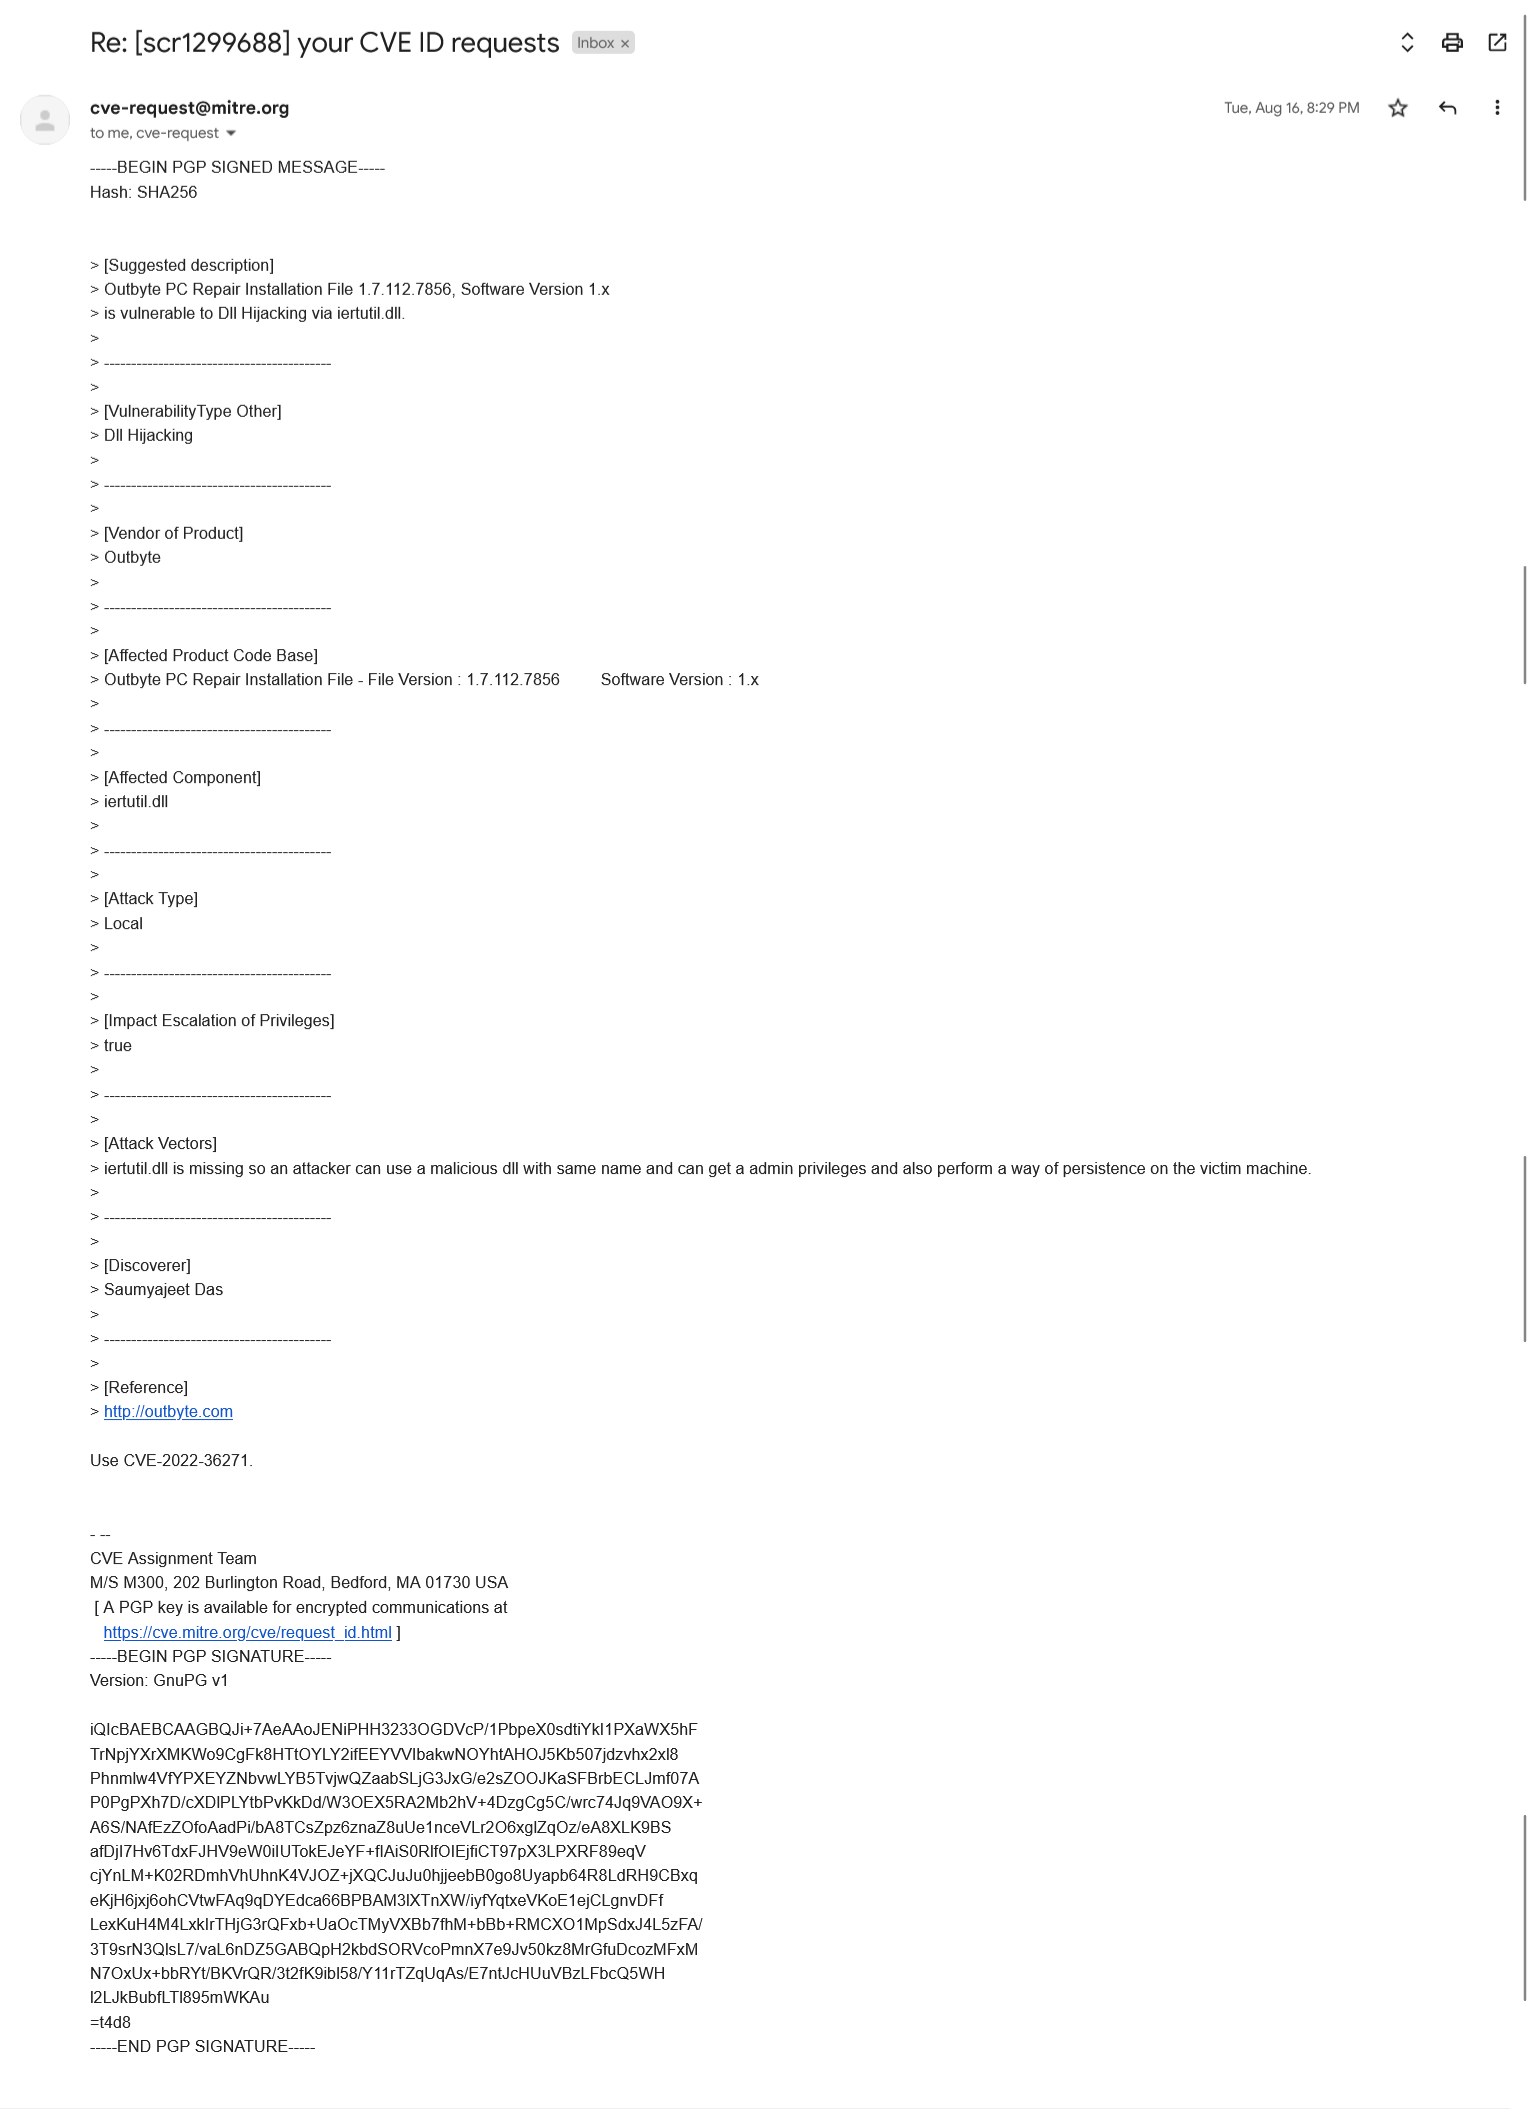 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 pawlokk/qlikview-poc-cve-2024-29863
PoC for LPE with QlikView
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 kobukovui/dll_injection_on_vlc
DLL Injection and CVE-2010-3124