
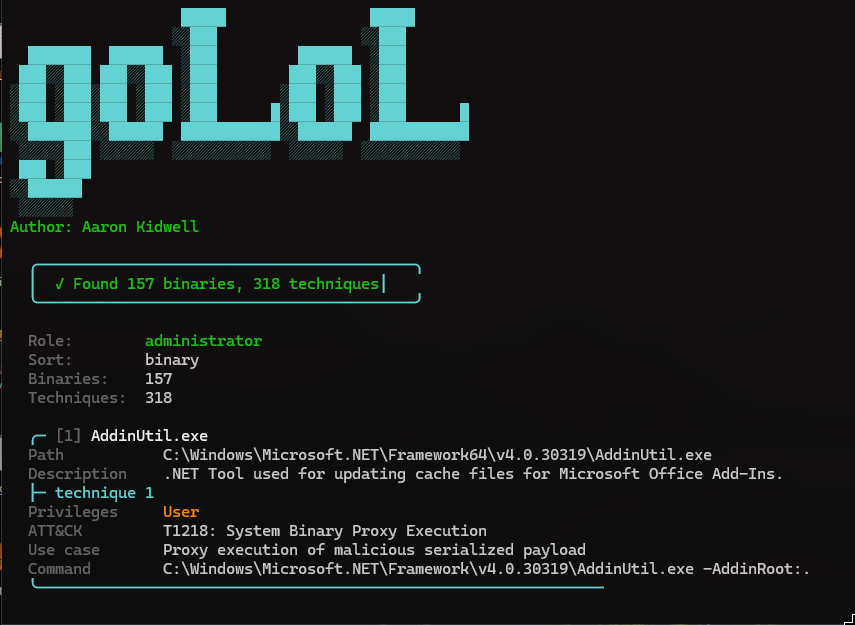
goLoL
 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
binary-analysiseducationinformation-gathering+6
70
aaron-kidwell/gololgoLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
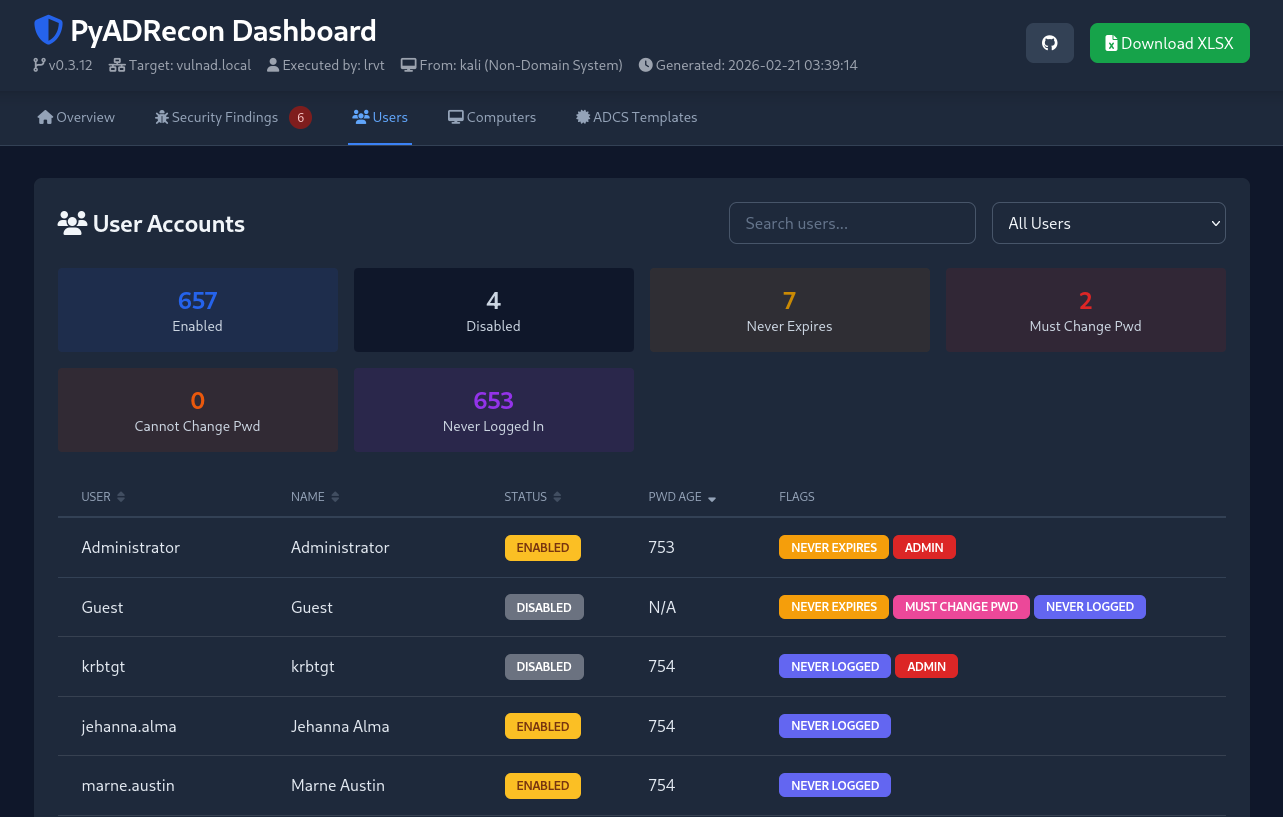 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
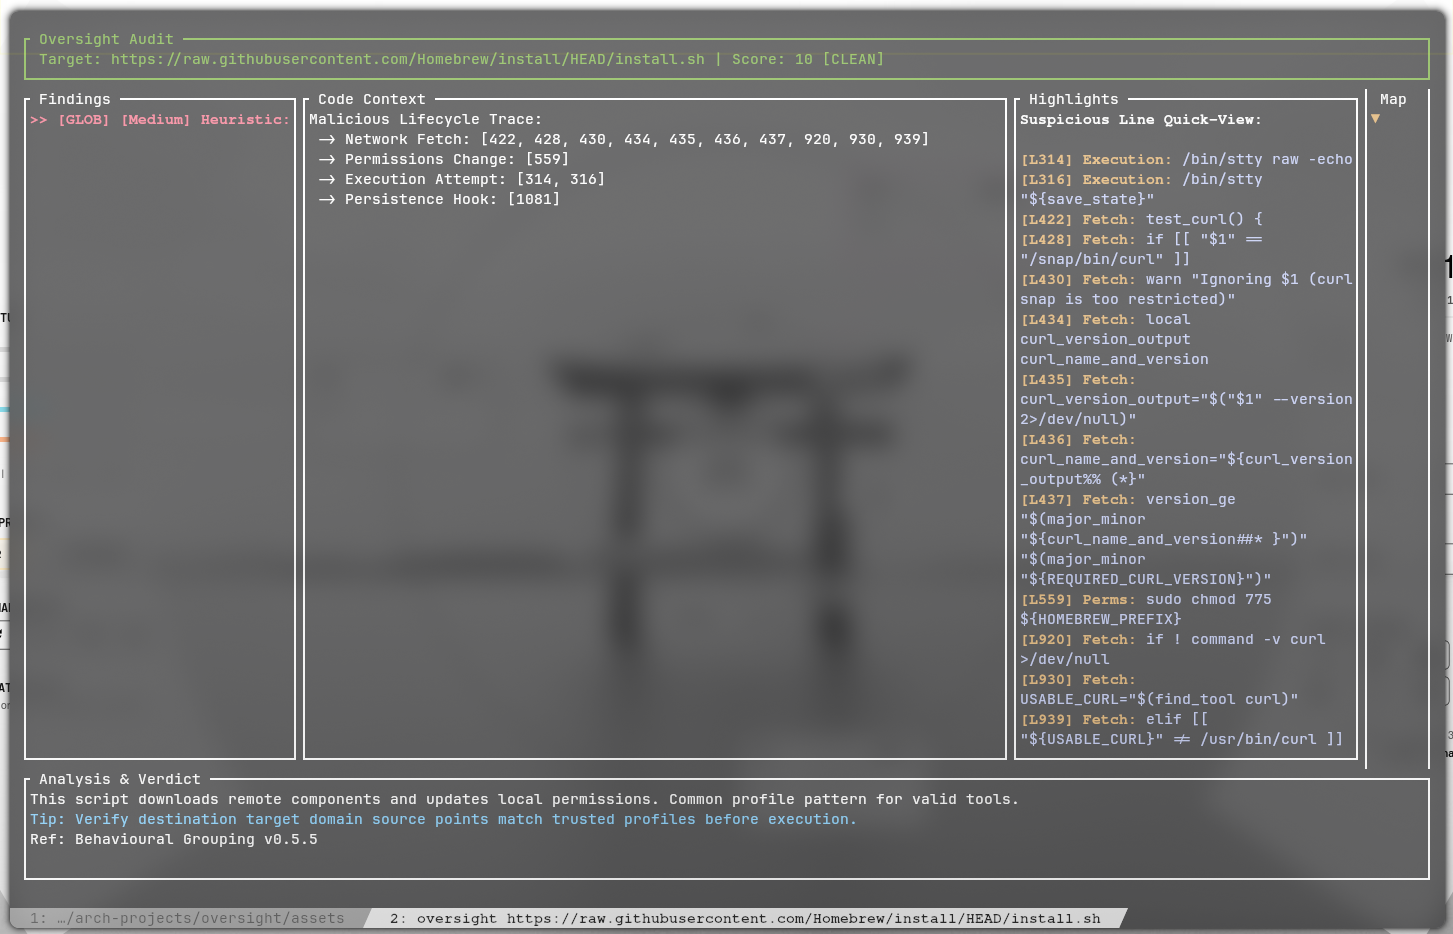 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
 mthbernardes/heimdall_webserver
It's a tool to manage vulnerables packages in your *nix server, in a centralized way
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 fredbrave/cve-2022-46169-cacti-1.2.22
This is a exploit of CVE-2022-46169 to cacti 1.2.22. This exploit allows through an RCE to obtain a reverse shell on your computer.
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
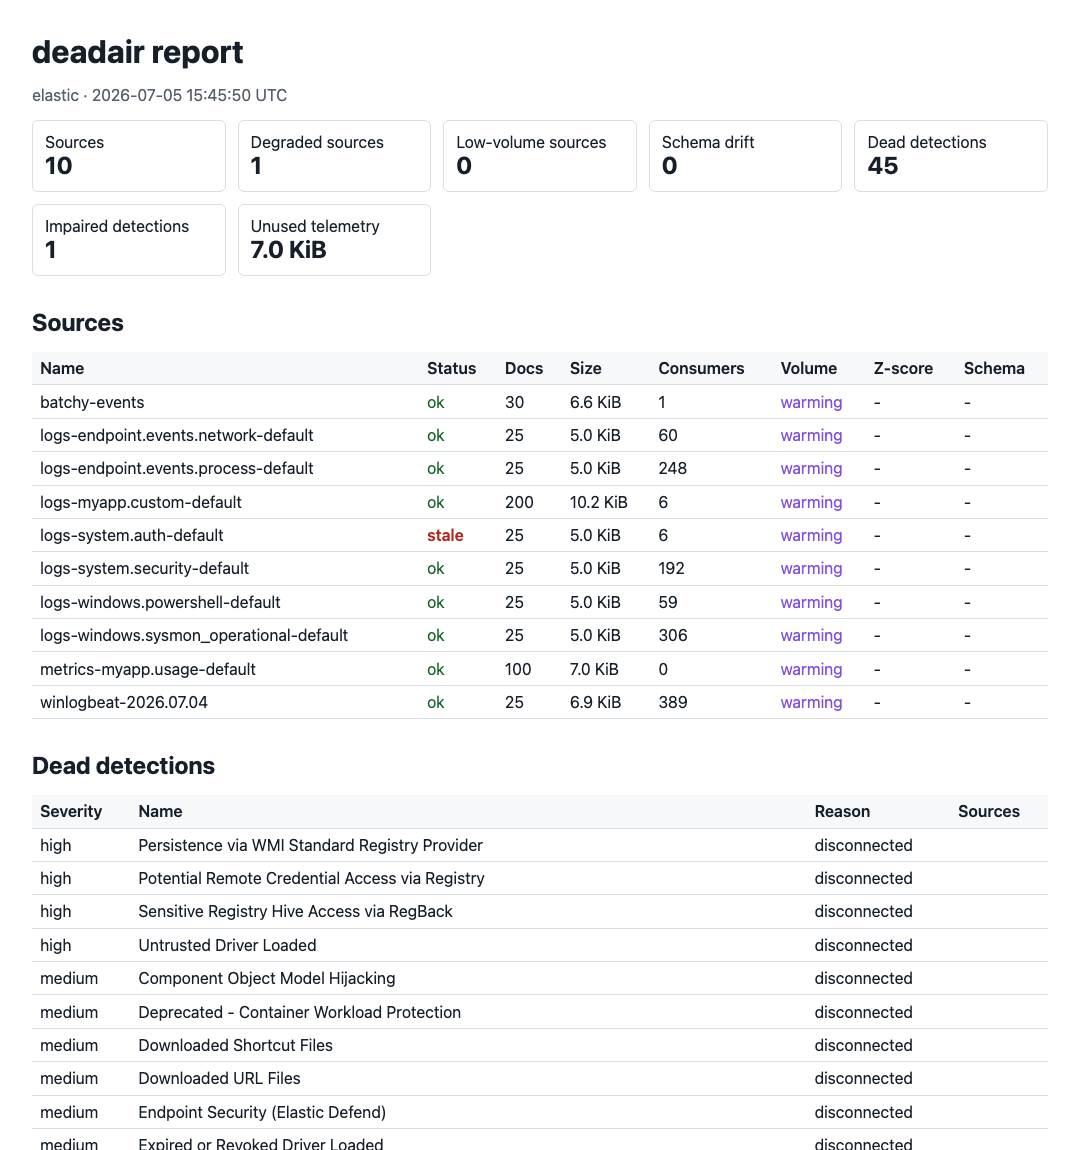 big-comfy/deadair
Finds the detection rules in your SIEM that are running blind
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
 boostedchaos/fleet-cve-scanner
An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…
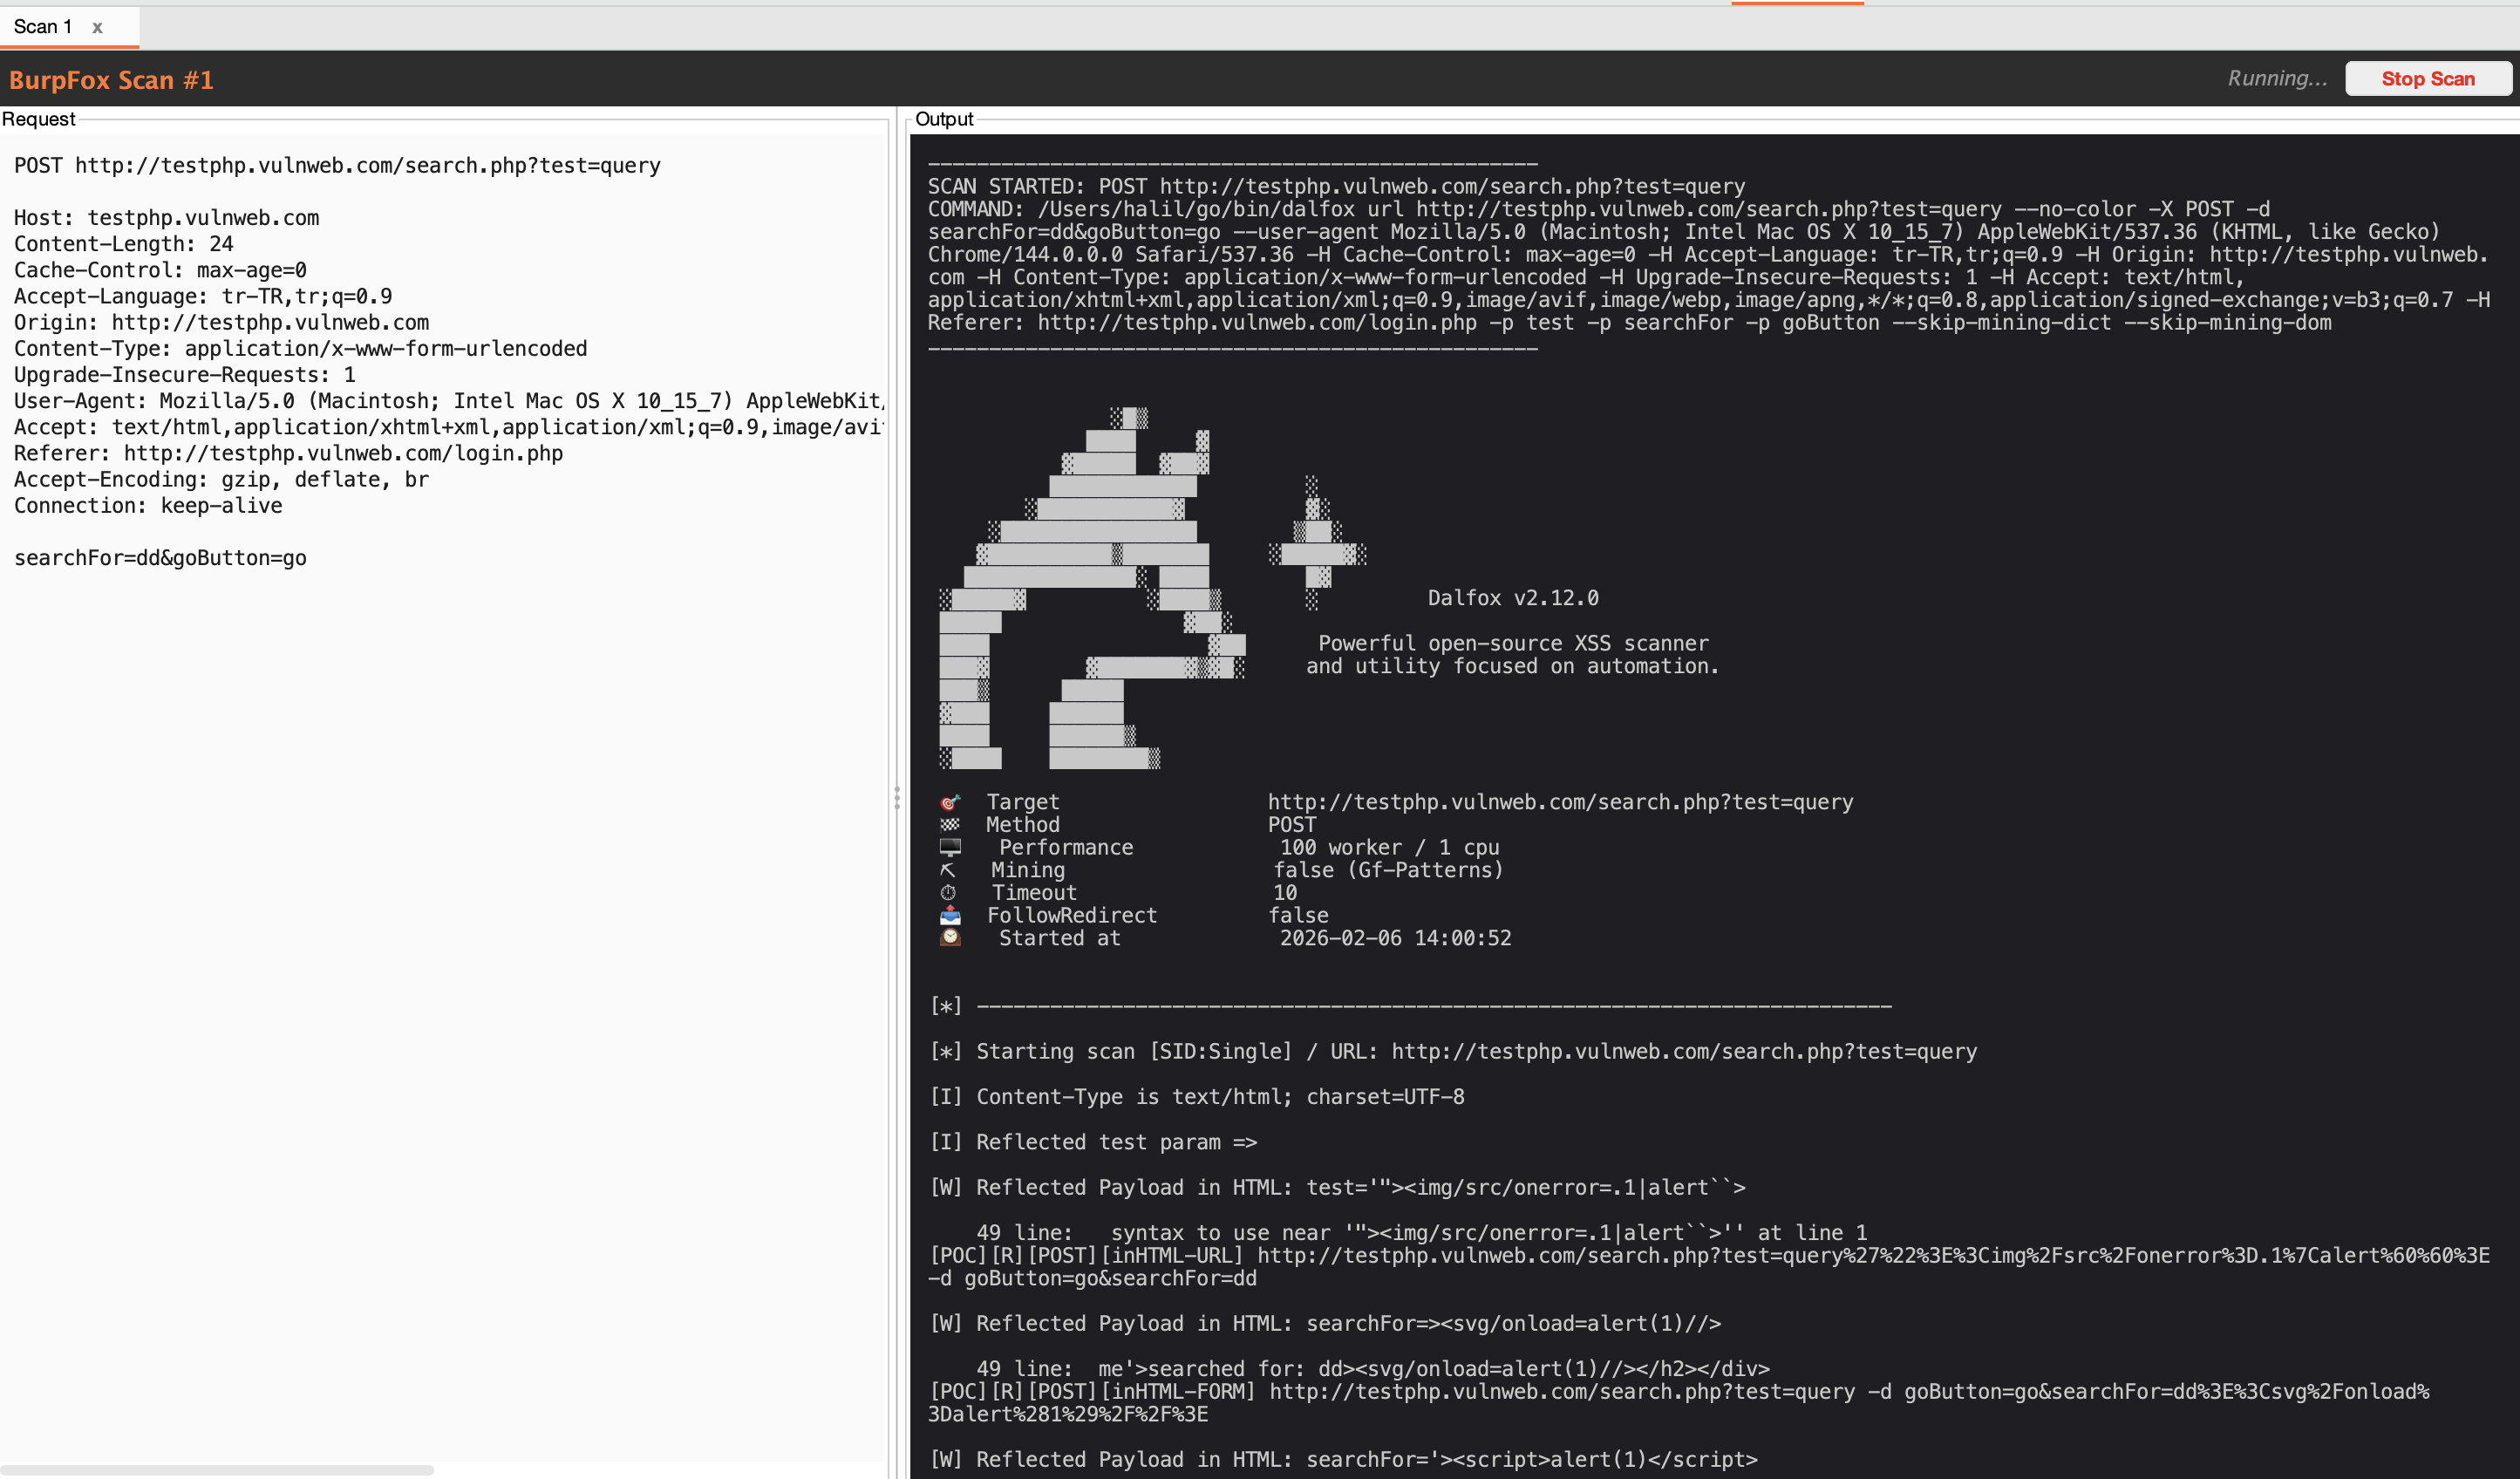 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 geosn0w/pentagram-exploit-tester
A test app to check if your device is vulnerable to CVE-2021-30955
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code