
vulpy
 fportantier/vulpy
Vulnerable Python Application To Learn Secure Development
educationlabs-practicepenetration-testing+2
fportantier/vulpyVulnerable Python Application To Learn Secure Development
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 almogopp/openssh-cve-2024-6387-fix
A Bash script to mitigate the CVE-2024-6387 vulnerability in OpenSSH by providing an option to upgrade to a secure version or apply a temporary…
 r00tpgp/http-pulse_ssl_vpn.nse
Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510
 ets-mse/secure-boot-cert-servicing
Standalone assessment and servicing for the Secure Boot 2011 to 2023 certificate rollover (CVE-2023-24932 / KB5025885). Assess-only by default; no…
 simoesctt/lctt-apple-silicon--resonance-vulnerability-cve-2024-23296
Research on a temporal coherence vulnerability in Apple Silicon M-series chips, exploiting golden ratio harmonic clock frequencies to potentially…
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 salesforce/metabadger
Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 minh3102011/cve-2026-18963_analyst
Docker-based lab for reproducing Keycloak CVE-2026-18963, including vulnerable version setup, realm seeding, and source-level workflow analysis with…
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
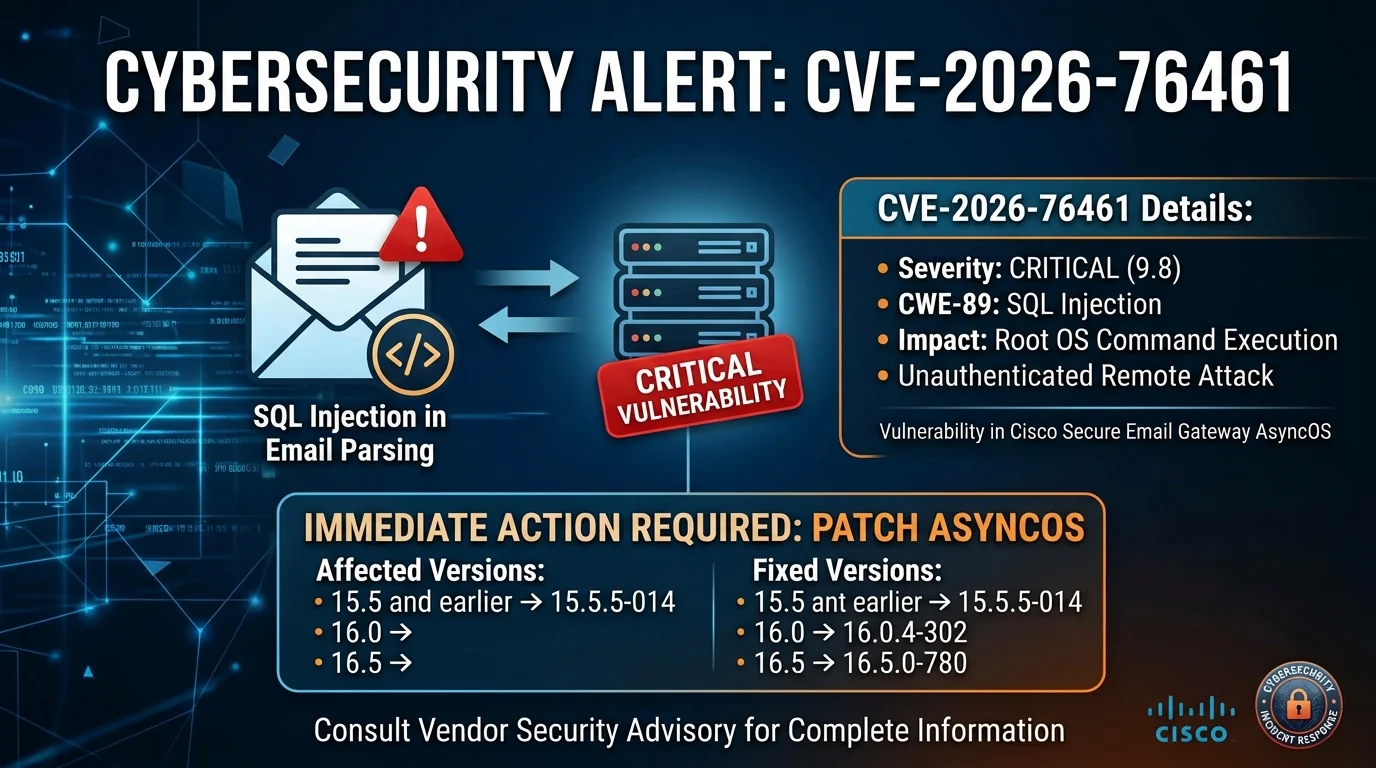 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 duy-31/cve-2023-46805_cve-2024-21887
An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…
 edmondscommerce/cve-2011-2461_magento_patch
Patched Adobe Flex SWF files (editor.swf, uploader.swf, uploaderSingle.swf) to fix the CVE-2011-2461 CSRF vulnerability in Magento. Replace…
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…