
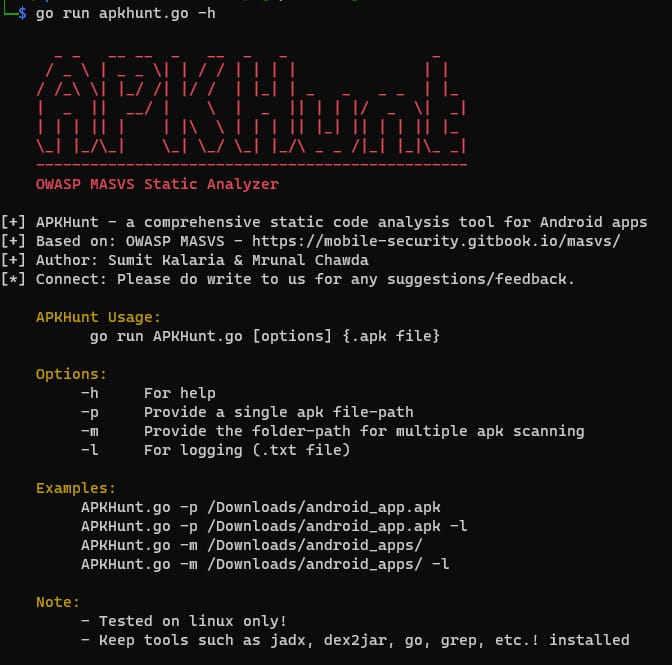
APKHunt
 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
android-securitycode-analysismobile-security+3
987
cyber-buddy/apkhuntStatic code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
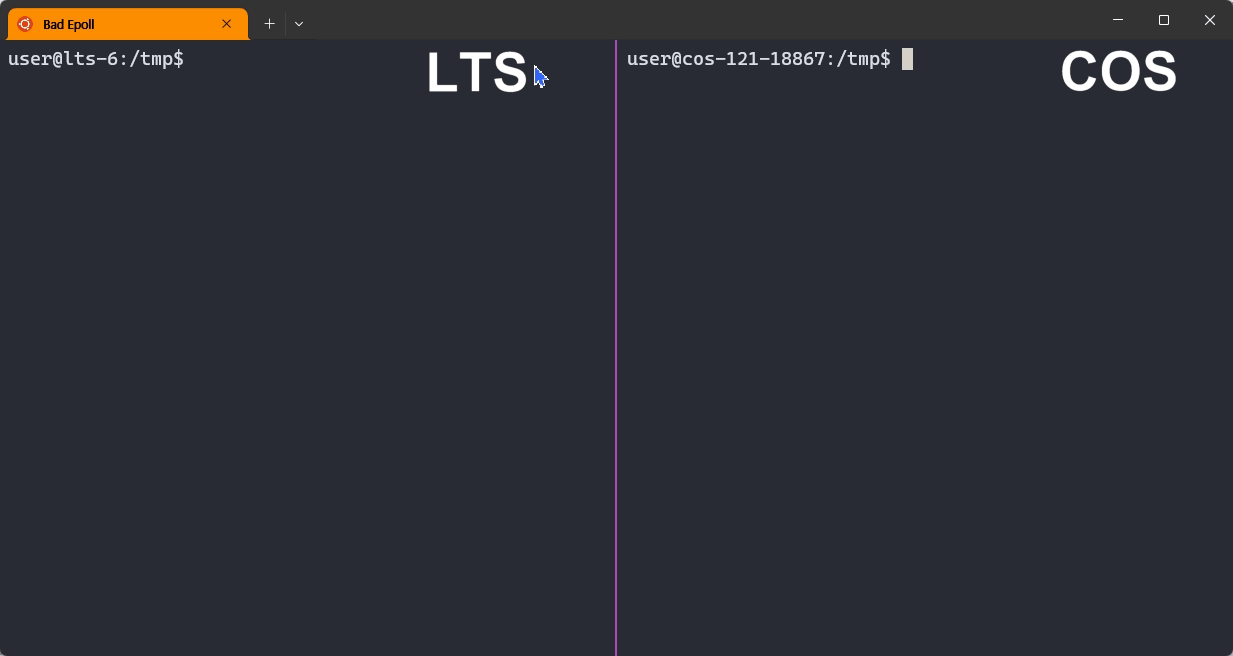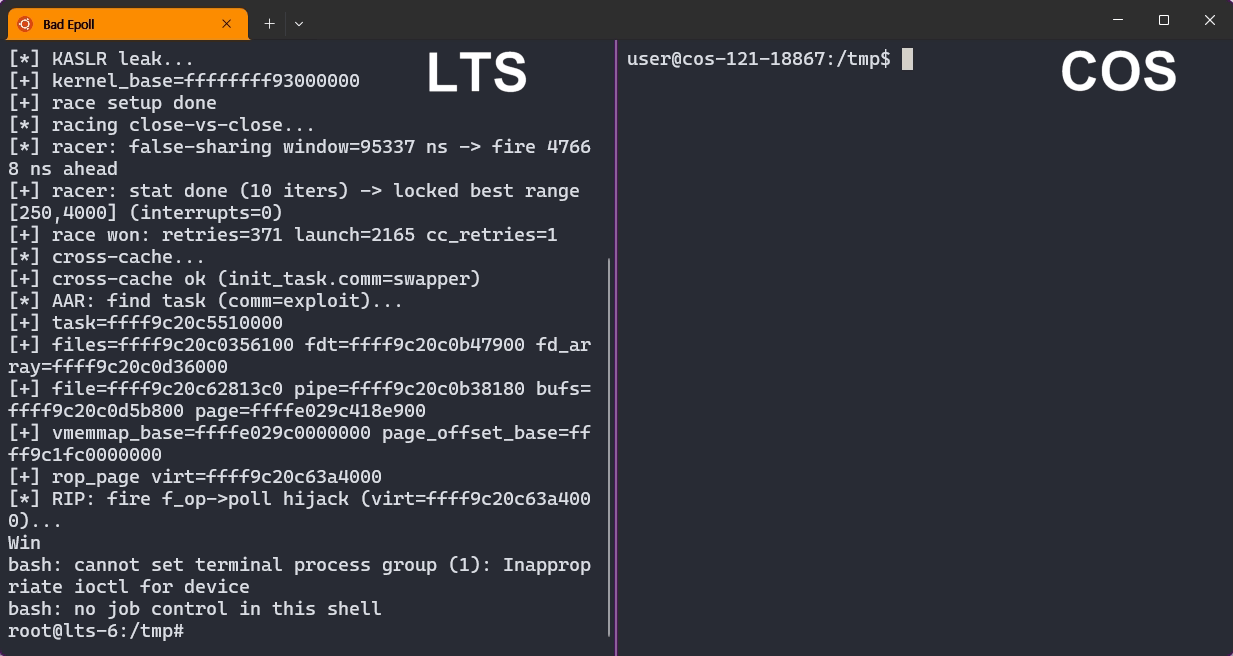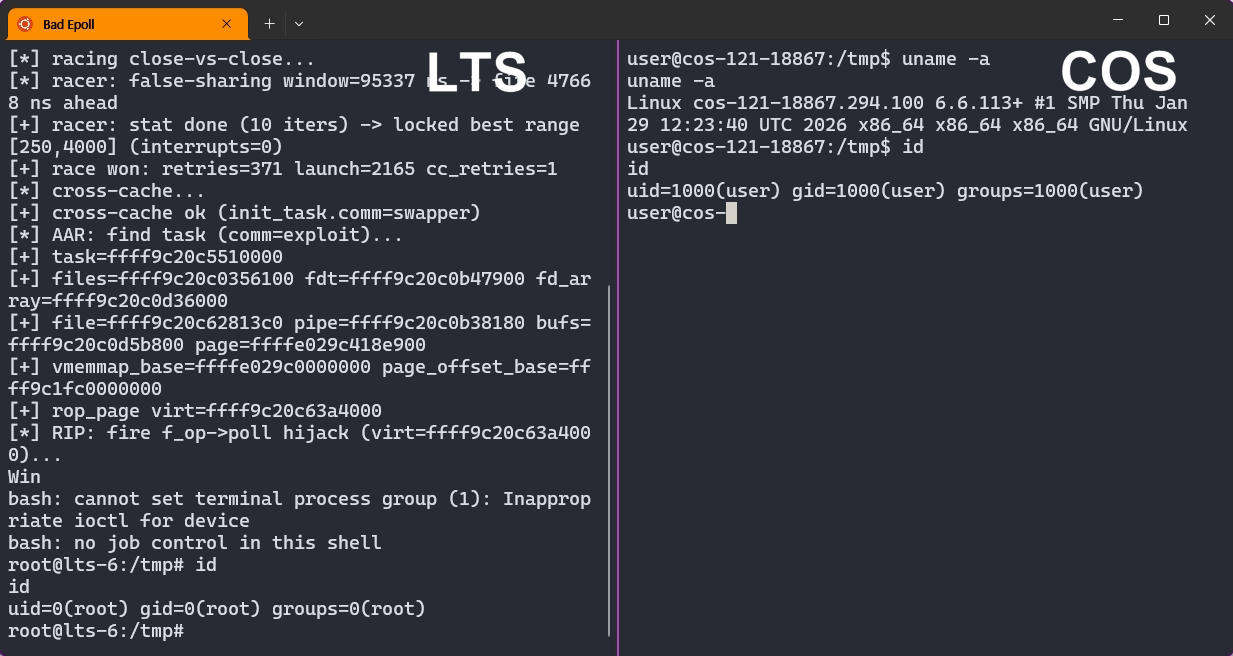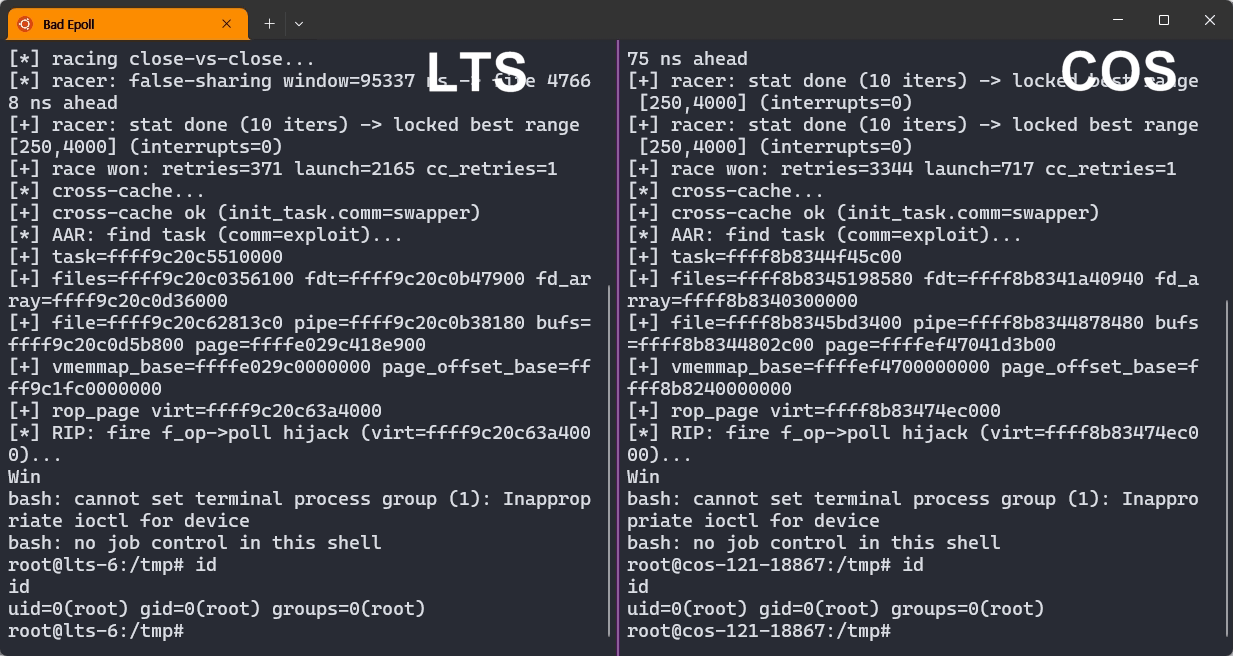 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
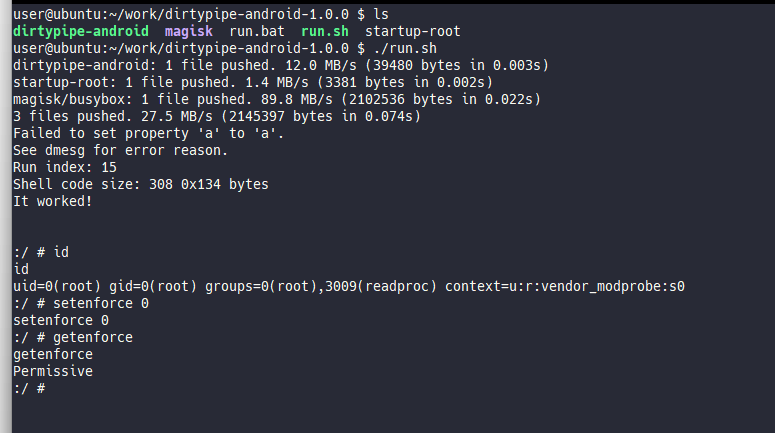 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability
 0x36/pixel_gpu_exploit
Android 14 kernel exploit for Pixel7/8 Pro
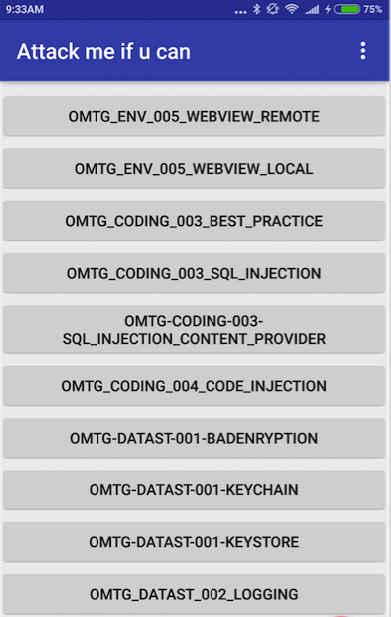 owasp/mastg-hacking-playground
Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…
 davidbuchanan314/nxloader
My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)
 michalbednarski/leakvalue
Exploit for CVE-2022-20452, privilege escalation on Android from installed app to system app (or another app) via LazyValue using Parcel after…
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 bluefrostsecurity/cve-2020-0041
Exploits for Android Binder bug CVE-2020-0041
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…