
Bludit-CVE-2019-17240-Fork
 triple-octopus/bludit-cve-2019-17240-fork
Better version of rastating.github.io/bludit-brute-force-mitigation-bypass/
exploitationpassword-attackspenetration-testing+2
triple-octopus/bludit-cve-2019-17240-forkBetter version of rastating.github.io/bludit-brute-force-mitigation-bypass/
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 saykino/cve-2023-34732
Proof-of-concept exploit for CVE-2023-34732 demonstrating authenticated function abuse in Flytxt NEON-dX to brute-force and reset user passwords,…
 pezwarinaan/cve-2014-0195
Exploit for CVE-2014-0195
 castro-ian/cve-2024-4573-mitigation-script
Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…
 zzzteph/kraker
Kraker is a distributed password brute-force system that focused on easy use.
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 wiire-a/cve-2017-9476
Hidden AP with Deterministic Credentials
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
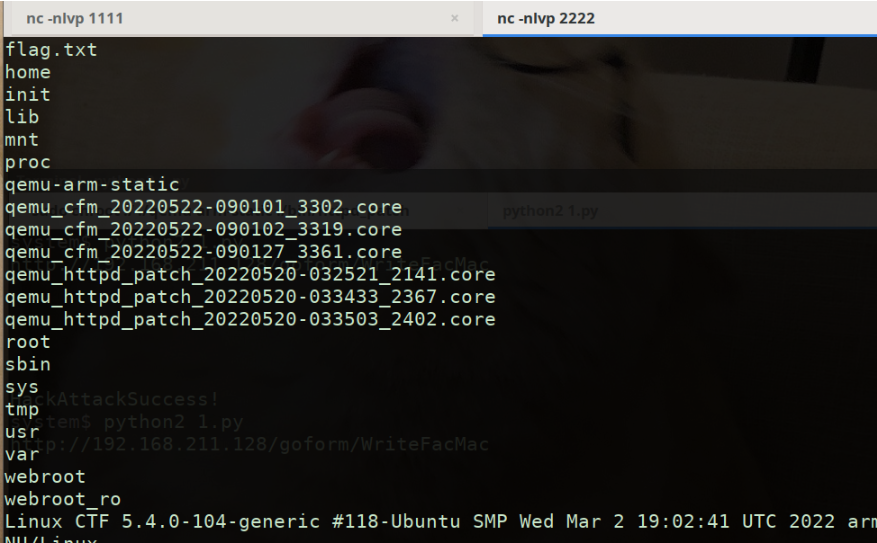 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 kyomahooin/cve-2008-6970
Blind SQL injection brute force.
 1n3/wordpress-xmlrpc-brute-force-exploit
Wordpress XMLRPC System Multicall Brute Force Exploit (0day) by 1N3 @ CrowdShield
 gregscharf/cve-2022-31007-python-poc
elabFTW < 4.1.0 - account lockout bypass and login brute force
 inflixim4be/cve-2020-15392
Proof-of-concept exploit for user enumeration vulnerability in Supravizio BPM 10.1.2 via password recovery response differences, enabling brute force…
 aljoharasubaie/cve-2024-53591
Proof-of-concept for CVE-2024-53591, demonstrating domain enumeration via brute force on Seclore's login page to identify internal services.
 im10n/cve-2024-3183-poc
POC for CVE-2024-3183 (FreeIPA Rosting)
 artemy-ccrsky/cve-2024-39211
User Enumeration vulnerability in Kaiten (workflow management system)