
cve-2023-1671
 csffs/cve-2023-1671
Python-based exploit for CVE-2023-1671 with test and exploitation functions. Tests vulnerability via DNS ping, then executes arbitrary commands on…
command-and-controleducationexploitation+3
csffs/cve-2023-1671Python-based exploit for CVE-2023-1671 with test and exploitation functions. Tests vulnerability via DNS ping, then executes arbitrary commands on…
 al1ex/cve-2020-9470
Wing FTP Server 6.2.5 - Privilege Escalation
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 ludongxu/cve-2015-3636
Proof-of-concept exploit for CVE-2015-3636, a Linux kernel ping socket vulnerability enabling local privilege escalation.
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
 mrowkoob/cve-2025-26466-msf
CVE-2025-26466 - SSH Ping DoS Ruby module for Metasploit Framework
 bytereaper77/cve-2025-7795
Proof-of-concept exploit for a buffer overflow vulnerability in Tenda routers. Sends crafted unauthenticated POST requests to trigger a crash and…
 zarcolio/sitedorks
Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
 mrtdlgc/goodoldsearch-oss
Local static query builder for precise search across web engines, Shodan, crt.sh, and Wayback Machine. Supports Google dorks, filetype filters, date…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 j2ekim/cve-2021-25646
Python exploit for Apache Druid remote code execution vulnerability CVE-2021-25646, enabling command injection via crafted HTTP requests.
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 mehdiledeaut/cve-2026-1281-ivanti-epmm-rce
Proof of Concept for CVE-2026-1281 & CVE-2026-1340 - Ivanti EPMM Pre-Auth RCE via Bash Arithmetic Expansion
 liumuqing/cve-2021-3899_poc
race condition in apport lead to Local Privilege Escalation on Ubuntu
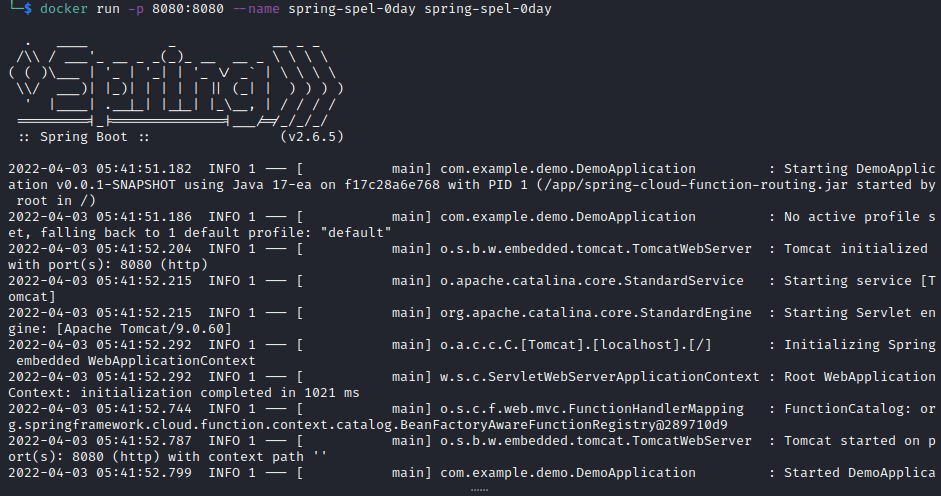 twseptian/cve-2022-22963
Spring Cloud Function SpEL - cve-2022-22963
 shadowgit30/cve-2025-47812
CVE-2025-47812 POC
 maxime288/cve-2026-8838-rce
Educational PoC for CVE-2026-8838, a critical RCE vulnerability in Amazon Redshift Python Driver via unsafe eval() in vector_in(). Includes technical…