
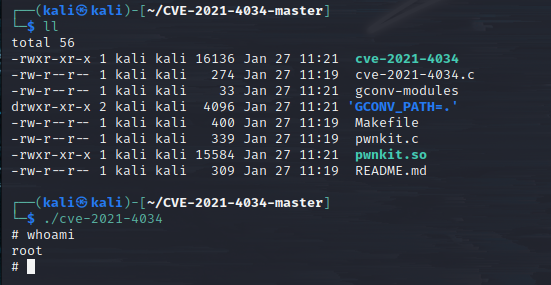
CVE-2021-4034
 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
binary-exploitationexploitationexploit-frameworks+2
2
locksec/cve-2021-4034Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 kernelpan1k/trans2open-cve-2003-0201
Samba exploit CVE2003-0201
 julichaan/cve-2026-31431-python-copyfail-poc
Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 anonymous-family/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) in Polkit's pkexec, providing local privilege escalation to root on Linux systems. Includes build instructions and…
 h1d3r/copy-fail_lpe_interactive
Exploit for CVE-2026-31431, a Linux kernel page cache corruption vulnerability, providing interactive root shell and non-interactive command…
 rosnlr5/modrosnlr5
Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…
 simoesctt/ctt-enhanced-px4-autopilot-exploit-cve-2026-32743
Exploit for CVE-2026-32743, a stack buffer overflow in PX4 Autopilot's MavlinkLogHandler, delivering a persistent denial-of-service via a 33-layer…
 ethanevans92/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo. Demonstrates chroot-based NSS manipulation to load a malicious…
 rat5ak/cve-2026-31431-copyfail-static-elf--poc
Minimal 587-byte static ELF exploit for CVE-2026-31431, achieving local privilege escalation via AF_ALG splice page cache corruption. No libc or…
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 isw-9/copy-fail-cve-2026-31431-aarch64
Python exploit for CVE-2026-31431 targeting aarch64, verified on Ubuntu 25.10. Executes the provided script to trigger the vulnerability.
 fangfang-yi/cve-2024-30088
C++ exploit for CVE-2024-30088, providing a proof-of-concept implementation for testing and analyzing this specific Windows kernel privilege…
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 uname1able/cve-2026-24291
Proof-of-concept exploit for CVE-2026-24291 targeting Windows 10 21H2 (build 19044.6937) AMD64, developed in C# with Visual Studio 2022.