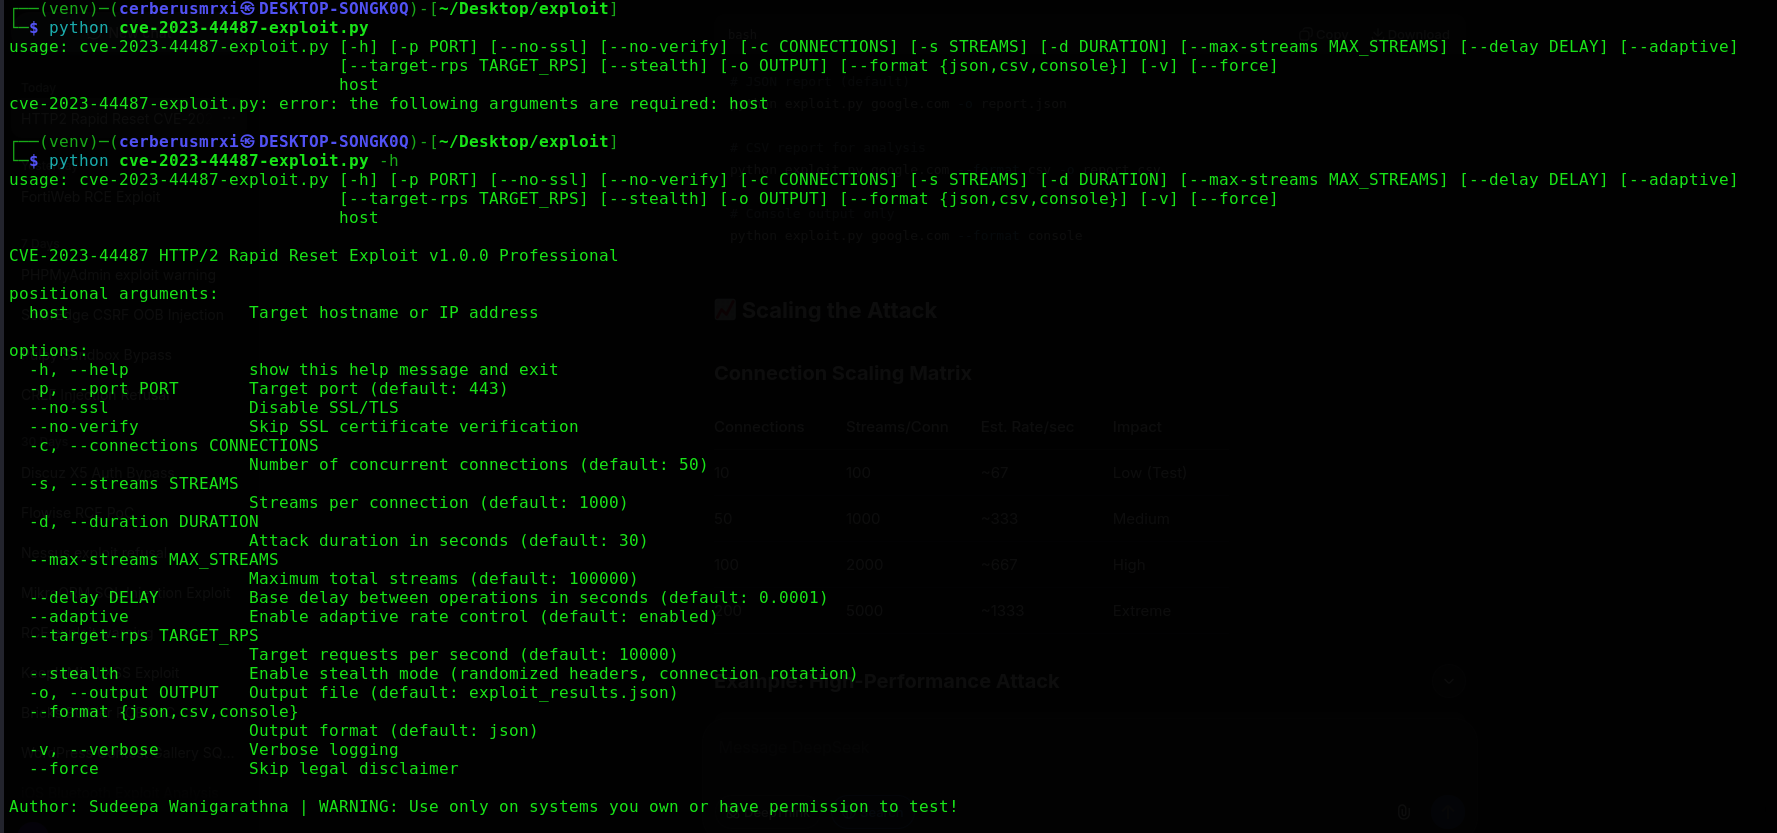
CVE-2023-44487-HTTP2-DoS-Rapid-Reset-Exploit

Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…

Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…

Local privilege escalation exploit for Fortinet FortiClientLinux, exploiting a symlink following vulnerability to gain root access on affected…

Go-based exploit for CVE-2026-31431, a local privilege escalation vulnerability, that modifies /usr/bin/su to gain root access on Linux distributions.

dnsmasq rop exploit with NX bypass

CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)

PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…

Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…

Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.

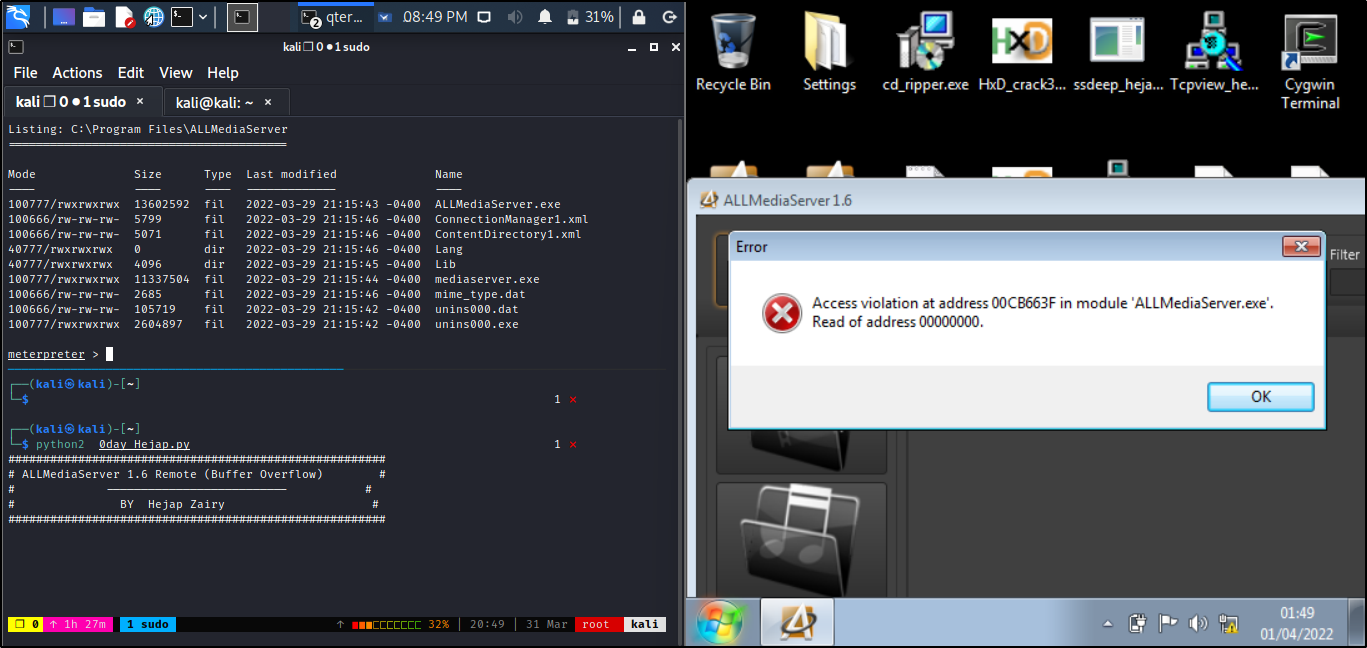
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.

Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…

Proof-of-concept exploit for CVE-2026-31431, a Linux local privilege escalation via authencesn logic bug, with ARM64 variant for authorized lab…

C implementation of a proof-of-concept exploit for CVE-2026-31431, demonstrating the vulnerability and providing a compile-and-run exploit for…

Python exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG and splice() to write to page cache, gaining root on arm64…

Standalone exploit for CVE-2017-16995, a Linux kernel local privilege escalation vulnerability, providing a ready-to-use proof-of-concept for…

Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.

Exploit implementation for CVE-2026-43499, providing a targeted proof-of-concept for vulnerability verification and security assessment.

Proof-of-concept exploit for CVE-2023-1281, a use-after-free vulnerability in the Linux kernel traffic control index filter (tcindex), demonstrating…

CVE-2020-17136 exploit