

 meridianlabs-ai/inspect_petri
An alignment auditing agent capable of quickly exploring alignment hypothesis

 k3ystr0k3r/cve-2021-43798-exploit
A PoC exploit for CVE-2021-43798 - Grafana Directory Traversal
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 rxerium/n8n-vulnerability-detection
Vulnerability detection scripts for the n8n product.
 antisecc/cve-2022-46169
Exploit for CVE-2022-46169 in Cacti, enabling unauthenticated remote code execution via crafted HTTP requests to remote_agent.php.
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
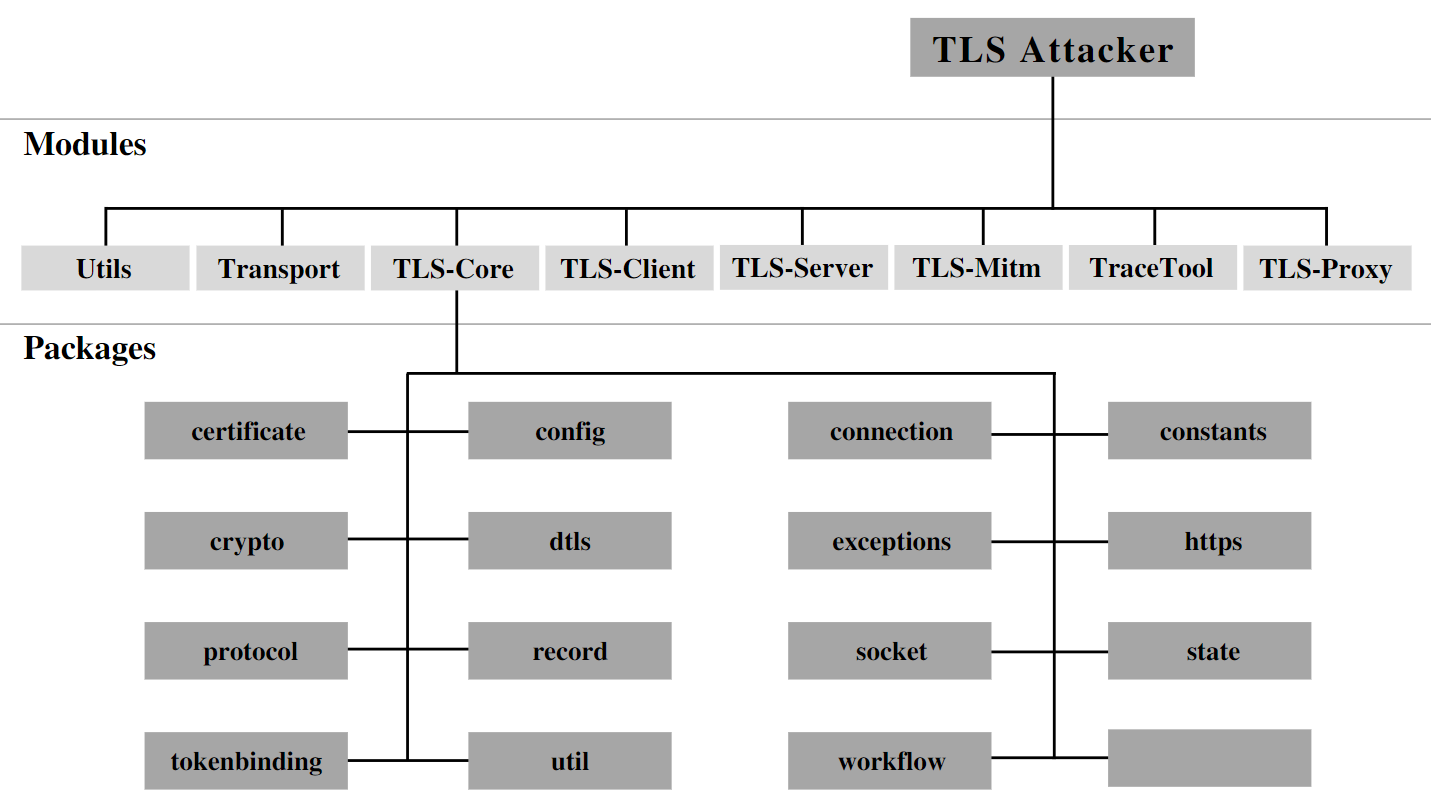 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 m0nad/hellraiser
Vulnerability scanner using Nmap for scanning and correlating found CPEs with CVEs.
 cisco-talos/mutiny-fuzzer
Network protocol fuzzer that replays PCAP traffic through a mutational engine (Radamsa) to quickly discover vulnerabilities in target hosts via…
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
 xen0vas/vscan
vulnerability scanner tool using nmap and nse scripts
 advanced-threat-research/cve-2020-16898
CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 rub-softsec/onelogon
Code and data for our paper "Onelogon: Taking over Active Directory Accounts via Netlogon" (WOOT’26).