
CVE-2018-1000861
 smokeintheshell/cve-2018-1000861
CVE-2018-1000861 Exploit
command-and-controlexploitationpenetration-testing+3
smokeintheshell/cve-2018-1000861CVE-2018-1000861 Exploit
 wickddavid/cve-2021-26814
A simple python PoC to exploit CVE-2021-26814 and gain RCE on Wazuh Manager (v.4.0.0-4.0.3) through the API service.
 anubissec/cve-2019-16278
A quick python exploit for the Nostromo 1.9.6 remote code execution vulnerability. Simply takes a host and port that the web server is running on.
 cys4srl/cve-2021-26814
PoC of CVE-2021-26814
 cowbe0x004/eximrce-cve-2019-10149
simple python socket connection to test if exim is vulnerable to CVE-2019-10149. The payload simply touch a file in /tmp/eximrce.
 b1d0ws/exploit-cve-2018-7448
Python script for CMS Made Simple 2.1.6 - Remote Code Execution.
 alexander-fernandes/cve-2019-16278
A quick python exploit for the Nostromo 1.9.6 remote code execution vulnerability. Only takes in host and port of web server as required arguments.
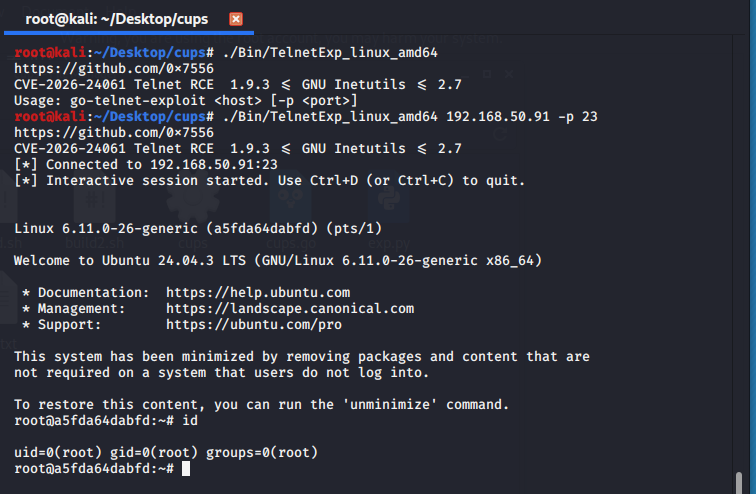 0x7556/cve-2026-24061
Cross-platform remote code execution exploit for GNU Inetutils telnet (versions 1.9.3 to 2.7), targeting CVE-2026-24061 with a simple command-line…
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 blipzip/cve-2022-31692
A project demonstrating an app that is vulnerable to Spring Security authorization bypass CVE-2022-31692
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
 maleeshaudan/wordpress-cve-2024-10924--exploit
WordPress CVE-2024-10924 Exploit for Really Simple Security plugin
 geozin/poc-cve-2018-25031
Proof-of-concept exploit for CVE-2018-25031 (Swagger UI XSS) that exfiltrates authorization codes via crafted configUrl/url parameters.
 nattisamson/serv-u-cve-2021-35211
Simple Serv-U CVE-2021-35211 PoC
 unknowndevice64/exploits_cve-2019-19781
Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…
 sharphack/cve-2019-19781
Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781) that executes arbitrary commands on vulnerable…