schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…

Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…

TP-Link Archer AXE75 Authenticated Command Injection

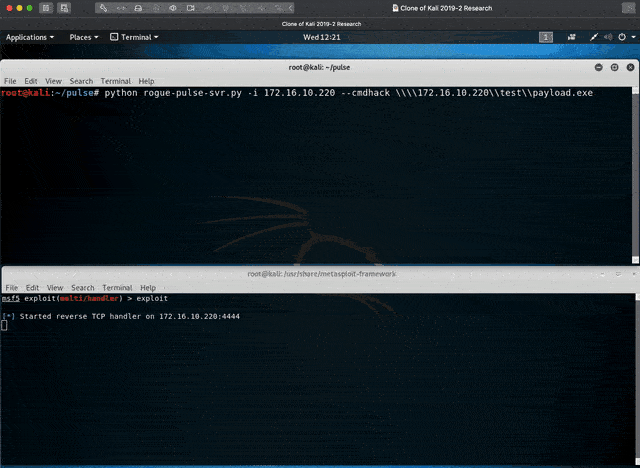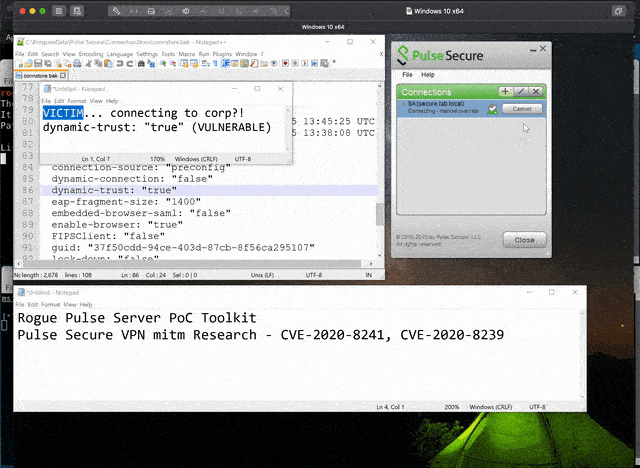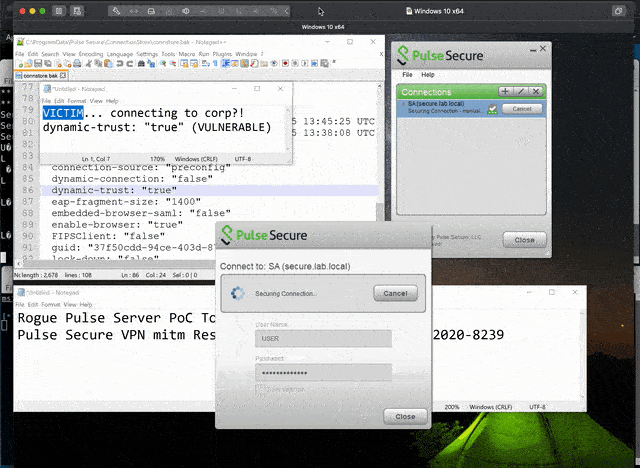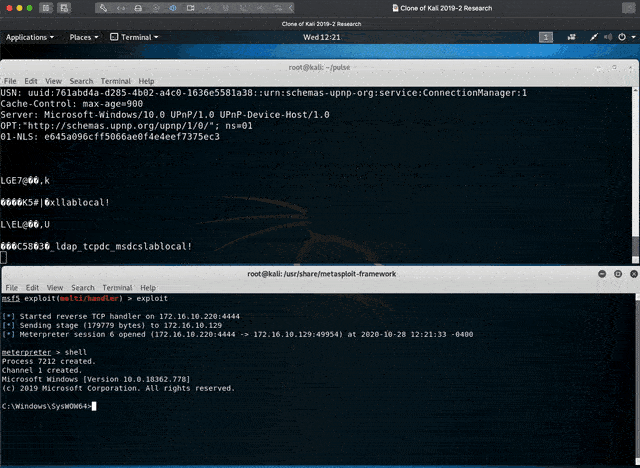
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239

CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client

CVE-2021-3449 OpenSSL denial-of-service exploit 👨🏻💻

PoC for CVE-2025-20265 Cisco Secure FMC Software RADIUS Remote Code Execution Vulnerability

Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…

CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…

Detection and mitigation scripts for CVE-2026-8838, providing vulnerability scanning, configuration auditing, and incident response guidance to…

A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…

Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…

One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️

baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability

This is a container of web applications that work with OWASP Bug Bounty for Projects

PoC

Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.

Parses the System Snapshot from an Ivanti Connect Secure applicance to identify possible IOCs related to CVE-2023-46805, CVE-2024-21887 and…

Exploit for CVE-2019-11510 targeting Pulse Secure VPN to perform unauthenticated arbitrary file reading and potential credential disclosure.