
suricata-rule-CVE-2025-53770
 nisargsuthar/suricata-rule-cve-2025-53770
Detection rules for CVE-2025-53770
exploitationids-ips-evasionintrusion-detection+3
nisargsuthar/suricata-rule-cve-2025-53770Detection rules for CVE-2025-53770
 duo-labs/mysslstrip
Proof-of-concept tool demonstrating MITM attack to strip SSL/TLS from MySQL connections, exploiting CVE-2015-3152 for network penetration testing.
 insomnisec/detections-cve-2026-23918
Detection rules for CVE-2026-23918 Apache http2 RCE - Credit: stringa.ai, isec.pl
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
 regit/opensvp
Opensvp is a security tool implementing "attacks" to be able to test the resistance of firewall to protocol level attack.
 drk1wi/portspoof
Emulates open ports and service signatures across all 65535 TCP ports to slow reconnaissance, confuse scanners, and waste attacker resources with…
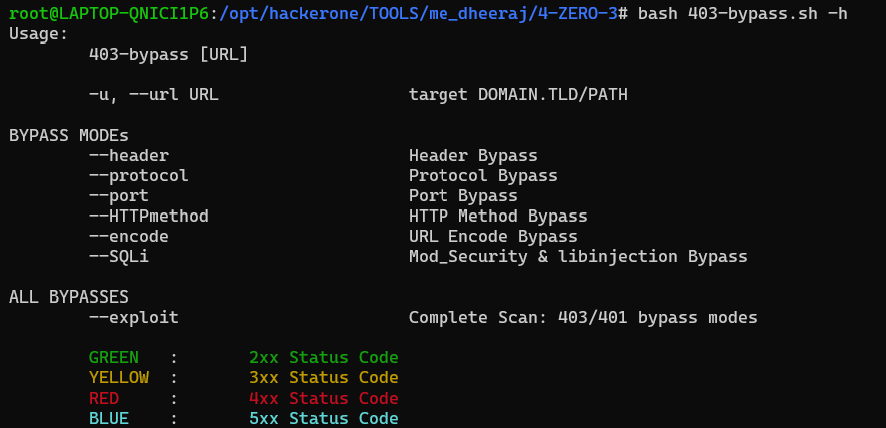 dheerajmadhukar/4-zero-3
403/401 Bypass Methods + Bash Automation + Your Support ;)
 garagehq/nightcrawler
Local AI powered red teamer on a phone
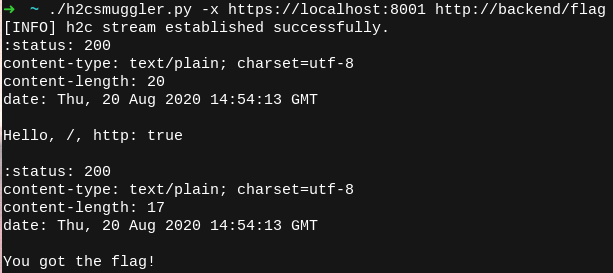 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
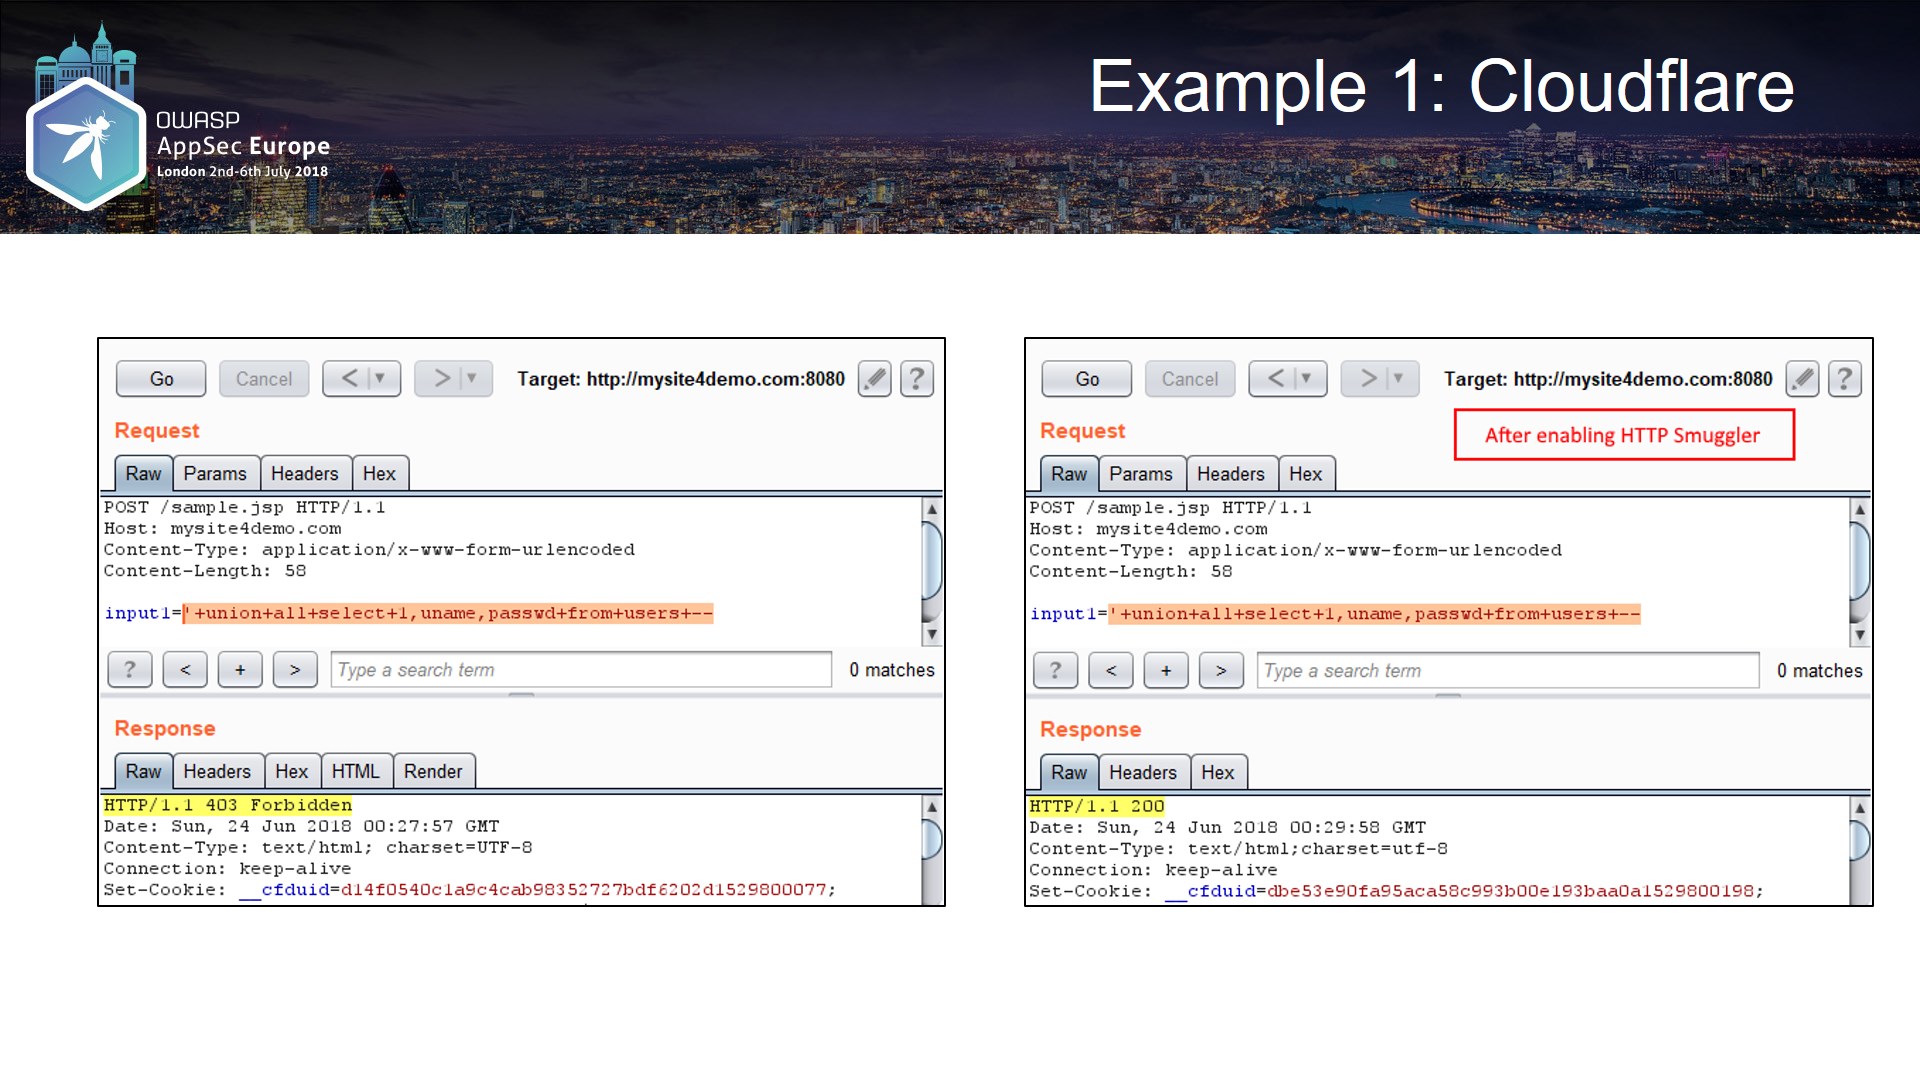 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.
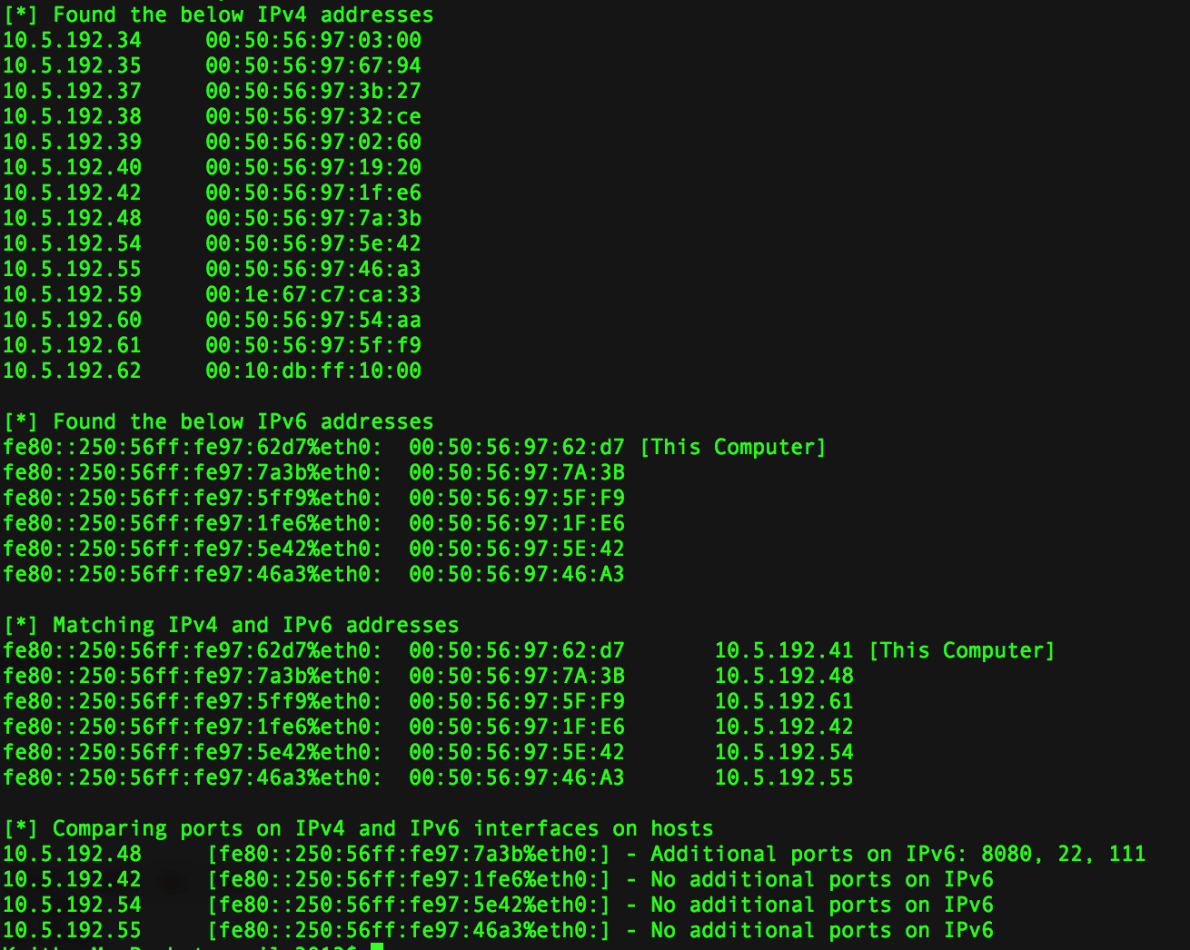 milo2012/ipv4bypass
Using IPv6 to Bypass Security
 zeronetworks/zerologon
Test script for CVE-2020-1472 for both RPC/TCP and RPC/SMB
 toperaproject/topera
IPv6 analysis tool: the other side
 synacktiv/amsi-bypass
Lists of AMSI triggers (VBA, JScript / VBScript)