gitlab-webhook-0net-ssrf

Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…

Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…

Exploit for CVE-2024-32002, providing a proof-of-concept hook for vulnerability verification and penetration testing.

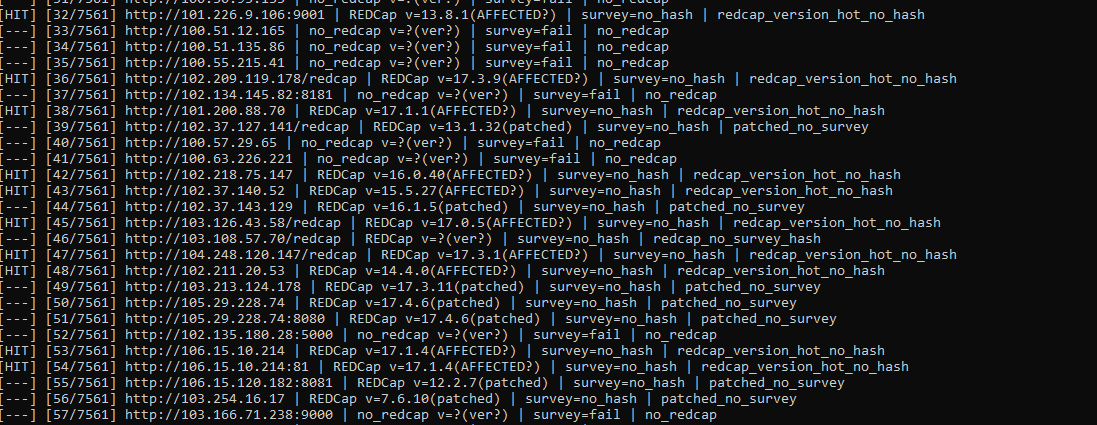
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…

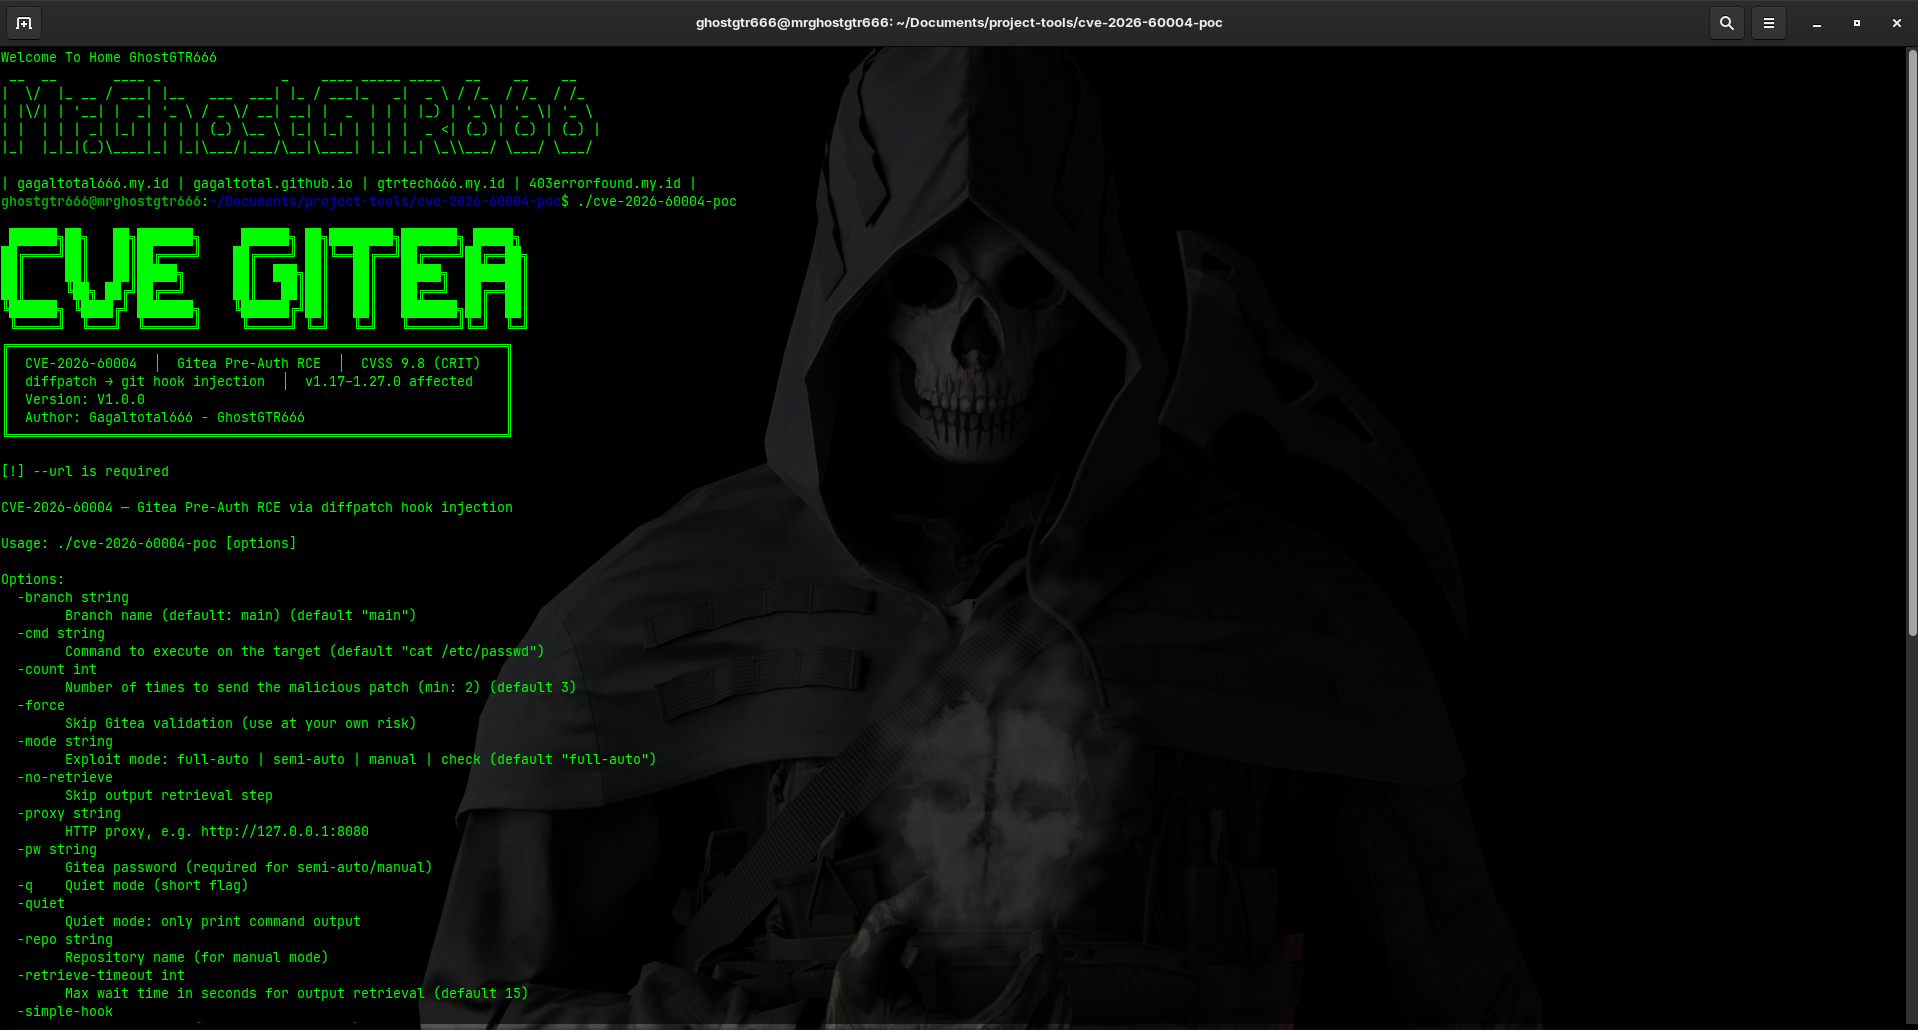
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection

Proof-of-concept exploit for CVE-2026-26216, demonstrating unauthenticated remote code execution via hook injection in Crawl4AI's Docker deployment.…

Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…

Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.

Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…

Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…

Local PoC for CVE-2026-54686 demonstrating DCS lifecycle hook spoofing in Warp terminal. Simulates spoofed CWD and SSH metadata acceptance in…

CVE-2025-10230 PoC - Samba WINS Hook Command Injection

Proof-of-concept exploit for CVE-2025-8110, a command injection vulnerability in Gogs Git hook mechanism enabling remote code execution on…

Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…

Exploit for CVE-2024-32002 targeting Git hook vulnerabilities, enabling remote code execution via crafted repositories during clone operations.

Proof-of-concept exploit for CVE-2025-48384, a Git submodule vulnerability leading to remote code execution through a malicious post-checkout hook.

Proof-of-concept demonstrating Git CR-path submodule misparsing vulnerability leading to arbitrary hook execution during recursive clone operations.

RCE hook

hook repo for cve-2024-32002