

CVE-2023-7028
 yoryio/cve-2023-7028
Exploit for CVE-2023-7028 - GitLab CE/EE
authenticationexploitationlabs-practice+3
yoryio/cve-2023-7028Exploit for CVE-2023-7028 - GitLab CE/EE
 solivaquaant/cve-2026-85706-poc
PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read
 dinosn/cve-2026-10053-lab
Reproducible lab for CVE-2026-10053 (GitLab npm package-registry path traversal -> arbitrary file write as git). Vulnerable 19.2.1 vs patched 19.2.2,…
 groppoxx/cve-2023-2825-poc
PoC for CVE-2023-2825: automated GitLab 16.0.0 arbitrary file read via nested public groups, project upload traversal, reusable upload paths, and…
 flowerwitch/cve-2026-85706_docker_exp
Docker-based reproduction environment and PoC for CVE-2026-85706, demonstrating GitLab LFI bypass via .json suffix and trailing slash path tricks.
 dannymas/cve-2021-22206
Exploit for CVE-2021-22205 targeting GitLab unauthenticated remote code execution via malicious file upload. Provides proof-of-concept code for…
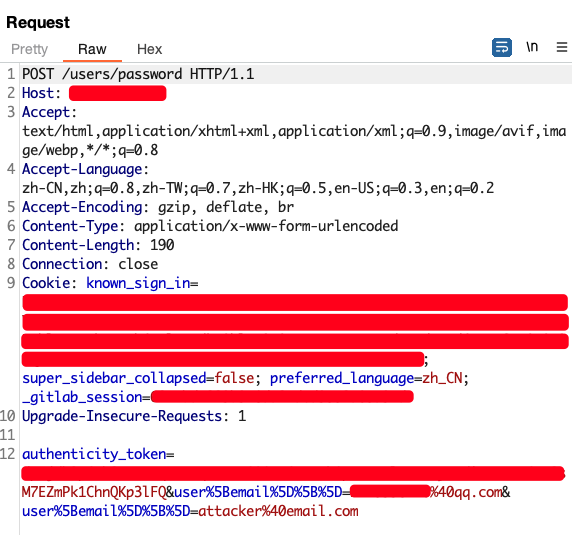 googlei1996/cve-2023-7028
Proof-of-concept exploit for CVE-2023-7028, a GitLab account takeover vulnerability via email confirmation bypass, demonstrating the attack with…
 sornphut/cve-2023-7028-gitlab
Exploit script for CVE-2023-7028 in GitLab, allowing password reset without authentication by sending crafted requests to the target server.
 sariamubeen/cve-2023-7028
Python exploit for CVE-2023-7028, abusing GitLab password reset poisoning to take over accounts including administrators via crafted email requests.
 shimon03/cve-2023-7028-account-take-over-gitlab
Proof-of-concept exploit for CVE-2023-7028, automating GitLab account takeover via password reset email manipulation. Includes temp-mail integration…
 logggg2402/cve-2025-27407
Local lab and proof-of-concept exploit for CVE-2025-27407, targeting GitLab's GraphQL introspection schema loader via the Direct Transfer HTTP path.…
 ipsbruno/cve-2022-1162
Exploit tool for CVE-2022-1162 that enumerates GitLab users and performs authentication bypass via a crafted login request.
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 hikikan/cve-2021-22205
Exploit for CVE-2021-22205 targeting a remote code execution vulnerability in GitLab. Provides a proof-of-concept for security testing and…
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
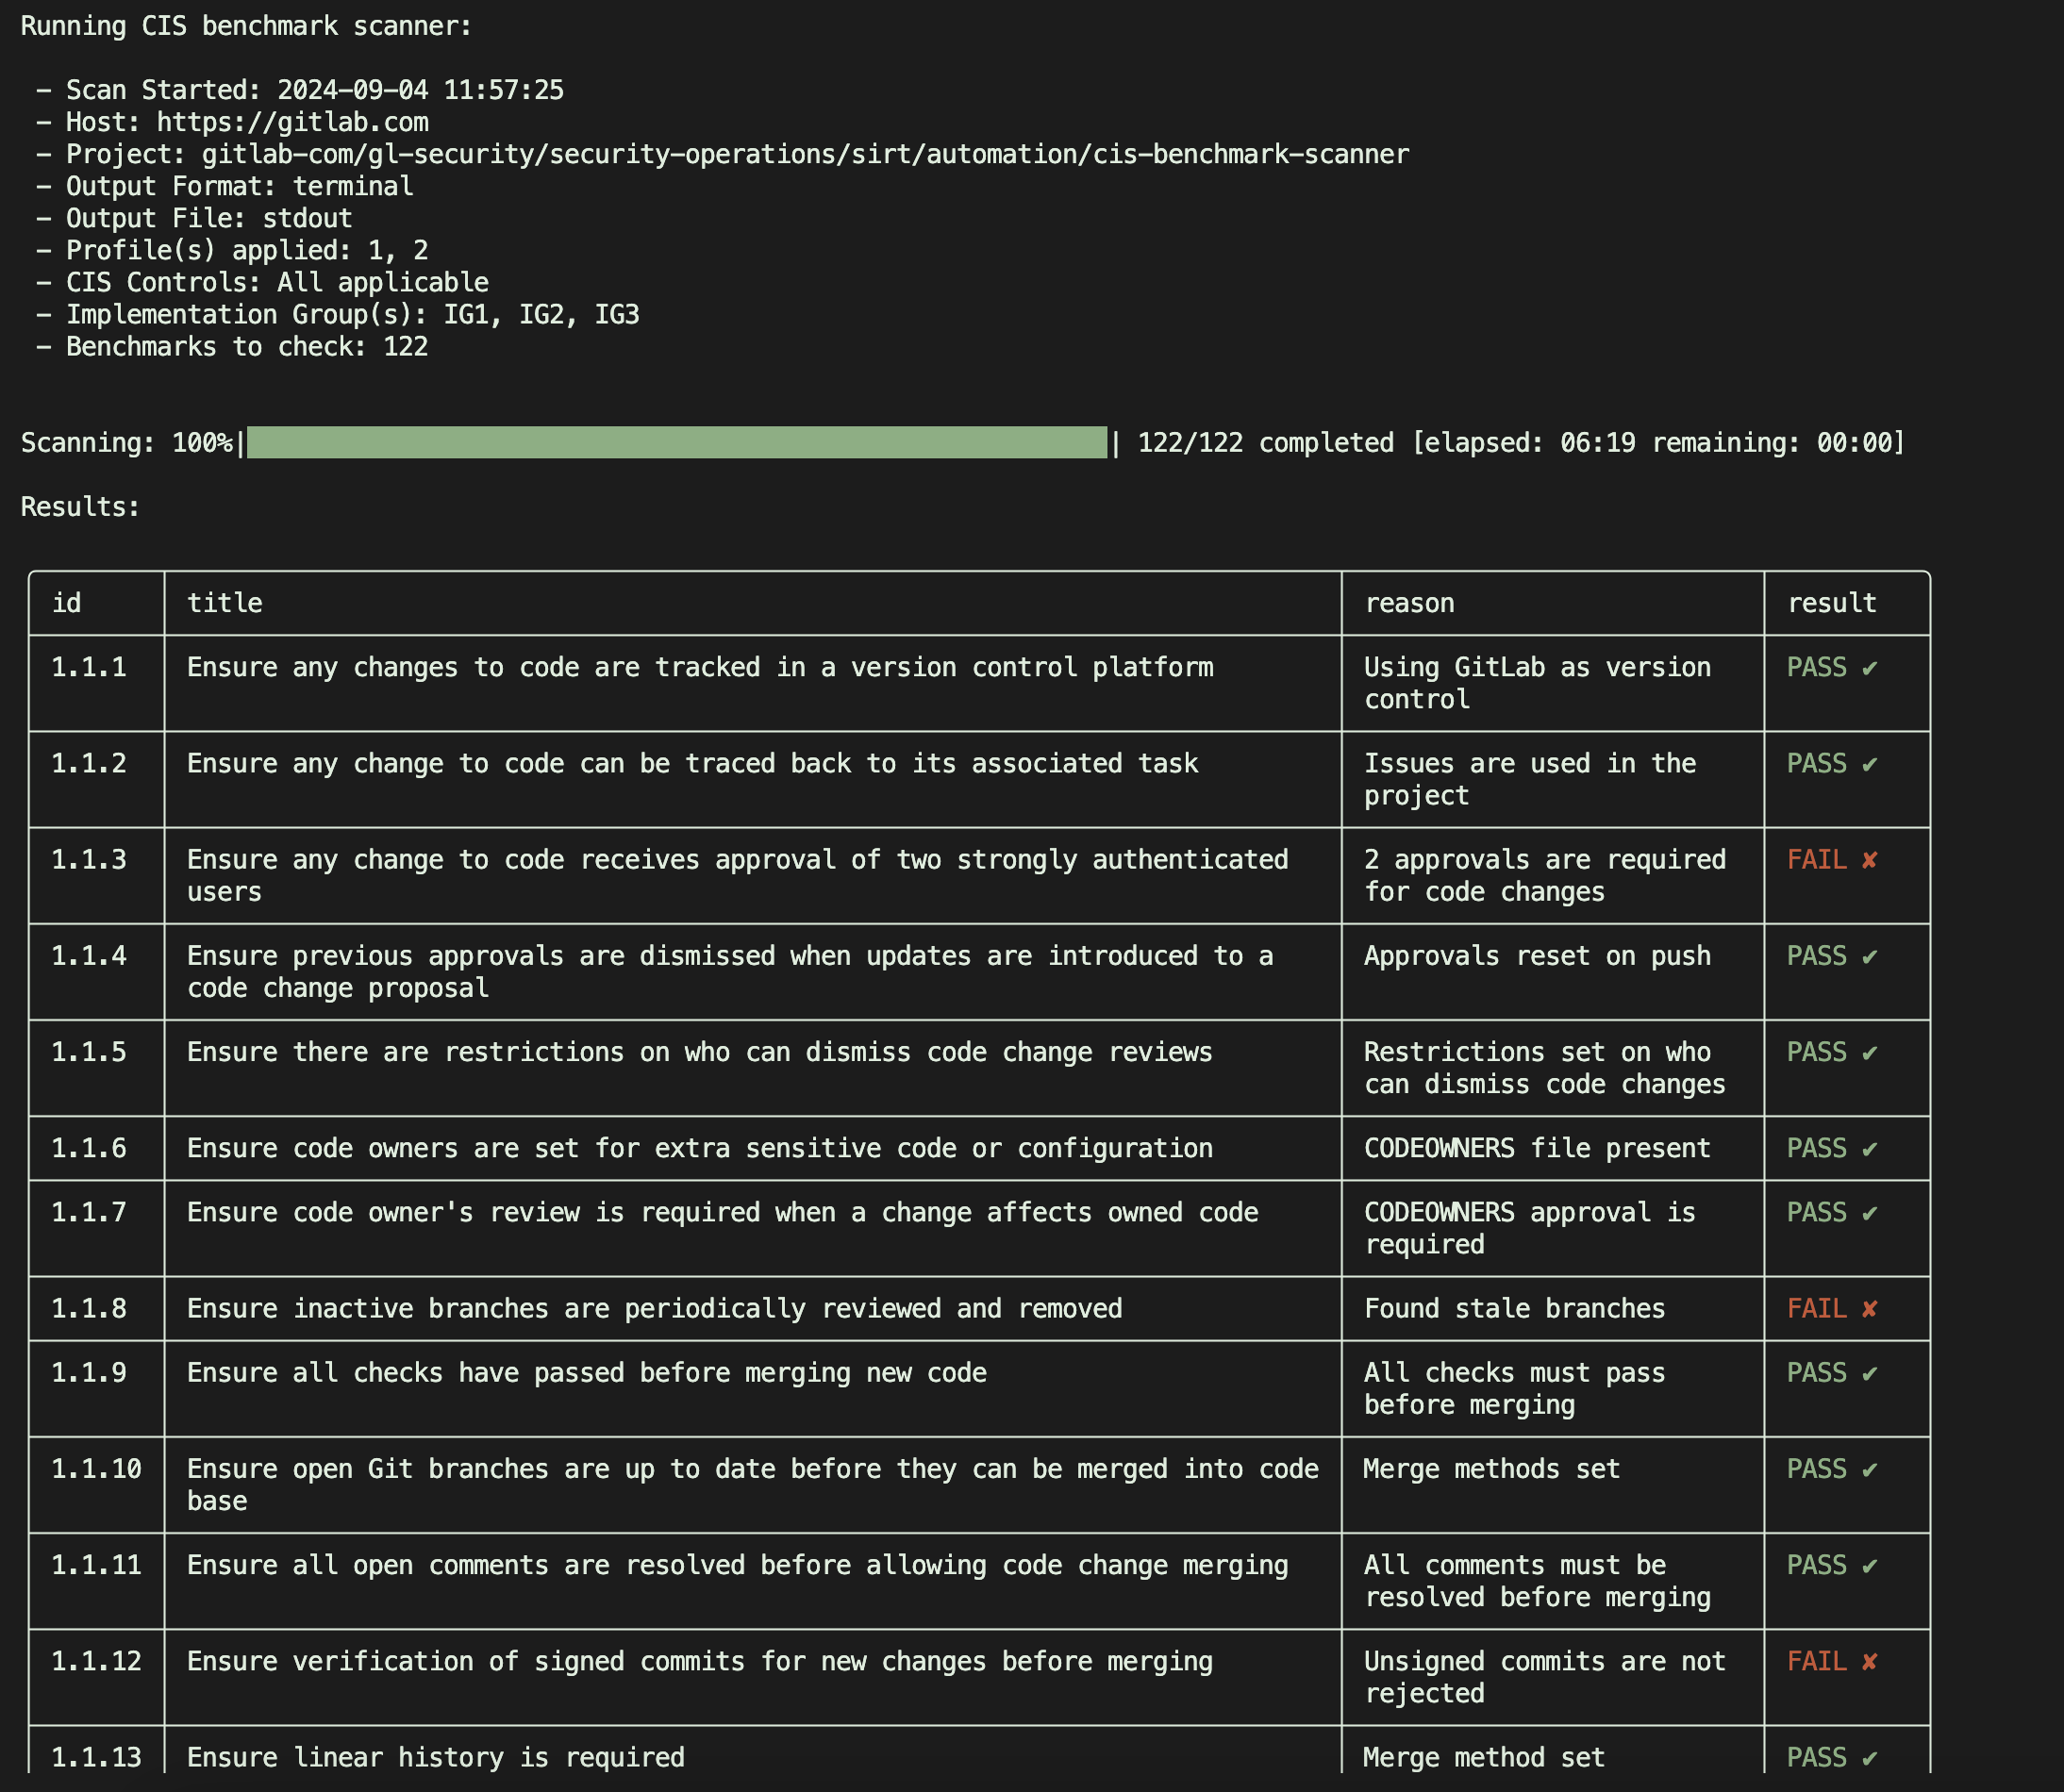
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 zz-socmap/cve-2021-22214
Gitlab CI Lint API未授权 SSRF漏洞 CVE-2021-22214