Ivanti-Pulse_VPN-Client_Exploit-CVE-2023-35080_Privilege-escalation

Exploit for CVE-2023-35080 leveraging a write primitive in the Ivanti/Pulse VPN client kernel driver on Windows to achieve privilege escalation.

Exploit for CVE-2023-35080 leveraging a write primitive in the Ivanti/Pulse VPN client kernel driver on Windows to achieve privilege escalation.

CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…

Exploit for CVE-2021-4034, a memory corruption vulnerability in pkexec of polkit, enabling local privilege escalation to root on Linux systems.

Proof Of Concept for the 2021's pkexec vulnerability CVE-2021-4034

Log4Shell (Cve-2021-44228) Proof Of Concept

Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.

Win32k elevation of privilege exploit for CVE-2015-1701, providing proof-of-concept code for kernel-mode privilege escalation on vulnerable Windows…


the metasploit script(POC) about CVE-2021-36260

Dell Driver EoP (CVE-2021-21551)

CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)

Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…

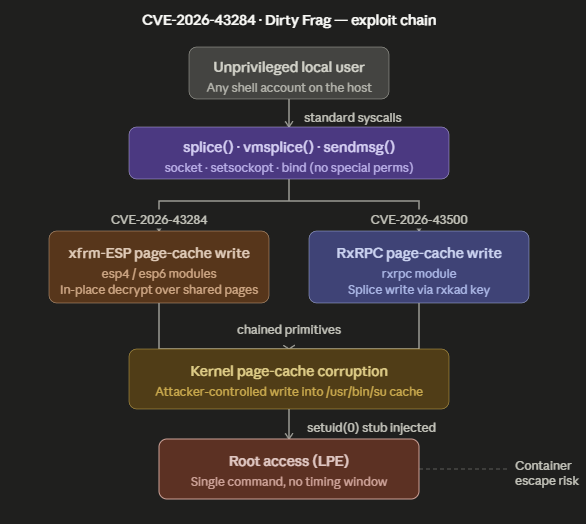
Dirty Frag - kernel Linux critical Vulnerability

CVE-2026-31431 (Copy Fail) novel exploit: live code corruption via page cache. Overwrites libc exit() code through MAP_PRIVATE page sharing — affects…