

CVE-2002-0082
 ratiros01/cve-2002-0082
CVE-2002-0082
binary-exploitationexploitationvulnerability-analysis+2
ratiros01/cve-2002-0082CVE-2002-0082
 mhe18/cve_project
CVE-2016-1240 exploit and patch
 swzhouu/cve-2020-27368
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE
 tulhan/commons-text-goat
An intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.
 arkha-corvus/letsdefend-soc235-atlassian-confluence-broken-access-control-0-day-cve-2023-22515-eventid-197
I was presented with a high-severity alert indicating a potential exploit attempt of CVE-2023-22515, a zero-day vulnerability in Atlassian…
 mobilelinux/iovy_root_research
A root tool based on the [CVE-2015-1805 vulnerability](https://access.redhat.com/security/cve/cve-2015-1805) It supports 32 and 64bit, get sys call…
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 elw0od/pentesterlab
OrangeBadge - Exercise CVE-2018-6574: go get RCE
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su
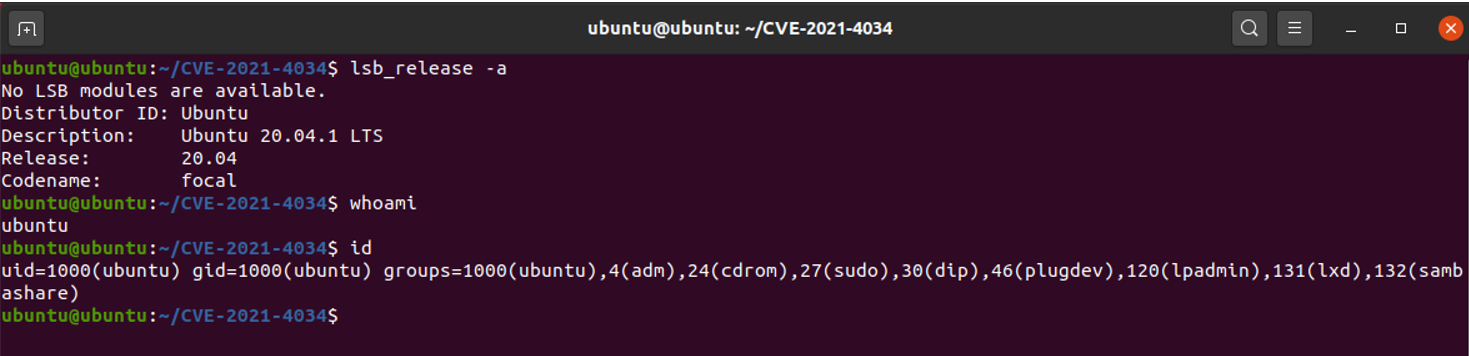 al1ex/cve-2021-4034
Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 wack0/cve-2022-35841
small writeup on EnterpriseModernAppManager::ProvisionApplication bug
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 digamma-ai/cve-2020-8835-verification
Coq-based formal verification of a Linux kernel eBPF verifier vulnerability (CVE-2020-8835) with reproducible build environment and proof artifacts.
 zzzz0317/log4j2-vulnerable-spring-app
CVE-2021-44228
 yup-ivan/cve-2024-9796
POC (SQLi) -> CVE-2024-9796