CVE-2022-40127-Airflow-RCE

Proof-of-concept exploit for CVE-2022-40127 targeting Apache Airflow RCE via crafted run_id parameter, with automated reverse shell delivery.

Proof-of-concept exploit for CVE-2022-40127 targeting Apache Airflow RCE via crafted run_id parameter, with automated reverse shell delivery.

Python 3 exploit for Kibana < 6.6.1 RCE (CVE-2019-7609) via prototype pollution, with automatic version detection and optional reverse shell.

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

Python exploit script for CVE-2024-28397 targeting js2py <= v0.74. Supports reverse shell and custom command execution via HTTP endpoint.

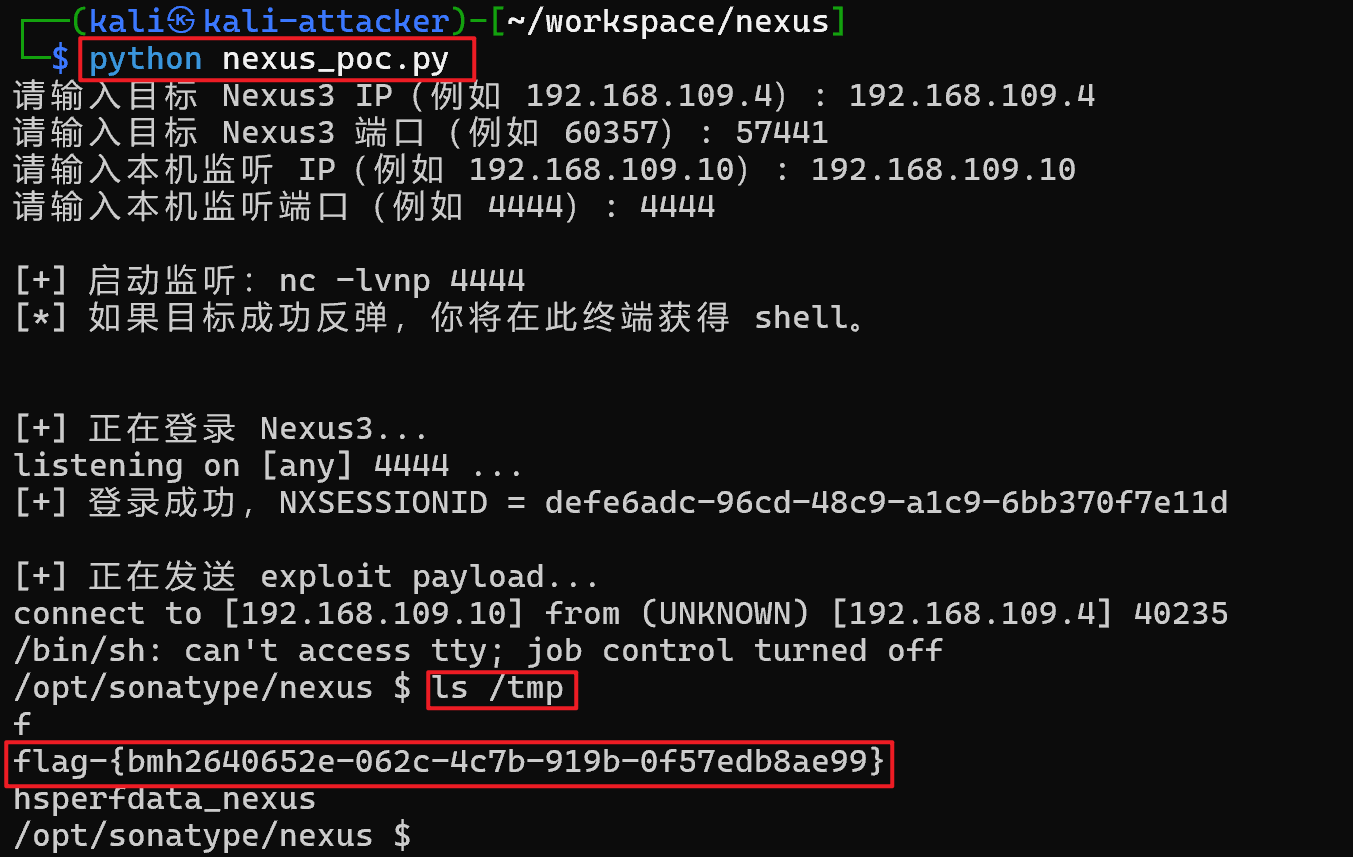
Automated one-click exploit for Nexus Repository Manager3 EL injection (CVE-2018-16621) that executes the vulnerability and returns a reverse shell.

Python exploit script for CVE-2024-36401 vulnerability check. Sends a reverse shell payload to a specified target and port for authorized security…

Proof-of-concept exploit scripts for CVE-2016-3714 (ImageTragick) using MVG/SVG files to deliver reverse shells via bash, nc, and PHP for ethical…

Exploit script for Apache Struts2 REST Plugin XStream RCE (CVE-2017-9805)

Python exploit script for Apache Struts2 REST Plugin XStream RCE (CVE-2017-9805) enabling remote command execution and reverse shell on vulnerable…

This script leverages CVE-2023046604 (Apache ActiveMQ) to generate a pseudo shell. The vulnerability allows for remote code execution due to unsafe…

Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)

Exploit script written in C# to aid gaining a reverse shell on targets with Windows Server Update Service(WSUS) CVE-2025-59287.

Standalone proof-of-concept exploit for CVE-2023-37903 that triggers the targeted vulnerability and establishes a reverse shell.

Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…

Exploit scripts for CVE-2024-28397, a js2py sandbox escape that executes arbitrary Python code to spawn a reverse shell on a target endpoint.

Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.

Proof-of-concept exploit for CVE-2022-29078 (ejs 3.1.6) enabling remote command execution via a Python script. Accepts a target URL and provides an…

CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)