
NGINX_2026_CVE_Bundle_CTI_Report
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
cloud-securitycurated-resourceseducation+6
chpratik/nginx_2026_cve_bundle_cti_reportCovered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 sentinel-aidefense/cve-2026-21509
CVE-2026-21509 Research writeup
 sentinel-aidefense/cve-2025-33073
CVE-2025-33073 Research writeup
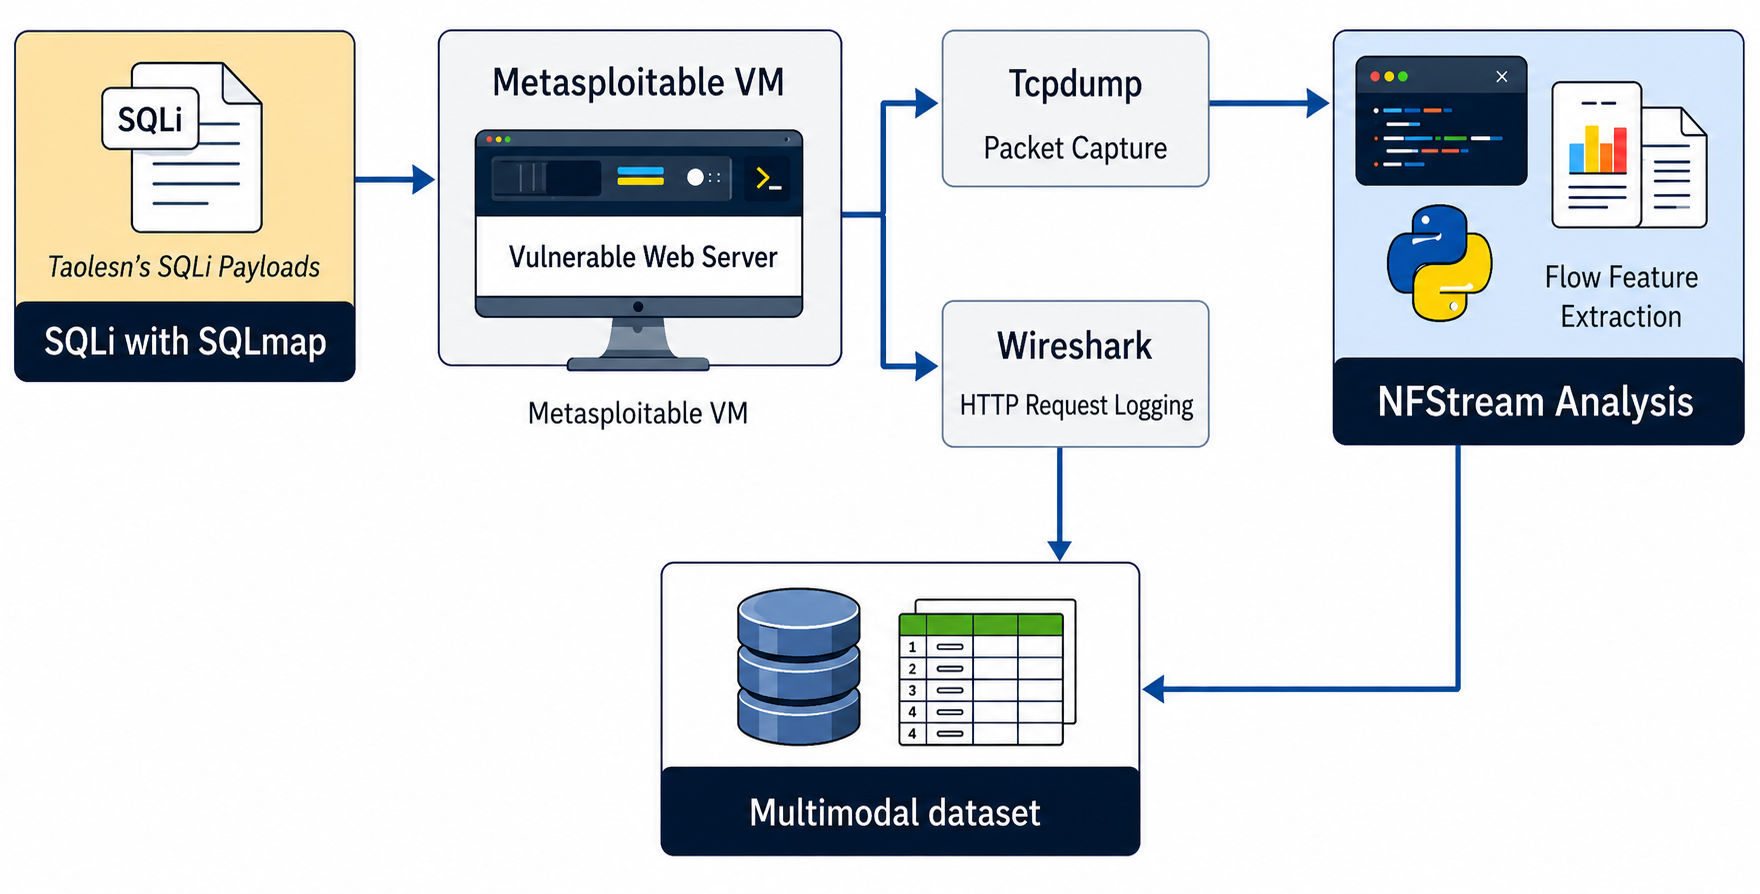 paul12345-cyber/multimodal-web-attack-dataset
This repository hosts a multimodal web attack dataset (MWAD) to advance AI-driven threat detection research.
 dorser/cve-2024-21626
Educational demo of CVE-2024-21626 runc container escape with eBPF-based detection gadget for exploitation attempts.
 sentinel-aidefense/cve-2025-10035
CVE-2025-10035 Research writeup
 k3ystr0k3r/mikrotik-winbox-scanner
Winbox Protocol Scanner (MikroTik RouterOS)
 bishopfox/cve-2026-19490-check
Safely detect Citrix NetScaler SAML auth bypass CVE-2026-19490
 glebusalt/cybersecurity_portfolio
Практические кейсы по информационной безопасности: развёртывание SIEM Wazuh и эксплуатация CVE-2021-41773
 rickgeex/cve-2025-5777-citrixbleed
CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”
 1337g/cve-2017-3881
credit to artkond
 0xa1m/cve-2025-63353
This is a Proof-Of-Concept of CVE-2025-63353
 iioch/ban-exploitable-bitcoin-nodes
Ban all denial-of-service vulnerability exploitable nodes from your node CVE-2018-17144
 rhysemmas/martian-packets
Crafting raw TCP/IP packets to send to poorly configured Kubernetes servers - CVE-2020-8558 PoC
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 aerchy/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a remote command injection in Zyxel NAS devices, demonstrating arbitrary command execution via crafted…
 polosss/by-poloss..-..cve-2026-11912
Missing Authorization to Unauthenticated File Modification