
stunner
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
exploitationmisconfigurationnetwork-security+3
868
firefart/stunnerTest and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 zerodayevil/cve-2026-41940-poc
Proof-of-concept code demonstrating CVE-2026-41940, providing a reproducible test case for vulnerability verification and security research.
 zerodayevil/cve-2026-41096-poc
Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and…
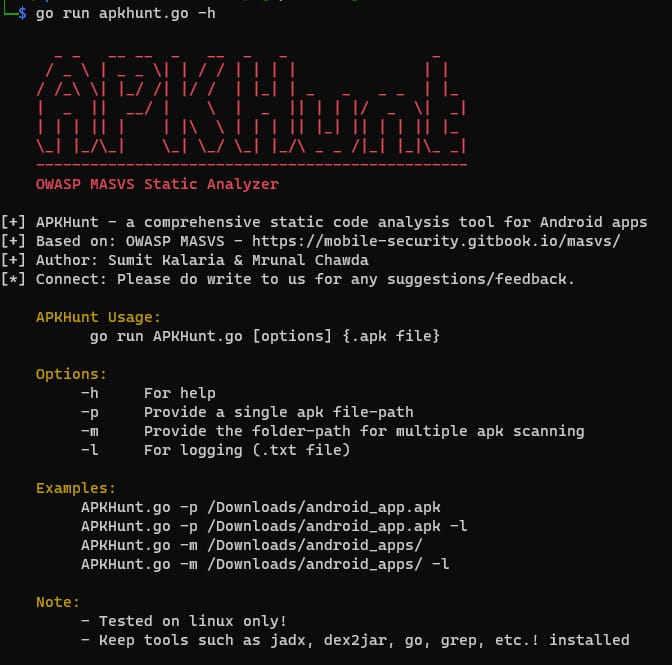 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 cumakurt/mudos
Command-line multi-vector DDoS test tool with 129 volumetric, protocol, application, and amplification attack vectors for authorized resilience…
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
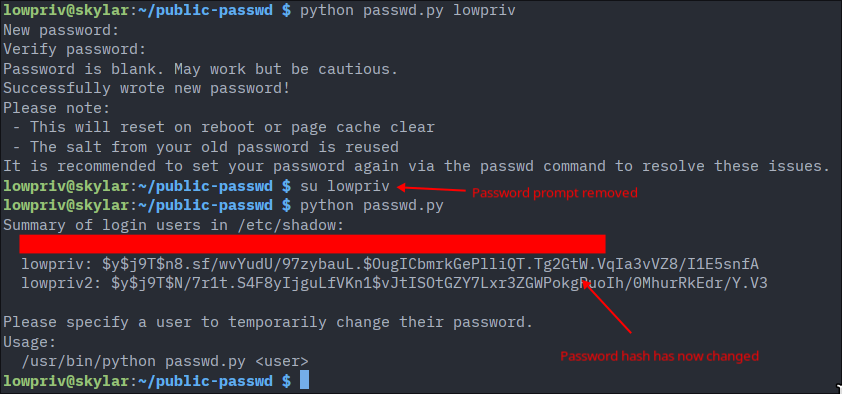 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
 xitexploiter96-dot/cve-2025-23419
Python-based TLS session reuse exploit tester that checks for authentication bypass vulnerabilities in misconfigured servers requiring client…
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 sorrence/cve-2021-44228
A simple Log4j PoC written in Go
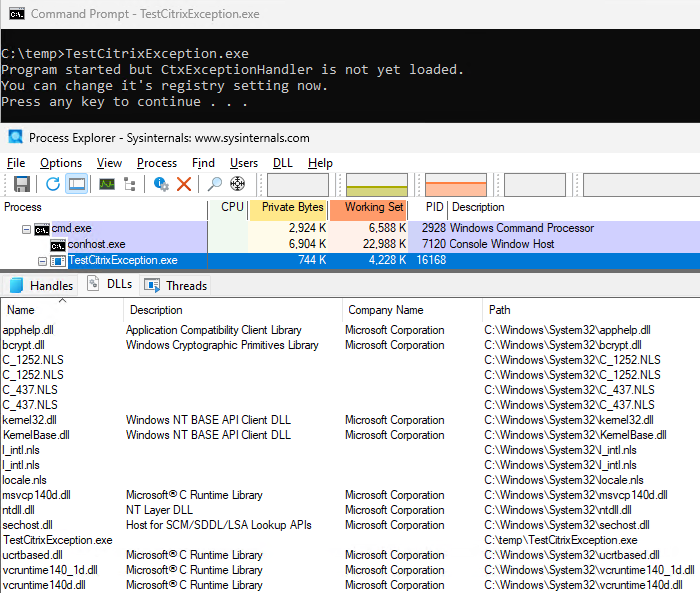 olljanat/testcitrixexception
Minimal tool to test CVE-2025-6759 mitigation
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 obscura-cert/cve-2025-31650
Multi-threaded HTTP/2 request flood tool targeting Apache Tomcat 10.1.10-10.1.39 using malformed priority headers for DoS stability testing. Strictly…
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers