
cynative
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
ai-securitycloud-securitycontainer-security+7
203
cynative/cynativeRead-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 techgaun/github-dorks
Find leaked secrets via github search
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 maxprog-svg/citrixbleedcve-2026-8452-2025-5777
CitrixBleed Exploit Tool - CVE-2025-5777 & CVE-2026-8452. Unauthenticated remote memory read from Citrix NetScaler ADC & Gateway. Steal admin session…
 maxprog-svg/cve-2026-55040-mass-exploit
Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 george0papasotiriou/cve-2026-23007-serverless-cold-start-memory-remanence-data-leakage-
Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…
 george0papasotiriou/cve-2026-22001-sphincs-wots-weak-randomness-forgeable-signature
Demonstrates a critical SPHINCS+ WOTS+ signature forgery caused by weak randomness and nonce reuse, recovering secrets from two (r,s) signature pairs.
 george0papasotiriou/cve-2026-21002-serverless-cold-start-credential-leakage-via-reused-tmp
PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…
 abdugafforov-bobur/cve-2026-65694-poc
PoC for CVE-2026-65694 — Microweber CMS (<=2.0.20) unauthenticated path traversal → arbitrary file read (.env / secrets)
 nvicloud/cve-2026-12352
Proof-of-concept for CVE-2026-12352, an authentication bypass in Digi PortServer TS that discloses device configuration including plaintext RADIUS…
 cain66666/openclaw-hardening-check
Offline, read-only hardening check for a self-hosted OpenClaw install — gateway exposure, auth, CVE-2026-25253. Never prints secrets, makes no…
 gagaltotal/cve-2026-26980-ghost-cms-api
Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…
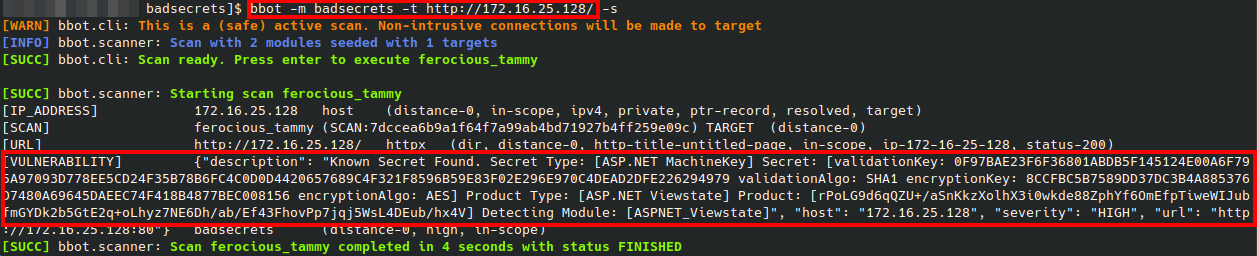 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks