pwned
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
information-gatheringosintpassword-cracking+1
246
wkovacs64/pwnedCLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
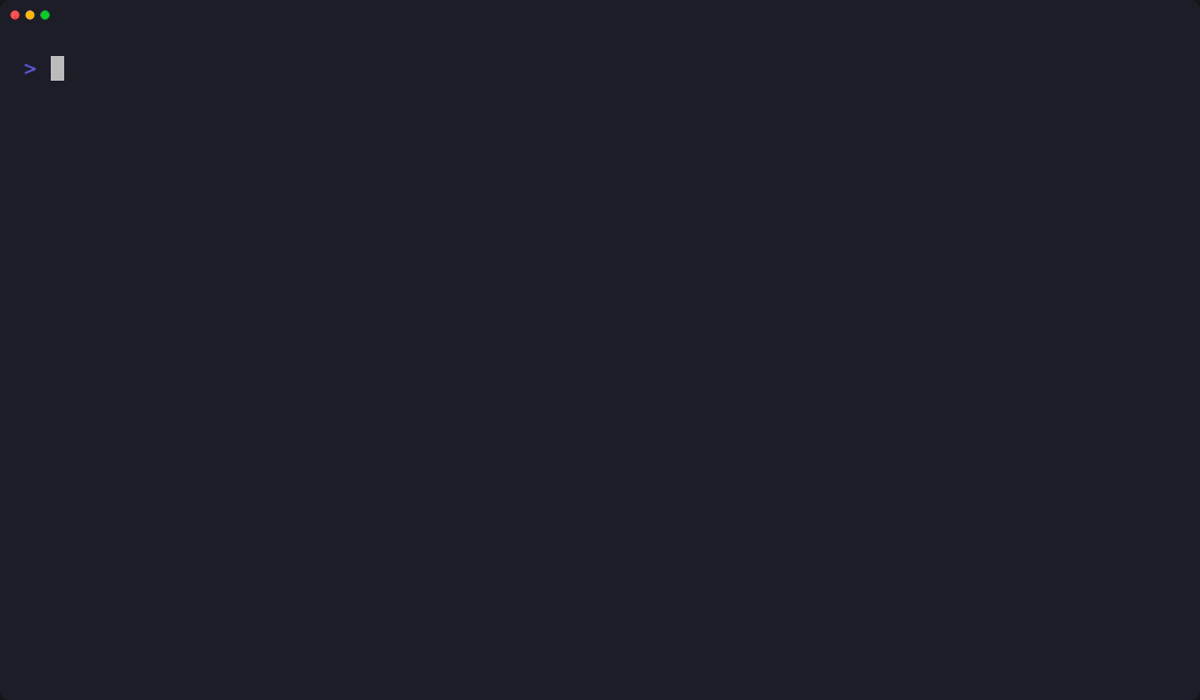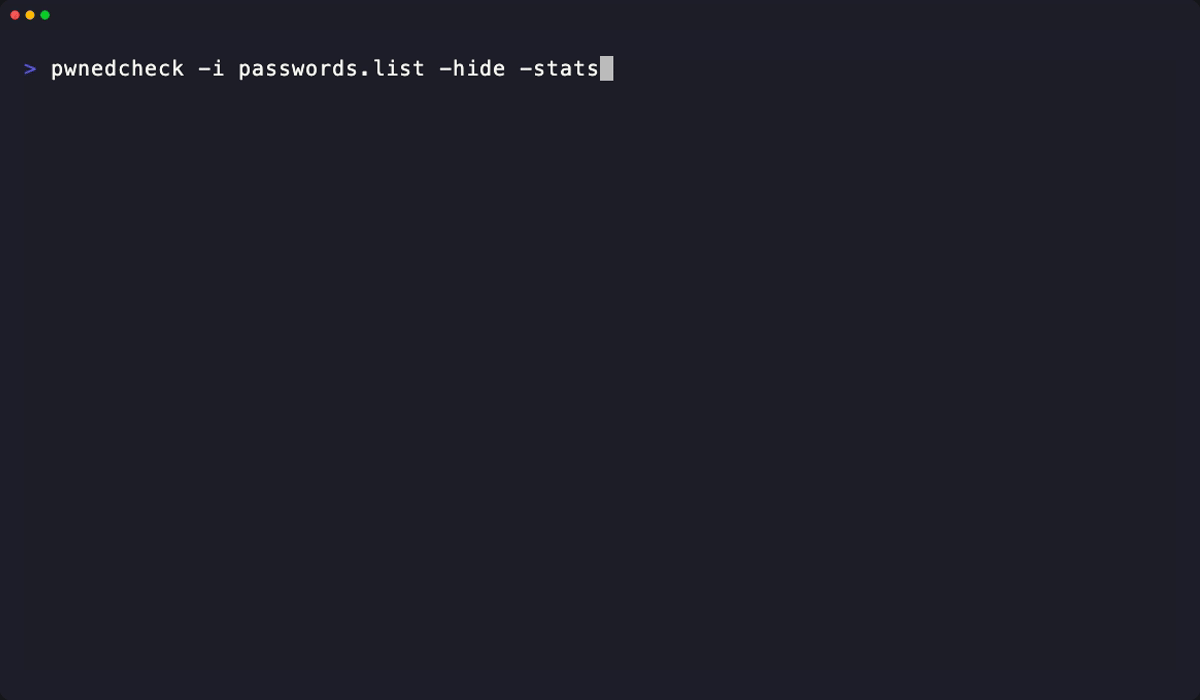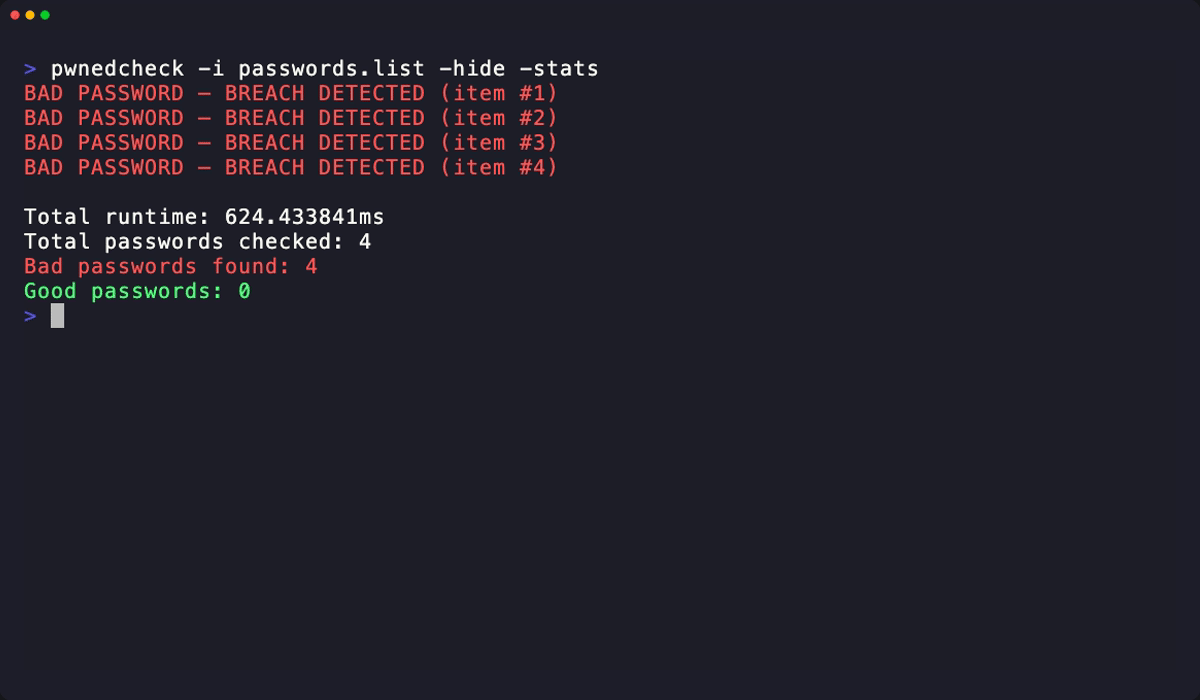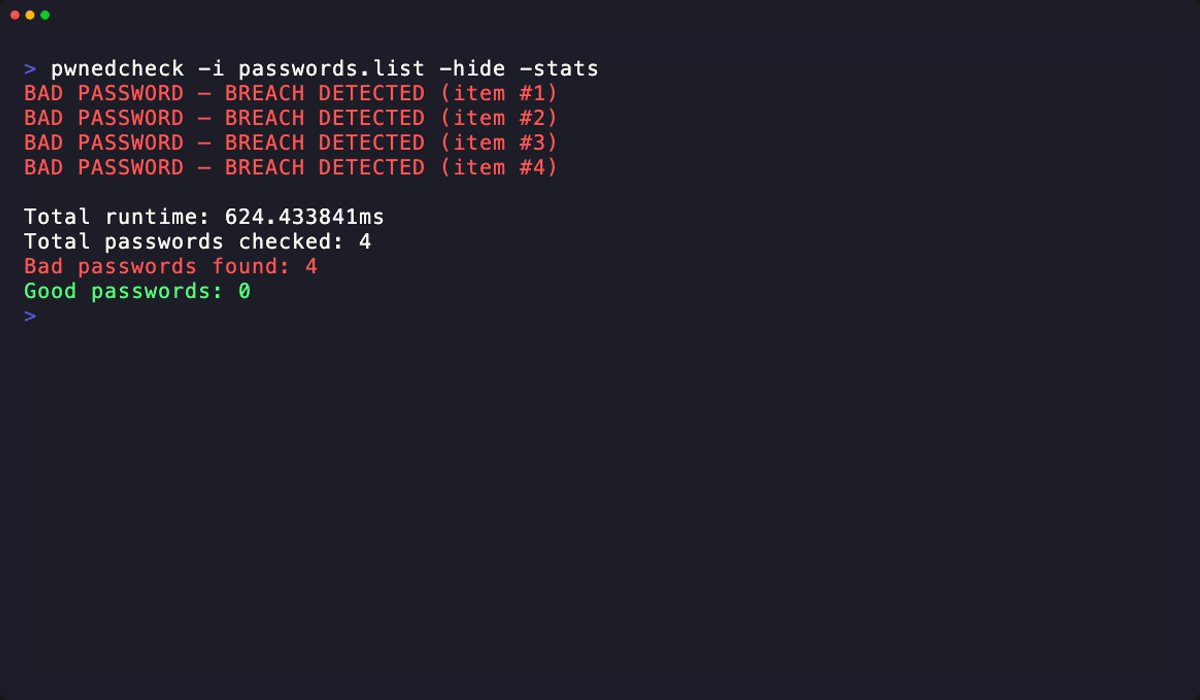 mohamedation/pwnedcheck
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
 pysectools/cve-2026-3629
WordPress Privilege Escalation Checker
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 m31r0n/sniprecover-cli
Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
 pentest-a2p2v/pentest-a2p2v-core
Core A2P2V functionality (command line based)
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
 municipalparkingservices/cve-2021-44228-scanner
Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…
 farjaalahmad/cve-2019-16759
Interactive-Like Command-Line Console for CVE-2019-16759
 kapejod/rtpnatscan
Minimal CLI scanner that probes RTP proxies and NAT helpers for NAT-stealing vulnerability, helping VoIP administrators validate and harden media…