
GitLab-CVE-2023-7028
 feartheploto/gitlab-cve-2023-7028
Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
educationexploitationlabs-practice+2
feartheploto/gitlab-cve-2023-7028Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 anothersec/cve-2025-4796
eventin <= 4.0.34 - privilege escalation via user email change / account takeover for authenticated contributor+
 saykino/cve-2025-54321
Documentation of CVE-2025-54321: an email bombing vulnerability in Ascertia SigningHub's reset password function due to missing rate limiting,…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 helloandrewpaul/reflected-xss-in-vvveb-cms-v1.0.7.2
CVE-2025-9728: Reflected XSS in Login Form (Email & Password Fields) Vvveb CMS v1.0.7.2
 cybersecplayground/cve-2024-48887-fortiswitch-exploit
a lightweight JavaScript snippet showcasing how unauthorized password changes can be triggered on vulnerable Fortinet FortiSwitch GUI endpoints.
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 sariamubeen/cve-2023-7028
Python exploit for CVE-2023-7028, abusing GitLab password reset poisoning to take over accounts including administrators via crafted email requests.
 theunknownsoul/cve-2023-23397-pow
Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.
 hatlesswizard/cve-2023-6875
CVE-2023-6875 exploit written for Xakep.Ru
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
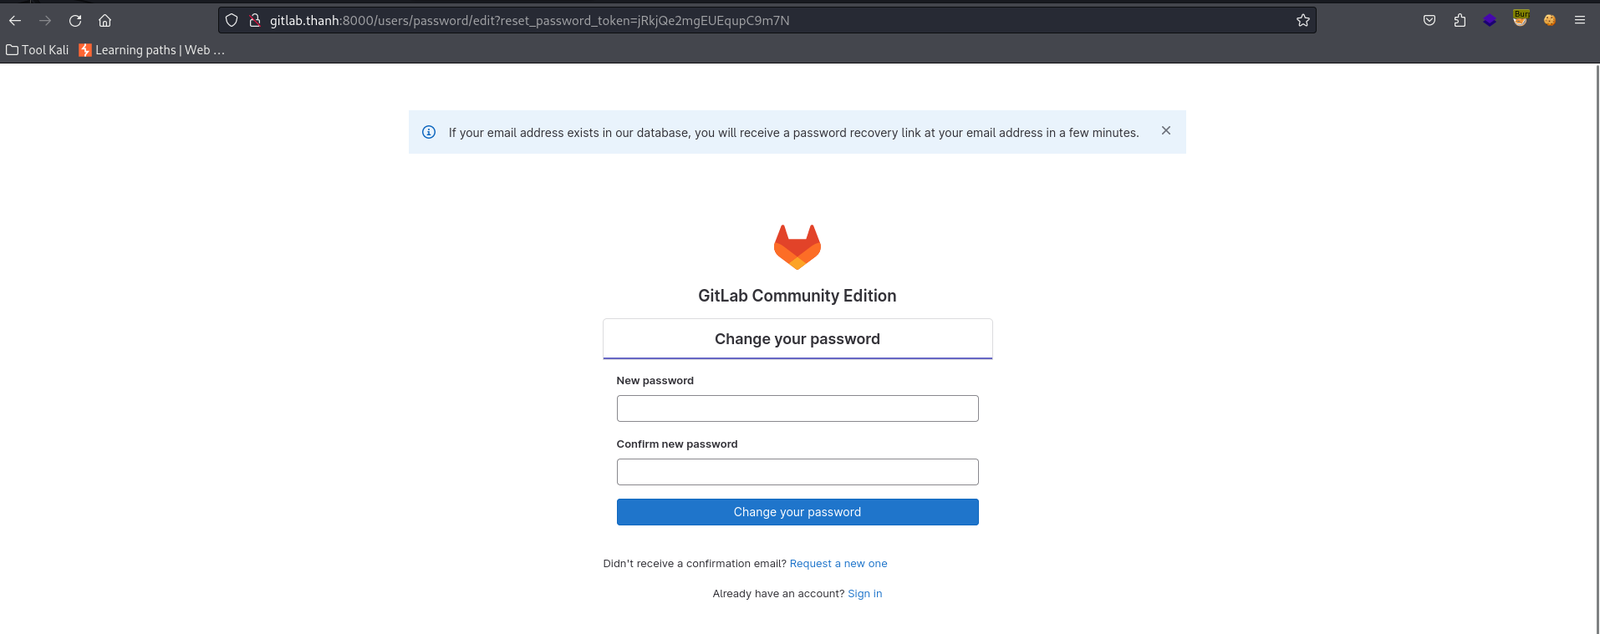 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 shimon03/cve-2023-7028-account-take-over-gitlab
Proof-of-concept exploit for CVE-2023-7028, automating GitLab account takeover via password reset email manipulation. Includes temp-mail integration…