

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.3k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
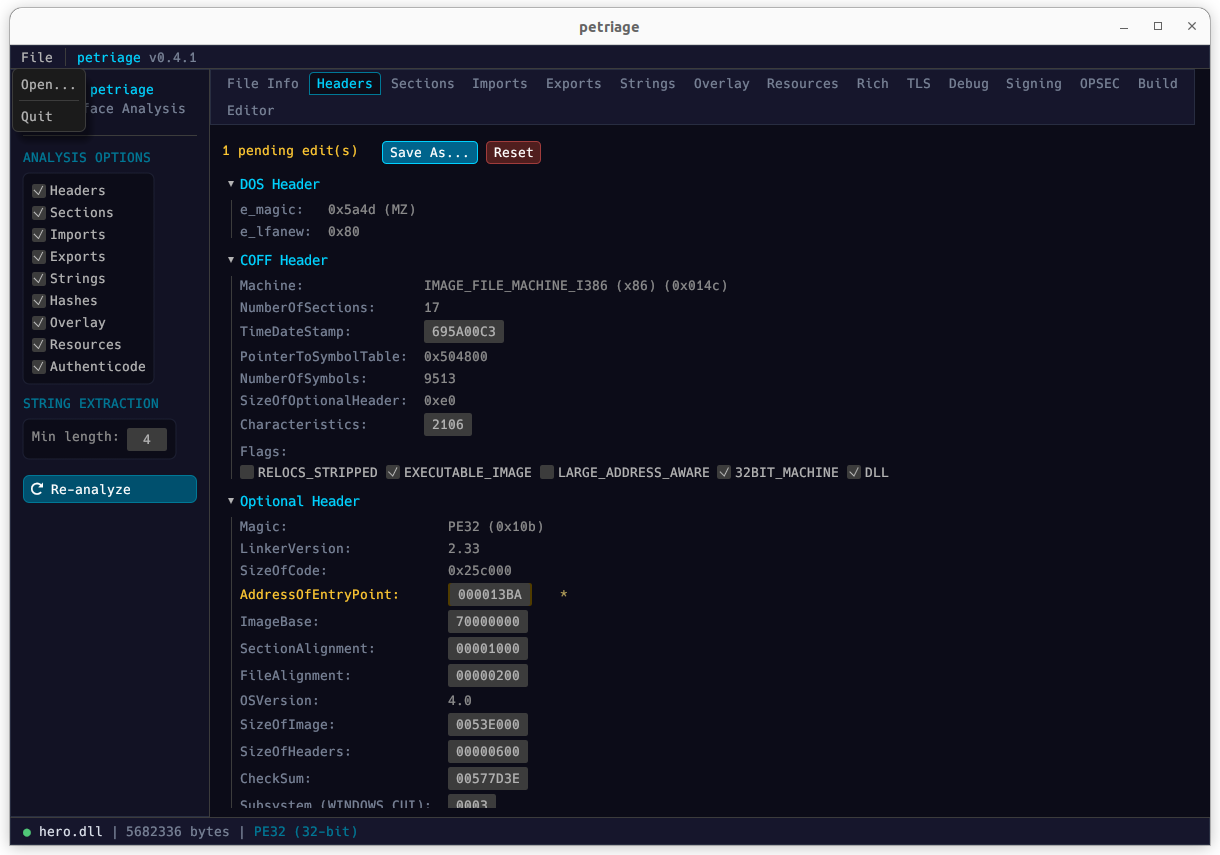 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
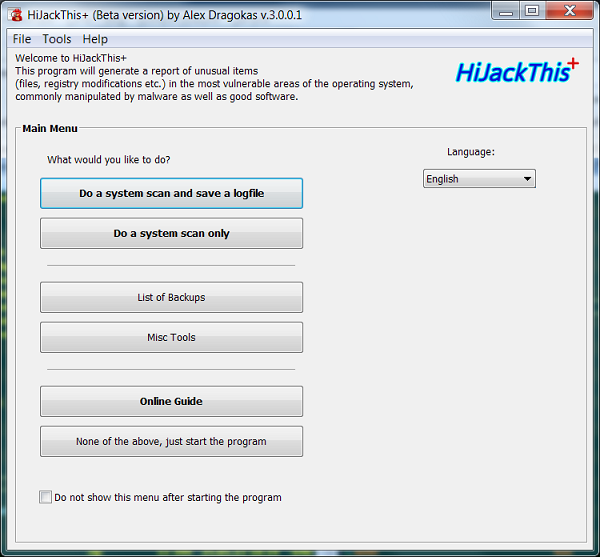 dragokas/hijackthis
A free utility that finds malware, adware and other security threats
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 gao-zuin/cve-2022-46395-qemu
QEMU-based lab for reproducing CVE-2022-46395 race condition in Arm Mali r36p0 GPU driver. Includes PoC, build scripts, and initramfs packaging for…
 4n4s4zi/copyfail-alpine
More portable PoC of copyfail LPE (CVE-2026-31431) that works on Alpine Linux
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
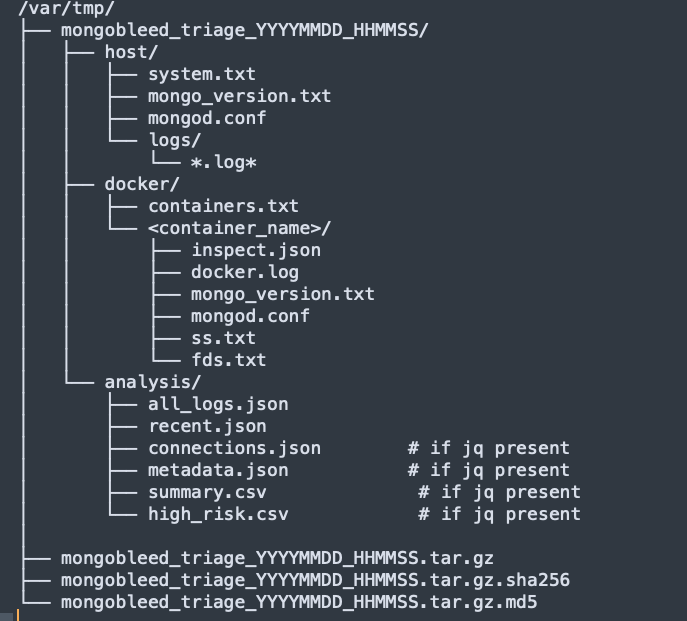 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 fufu-byte/cve-2024-46506
Standalone Python exploit for CVE-2024-46506, providing a lightweight, portable remote code execution module without requiring the Metasploit…
 gonaumov/cve-2025-55182-checker
A portable Bash script to detect vulnerable versions of React Server DOM and Next.js packages affected by [CVE-2025-55182]
 sabecomoeh/cve-2013-3900
Proof-of-concept exploit for CVE-2013-3900, a WinVerifyTrust signature validation vulnerability enabling arbitrary code execution via crafted…
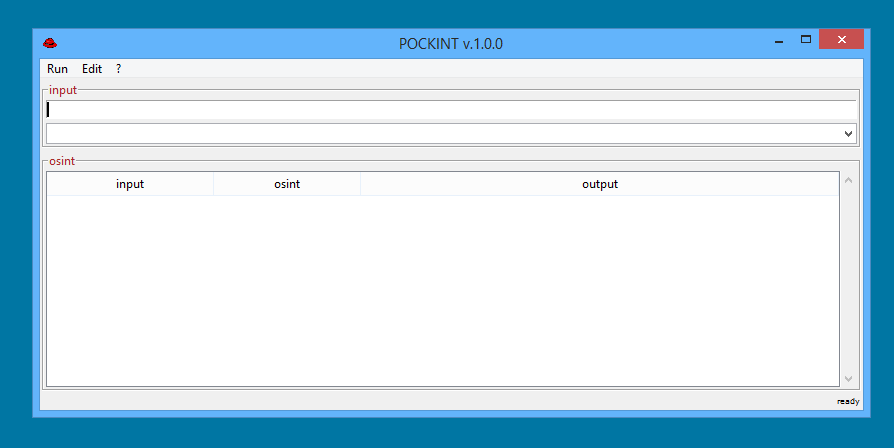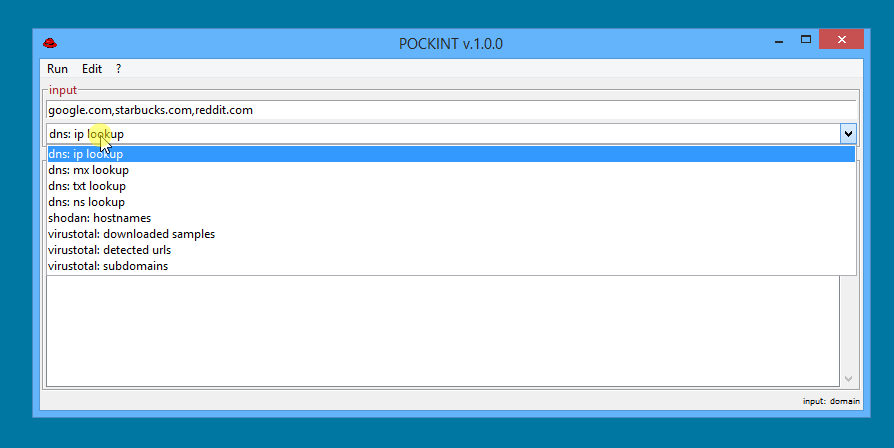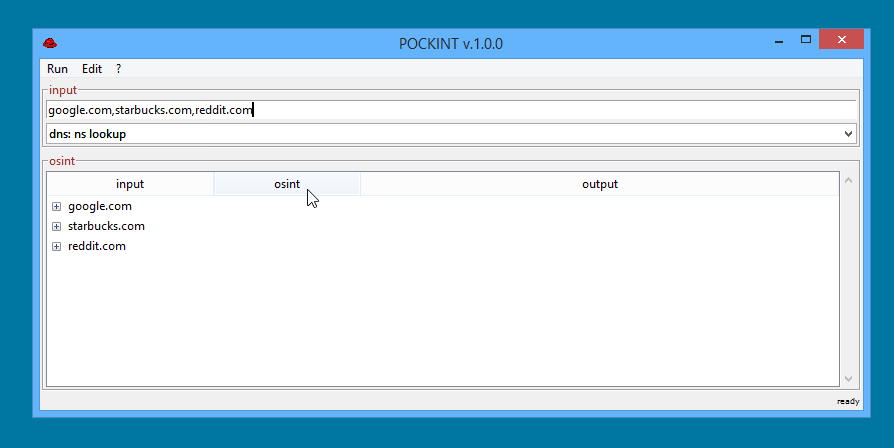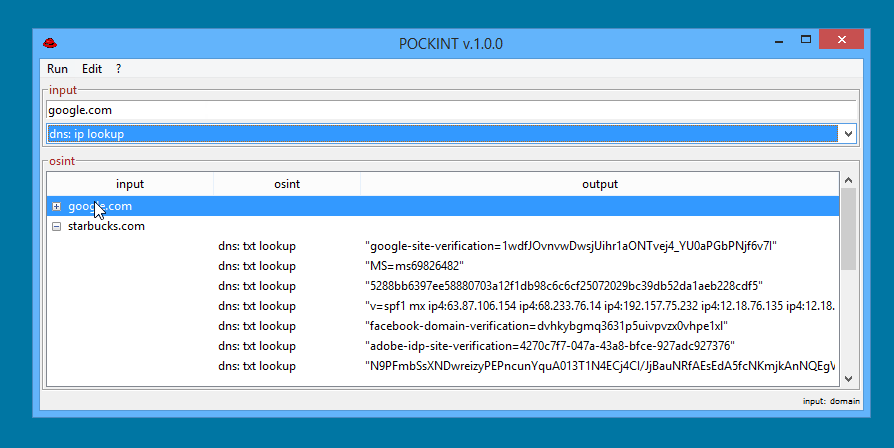 edoardogerosa/pockint
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 1n3/exploits
Exploits by 1N3 @CrowdShield @xer0dayz @XeroSecurity
 mandatoryprogrammer/xsshunter
The XSS Hunter service - a portable version of XSSHunter.com
 guelfoweb/peframe
PEframe is a open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.