
cve-2021-44790-lab
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
educationexploitationfuzzing+5
mohammadalimehri/cve-2021-44790-labDockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 joaovicdev/exploit-cve-2026-56121
Proof-of-concept exploit for CVE-2026-56121, an unauthenticated RCE in Feast's registry gRPC server via unsafe dill deserialization. Includes a…
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…
 nu11secur1ty/cve-2021-44228-vuln-app
Dockerized vulnerable web application demonstrating the Log4j CVE-2021-44228 remote code execution vulnerability for educational exploitation and…
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…
 phor3nsic/cve-2021-40822
PoC and Dockerized vulnerable lab for CVE-2021-40822 (SSRF in GeoServer)

 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
 yusufdalbudak/cve-2026-42945
Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…
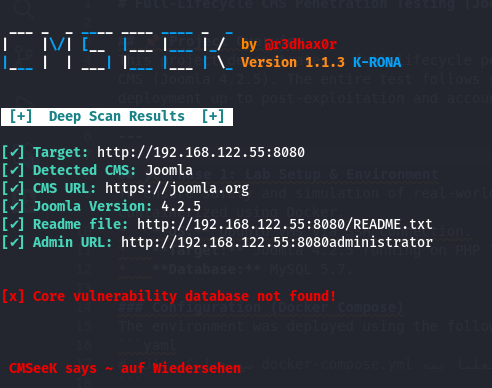 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 meh098/cve-2026-24072-analysis
Technical analysis of CVE-2026-24072, a local privilege escalation in Apache HTTP Server mod_rewrite, including root cause, patches, and Dockerized…
 rootdirective-sec/cve-2026-33017-lab
Reproducible lab for CVE-2026-33017, an unauthenticated RCE in Langflow. Includes a Dockerized vulnerable service and a least-harm PoC that…
 saptaktdk/zenml-cve-2024-2083-poc
Dockerized vulnerable lab demonstrating CVE-2024-2083 in ZenML, a path traversal vulnerability in the step logs API allowing arbitrary file read.
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…