
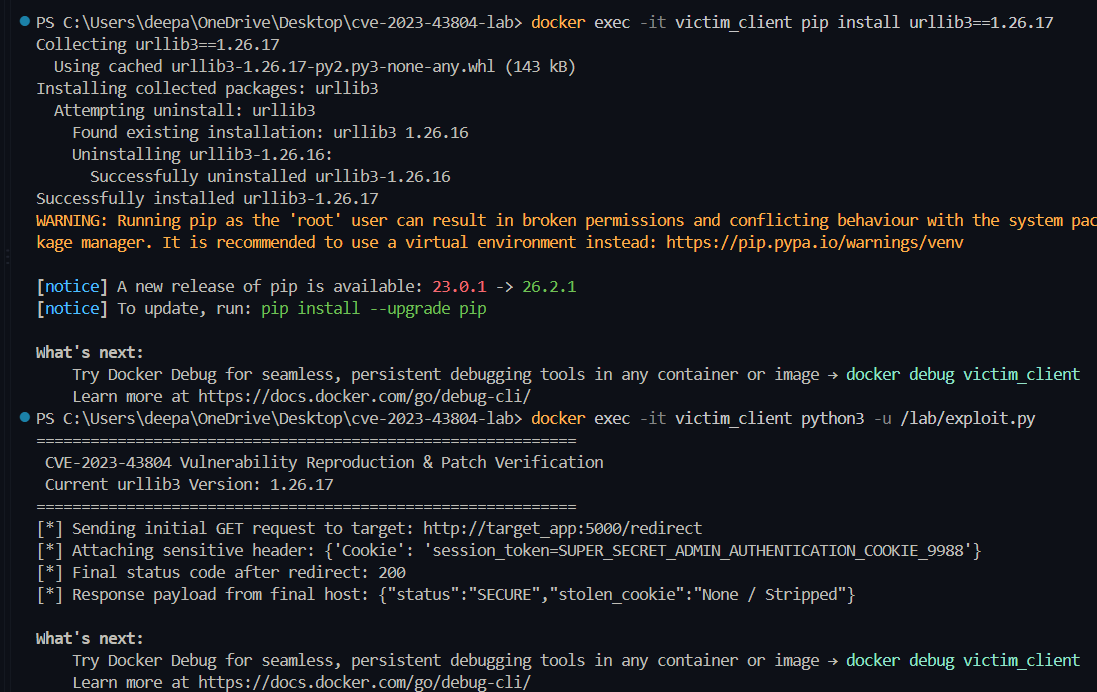
CVE-2023-43804
 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
container-securitydefensive-toolseducation+5
deepanshu-khurana/cve-2023-43804Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 eliot-code/cve-2026-52924
Technical analysis of CVE-2026-52924, a critical use-after-free in Linux kernel SCTP stale cookie handling, including root cause, attack flow, fix,…
 ghostpels/cve-2026-75865
Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 charanmv08/cve-2022-29117-assessment
CVE-2022-29117 (.NET Cookie-Handling DoS) Assessment, Understanding & Questions Framework
 toanln-cov/cve-2026-74252
Stored XSS in J2Commerce Guest Checkout via Cookie Filter Bypass
 4minx/cve-2026-50522
CVE-2026-50522 PoC
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 baktistr/cve-2026-23550-poc
Bash-based proof-of-concept tester for CVE-2026-23550. Checks WordPress modular connector login endpoints for admin cookie issuance and verifies…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 junghyeonkum/cve-2022-24706
Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…
 heisenbergh4x/cve-2008-1930
CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…
 lorenzocamilli/cve-2025-10720-poc
Proof-of-concept exploit for an authentication bypass vulnerability (CWE-565) in WP Private Content Plus v3.6.2, allowing unauthenticated access to…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 akashsingh0454/cve-2026-0257-poc
Passive, read-only remote detection tool for CVE-2026-0257, an authentication bypass in Palo Alto Networks PAN-OS GlobalProtect. Fingerprints PAN-OS…
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…