
CVE-2024-30804
 geozstevenzz/cve-2024-30804
Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
binary-exploitationexploitationpayload-development+3
geozstevenzz/cve-2024-30804Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
 416rehman/razer-lycosa-kernel-lpe-byovd-vulnerability-poc
Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
 kagurazakasanae/mhyprot2drvcontrol
A lib that allows using mhyprot2 driver for enum process modules, r/w process memory and kill process.
 kkent030315/evil-mhyprot-cli
A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
 r1l4-i3pur1l4/cve-2021-1732
Windows kernel privilege escalation exploit for CVE-2021-1732, a Win32k elevation of privilege vulnerability, with techniques inspired by related…
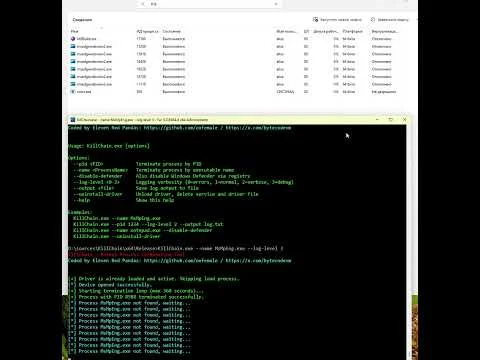 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
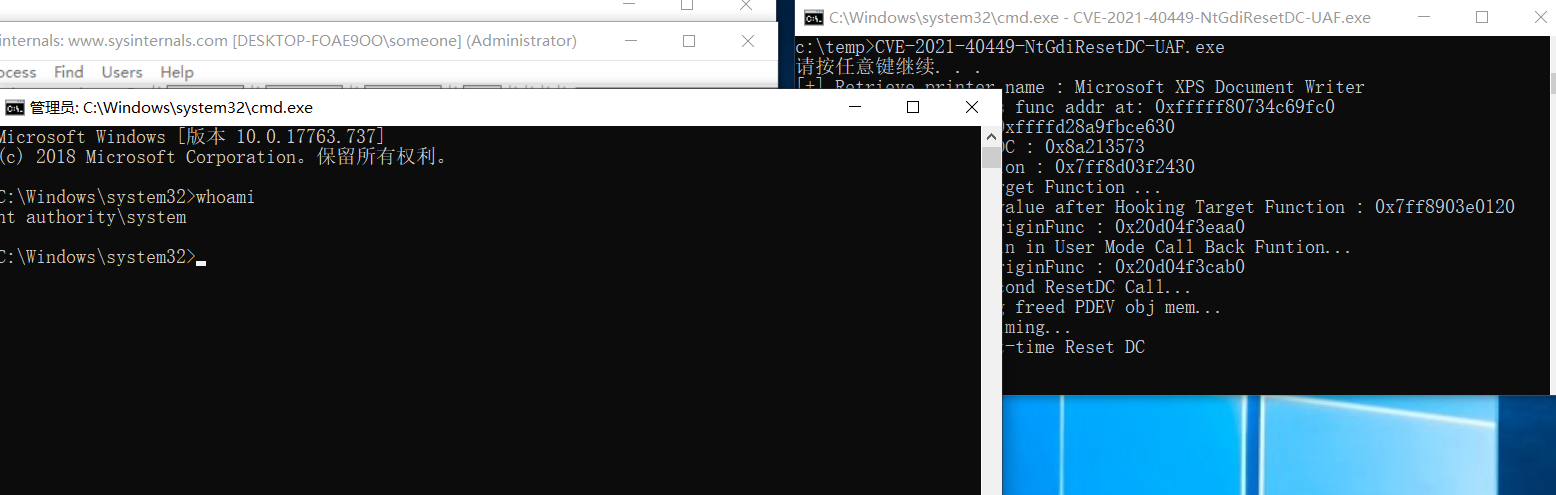 bl0odz/cve-2021-40449-ntgdiresetdc-uaf
Proof-of-concept exploit for CVE-2021-40449, a Windows kernel use-after-free in NtGdiResetDC, demonstrating privilege escalation via user-space…
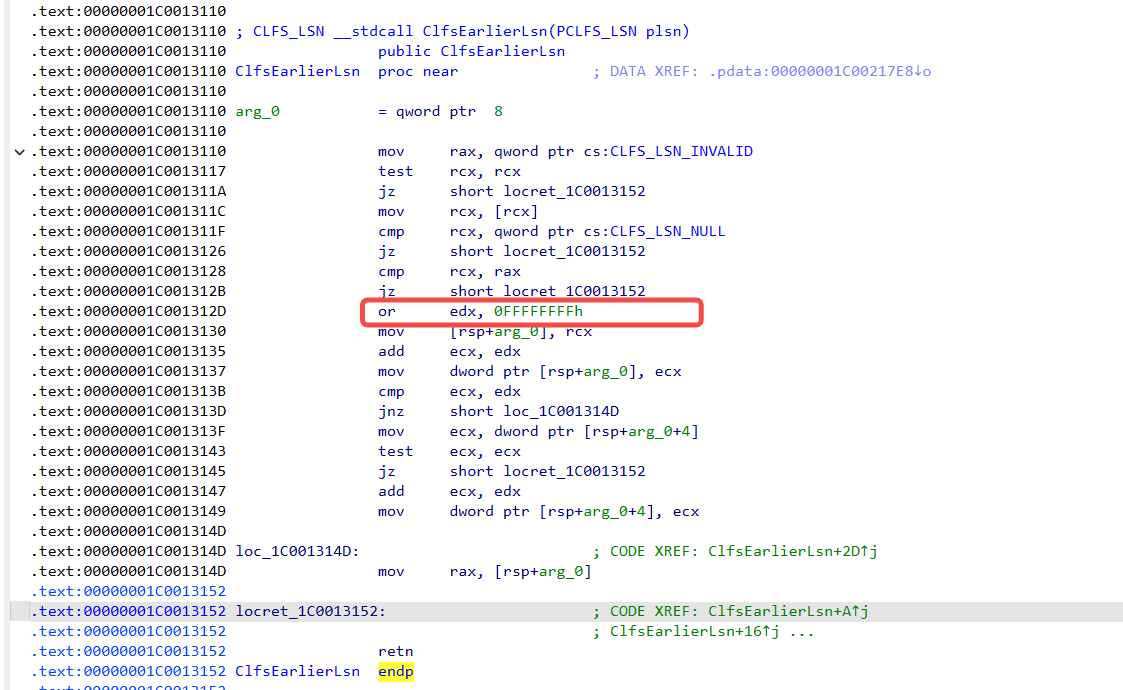 uname1able/cve-2022-24481-analysis
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…
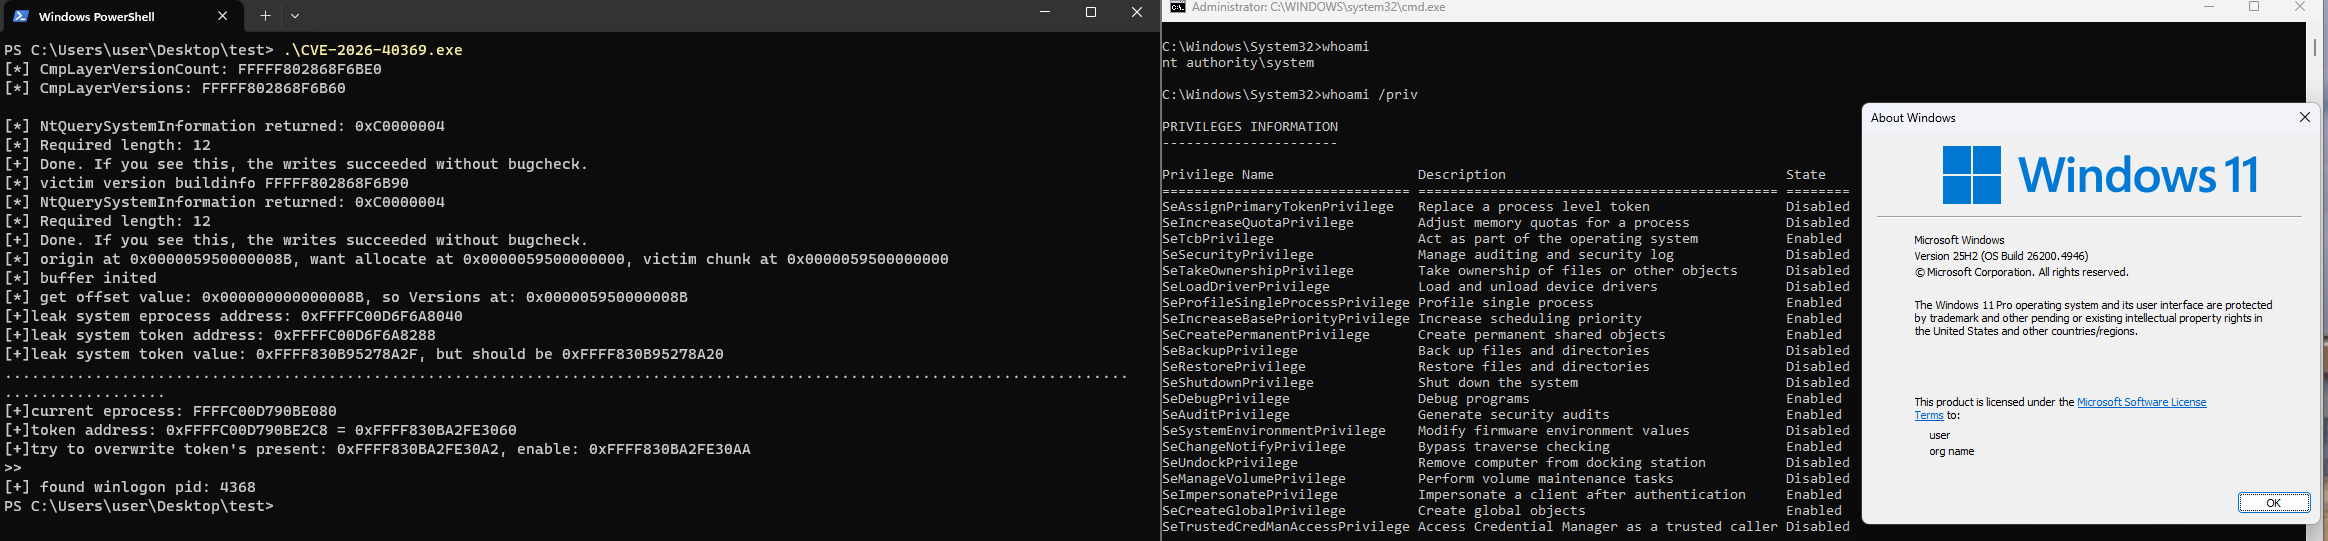 joe1sn/cve_2026_40369
Exploit PoC for CVE-2026-40369 targeting Windows kernel; includes kASLR bypass, heap grooming, remote thread injection, and per-build offsets.
 patrickt2017/cve-2026-19195-poc
CVE-2026-19195 Proof of Concept
 ascotbe/kernelhub
:palm_tree:Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability…
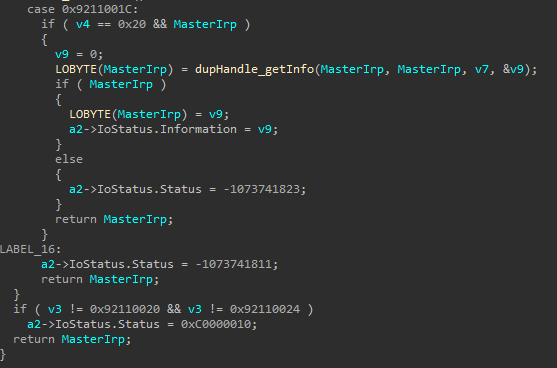 alfarom256/logmeinpochandledup
Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…
 wh04m1001/sysmoneop
PoC for CVE-2022-41120/CVE-2022-44704: arbitrary file delete/write in Sysmon via ClipboardChange RPC leading to local privilege escalation on Windows.
 leandrofleury/cve-2023-21768
PoC exploit for CVE-2023-21768, a Windows kernel elevation-of-privilege vulnerability, demonstrating local privilege escalation via crafted kernel…
 pawlokk/mindmanager-poc
public disclosure