

waf-dojo
 nishikawaakira/waf-dojo
Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
cloud-securityctfdefensive-tools+7
18
nishikawaakira/waf-dojoHands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
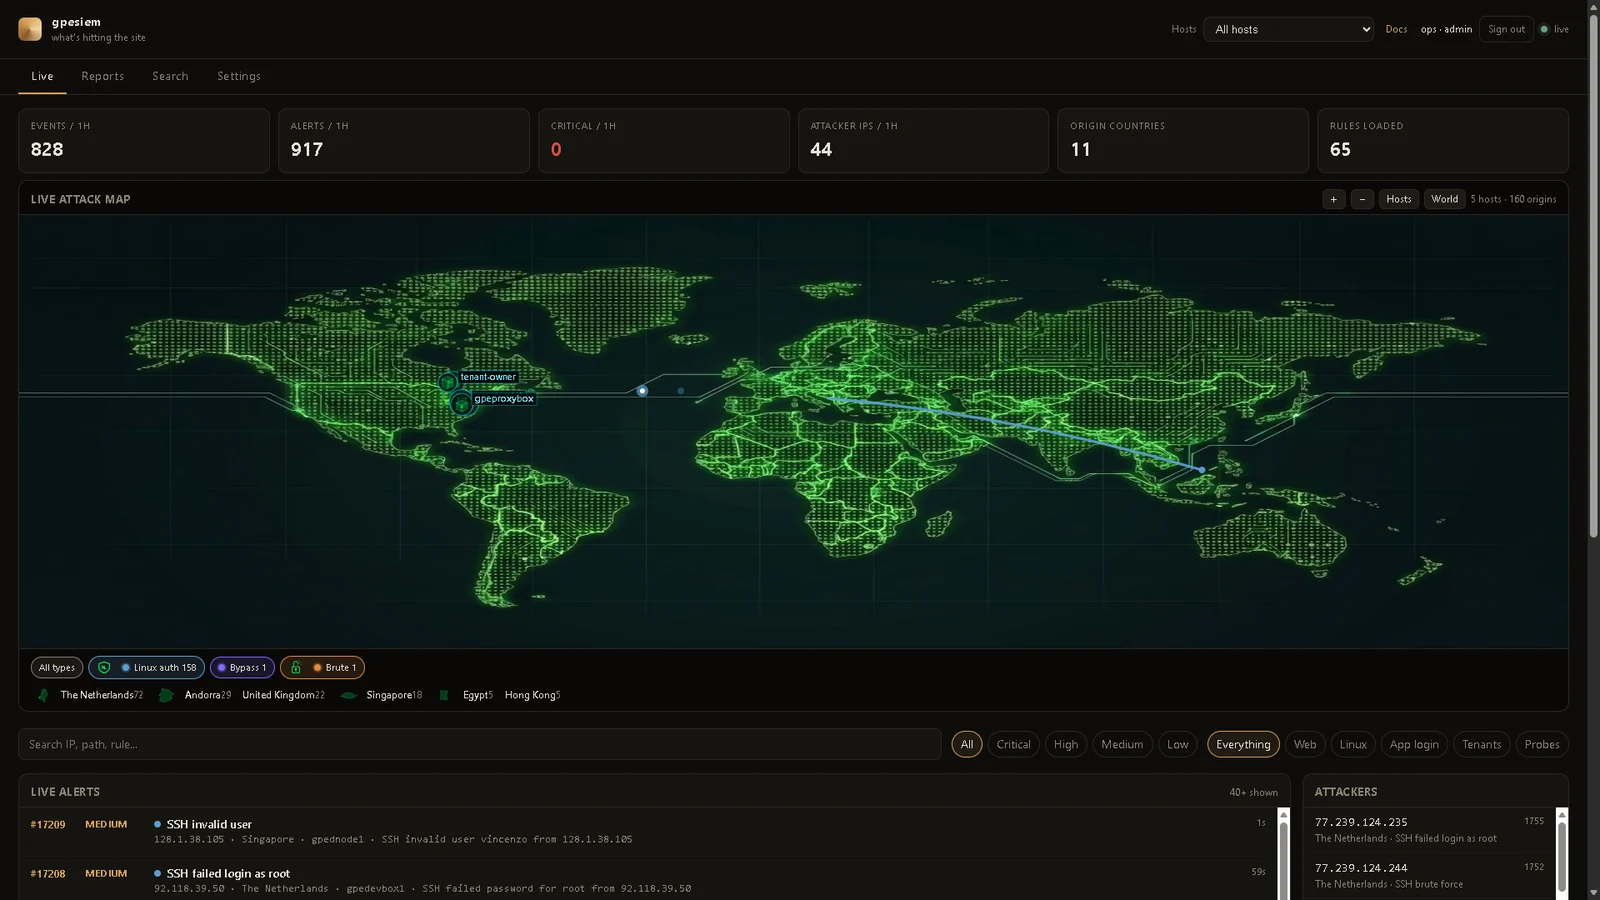 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
 maximofernandezriera/cve-2021-44228
Proof-of-concept exploit for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including payload compilation, LDAP…
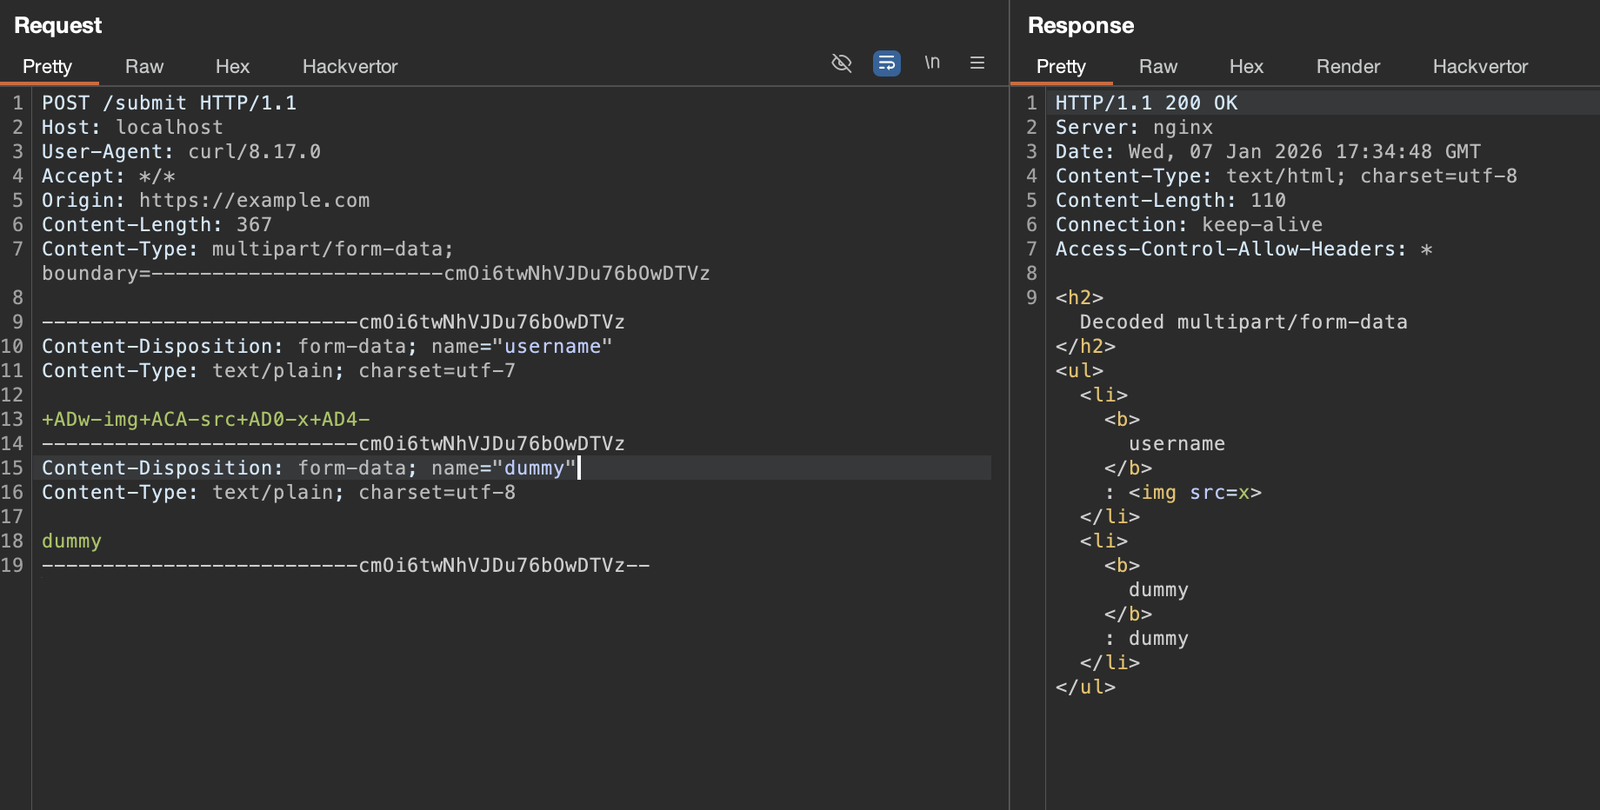 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 exploreunknowed/cve-2026-24306
Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…
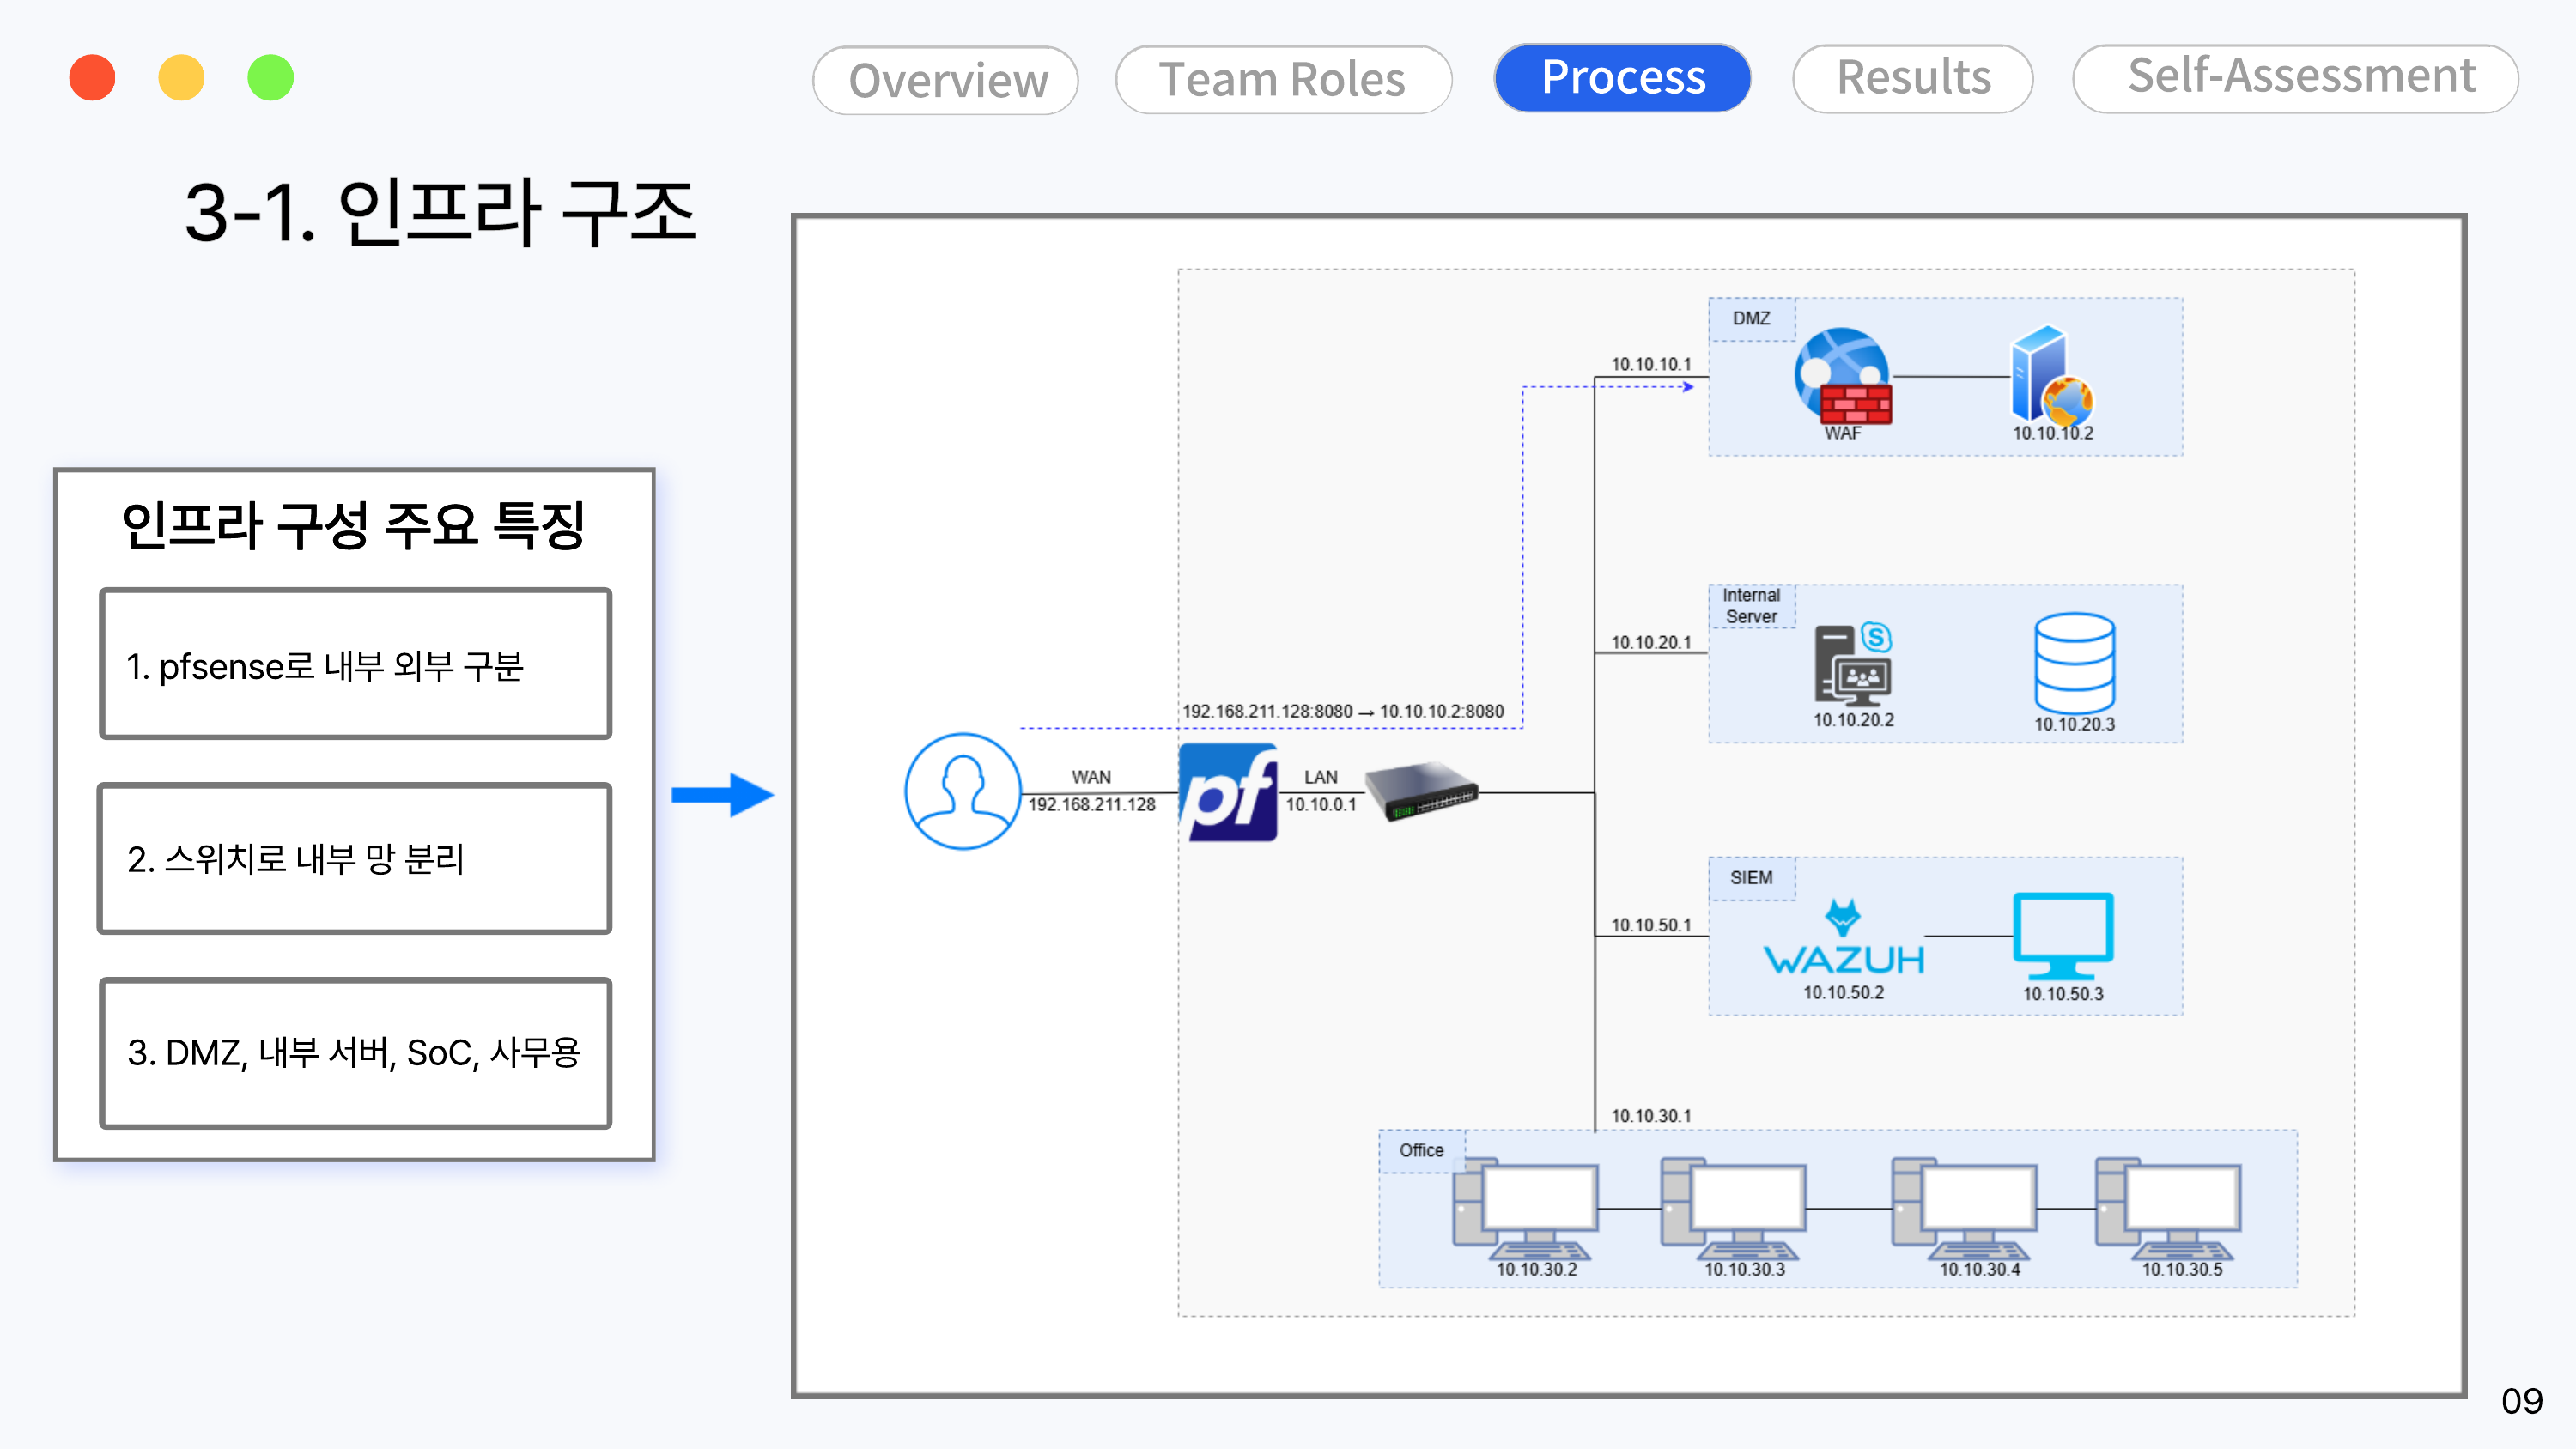 kevin9480/security_incident_report
React2Shell(CVE-2025-55182) 취약점 기반 침해 시나리오를 재현하고, Wazuh/Sysmon/Coraza WAF 로그로 침해사고를 분석·대응한 DFIR 프로젝트
 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
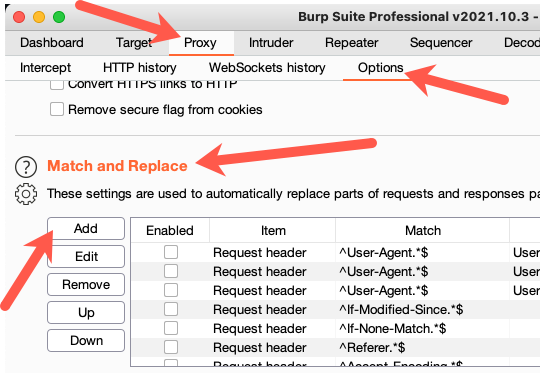 bishopfox/imperva_gzip_waf_bypass
Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
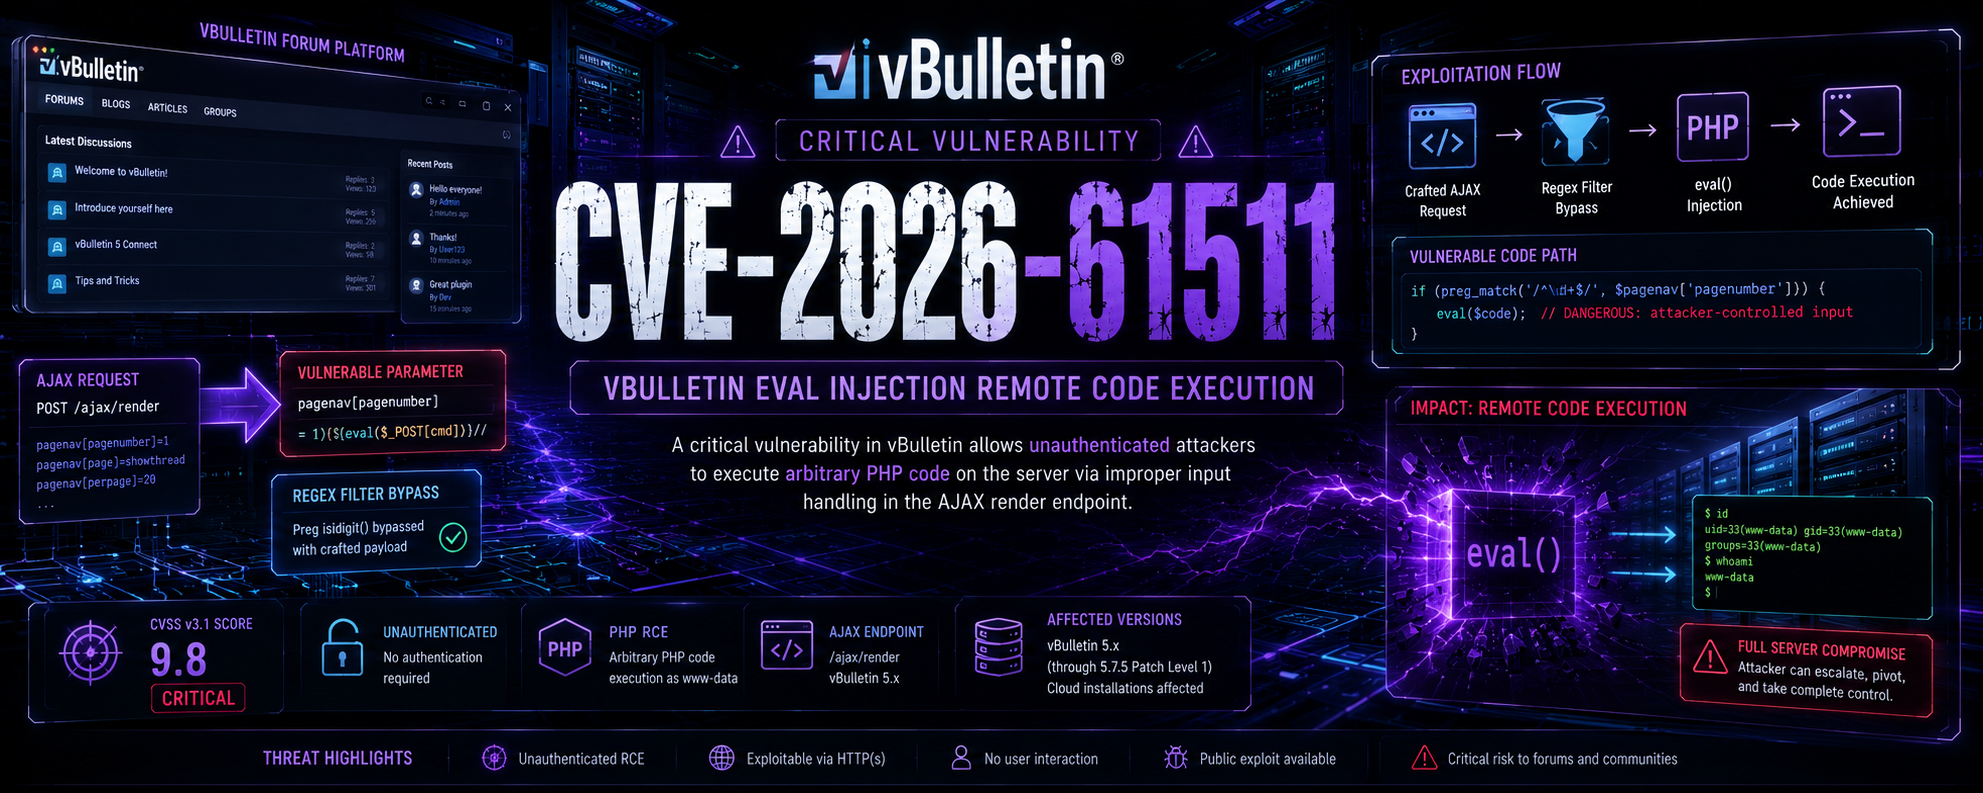 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
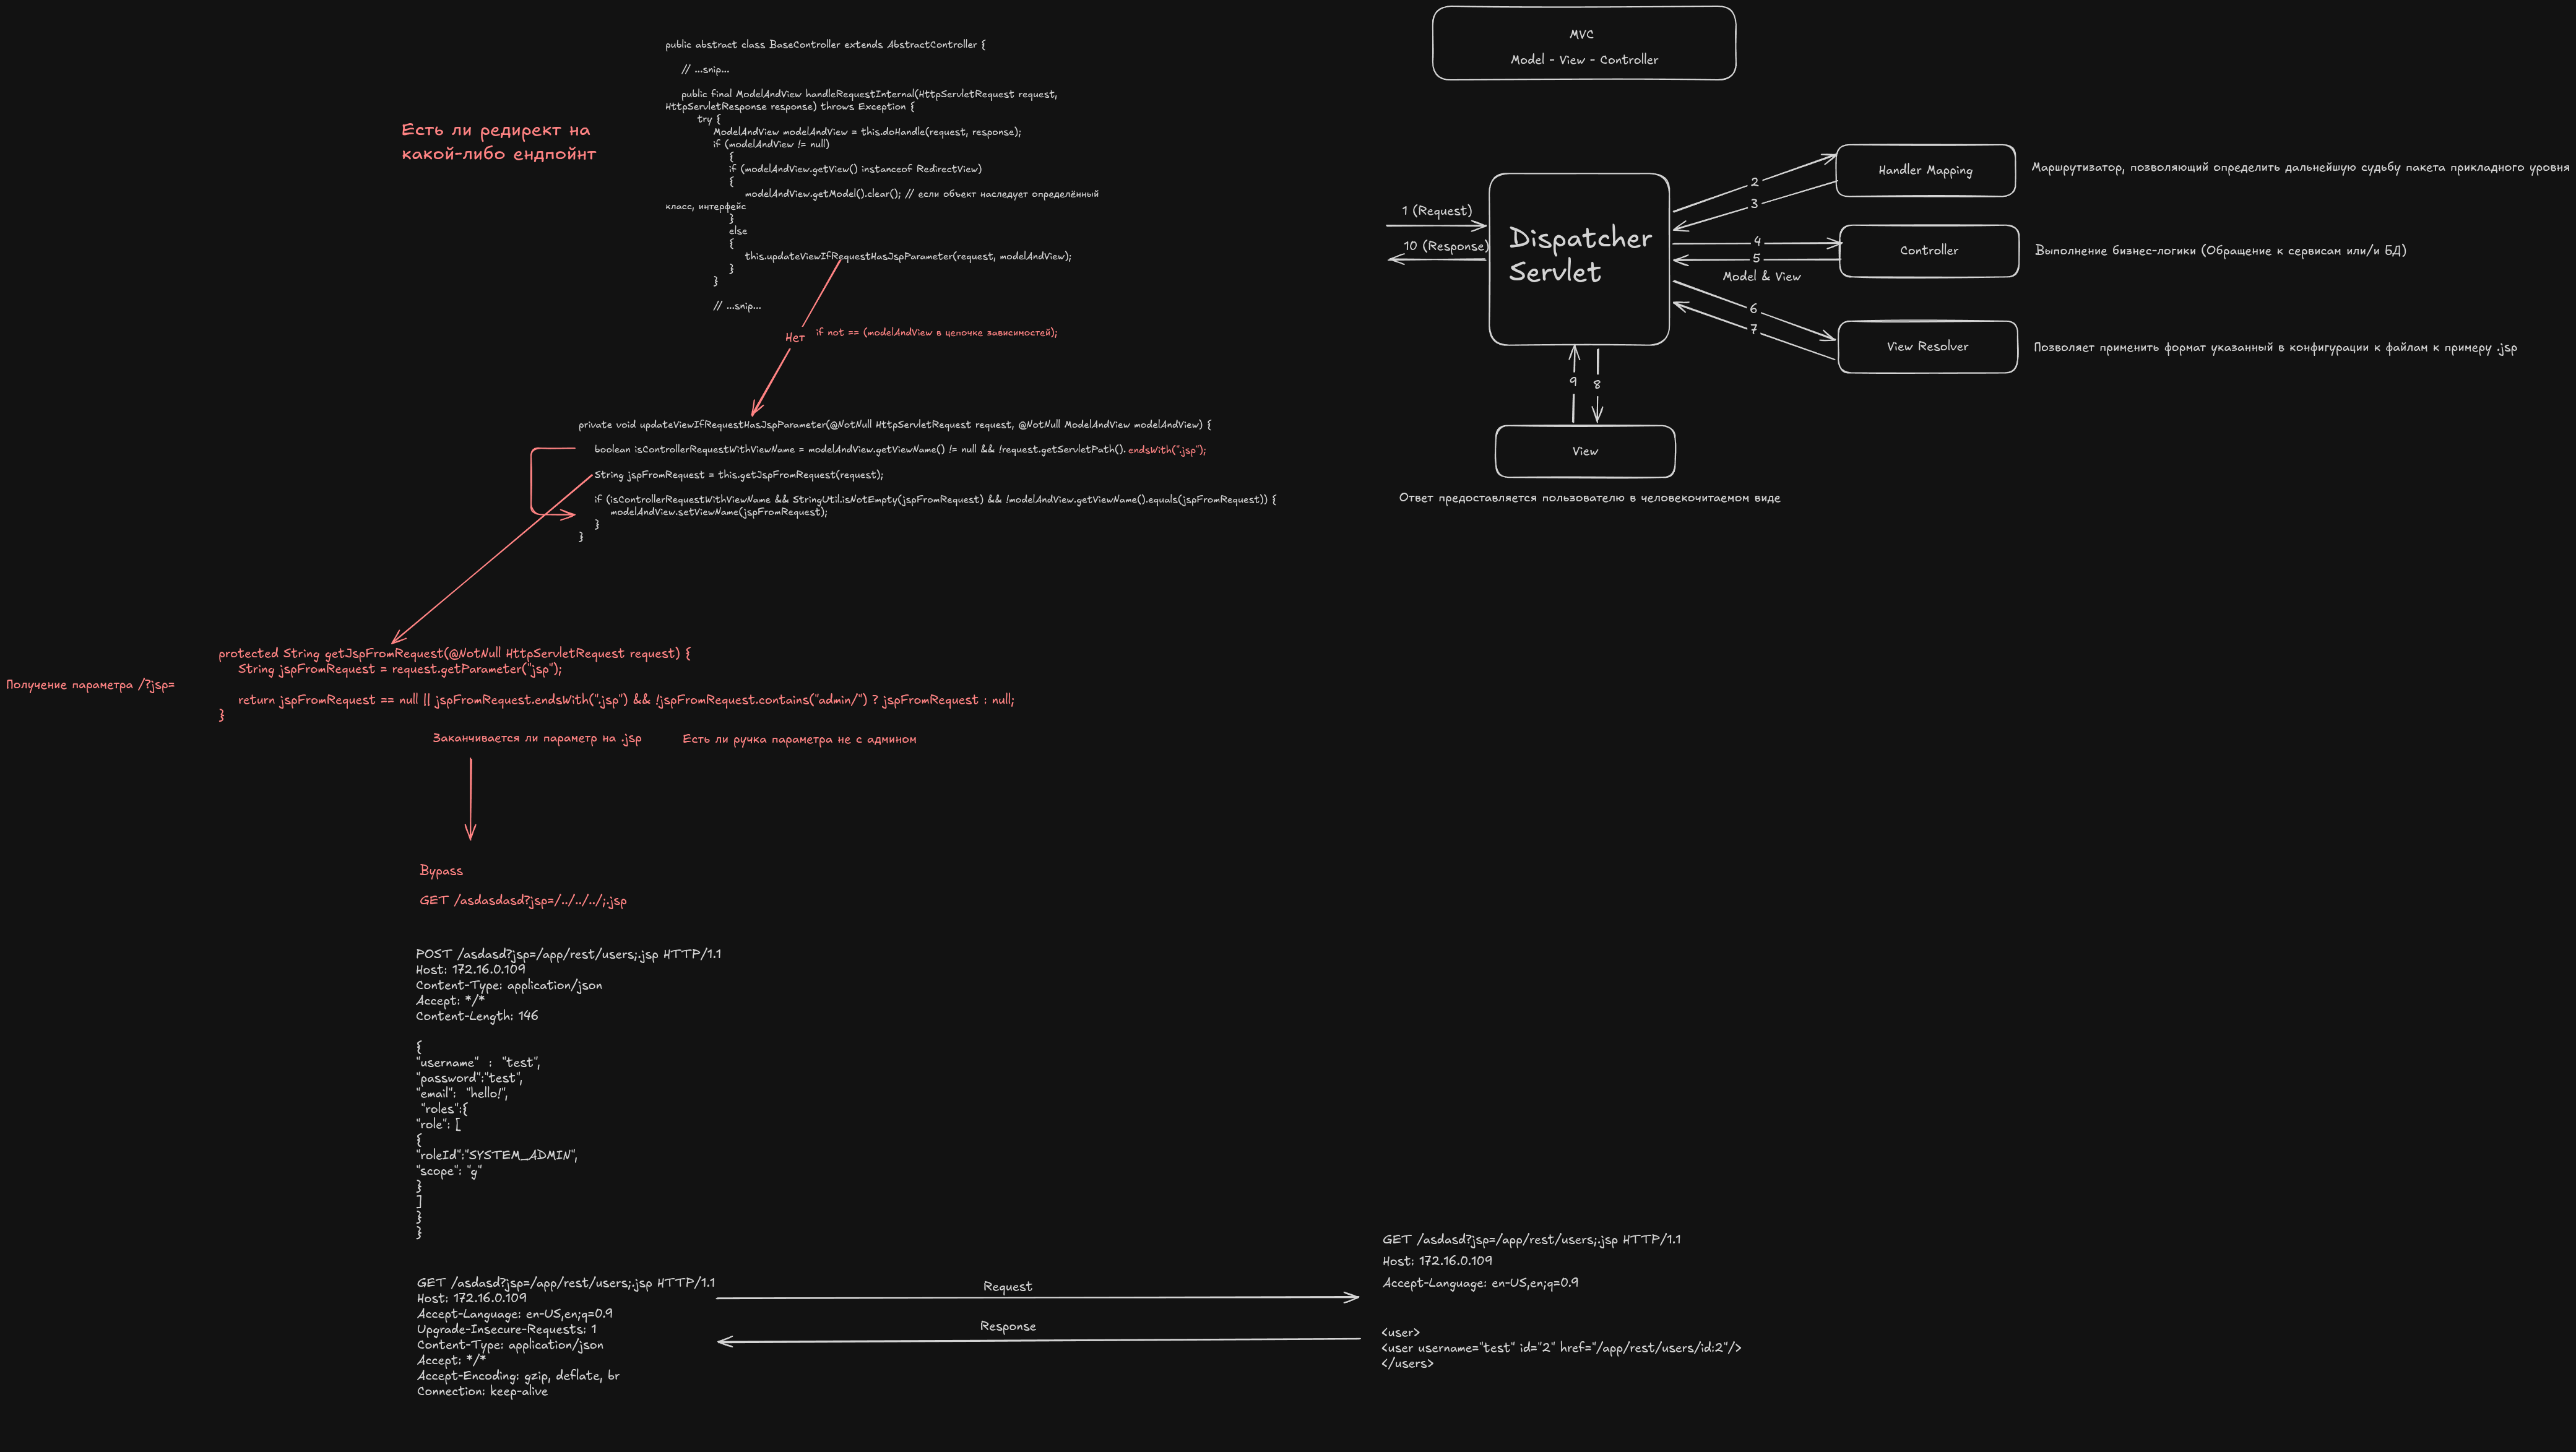 kxom9ks/cve-2024-27198-teamcity
Proof-of-concept exploit and mitigation guide for CVE-2024-27198 authentication bypass in JetBrains TeamCity, including WAF regex patterns.
 azurit/crsprober
Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.