

PIIHunter
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
ai-securitydatabase-securitydata-exfiltration+6
2
owasp/piihunterScans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 cumakurt/mudos
Command-line multi-vector DDoS test tool with 129 volumetric, protocol, application, and amplification attack vectors for authorized resilience…
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 faizanali8232/cve-exploit-research-development
A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…
 babydessy/cve-2024-2876
Proof-of-concept for CVE-2024-2876, an unauthenticated SQL injection in the Email Subscribers WordPress plugin, with dork queries and a working…
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 4ybrick/cve-2026-79303
Proof-of-concept for CVE-2026-79303, a critical boolean-blind SQL injection in Kaiten affecting order_by and order_direction parameters, with…
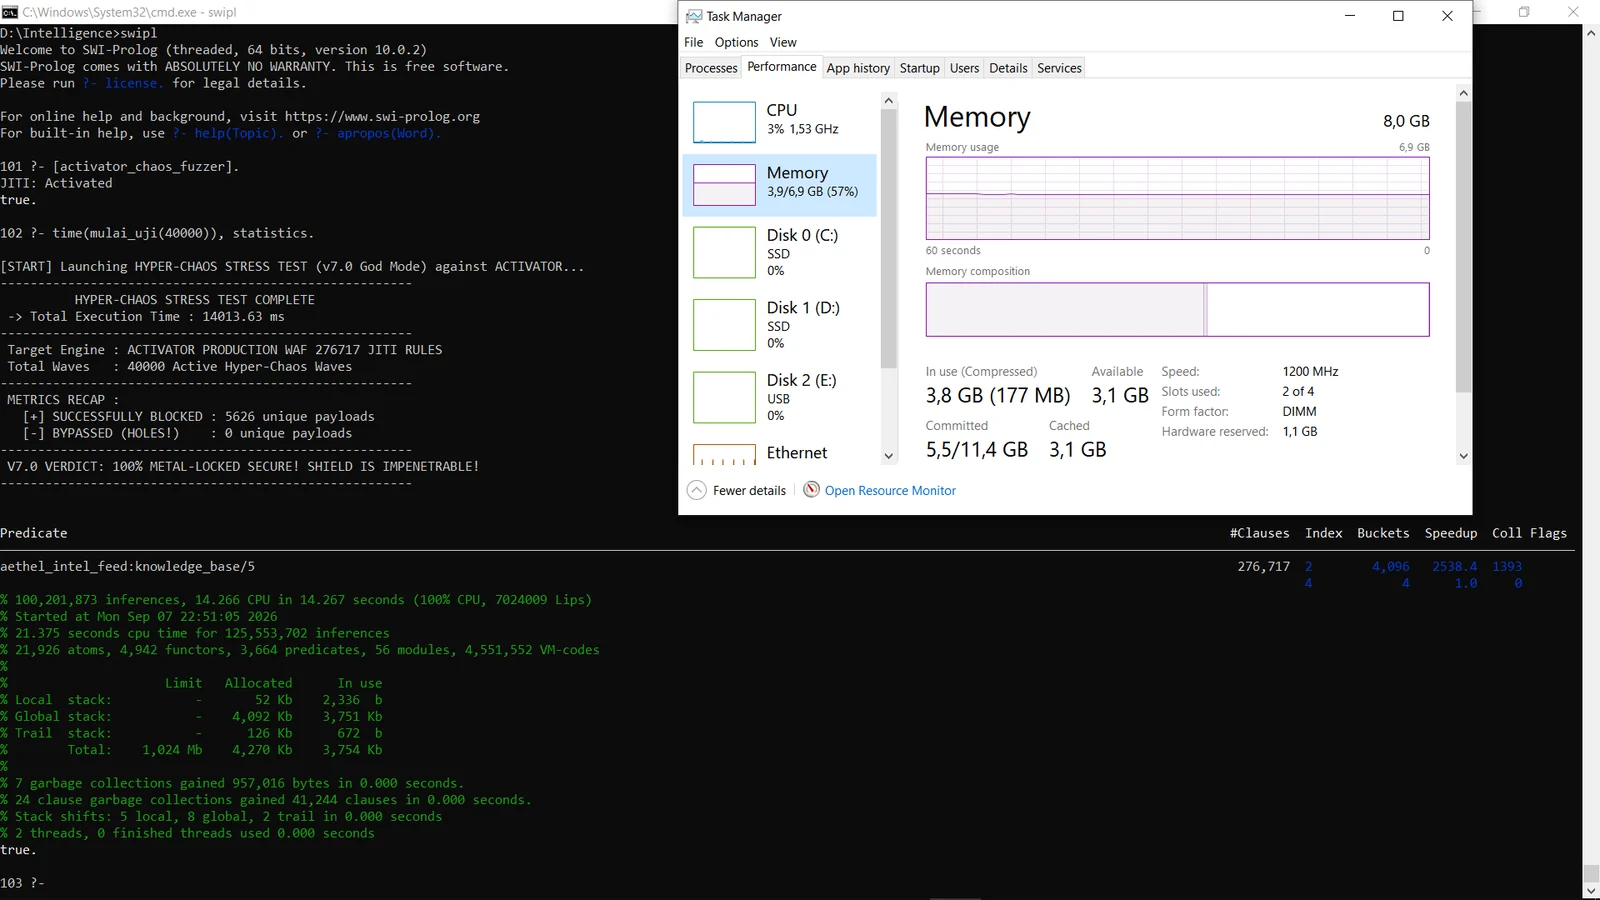 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 linan-oo/cve-2026-52307
Proof-of-concept for CVE-2026-52307, an authenticated stored XSS in 1CMS v5.6 Column Management, with reproduction steps and impact analysis.
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…
 dannydoodlesstory/evm-audit-helpers
Collection of Solidity snippets and Foundry scripts for smart contract security audits
 db-ol/cuaharm
Benchmark for evaluating safety risks of computer-using agents, with 104 realistic misuse scenarios across seven malicious categories, supporting…
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 blinky-keys/cve-2026-48060
Proof-of-concept exploit and vulnerable application demonstrating an HTML injection vulnerability in Litestar 2.21.0 via CSRF token, with Docker…