Windows-Kernel-Exploitation

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)

Kernel Arbitrary Read Vulnerability + Superfetch EOP based on reacher from https://starlabs.sg/blog/2022/06-trying-to-exploit-a-windows-kernel-arbitra…

Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.

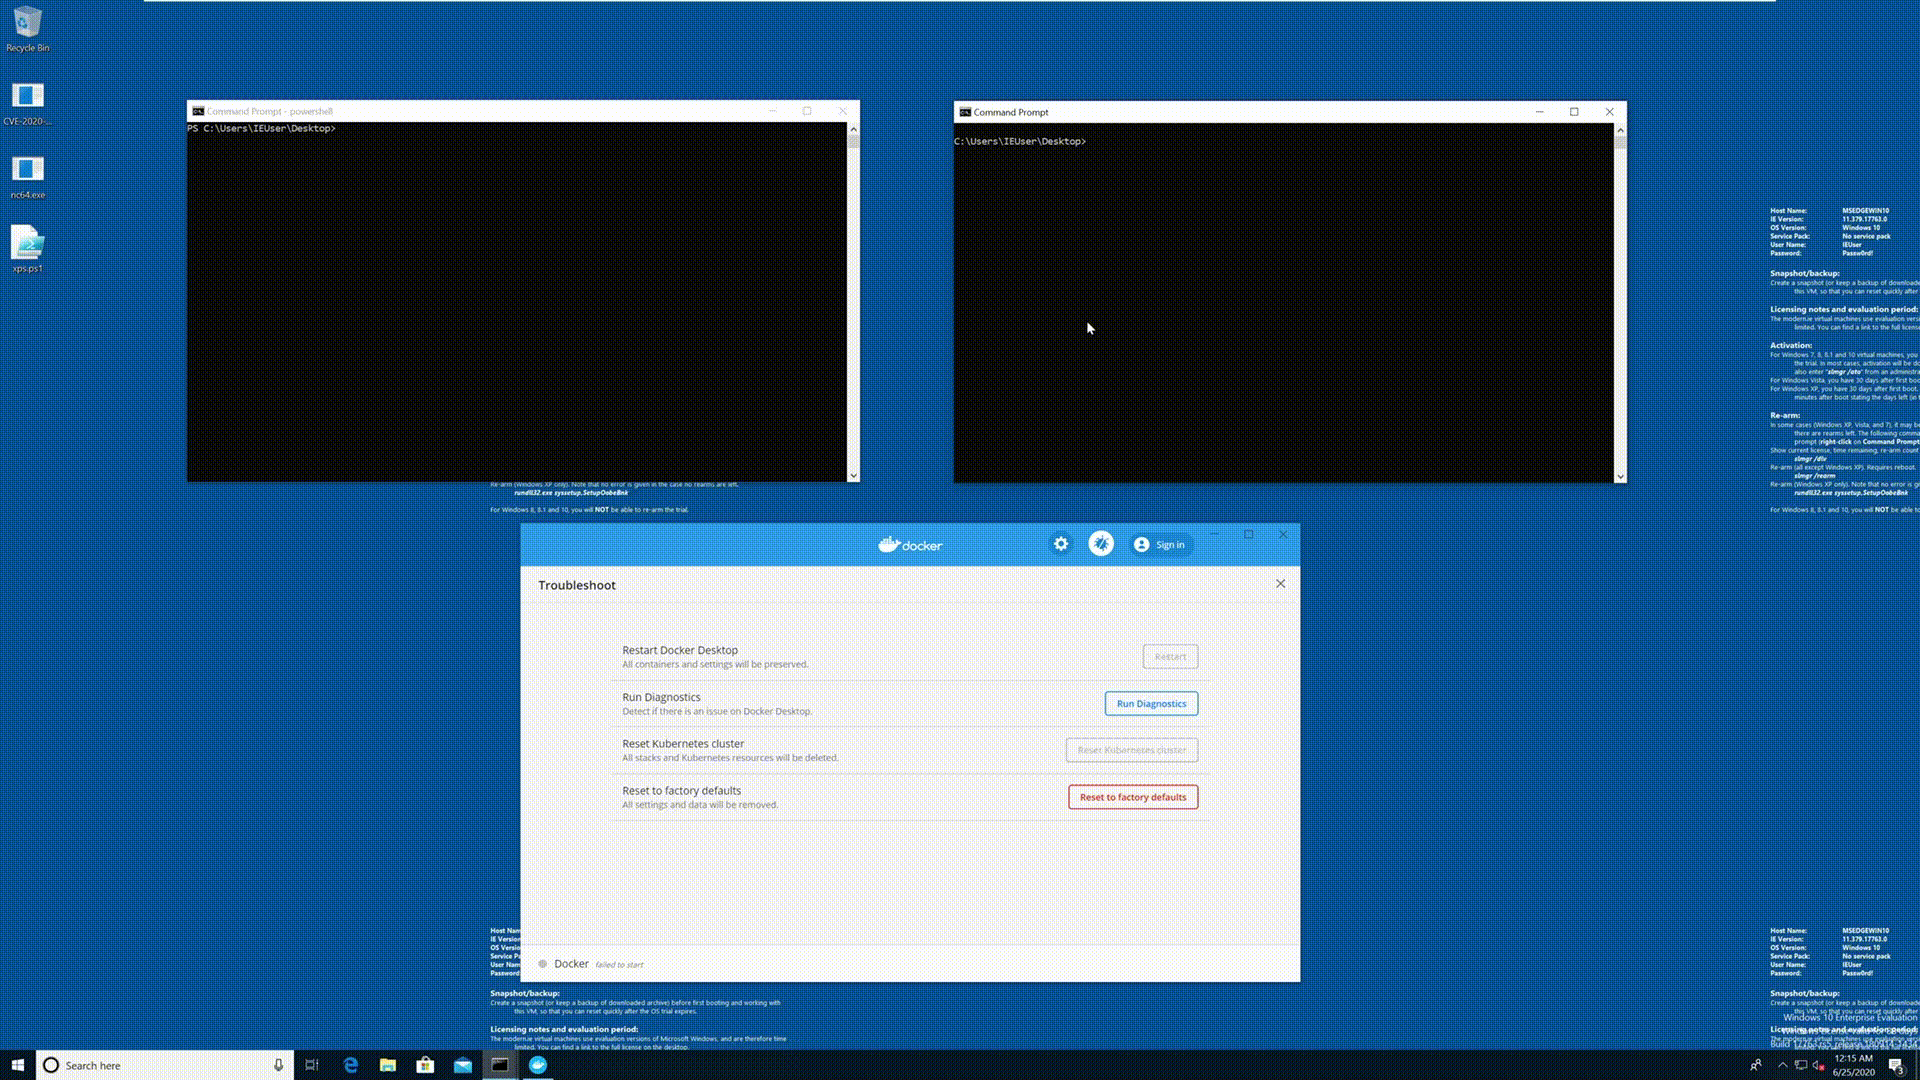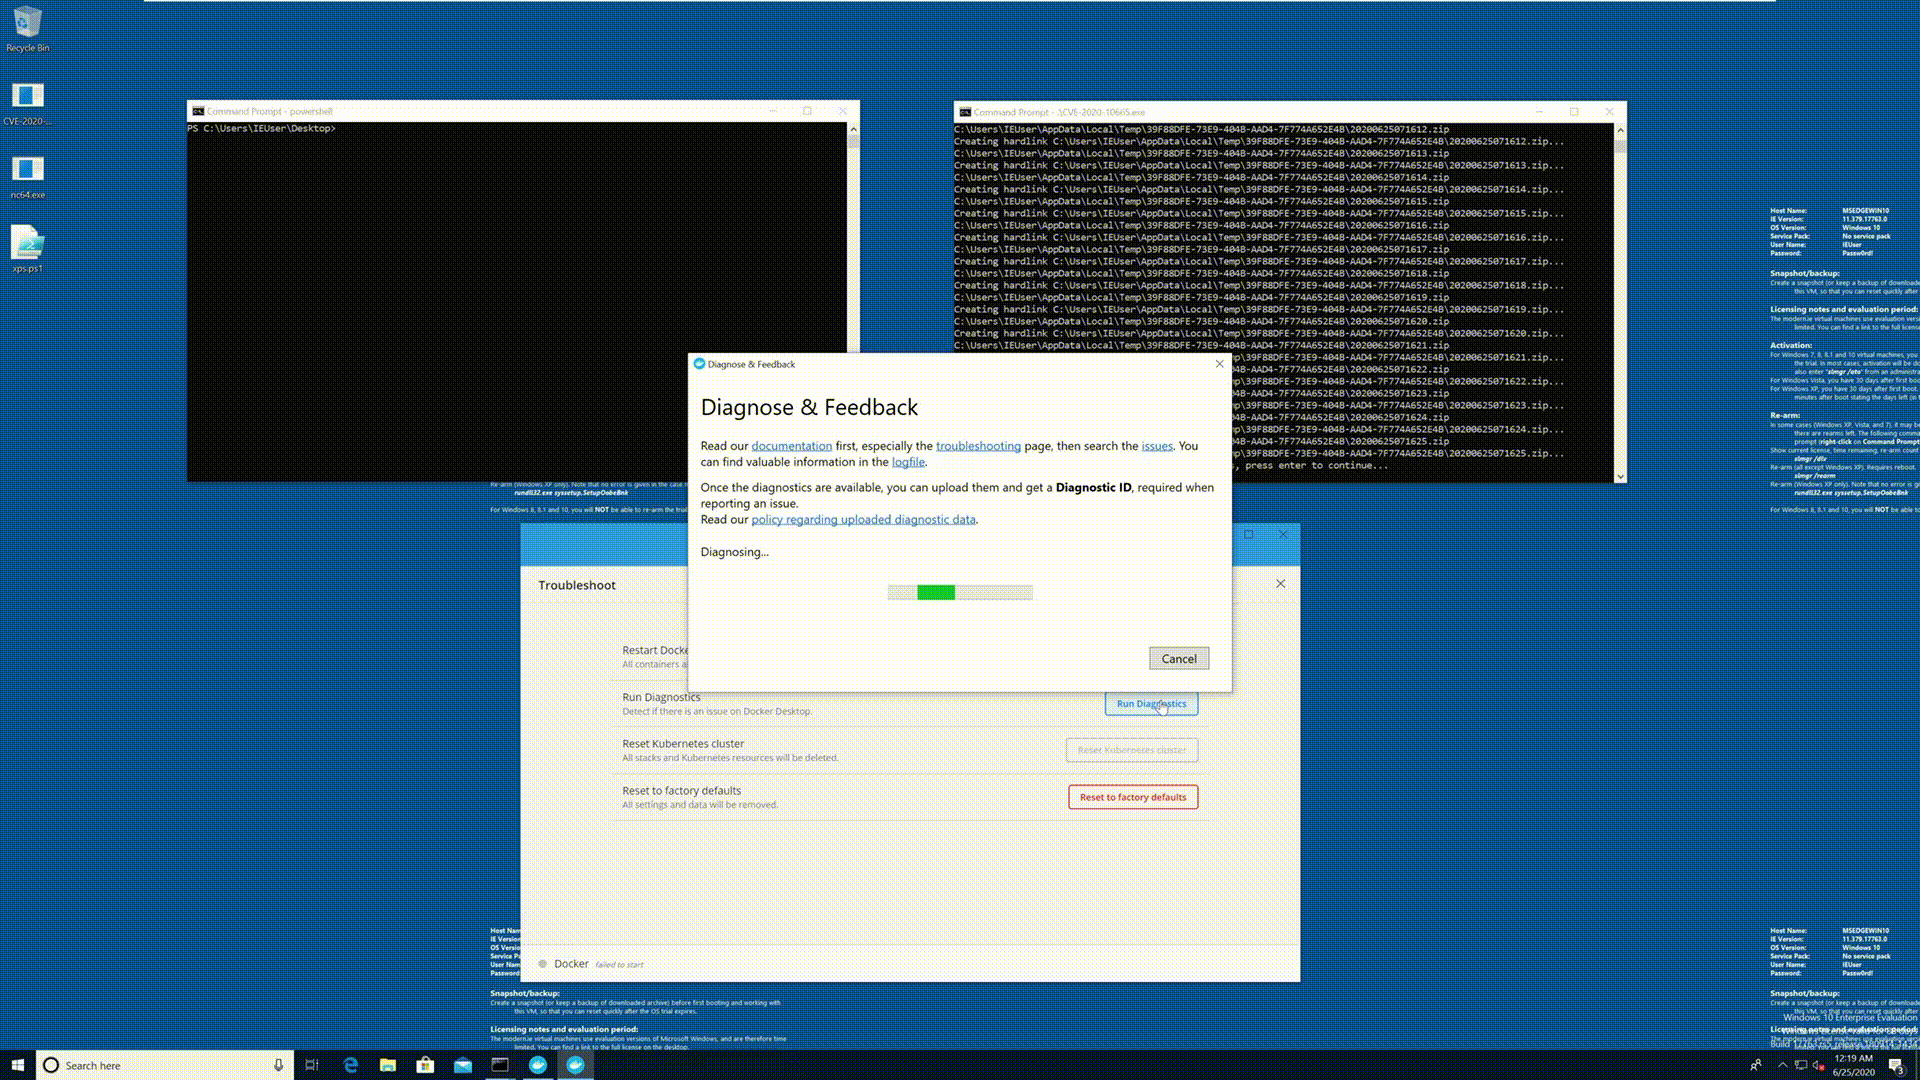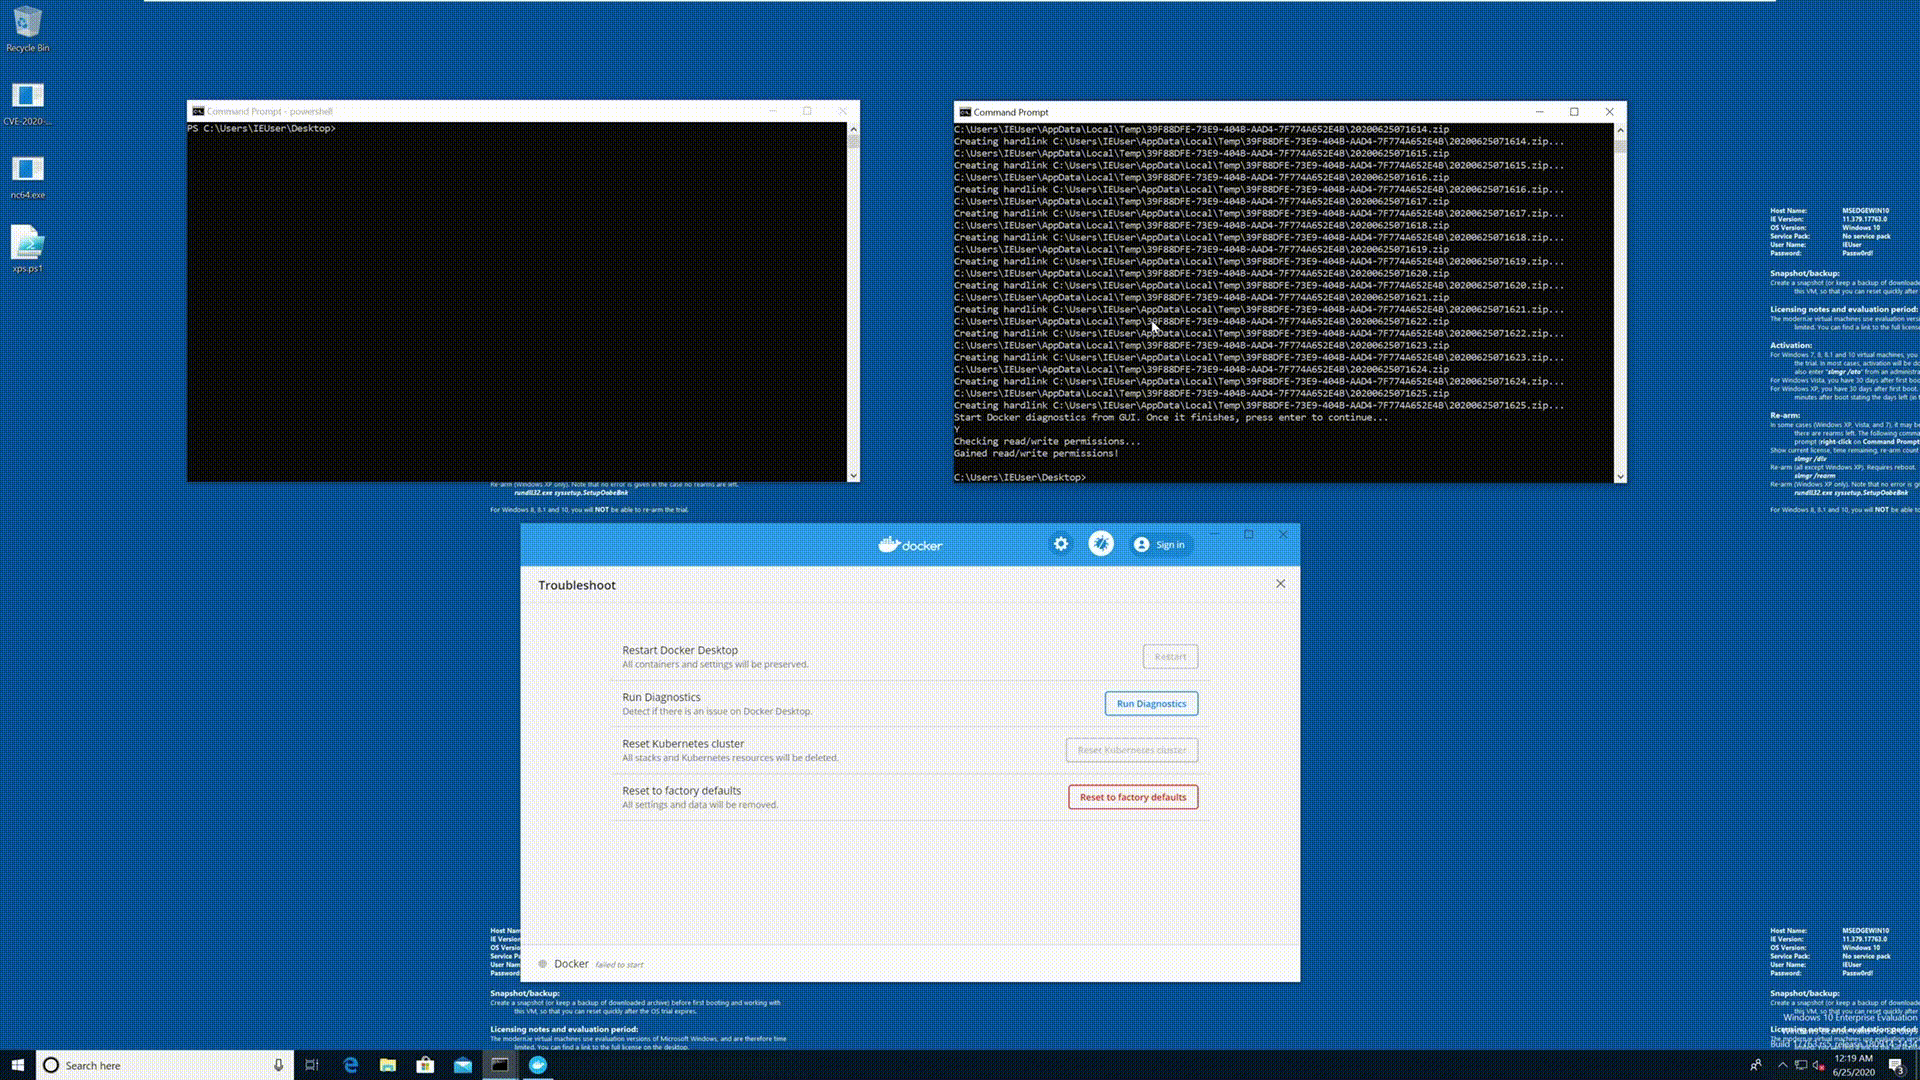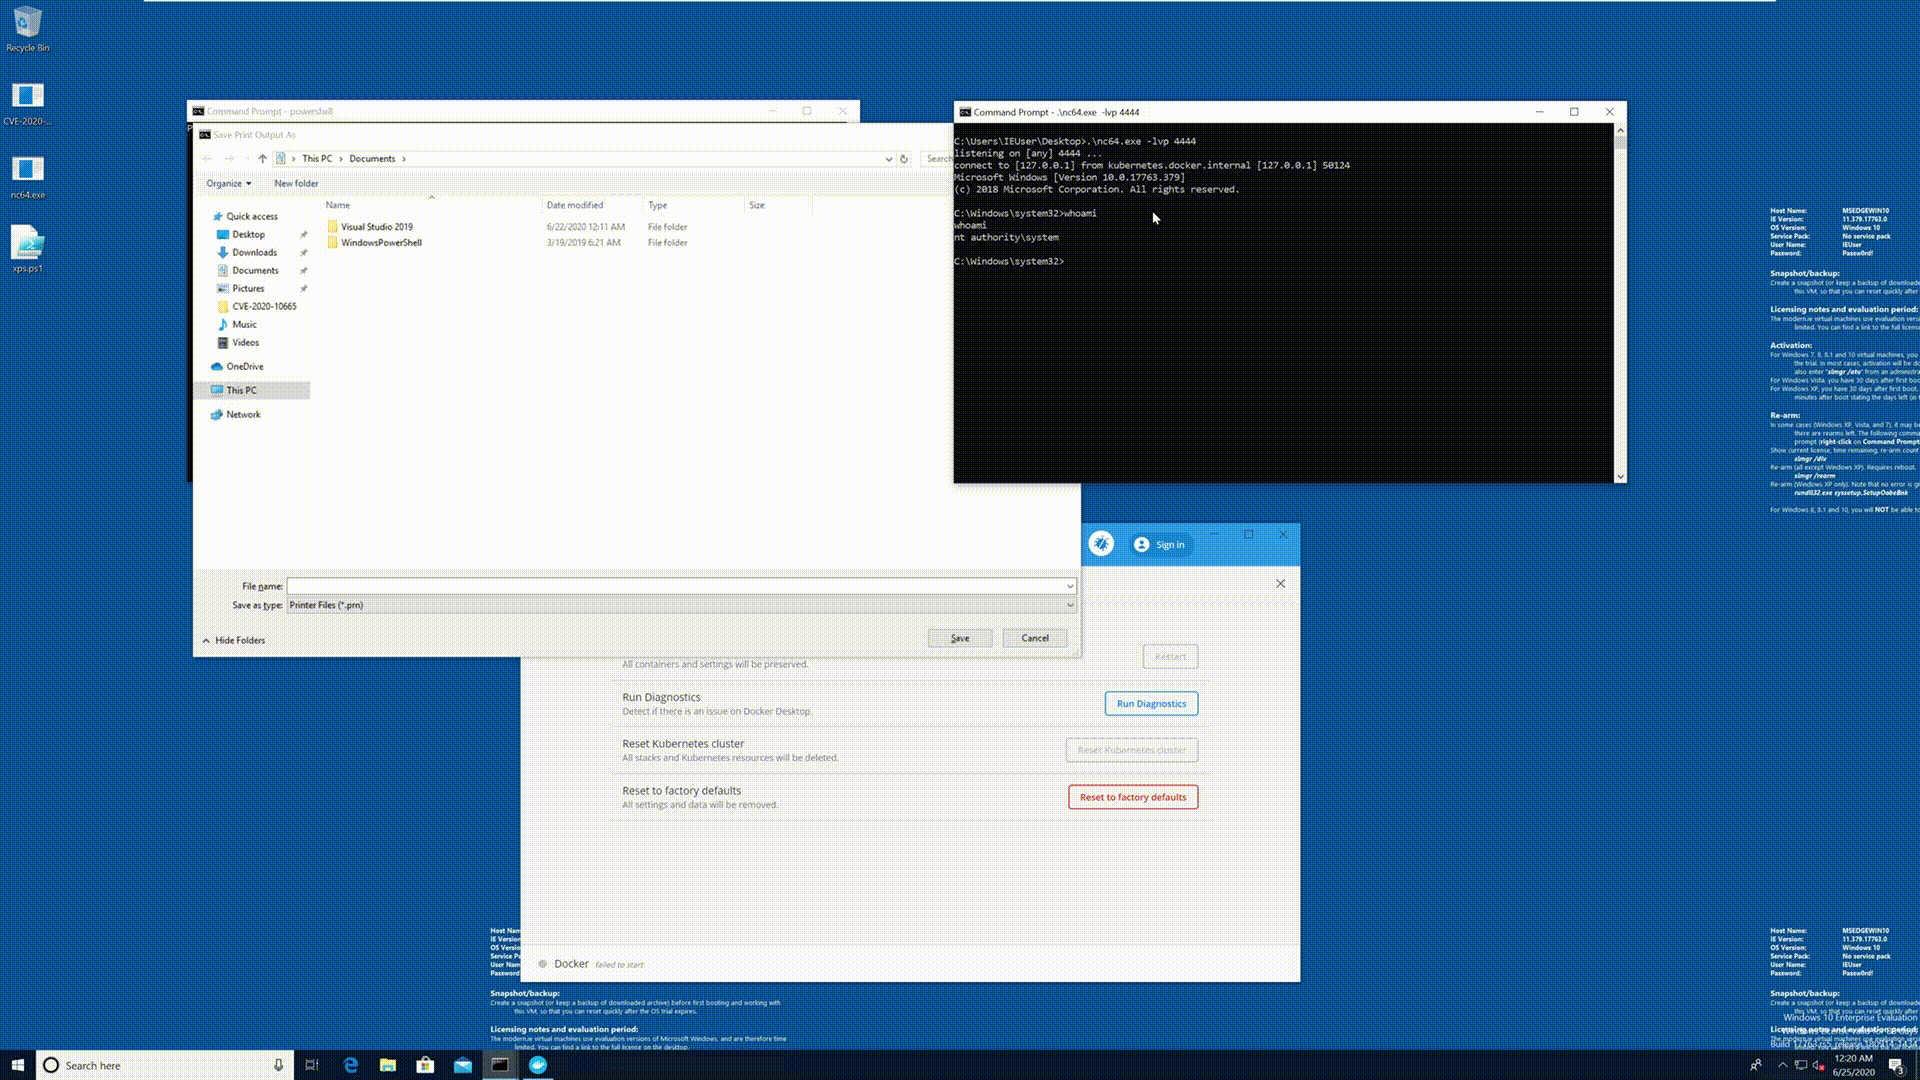
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation

This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250

Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943

Windows POC for CVE-2021-34427 affecting Birt Viewer

stack based buffer overflow in MsIo64.sys, Proof of Concept Local Privilege Escalation to nt authority/system


LLVM based static binary analysis framework

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…


Proof-of-concept exploit for PreAuth RCE in ManageEngine ServiceDesk Plus (CVE-2021-44077). Uploads and executes arbitrary Windows executables on…

Scanner for Windows Print Spooler service vulnerability CVE-2021-34527, based on cube0x0's PoC, enabling detection of exploitable targets.

Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices

proof of concept for CVE-2020-0601

Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.