
CVE-2026-100740
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
embedded-systems-securityexploitationfirmware-analysis+6
1
murrez/cve-2026-100740Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 nccgroup/upnp-pentest-toolkit
UPnP Pentest Toolkit for Windows
 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 azurit/crsprober
Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework
 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
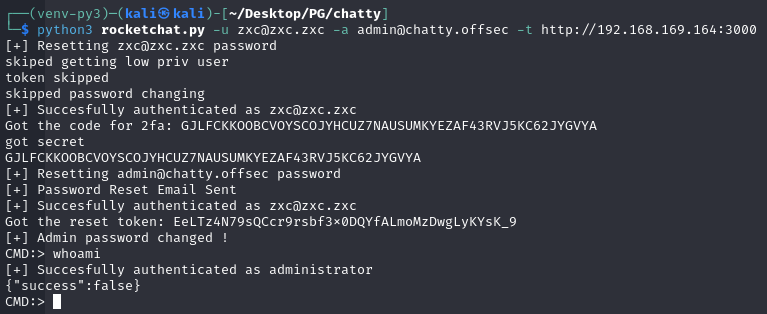 yoohhuu/rocket-chat-3.12.1-poc-cve-2021-22911-
Proof-of-concept exploit for CVE-2021-22911 targeting Rocket.Chat 3.12.1. Automates privilege escalation from low-privileged user to administrator…
 stavrosgns/text4shellpayloads
This project includes a python script which generates malicious commands leveraging CVE-2022-42889 vulnerability
 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045