
CVE-2026-80844
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
binary-exploitationeducationexploitation+3
0xblackash/cve-2026-80844Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 manizada/dirtyah6
Python PoC for CVE-2026-80844: IPv6 AH6 skb corruption and ESP-in-UDP decryption to overwrite /etc/pam.d/su and escalate to root on Linux.
 hibanitt/cve-2024-38063
In-depth technical analysis and proof-of-concept for CVE-2024-38063, a critical Windows IPv6 kernel RCE. Includes root-cause breakdown, Scapy-based…
 mbanyamer/cve-2026-26988-librenms-sqli
Proof-of-concept exploit for unauthenticated SQL injection in LibreNMS ajax_table.php, demonstrating time-based and boolean-based blind injection…
 cryptogenic/ps5-ipv6-kernel-exploit
An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 toperaproject/topera
IPv6 analysis tool: the other side
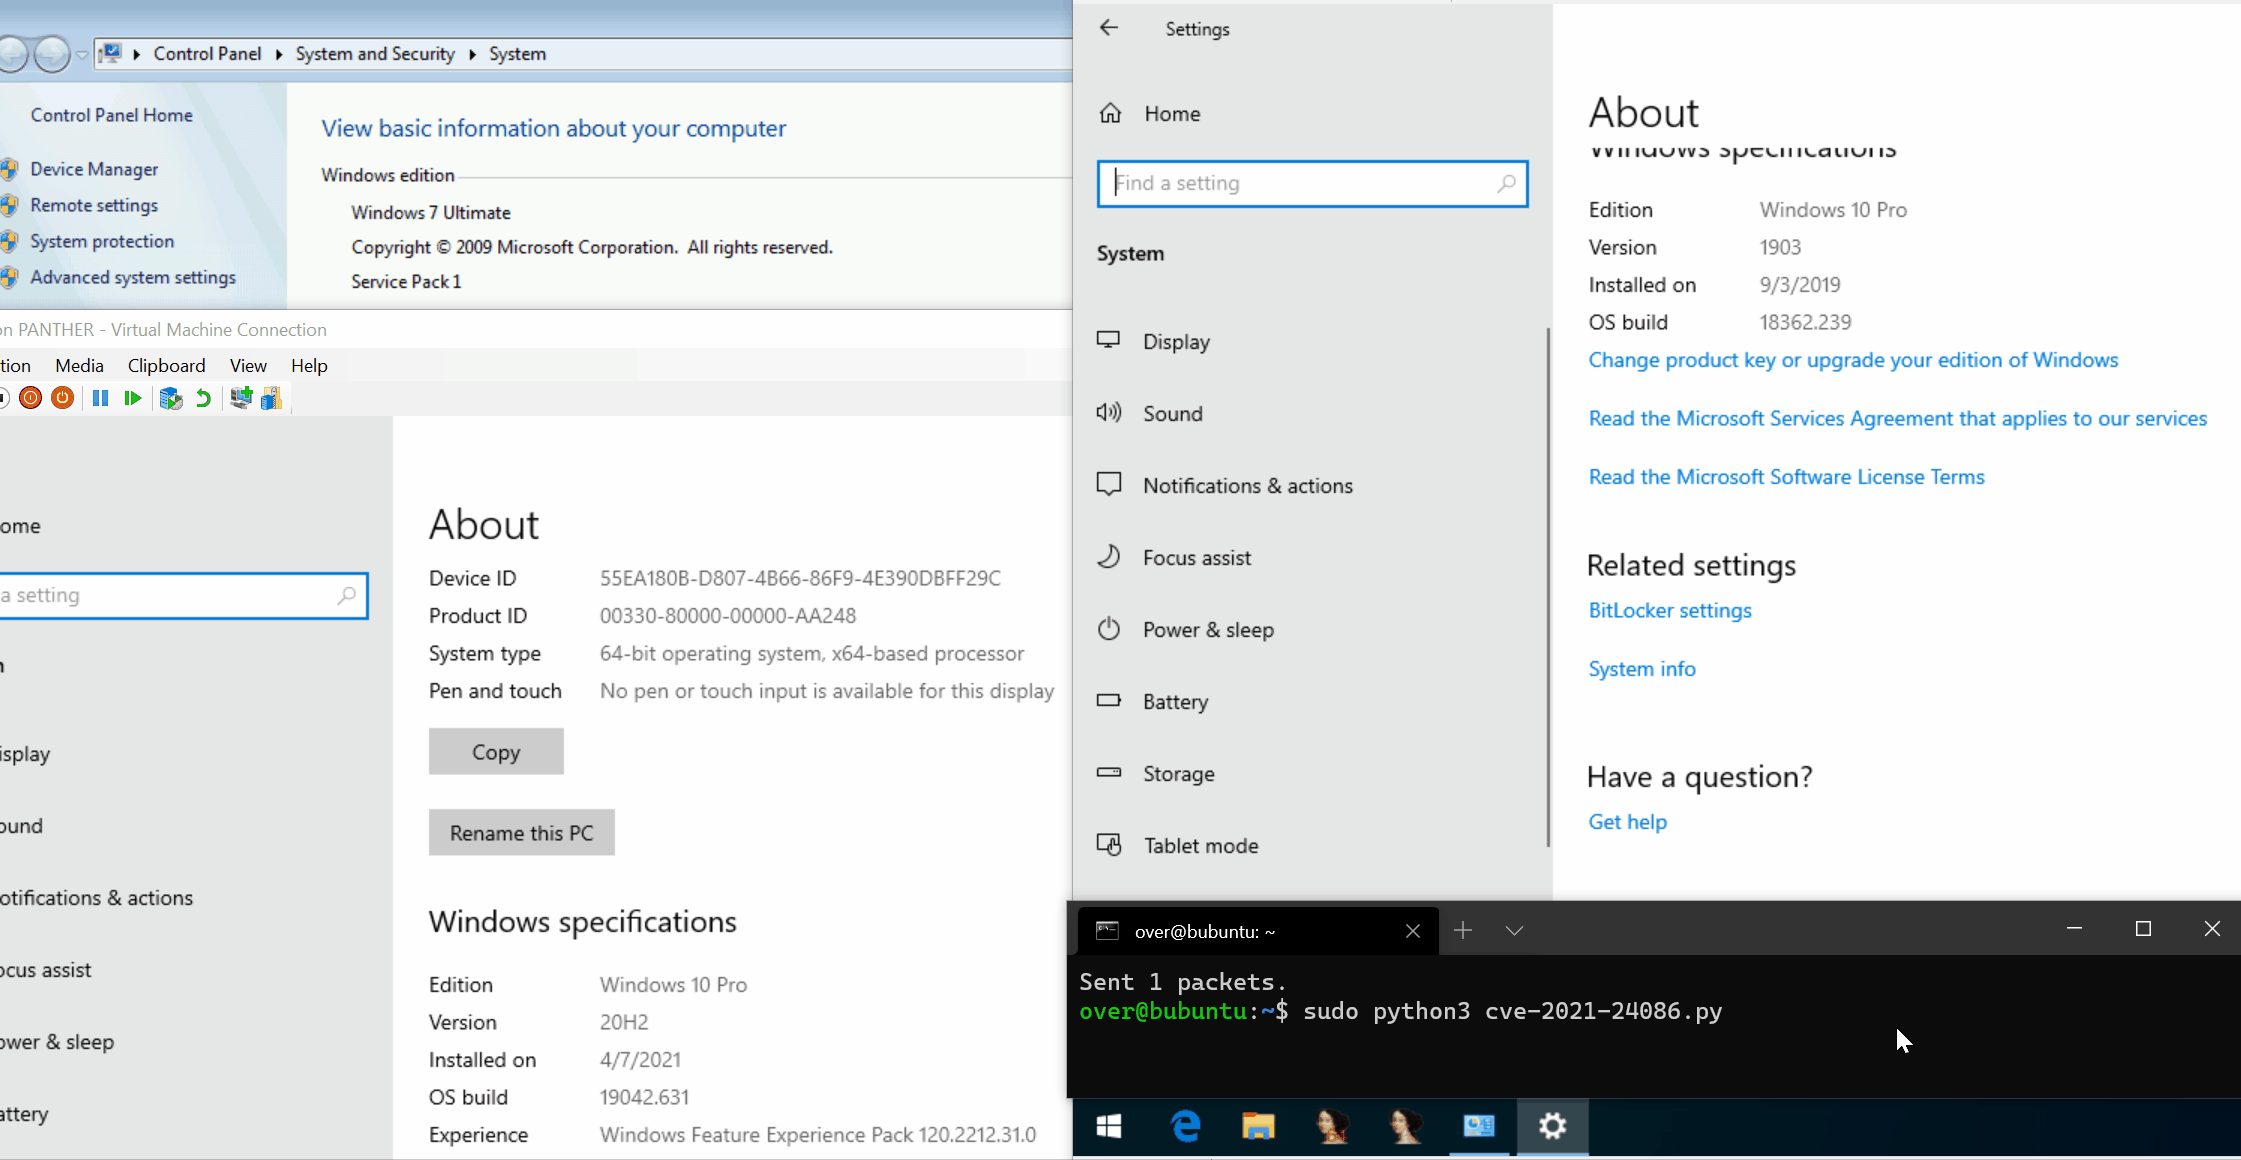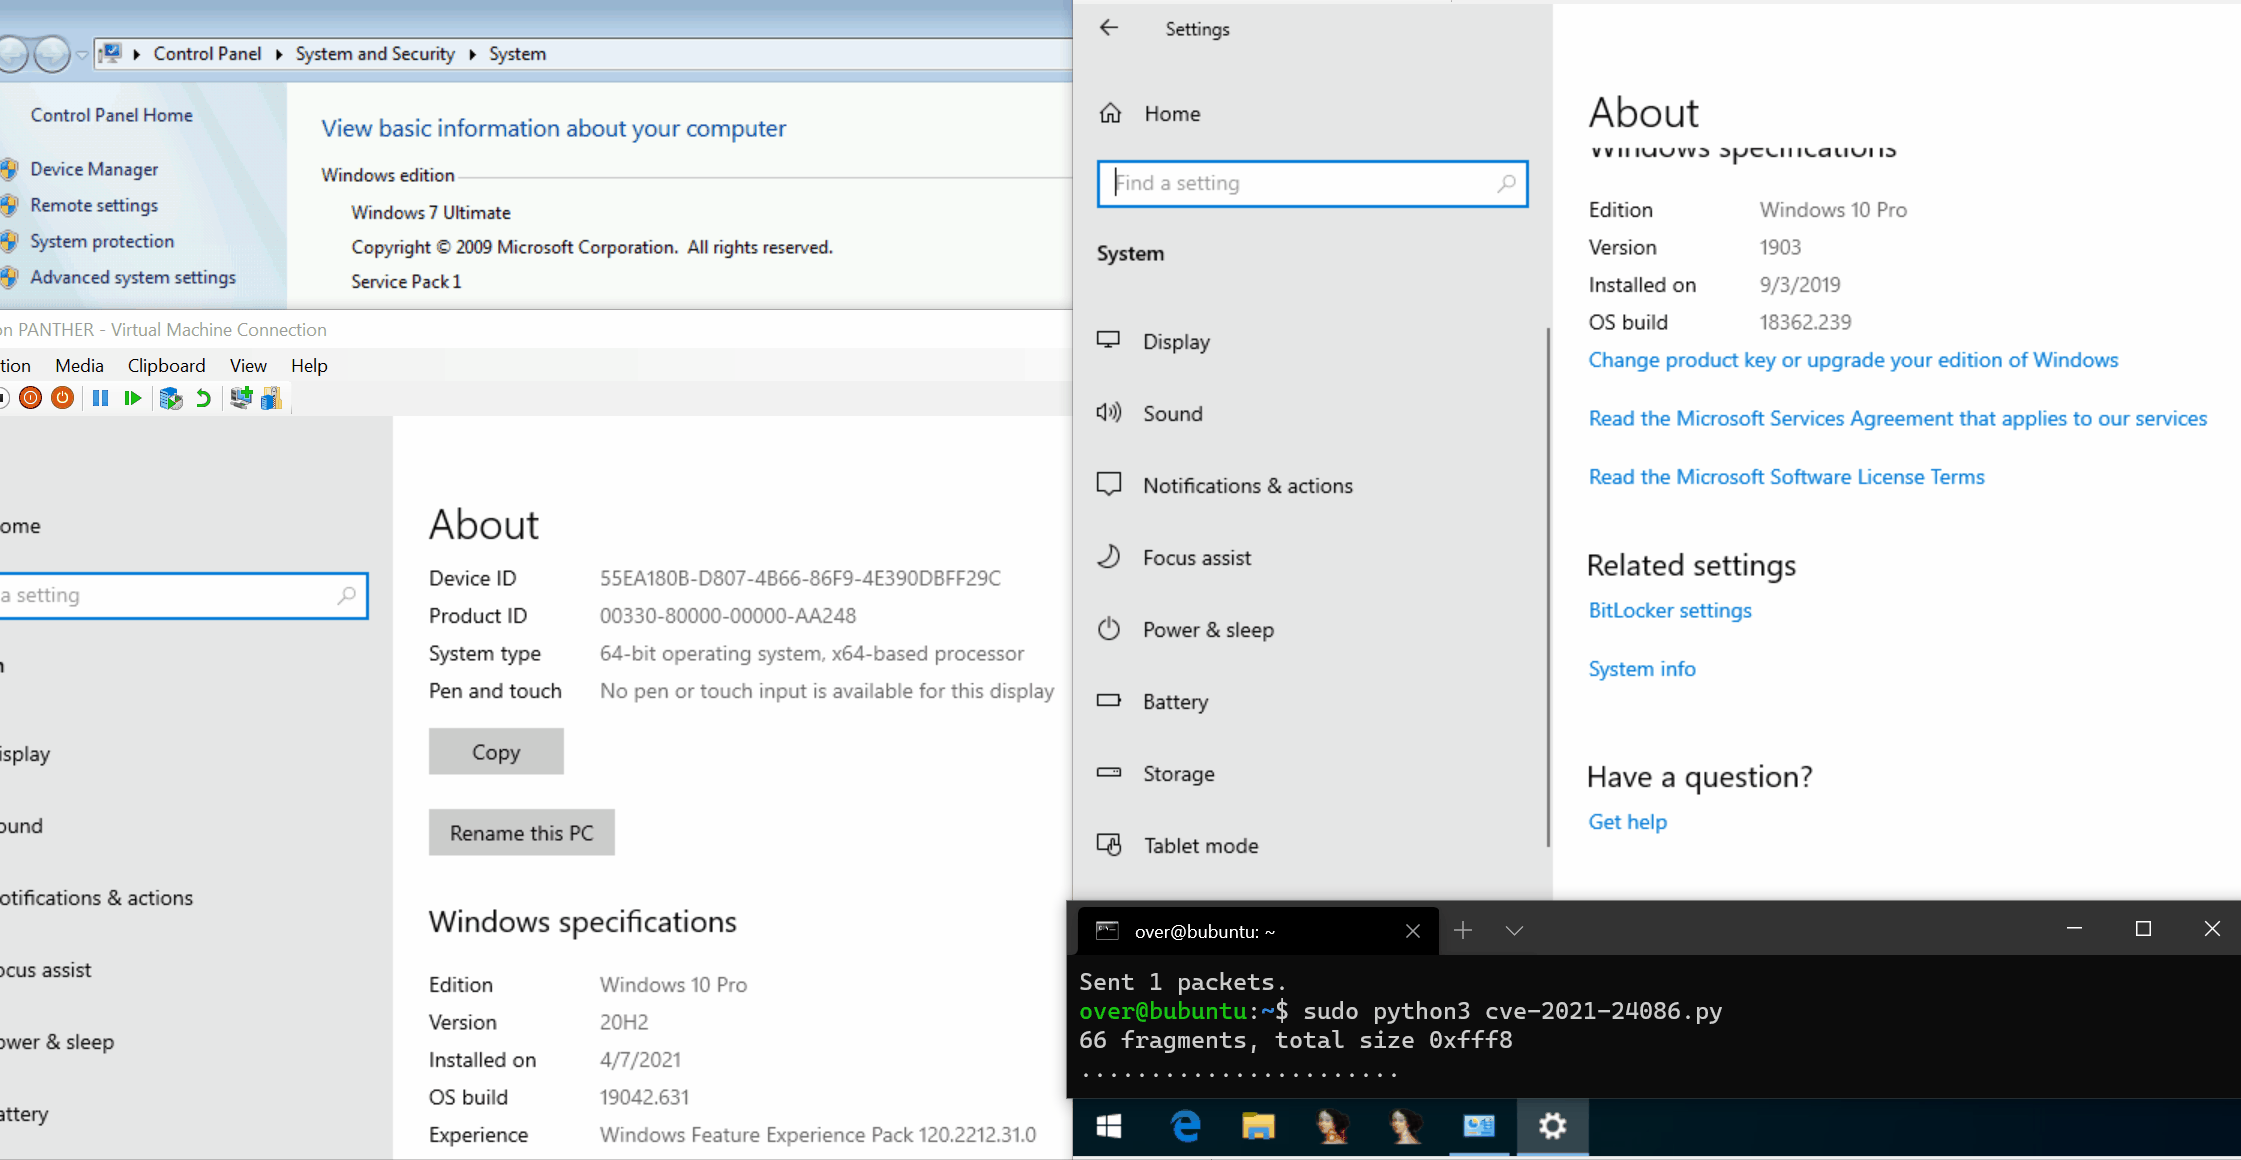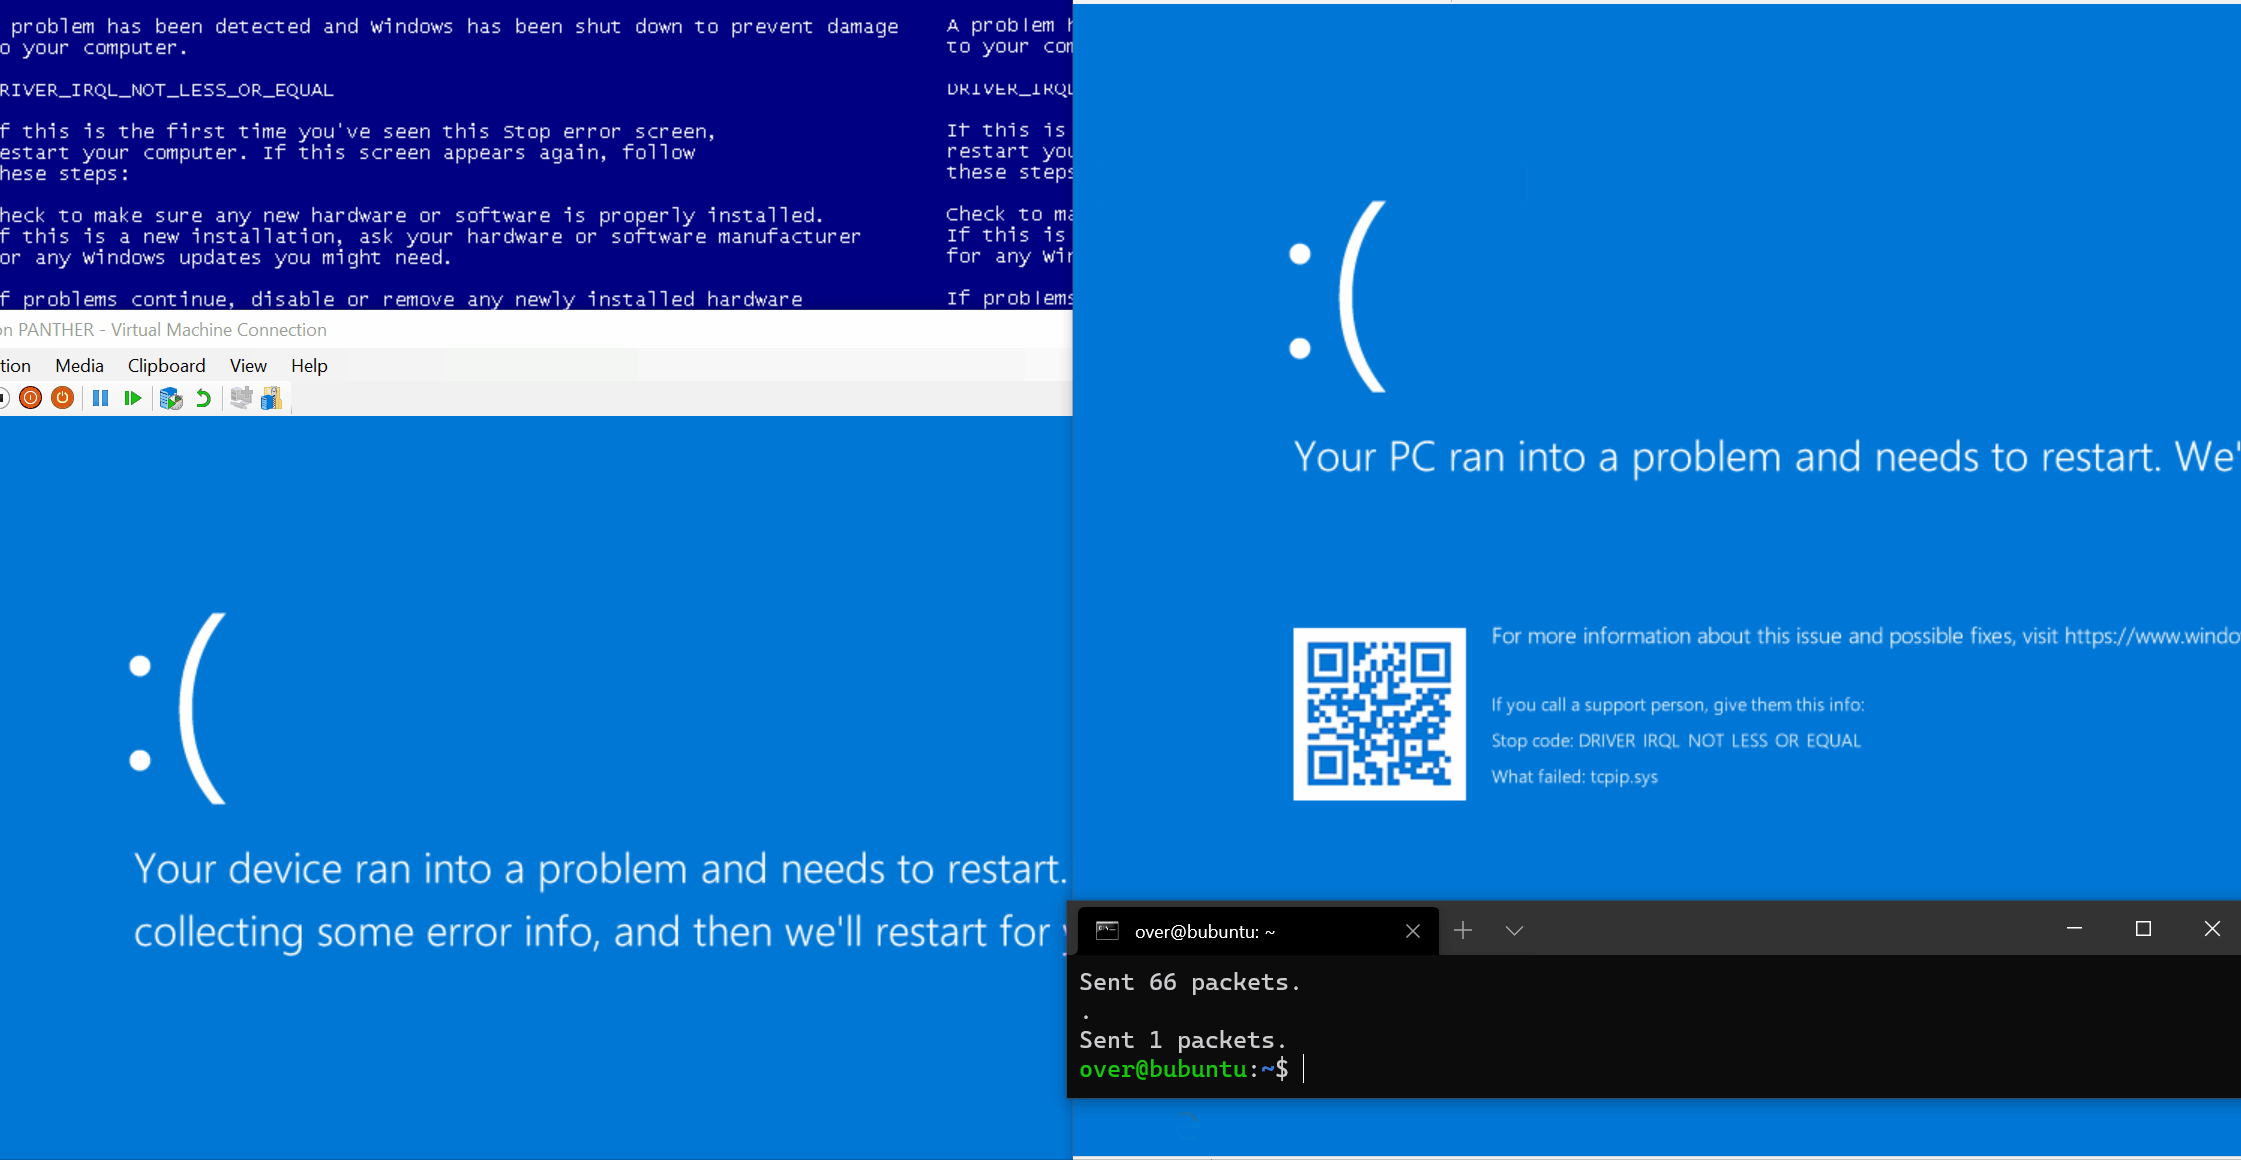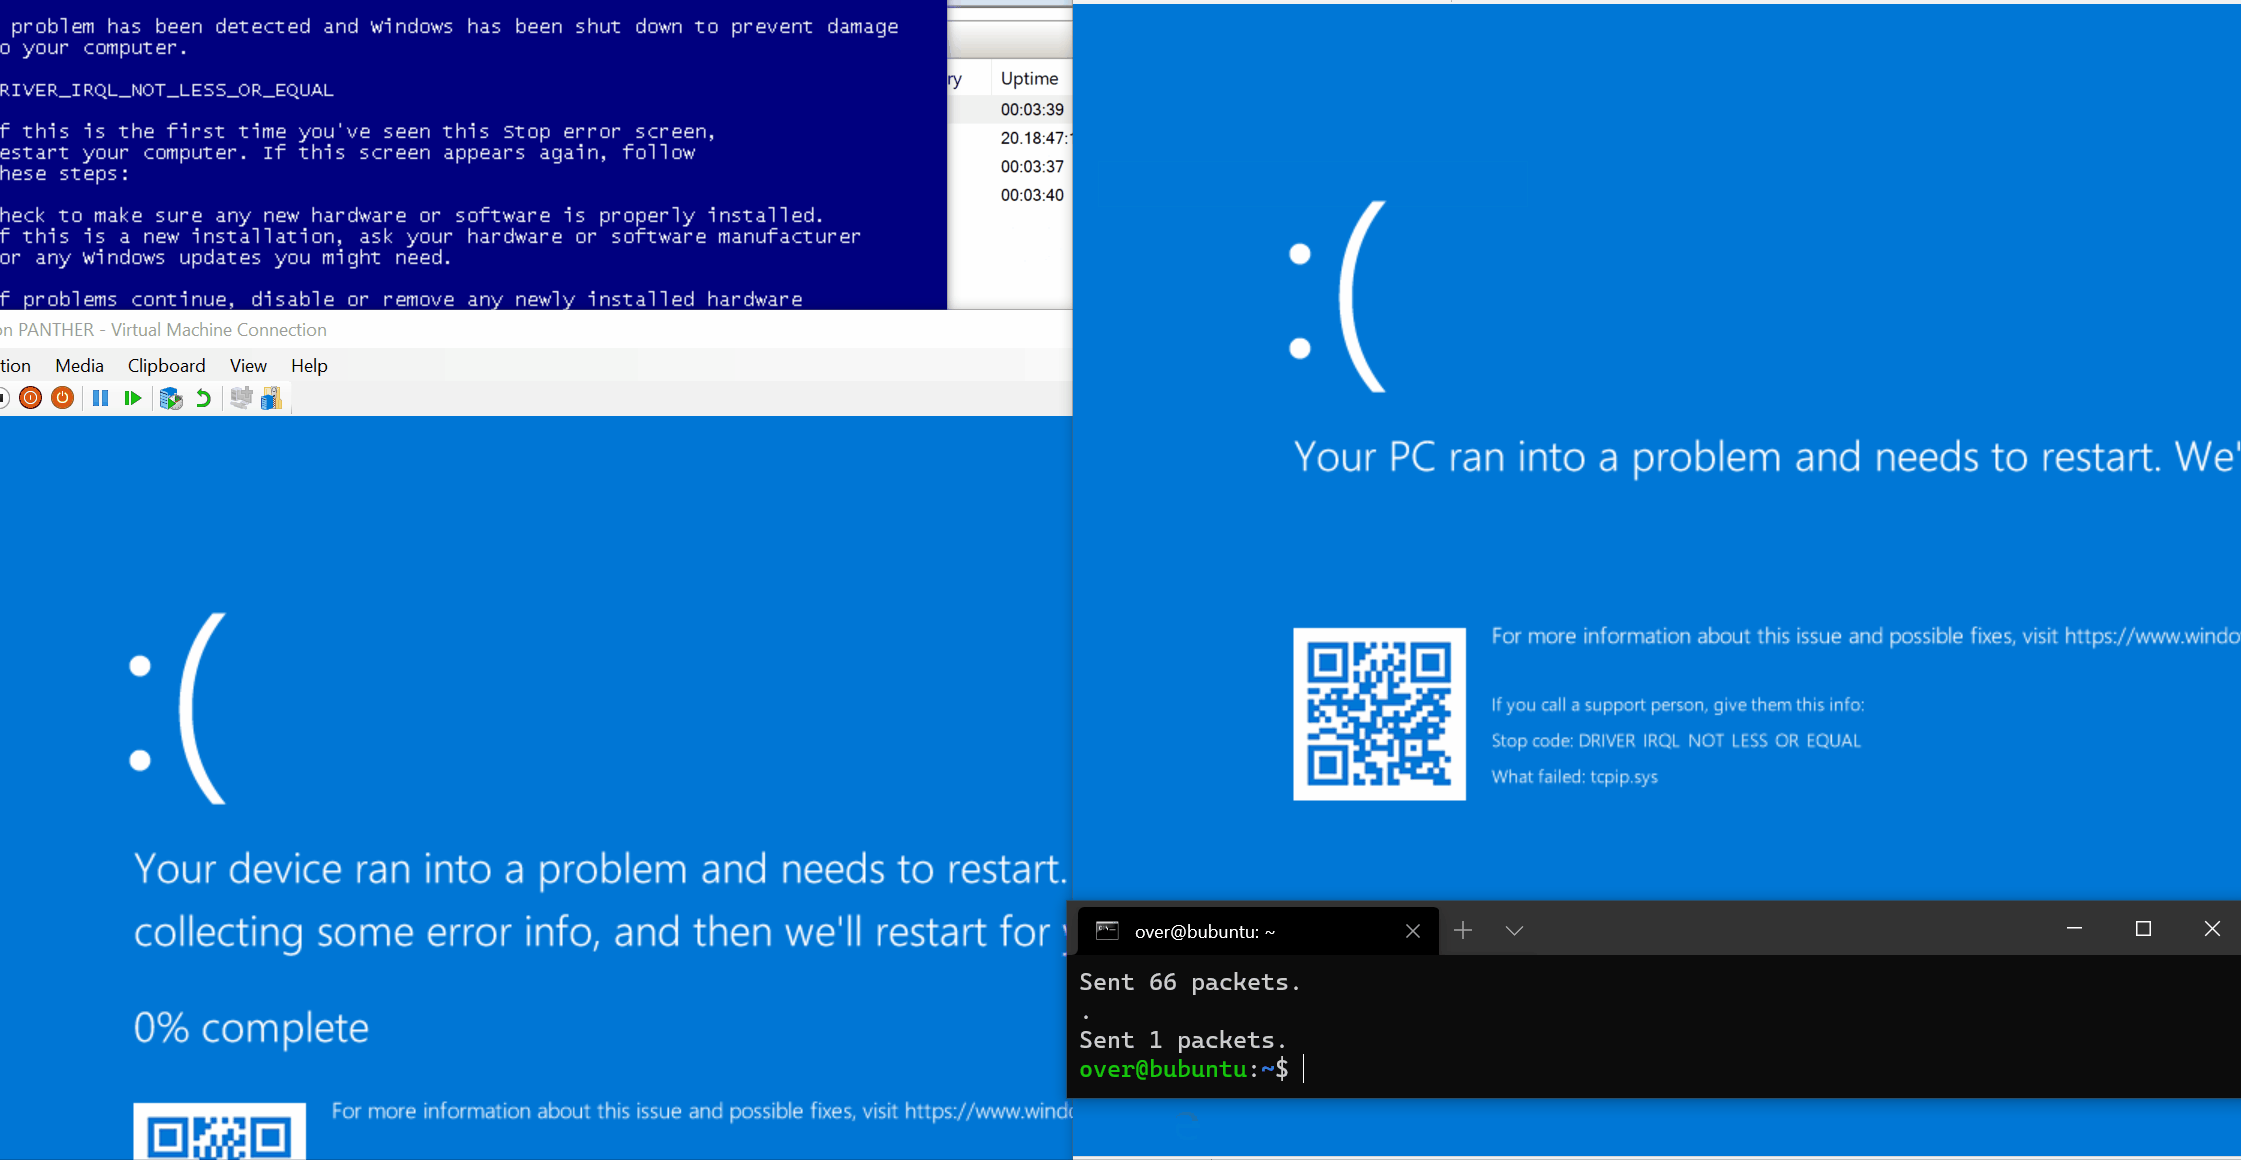 lisinan988/cve-2021-24086-exp
Proof-of-concept exploit for CVE-2021-24086, a NULL dereference in tcpip.sys causing remote denial of service via malicious UDP packets over IPv6.
 patchpoint/cve-2024-38063
Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…
 faizan-khanx/cve-2024-38063
CVE-2024-38063 - Remotely Exploiting The Kernel Via IPv6
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 m8seven/cve-2026-22874-gitea-ssrf-allowlist
CVE-2026-22874 writeup: incomplete SSRF allow-list in Gitea webhook/migration (IPv6 transition and cloud metadata). Fixed in Gitea 1.26.3.
 joshuaprovoste/cve-2025-22870
Proof-of-concept for CVE-2025-22870 demonstrating HTTP proxy bypass in vulnerable versions (<0.36.0) of golang.org/x/net/http/httpproxy. Exploits…
 zenzue/cve-2024-38063-poc
potential memory corruption vulnerabilities in IPv6 networks.
 dragkob/cve-2024-38063
PoC for Windows' IPv6 CVE-2024-38063
 mr-xn/cve-2022-25064
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…