
Hundred OSINT
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
dns-analysiseducationemail-harvesting+7
t-beckett/h-osintLocal-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 randomrobbiebf/ninja-forms-brute
Exploit for Ninja Forms plugin vulnerability allowing unauthenticated download of submission CSVs to disclose email addresses.
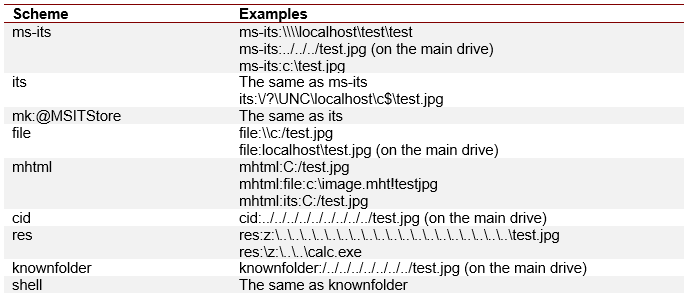 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
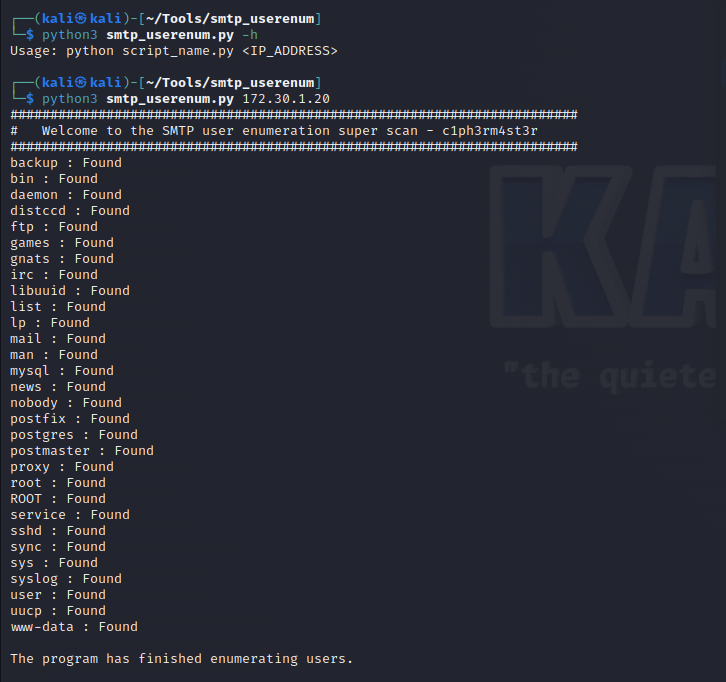 h3x0v3rl0rd/smtp_userenum
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
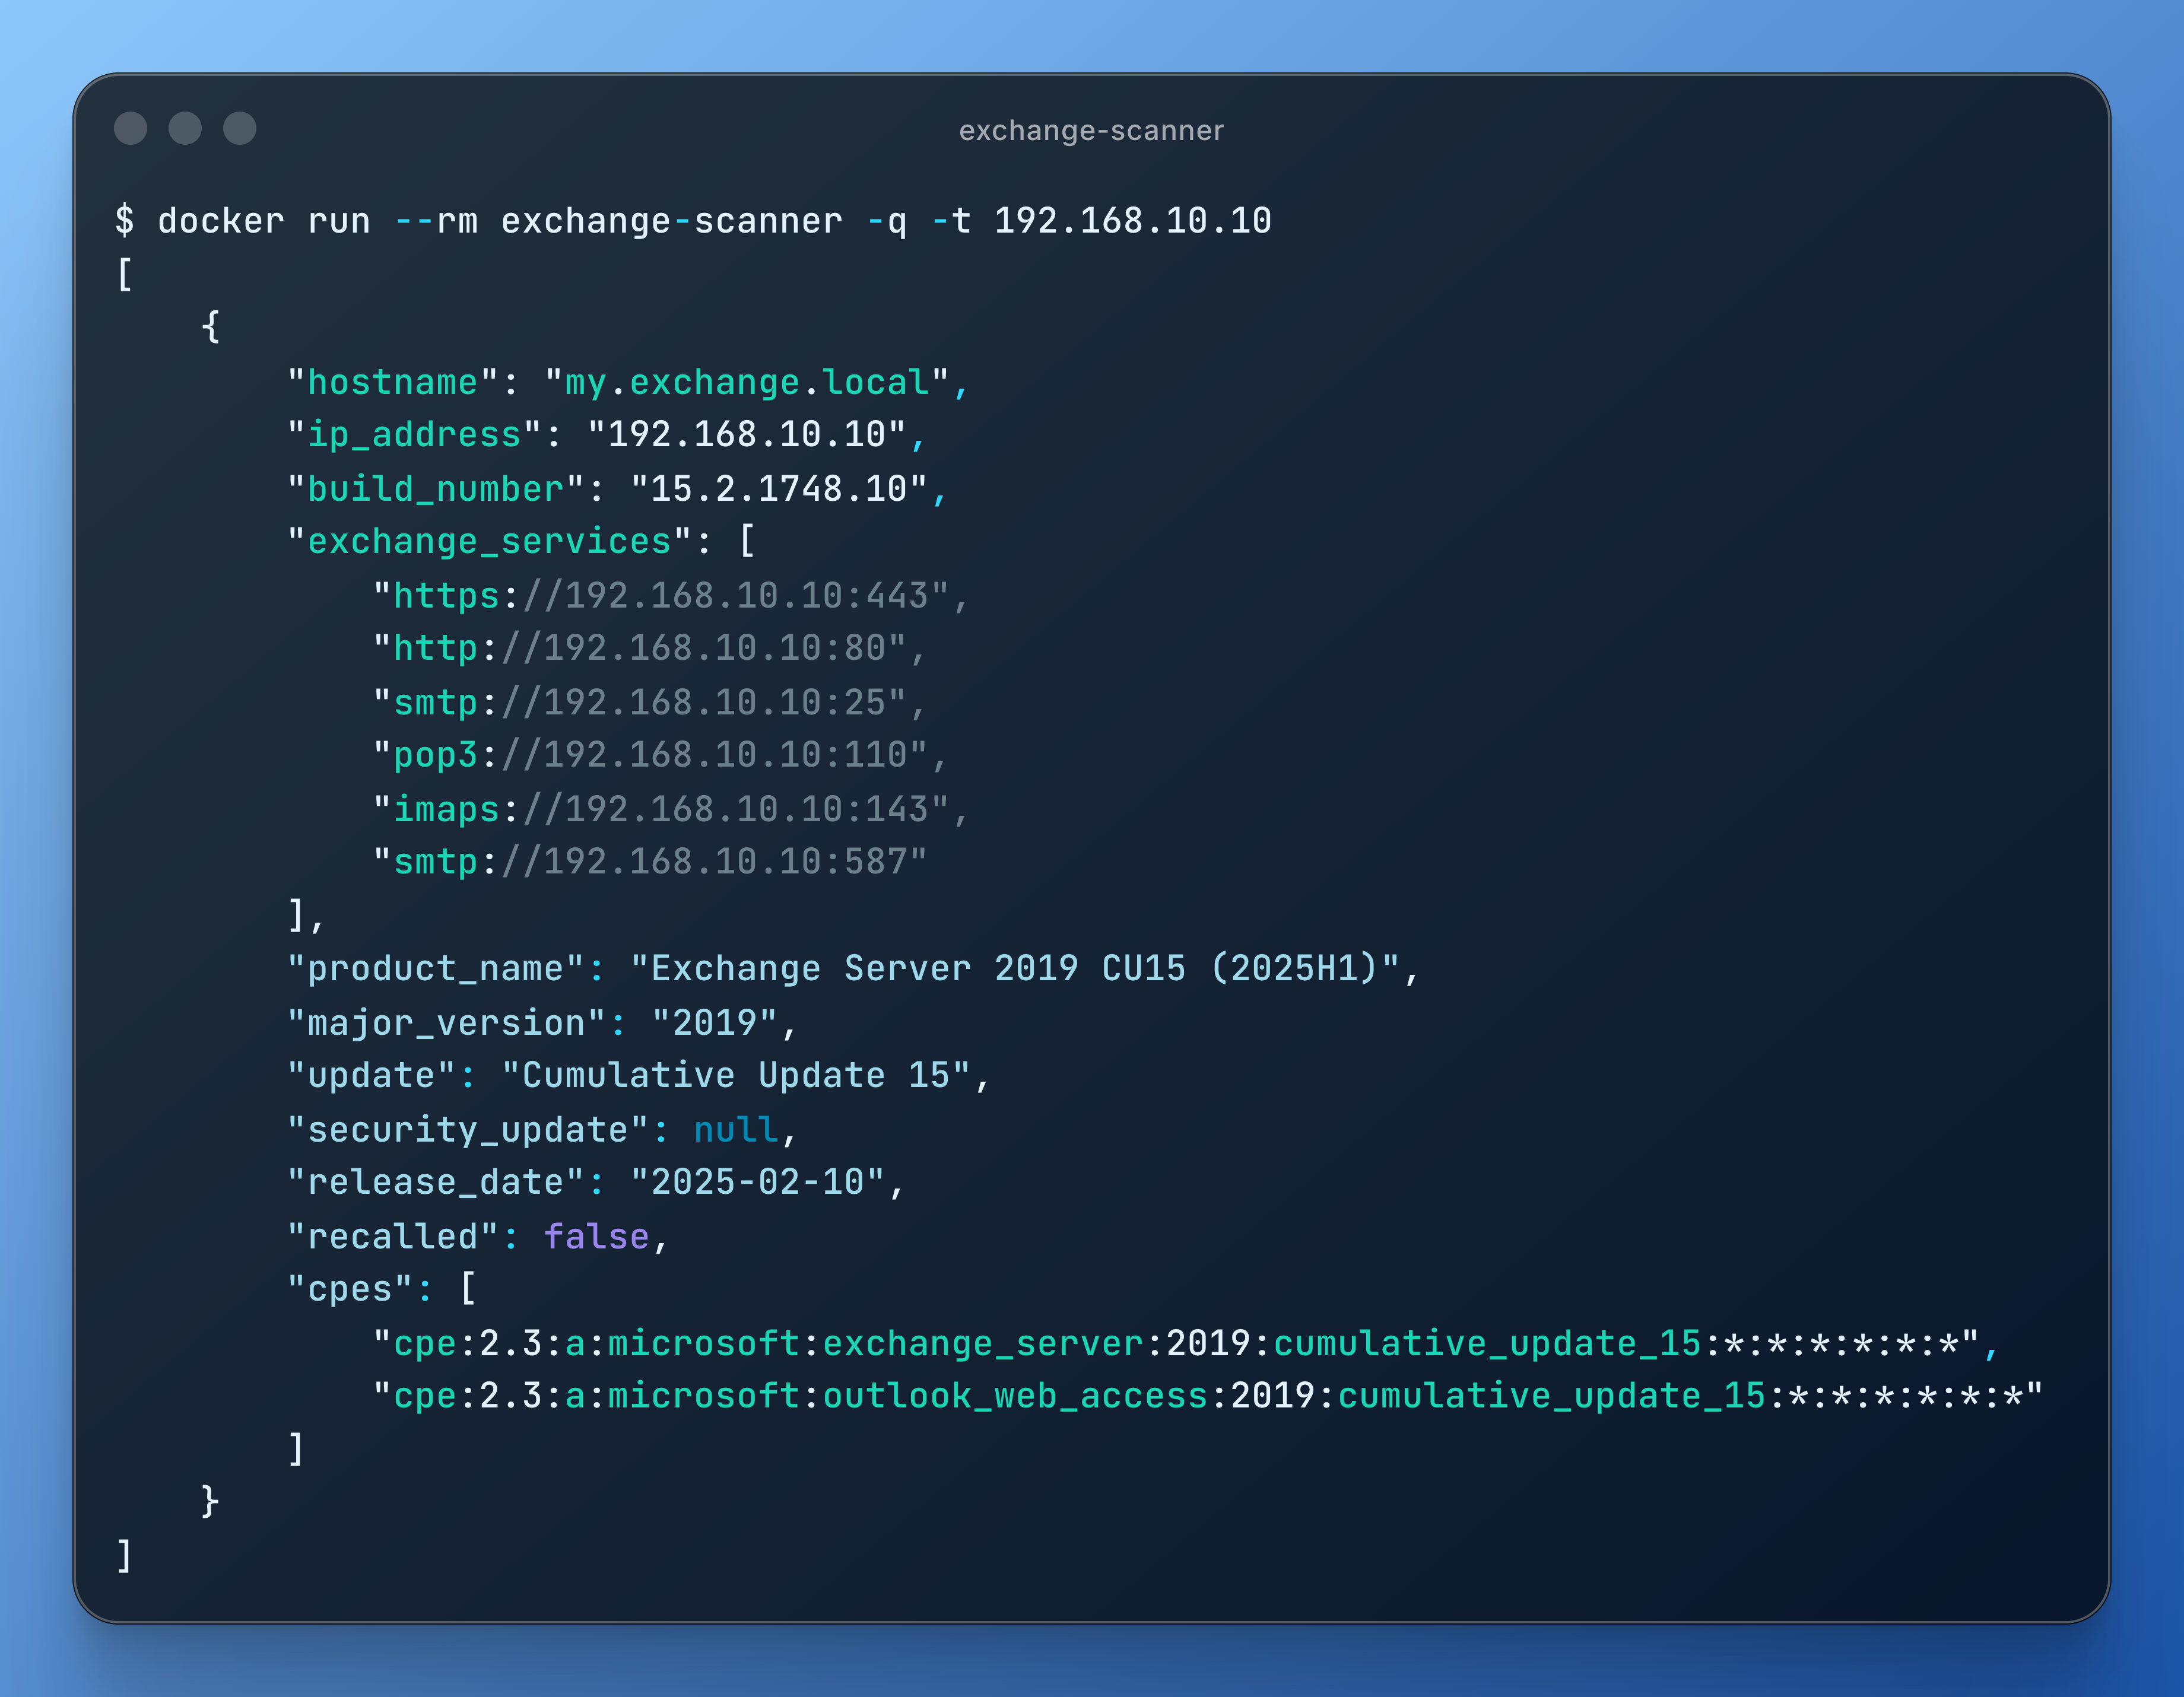 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 kernel364/cve-2024-2876
Proof-of-concept exploit for a critical SQL injection vulnerability in WordPress Email Subscribers plugin. Includes exploitation details, HTTP…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 wh4l3x/cve-2026-xxxx-atlassian-email-enumeration
CVE-2026-XXXX: Atlassian GraphQL Email Enumeration Oracle (CWE-204, CVSS 5.3 MEDIUM)
 redpack-kr/blackash-cve-2025-20393
CVE-2025-20393
 leakix/sentryexploit
CVE-2023-38035 Recon oriented exploit, extract company name contact information
 shinthink/cve-2026-54390
CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
 randomrobbiebf/cve-2025-8422
Propovoice <= 1.7.6.7 - Unauthenticated Arbitrary File Read
 nxploited/cve-2024-0235-poc
The EventON WordPress plugin before 4.5.5, EventON WordPress plugin before 2.2.7 do not have authorisation in an AJAX action, allowing…
 rootxsushant/cve-2023-5561-poc-updated
Updated POC for Unauth Post Author Email Disclosures WordPress CVE-2023-5561