

CVE-2026-48907
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
exploitationpayload-developmentpenetration-testing+6
noname-elv/cve-2026-48907Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 jaycelation/cve-2026-25645
Insecure Temp File Reuse in extract_zipped_paths()
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 xhowenma/rope
Defense framework enforcing routed origin policy to prevent indirect prompt injection in tool-using LLM agents, with deterministic origin checks and…
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
 mbanyamer/cve-2026-25130-cybersecurity-ai-cai-framework-0.5.10
Proof-of-concept demonstrating argument injection leading to OS command injection in the CAI framework's find_file utility, enabling arbitrary…
 krn966/cve-2025-27591
Local privilege escalation exploit for CVE-2025-27591, abusing insecure symlink handling in the below utility's logging to overwrite arbitrary files…
 onedemobird/copy-fail-cve-2026-31431-pythonlower3.10
Python 3.10-compatible implementation of the CVE-2026-31431 exploit, providing a workaround for missing os.splice in older Python versions.
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
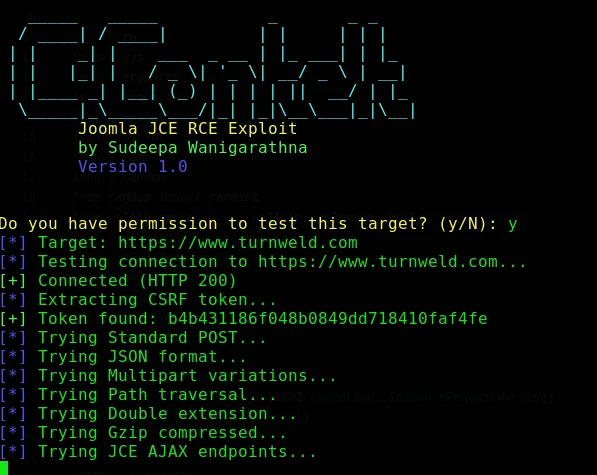 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
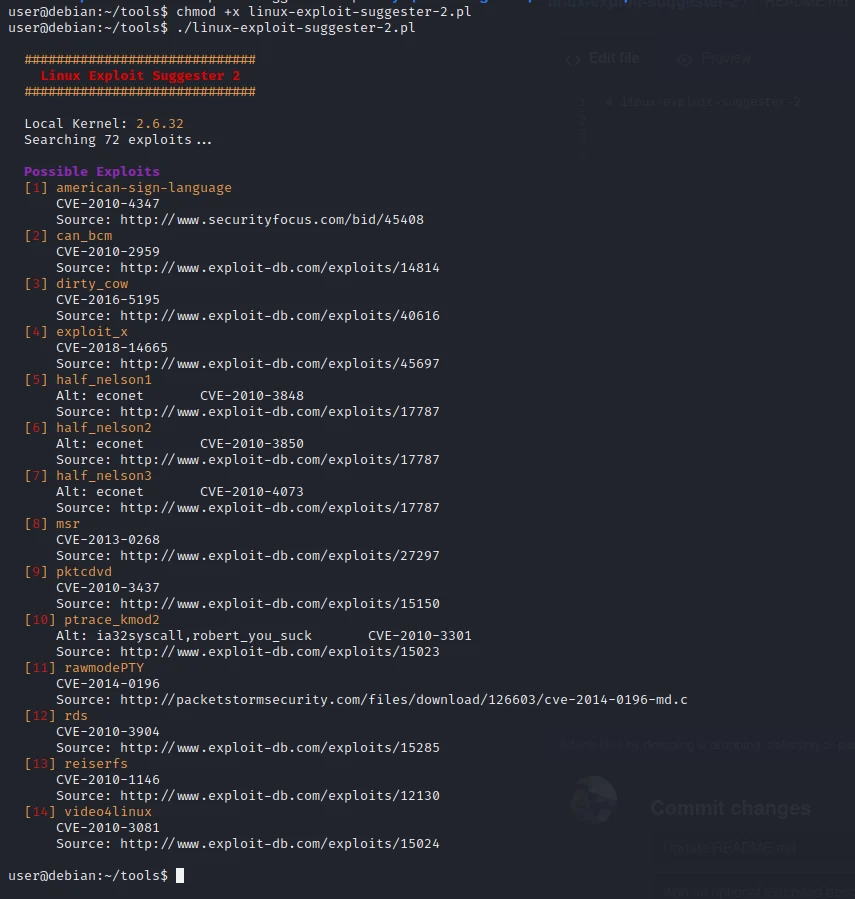 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 pimpamebanihah/cve-2026-43499-app.s0
Placeholder repository referencing CVE-2026-43499; no source code, documentation, or security functionality is evidenced in the available metadata.
 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
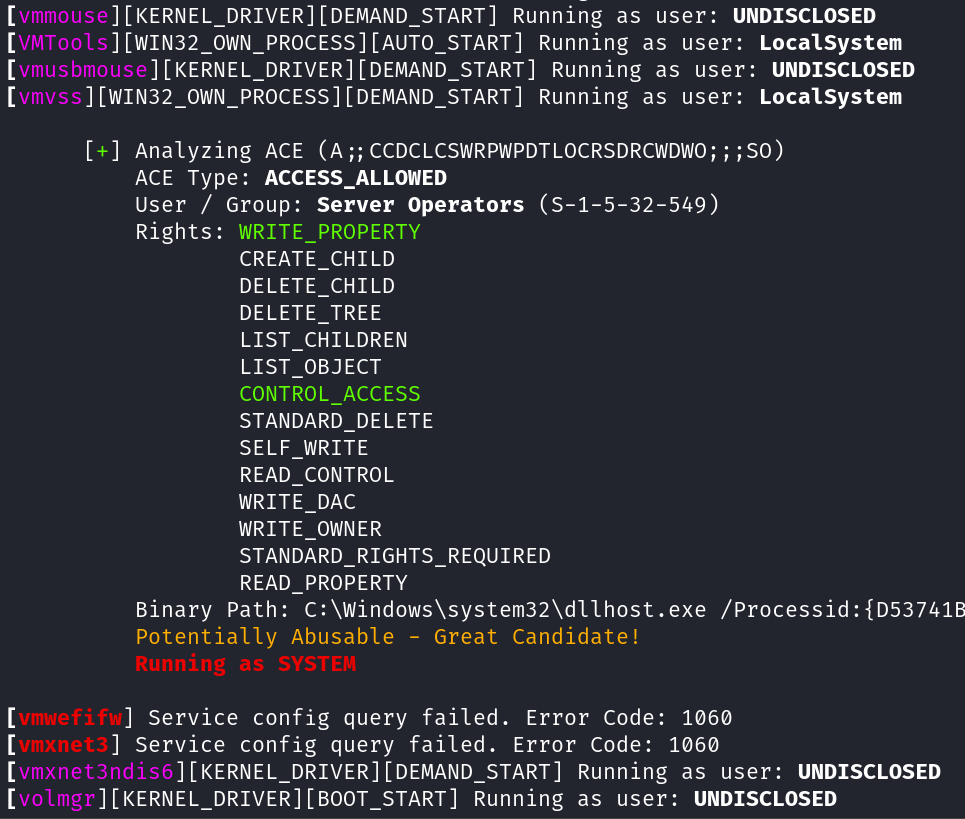 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
 scitotec/log4j-recognizer
A Java helper to identify log4j in the current classpath