

splitting-the-email-atom
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
99
portswigger/splitting-the-email-atomResearch materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 theemperorspath/cve-2026-2441-poc
Proof-of-concept exploit for CVE-2026-2441, a Chrome CSS Use-After-Free in Blink CSSFontFeatureValuesMap, achieving renderer RCE via V8…
 huseyinstif/cve-2026-2441-poc
Proof-of-concept for CVE-2026-2441, a use-after-free in Chrome's CSS engine, demonstrating renderer crash and potential sandboxed code execution via…
 netvanguard-cmd/cve-2026-2441
Exploit for CVE-2026-2441, a use-after-free in Google Chrome's CSS engine, enabling remote code execution via crafted HTML pages. Includes Python…
 d3b0j33t/cve-2026-2441-poc
Proof-of-concept for CVE-2026-2441, a Chrome CSS use-after-free leading to sandboxed renderer RCE. Includes three trigger methods, heap grooming, and…
 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 rvzsec/cve-2022-28368
Dompdf RCE PoC Exploit - CVE-2022-28368
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
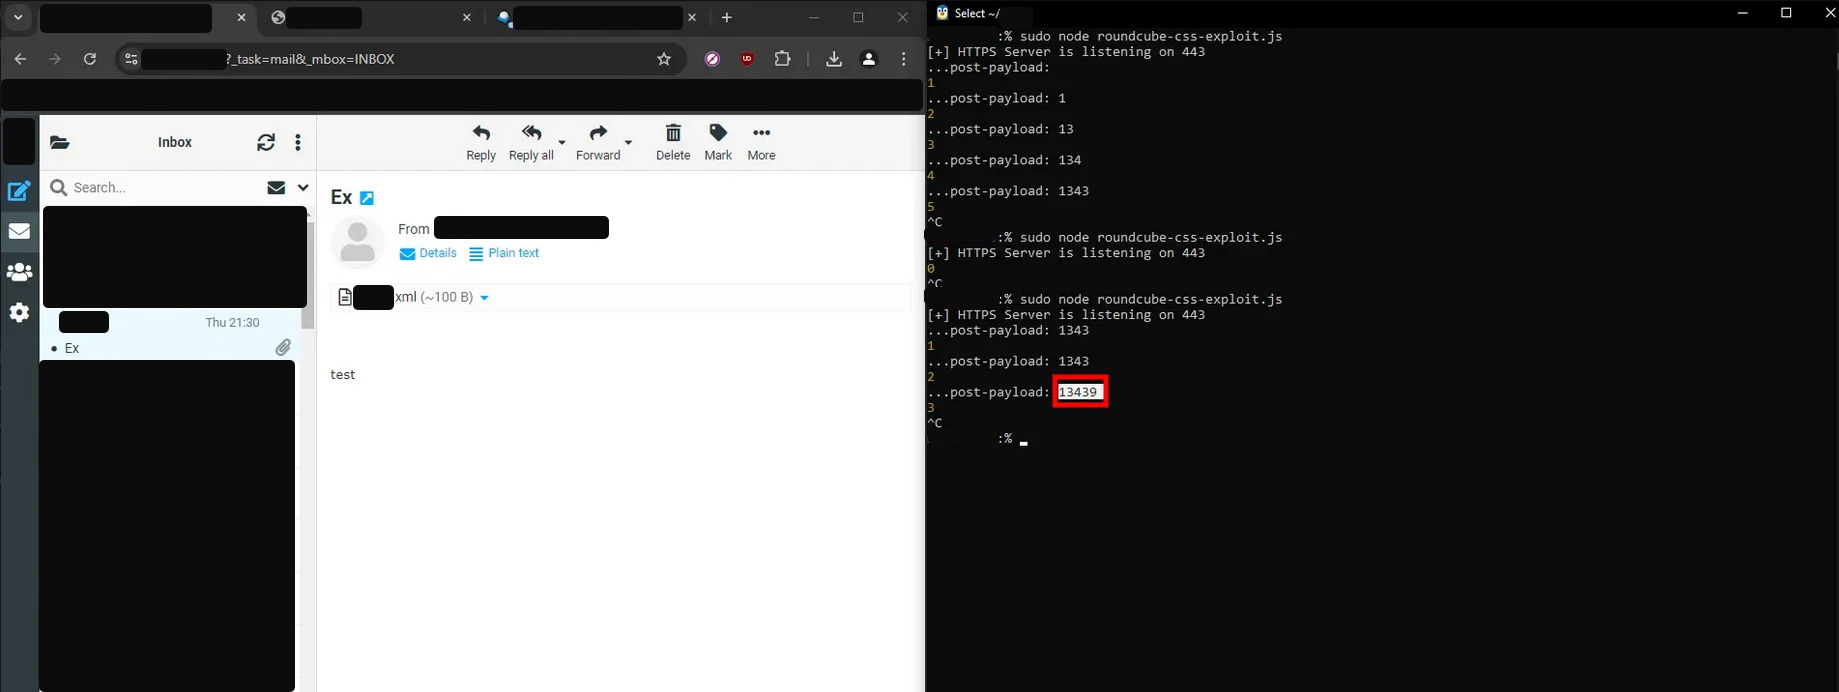 victoni/roundcube-cve-2024-42008-and-cve-2024-42010-poc
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 ktn1990/cve-2024-43160
The BerqWP – Automated All-In-One PageSpeed Optimization Plugin for Core Web Vitals, Cache, CDN, Images, CSS, and JavaScript plugin for WordPress is…
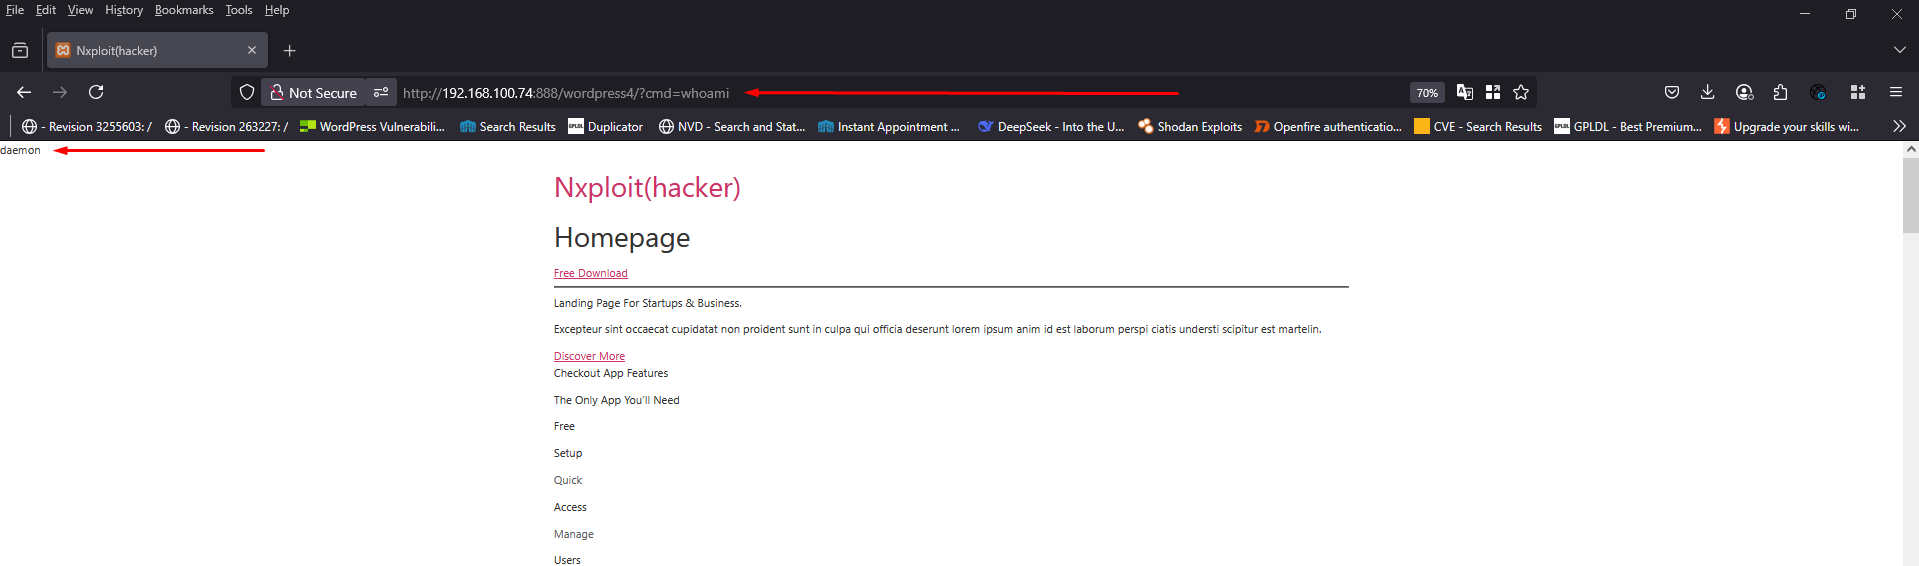 nxploited/cve-2025-39601
WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 murrez/cve-2026-6433
PoC for CVE-2026-6433: WordPress FlipperCode Custom CSS, JS & PHP (≤2.0.7) — unauthenticated SQLi to RCE. Python 3 stdlib; single target or bulk…
 kre80r/cve-2020-13756-env
Vulnerable test environment for CVE-2020-13756 (Sabberworm PHP CSS Parser RCE)
 notthemystery/cve-2026-6300-poc
This is a Proof-of-Concept for the Blink CSS UAF vulnerability tracked as CVE-2026-6300.
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…